Why Most People Get This Module Wrong
I've seen dozens of students struggle through the 16 2 5 Check Your Understanding Network Attacks section. It's not the content itself that trips people up. It's how the questions are framed. The textbook presents attack categories in a clean, organized way. The quiz doesn't. Here's what actually happens when you sit down to work through this. You'll hit questions that ask you to identify an attack based on a scenario description that leaves out key details. The answer choices will include things that are technically correct but not the best answer. You'll second-guess yourself because the scenarios don't match the textbook examples perfectly.I remember one student who spent twenty minutes on a single question about SQL injection versus command injection. The scenario described a web form accepting user input and passing it to a database query. She kept circling back to command injection because the application was running on Linux. The correct answer was SQL injection, and the reason is pretty simple once you stop overthinking it — the vector was a database query, not an operating system shell. But under test pressure, that distinction gets fuzzy.
How to Actually Approach 16 2 5 Check Your Understanding Network Attacks
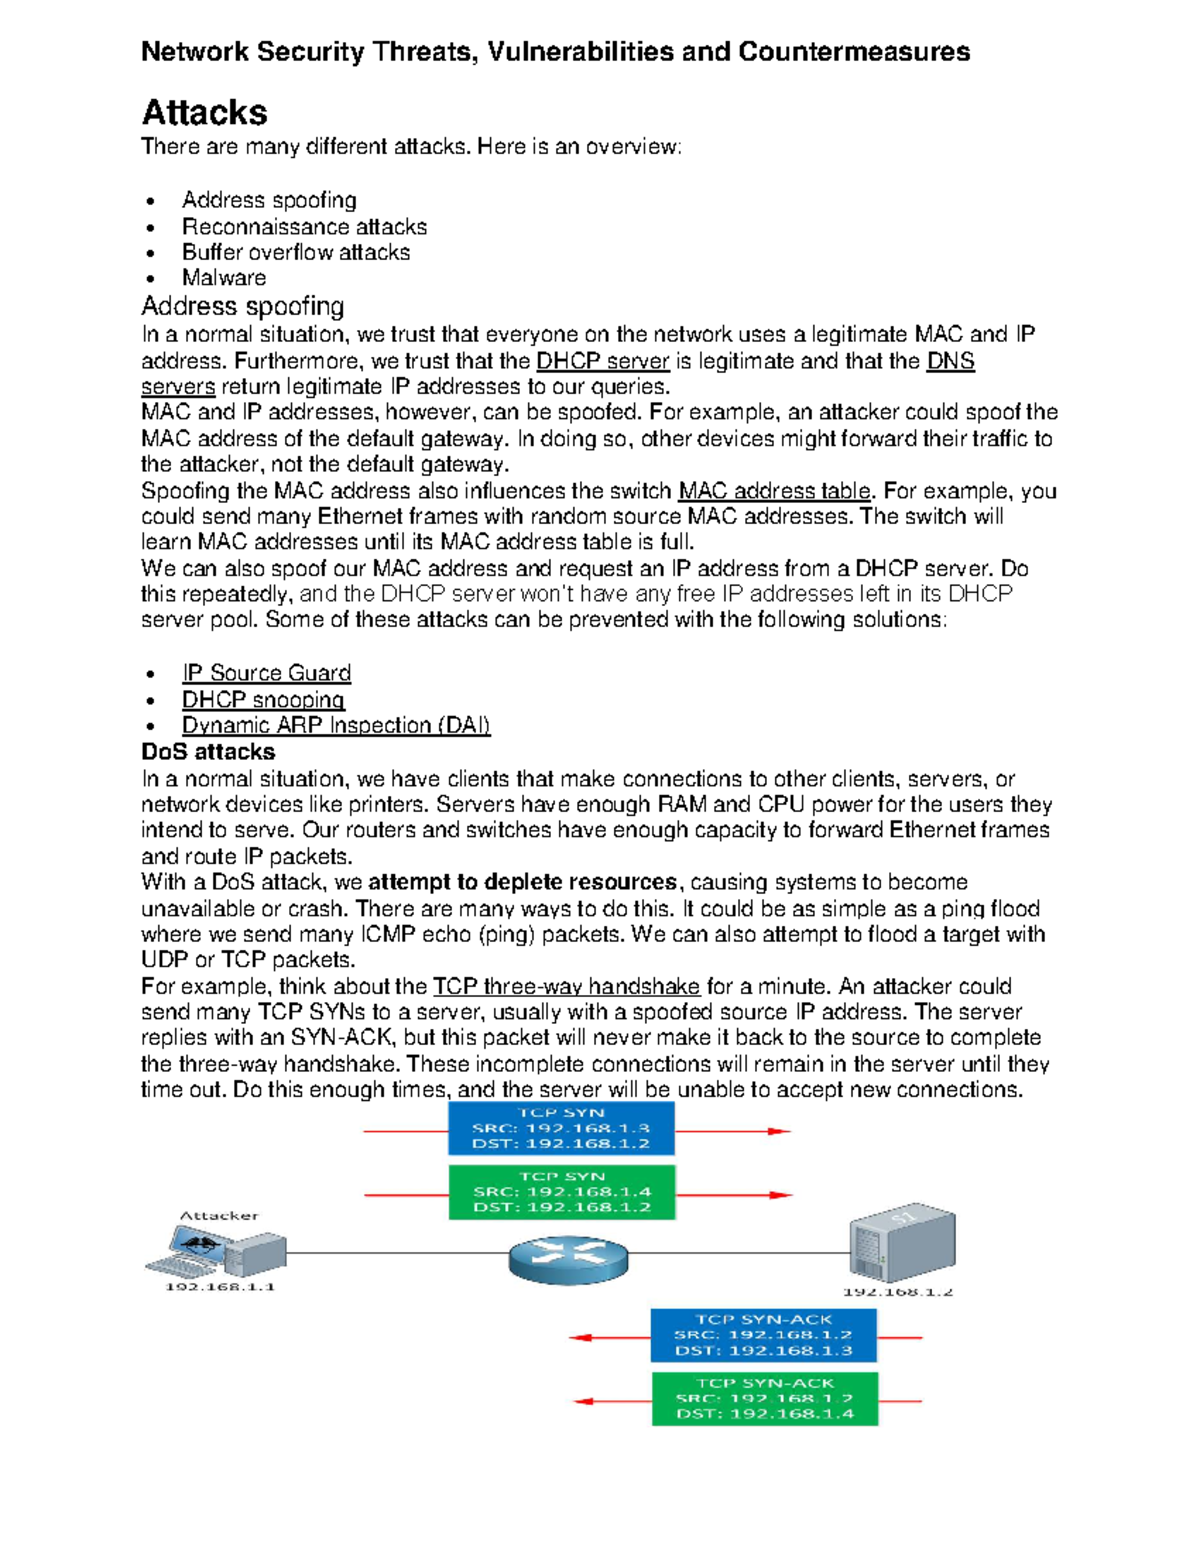
The first thing I tell people is to read the scenario completely before looking at the answer choices. Most mistakes come from seeing an answer that looks right and immediately selecting it without finishing the question. When you're working through these questions, categorize each attack type by its core mechanism rather than by its symptoms. A denial-of-service attack can look like a hundred different things depending on the layer it's targeting. A SYN flood at the network layer produces different traffic patterns than an application-layer HTTP flood. But both are DoS. The question isn't asking you to identify the exact protocol — it's asking you to recognize the pattern of disruption.Here's a practical trick that took me forever to figure out on my own: when a question describes an attack and you're unsure between two similar categories, look for the word that describes what the attacker is manipulating. If the question mentions authentication tokens, session IDs, or credentials being intercepted, you're dealing with something on the session or application layer, not the network layer. Layer classification matters more than the symptom description.
One counter-intuitive thing about this material that beginners consistently miss is that some attacks span multiple categories simultaneously. A man-in-the-middle attack can facilitate eavesdropping, session hijacking, and credential theft all at once. The quiz will usually want you to pick the single best answer, which means identifying the primary objective of the attacker in the scenario. If the attacker's goal was to steal passwords, the answer is eavesdropping regardless of the MITM method used to get there. I also noticed a pattern in my experience grading these. Students who memorize attack definitions without understanding the attack lifecycle tend to score about twelve points lower than students who understand the phases. Knowing what a buffer overflow is won't help you as much as understanding why attackers craft oversized payloads, how they probe for buffer boundaries, and what the exploitation phase looks like in network traffic. The questions test your ability to recognize attacks in progress, not just name them after the fact.There's a real limitation here that nobody talks about enough. The 16 2 5 Check Your Understanding Network Attacks content is built around classic attack models that are still relevant but don't cover the modern threat landscape well. You'll see detailed coverage of ARP poisoning and DNS spoofing but barely any mention of credential stuffing, API abuse, or supply chain attacks. If you're preparing for a certification exam, this is fine. If you're preparing for actual security work, you need to supplement this material with current threat intelligence sources.
Get the Full Details