Understanding Network Security Fundamentals Module 16 5 4
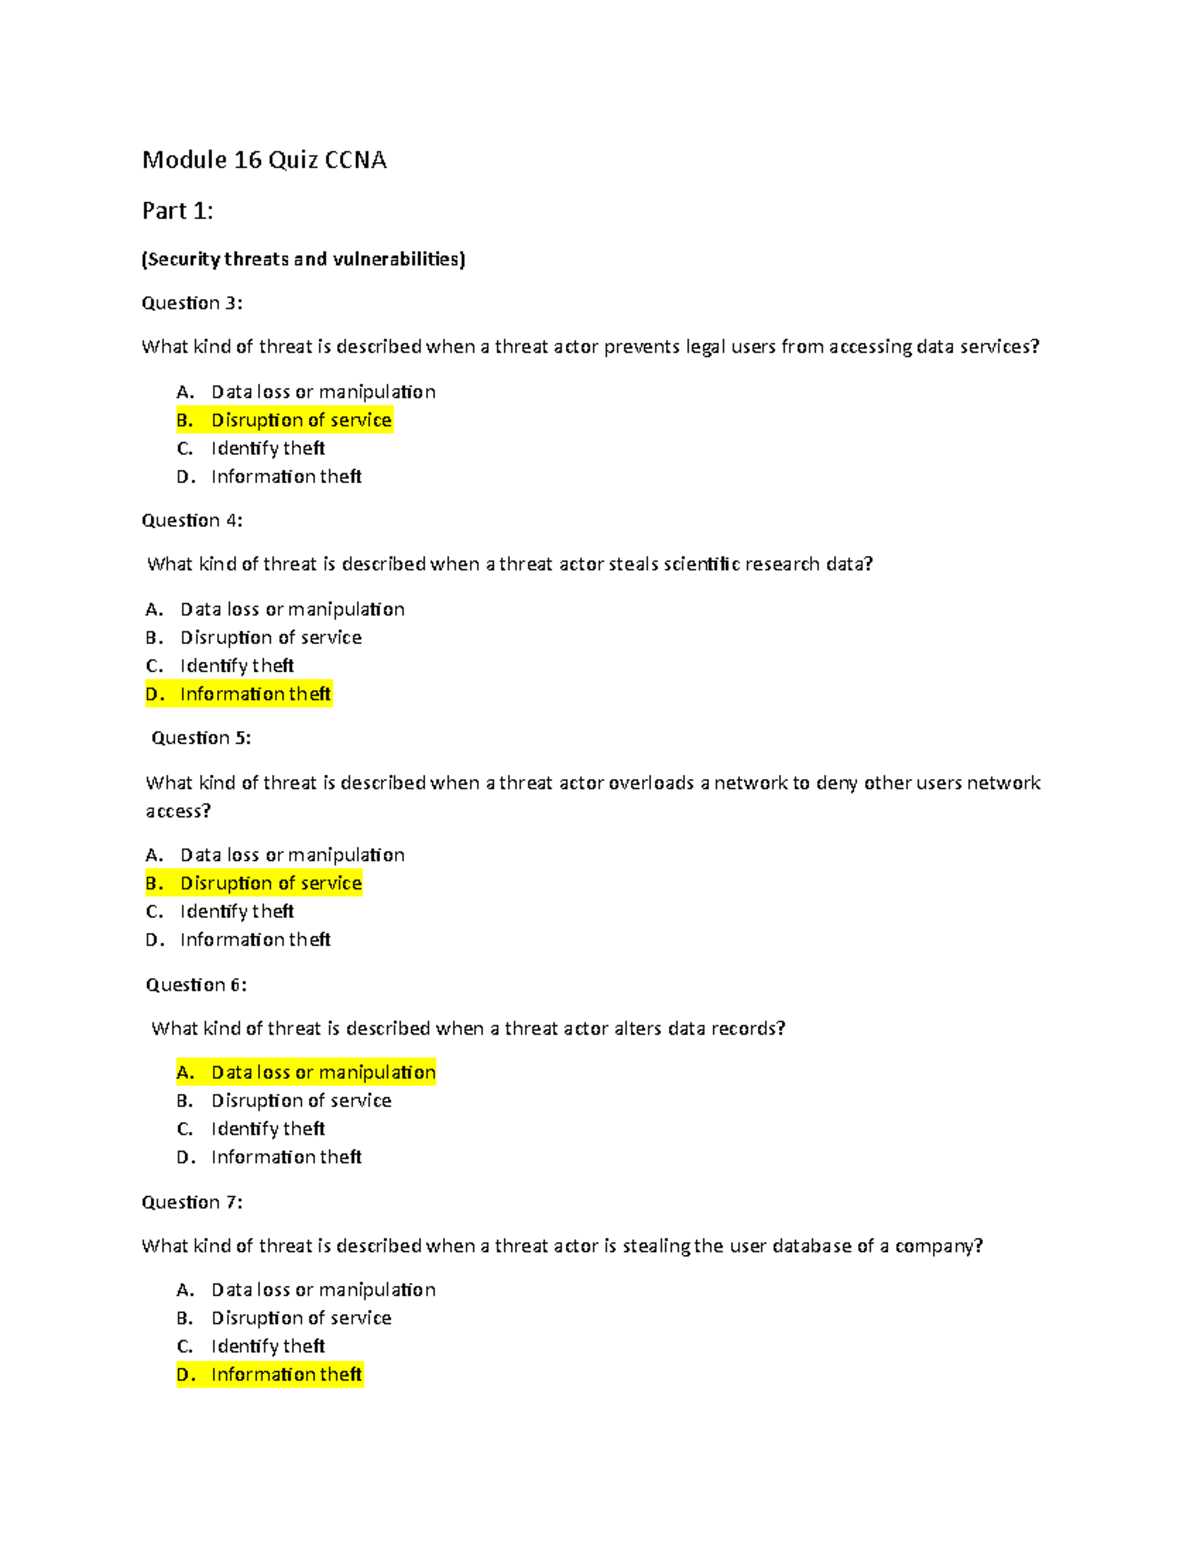
Most people treat these quizzes as checkboxes. They're not. Module 16 5 4 covers the practical side of network security that textbooks skip over entirely. I've seen students pass every theoretical section and still fail when asked to diagram a real segmentation strategy for a mid-size enterprise. The module is broken into three main sections. The first deals with segmentation and zero-trust architecture. You need to understand microsegmentation not just as a buzzword but as an actual deployment challenge. I spent two days trying to implement VLAN isolation on a legacy switch that didn't fully support 802.1Q tagging on all ports. The workaround was moving the critical devices to a separate physical switch entirely. It's ugly but it works when your hardware doesn't cooperate. The second section covers threat detection using network-based tools. IDS versus IPS matters here but the quiz often tricks students on the deployment mode. A IDS in promiscuous mode only monitors. An IPS sits inline and can drop packets. Mixing those up will cost you questions fast. The key thing nobody mentions is that signature-based detection misses almost nothing on known threats but fails completely on zero-day patterns. You need behavioral analysis layered on top and the module expects you to know both approaches exist.
The third part is access control and authentication. RADIUS, TACACS+, and Kerberos get heavy coverage. Here's a common trap: TACACS+ separates authentication and authorization while RADIUS combines them. That difference matters when you're designing a system where different teams need different permission levels. I ran into this when a client asked for granular command-level access on their Cisco routers. RADIUS couldn't give them what they needed without exposing the whole device to broader permissions. TACACS+ solved it cleanly.
How to Approach the Quiz
Don't memorize definitions. The questions test application not recall. Expect scenario-based problems where you have to pick the right security control for a given situation. For example, you might be told a company has guest WiFi users who also need occasional file server access and you have to choose the right authentication method. The answer involves network access control combined with something like NAC or 802.1X rather than just a simple username password setup. Pay attention to the timing questions. Some modules have a two hour window but most students finish in about forty five minutes if they actually understand the material. If you're spending over an hour you're likely second-guessing answers instead of trusting your knowledge. I've timed myself and my best runs hover around thirty eight minutes with everything correct. The ones where I rushed through under twenty minutes usually had two or three wrong answers I wouldn't have missed with more care. There's also a hands-on component in some versions of the module. You'll configure firewall rules or analyze packet captures. Wireshark is essential here. If you can't read a TCP handshake or spot anomalous traffic patterns in a capture file you'll struggle with the practical portion. Practice with sample .pcap files available online before the quiz hits you with a real one.
Get the Full Details

Common Pitfalls to Avoid
Students regularly confuse symmetric and asymmetric encryption use cases on this quiz. Symmetric is for bulk data encryption. Asymmetric is for key exchange and digital signatures. If a question asks about encrypting a large file transfer between two servers the answer is almost always symmetric unless it's specifically about establishing the initial secure channel. That initial handshake uses asymmetric methods to negotiate the symmetric key. Another mistake is assuming more security controls always equal better protection. The module tests whether you understand trade-offs. Adding an IPS in front of a sensitive database server might look good but it introduces latency and creates a single point of failure. Proper placement behind a firewall and using intrusion detection without inline blocking in certain segments can be the smarter choice depending on your risk assessment. The quiz will throw scenario questions that require this kind of judgment call. Lastly, don't overlook the compliance angle. The module references standards like NIST and ISO frameworks. You don't need to memorize every control ID but knowing which framework covers what area helps. NIST 800-53 handles federal systems. ISO 27001 is the general standard. If a question mentions HIPAA or PCI DSS requirements you need to connect those to the right security practices like encryption at rest or quarterly vulnerability scans.
Resources and Downloads
I've compiled some practice materials that mirror the actual quiz structure. These aren't official dumps which would be useless anyway. They're reconstructed scenarios based on what students typically encounter. The file covers segmentation design problems, authentication method selection, and packet analysis exercises. You can find it shared across several study forums. Search for the module number and someone usually has a copy from last semester. The official learning management system also has a resource folder with additional reading. Most people skip it but the supplemental materials there explain the why behind certain controls better than the main lecture content. The instructor who writes this module tends to reference real breach reports and the reading materials show you exactly which incidents each control was designed to prevent. Understanding the origin of a security measure makes it much easier to remember when to apply it.
Final Thoughts
This module isn't difficult if you approach it correctly. The people who fail are the ones who treat it like a trivia test instead of a practical skills assessment. Network security is about making decisions with incomplete information and the quiz reflects that. You'll encounter questions where two answers seem right and you have to pick the one that best fits the scenario constraints given. That's the actual job. This module just checks whether you're ready for it. Study the scenarios not just the slides. Practice reading packet captures until it becomes second nature. And remember that understanding why something works matters more than knowing that it works. The quiz will test both but the second one is what actually keeps networks secure once you're done with the course.