Network Slicing in 5G Changes the Security Picture Entirely
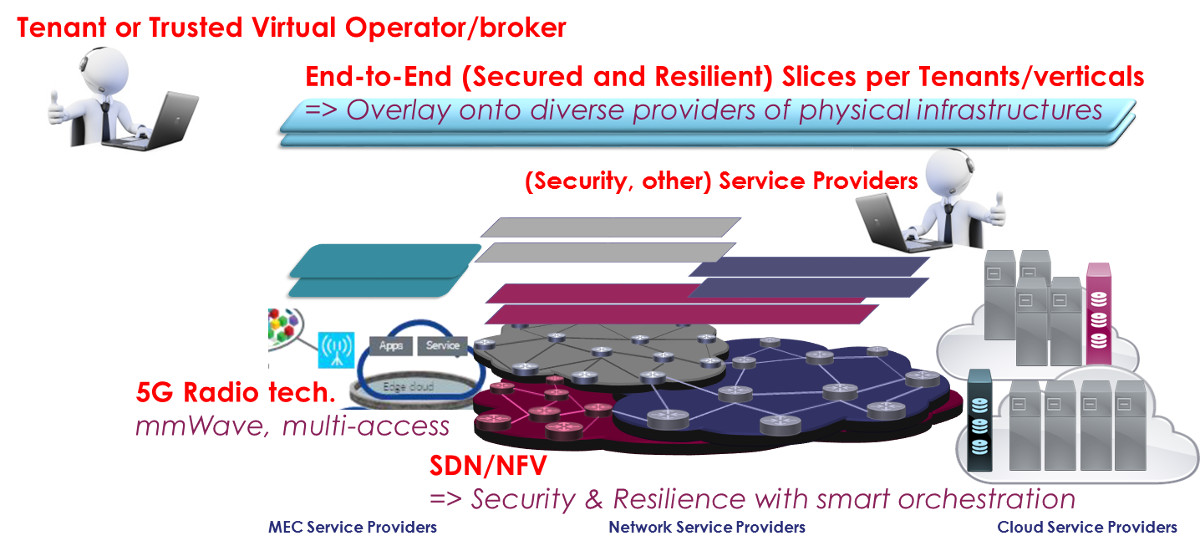
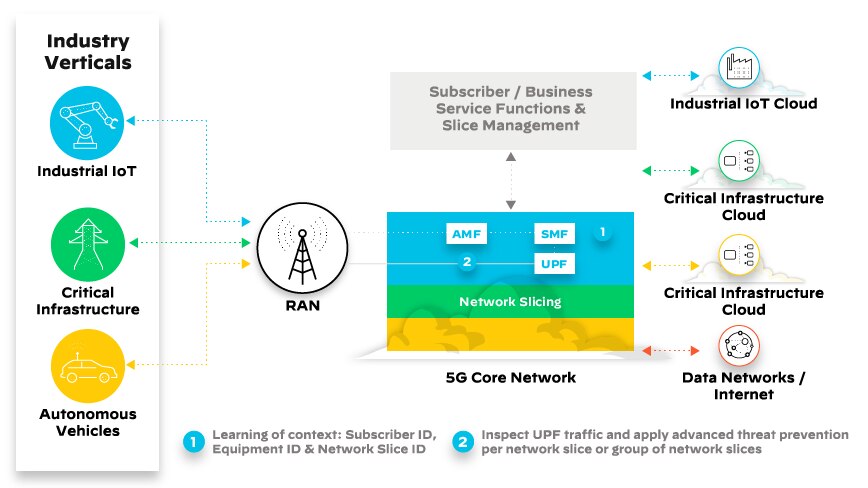
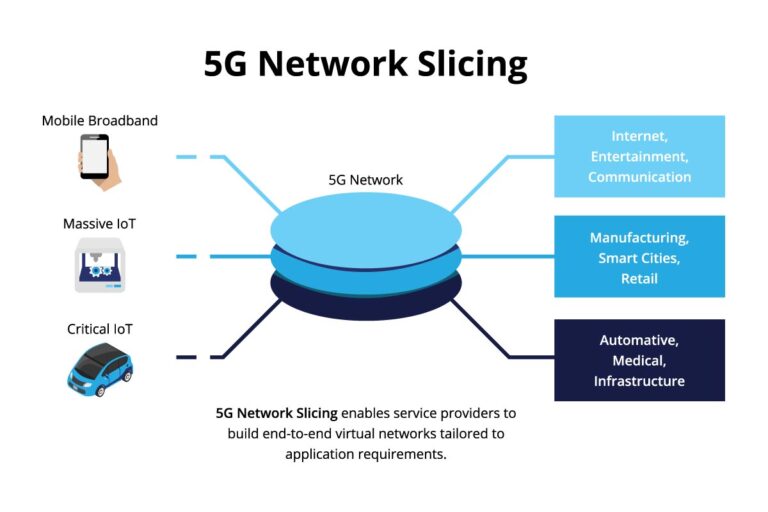
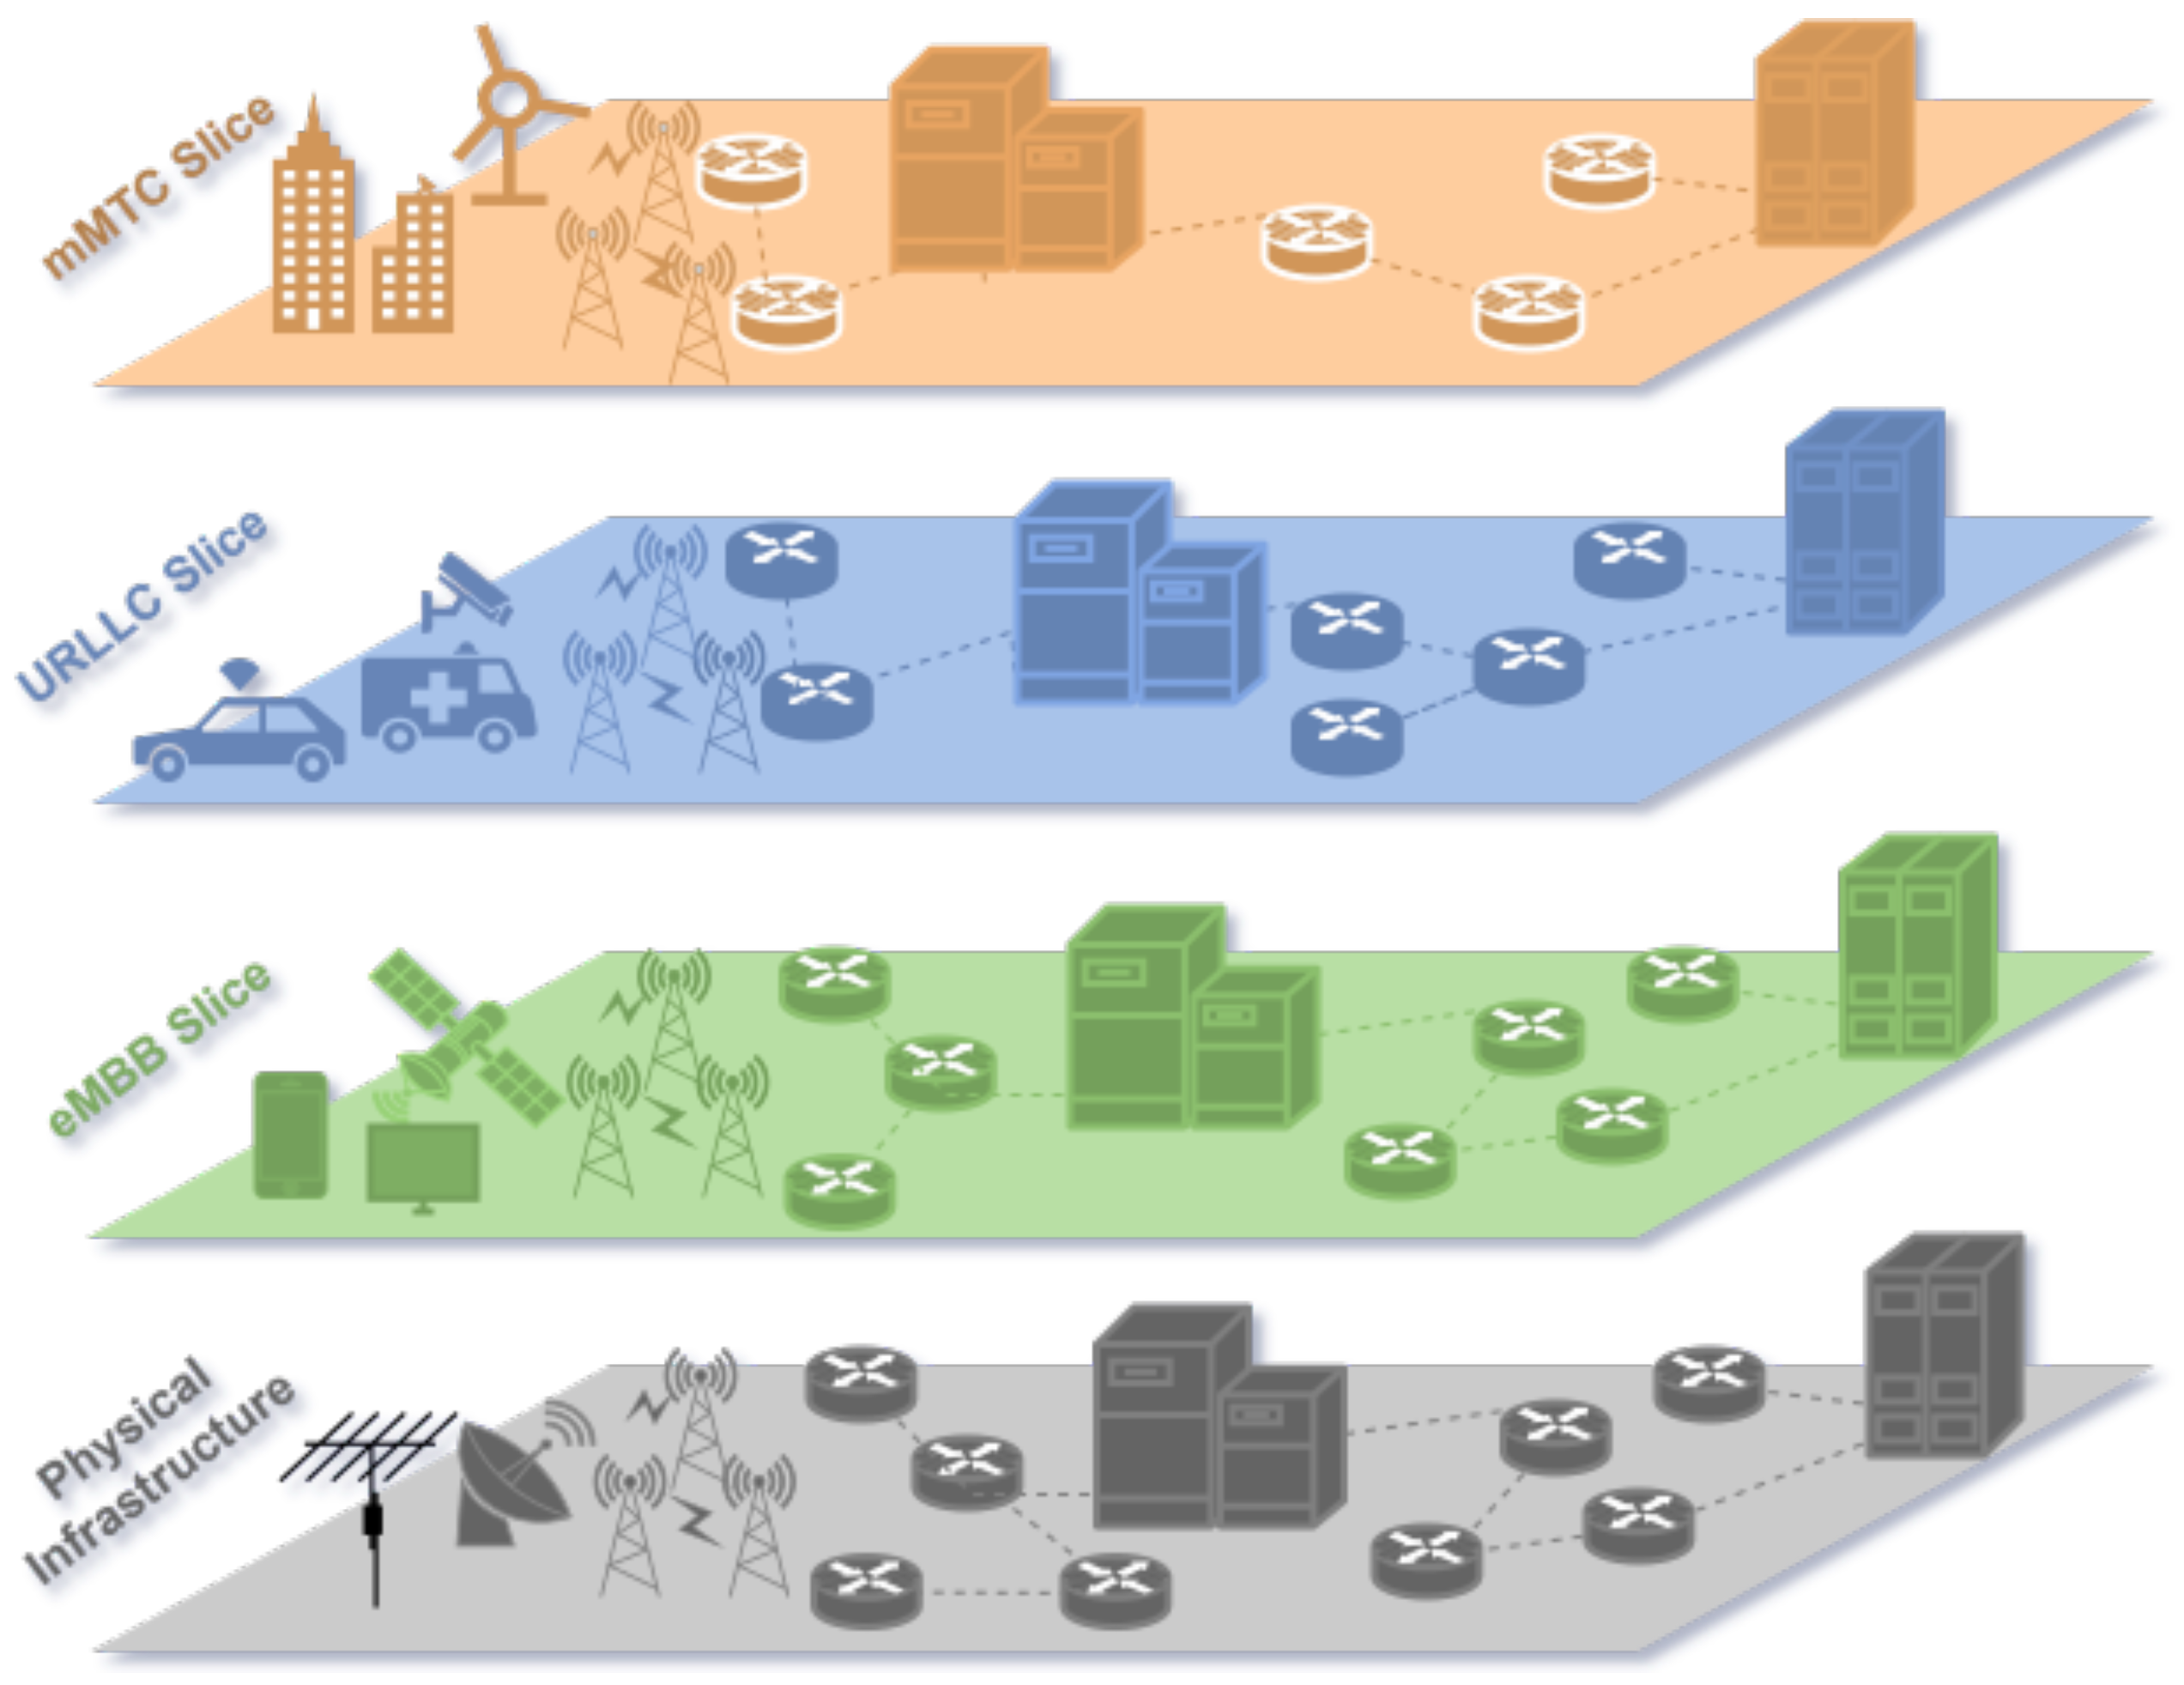
When you slice a 5G network, you're not just segmenting bandwidth. You're creating isolated virtual environments that share the same physical infrastructure. That separation is where the security model breaks down if nobody documents it properly. I've seen teams build elaborate slice architectures and then hand over a blank PowerPoint with three slides claiming "security is handled." It doesn't work that way. A proper deck covers isolation mechanisms first. NS-level isolation using lightweight containers or VMs, NFV infrastructure isolation, and control plane versus user plane separation. Most people skip right to encryption and call it a day. That's backwards. If the isolation layer fails, encryption becomes irrelevant because the attacker already has access to the slice environment. Then you document authentication and authorization per slice. Each slice can have its own AMF (Access and Mobility Management Function) and SMF (Session Management Function) instances. The key point is that credentials and policies must be slice-specific, not global. I learned this the hard way during a deployment where a shared credential pool between two slices allowed a compromised IoT device to pivot into a URLLC slice meant for industrial control systems. Took us six weeks to patch after the fact.
Your slides need to cover traffic filtering at the N3 and N9 interfaces, service-based architecture (SBA) message protection using TLS 1.3, and how you handle slice-specific key derivation. The 5G AKA procedure produces separate keys per slice, but only if your UDM and AUSF are configured correctly. I've seen misconfigured UDM instances where the SUCI decryption failed silently and the system defaulted to a fallback authentication path that didn't bind keys to the requested slice identifier.
Building the Deck from Scratch
Start with a threat model mapped directly to 3GPP TS 33.501. Don't use a generic threat framework. The standard already identifies the relevant attacks: cross-slice eavesdropping, slice hijacking, denial of service through resource exhaustion, and man-in-the-middle on service-based interfaces. Structure your slides around these four categories. That gives you a clean narrative without wandering into irrelevant security territory. For each threat, show the countermeasure, the specific 5G network function that implements it, and the configuration parameter you need to verify. This is where most presentations become vague. "We use encryption" tells the reader nothing. Write "N3 interface uses IPsec ESP mode with AEAD cipher suite, keys derived from K SEAF bound to S-NSSAI." That level of detail is what separates a usable document from filler content. I recommend including a topology diagram on slide three showing your instantiated network functions, which ones are shared versus dedicated per slice, and where the security boundaries sit. Label the trusted and untrusted non-access stratum (NAS) interfaces clearly. During a vendor review last year, our security team couldn't locate the N14 interface between AMF instances in anyone's diagrams. We found it by reading the configuration files because nobody had documented the handover security context transfer between AMFs serving the same slice.
Get the Full Details
Common Mistakes That Wreck These Presentations
The biggest issue is treating network slicing as a software feature rather than an infrastructure dependency. Slices require dedicated RAN configuration, core function instances, and transport network settings. If your presentation doesn't address RAN slicing security — specifically how the gNB enforces slice-specific policies through the RRC layer — you're missing a critical attack surface. The gNB can be tricked into assigning a UE to the wrong slice through malformed registration requests. That's a real vulnerability in early 5G releases. Another frequent error is conflating VPN security with slice security. A VPN tunnel protects data in transit. A network slice defines compute, storage, and networking resources for a specific service type. They serve different purposes. I worked with a team that deployed IPsec tunnels between slices and called it isolation. When the tunnel implementation had a buffer overflow, both slices were compromised simultaneously because they shared the same hardened gateway appliance. True isolation would have contained the breach to a single slice. Slide count matters less than coverage. I've seen 40-slide decks that repeat the same concept three different ways and still miss slice-specific key management. I've also seen 12-slide decks that are immediately useful to a security engineer. Aim for the latter. Each slide should answer one question: what is the threat, what function mitigates it, and what configuration proves it's active.
Where 5G Network Slice Based Security Pptx Falls Short
A PowerPoint cannot replace actual security validation. Presentations describe intent. They don't prove enforcement. After building dozens of these decks, I stopped relying on them as proof of compliance. Instead, I pair every presentation with a live demonstration using a testbed — even a small one with two instantiated slices and a controlled attack simulation. Show the cross-slice traffic filter blocking an illegal packet. Demonstrate the slice-specific authentication rejecting a credential meant for another slice. That takes fifteen minutes and is worth more than fifty well-designed slides. There's also the documentation drift problem. Your network slice architecture changes monthly as new services get onboarded. A static PowerPoint becomes inaccurate within weeks unless someone maintains it. I implemented a habit of version-stamping every deck and linking it to the current NFV orchestrator export. When the orchestrator changes, the deck flags that discrepancy during review. It costs maybe twenty minutes per iteration but prevents the embarrassment of presenting outdated architecture to stakeholders. One more practical note about the download and distribution side. People often ask where to find a 5G Network Slice Based Security Pptx template. The honest answer is that most freely available templates are too generic to be useful. They cover 5G security broadly without addressing slice-specific concerns. The ones that do focus on slicing tend to be academic papers dressed up as presentations — heavy on theory, light on deployment reality. Building your own from the structure I described above usually takes less time than adapting someone else's incomplete template. Start with the 3GPP reference, map threats to functions, add your topology, and fill in the configuration proof. That process produces something that actually survives a technical review.
If you need a starting point before customizing, grab the 3GPP TS 33.501 specification and TS 28.531 for management and monitoring. Those two documents contain everything you need to populate accurate slides. Everything else is formatting and emphasis decisions.