A Software Engineering Approach To Mathematical Problem Solving
Verma
2026-07-19
Decomposing Proof Problems Like Production Code
I spent three weeks debugging a single number theory problem last semester. The issue wasn't the math — it was my approach. I kept writing proofs linearly, top to bottom, assuming each step would obviously lead to the next. It didn't. What fixed it was treating the problem like a software architecture challenge: define the types, write the test cases (boundary conditions), then implement the proof as a series of small verified functions rather than one monolithic argument.
This is what an A Software Engineering Approach To Mathematical Problem Solving actually looks like in practice.
Why the Conventional Method Fails Under Pressure
Most students learn to solve problems by reading the question, thinking for a while, and then writing a continuous narrative from axioms to conclusion. This works fine for homework. It collapses completely when problems involve multiple interacting constraints, recursive structures, or when you're working against a clock. The cognitive load of holding the entire proof in working memory at once is far higher than most people account for.
In software engineering terms, you're trying to run the entire program in your head before typing a single line. Of course it crashes. The alternative is incremental development: verify each component independently before composing them.
The Four-Phase Pipeline
Phase one is specification. Before touching any technique or identity, write down exactly what you're trying to prove in formal notation. Define all variables. State the domain. This sounds obvious until you've spent twenty minutes proving a lemma that isn't actually needed because you never pinned down what "needed" meant. I once wasted an entire afternoon on a combinatorics problem because my initial specification didn't include a constraint that the partition must be non-decreasing. The problem statement implied it. My proof didn't catch it. The workaround was to write a brute-force verification script in Python that enumerated all valid partitions up to n=20, compared them against my formula, and flagged the discrepancy immediately. A single unit test, ten lines of code, saved three hours of frustration.
Phase two is decomposition. Break the problem into subgoals. In software terms these are your functions. Each subgoal should have a clear input and output. In mathematics, this means identifying intermediate claims you need to establish. The key insight here is that decomposition isn't just organizational — it's strategic. The way you split a problem determines whether the subgoals become trivial or remain hard.
For recursive problems, the decomposition maps directly to induction. The base case is your base case. The inductive step is your recursive function call. The difference from the usual textbook treatment is that you write the inductive claim first as a standalone proposition, prove it in isolation, and only then assemble the full argument. This catches errors in the inductive hypothesis before they propagate.
Phase three is implementation. This is where you write the proof. But you write it the way you'd write a module: one verified piece at a time. Establish a lemma. Verify it with a concrete example if needed. Move to the next. Don't backtrack through earlier sections unless the new step actually requires it.
Here's a counter-intuitive detail that most students miss: the order in which you write the proof sections often differs from the order they should appear in the final version. I found this out the hard way with an analysis problem involving uniform convergence. I wrote the epsilon-delta estimates first, got stuck for an hour, and nearly abandoned the whole approach. Then I reordered the sections — put the convergence argument before the estimates — and the estimates became straightforward algebra. The proof itself didn't change. The mental path through it did. Writing proofs in dependency order rather than narrative order is one of those things that feels useless until it saves you.
Phase four is testing and review. Read your proof forward as if you're a peer reviewer who knows nothing about the problem. Every claim should follow from the previous one without requiring the reader to fill in gaps. If you find yourself writing "it is easy to see that" more than once, that's a code smell. Either the step genuinely requires justification, or you haven't fully worked it out yourself.
Edge Cases Where This Approach Breaks Down
It doesn't work for everything. Problems that require a single elegant insight — a clever substitution, a symmetry argument, a moment of pattern recognition — resist decomposition because the insight *is* the solution. You can't write a function for a heuristic that you haven't discovered yet. I ran into this with a geometry problem that boiled down to recognizing a hidden cyclic quadrilateral. No amount of modular decomposition helped until I sketched the figure differently. The software engineering framework is powerful but narrow. It excels at structural problems — proofs by induction, construction problems, optimization with constraints, algorithm analysis. It struggles with insight-driven problems where the breakthrough is non-compositional.
When that happens, switch tactics. Draw a diagram. Try small cases. Look for analogies. The pipeline approach is a default mode, not a universal one.
Practical Implementation: A Concrete Example
Let me walk through a specific problem to show how this actually plays out. Consider proving that for all positive integers n, the sum 1/1² + 1/2² + 1/3² + ... + 1/n² is strictly less than 2.
Specification: Prove S(n) < 2 for all n 1, where S(n) = (k=1 to n) 1/k². Domain: positive integers. Target bound: 2. Tightness: we know the infinite sum converges to ²/6 1.645, so 2 is a loose bound. That means a crude comparison test should work.
Decomposition: The main subgoal is finding a telescoping upper bound. We need to compare 1/k² to something that telescopes. The standard comparison is 1/k² < 1/(k(k-1)) for k 2, which equals 1/(k-1) - 1/k. The base case S(1) = 1 < 2 is immediate. The inductive step reduces to showing the telescoping sum stays below 1 for the tail.
Implementation: Write the base case. Handle the tail separately from k=2 to n. Apply the inequality. Sum the telescoping series. Combine. The result is S(n) < 1 + (1 - 1/n) = 2 - 1/n < 2. Done.
Testing: Check n=1. Check n=2. Both satisfy the strict inequality. The argument holds for all n because 1/n > 0. No gaps.
What took me five minutes this time took me forty-five minutes the first time because I tried to construct a tighter bound instead of accepting the loose one. The decomposition phase should include a brief note about bound selection strategy: loose bounds simplify the algebra. Tight bounds complicate it. Start loose.
The Tooling You Should Actually Use
You don't need special software. A text editor and a notebook are sufficient. But there are a few tools that make the pipeline noticeably faster.
For verification, write small scripts that check your formulas against computed values. Python with sympy handles symbolic verification cleanly. For a proof involving a closed form, compute the first ten terms numerically and compare them to your formula. If they match, you've caught specification errors early. If they don't, you save yourself from building an elaborate argument on a wrong foundation.
For decomposition, maintain a running list of subgoals. I use a simple markdown file where each subgoal is a checkbox. Checking it off is a genuine psychological reinforcement. The file also becomes a traceable record of your reasoning path, which is invaluable when you return to a problem days later and can't remember why you made a particular choice.
For the review phase, read your proof aloud. This forces you to confront every transition. Gaps become audible. Circular reasoning becomes obvious when you hear yourself say the same thing twice in different words.
Common Pitfalls
Over-decomposition is the most frequent mistake. Splitting a problem into too many subgoals creates overhead without reducing complexity. If a subgoal takes longer to prove than the original problem, you've decomposed poorly. The test is whether each subgoal is independently easier than the whole. If not, merge it back.
Under-testing is the second. Students verify the base case and move on. They skip checking edge cases, boundary conditions, and the tightness of their bounds. A proof that fails at n=0 when the domain is n1 is still wrong. Verify the domain boundaries explicitly.
The third pitfall is treating the pipeline as rigid. Real problem solving is iterative. You'll decompose, attempt an implementation, hit a wall, and need to re-decompose. That's fine. The framework is a workflow, not a protocol. Adapt it.
Gallery A Software Engineering Approach To Mathematical Problem Solving
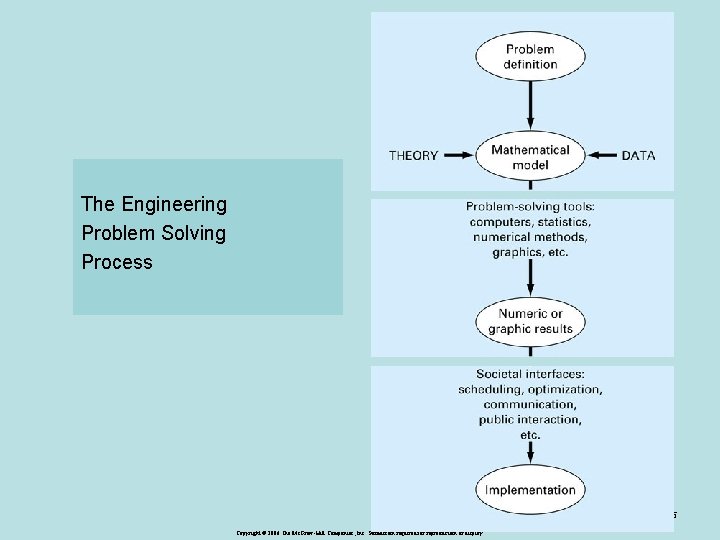
Mathematical Modeling and Engineering Problem solving Chapter 1
Mathematical Foundations of Software Engineering: A Practical Guide to Essentials | Springer ...
(PDF) The Difference of Mathematical Problem Solving Ability through the Scientific Approach and ...
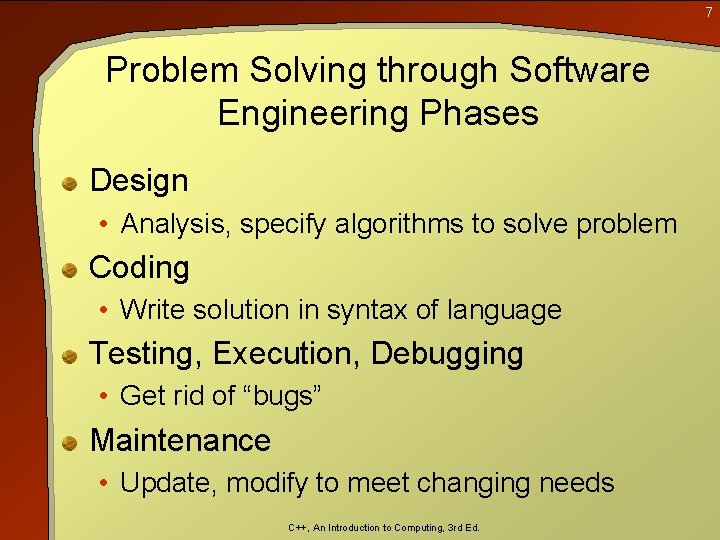
Problem Solving and Software Engineering Chapter 1 C
Soft Computing Approach for Mathematical Modeling of Engineering Problems eBook by - EPUB ...