Why This Practice Exam Actually Matters
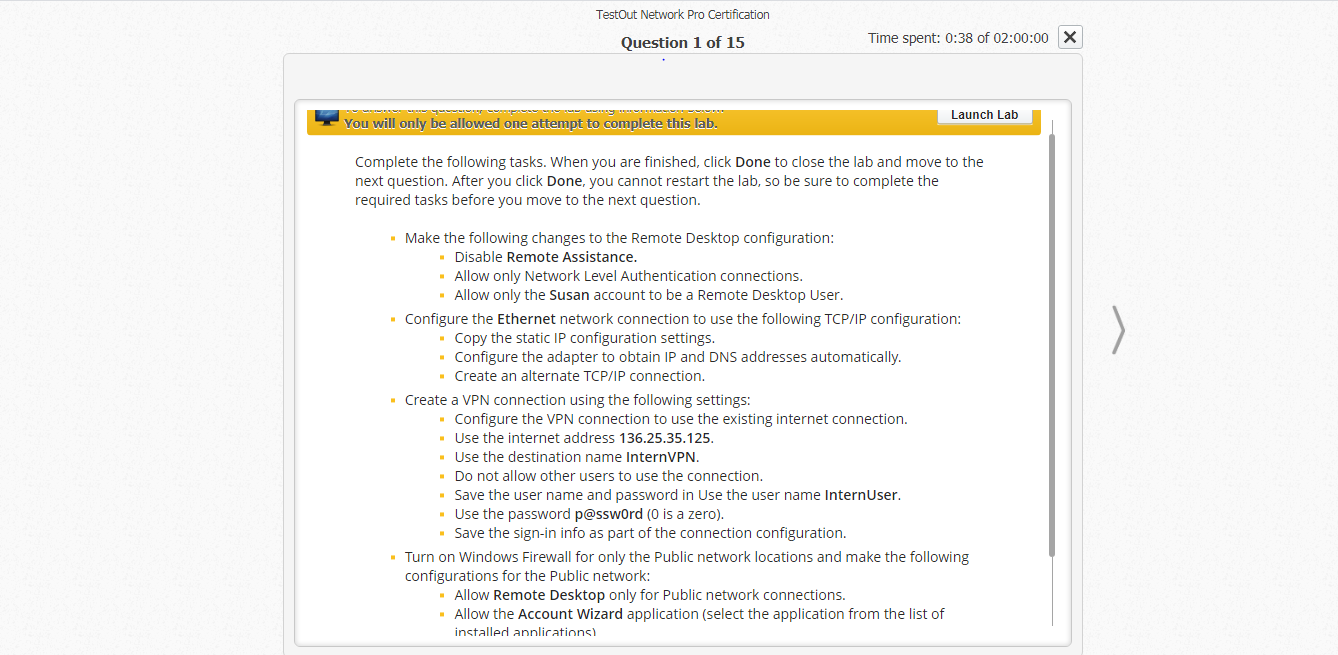
I spent four years on vendor-neutral security certifications before I learned that most people fail because they study the wrong material, not because they lack knowledge. The A3 Testout Security Pro Certification Practice Exam sits somewhere in the middle of that problem space. It is not the same as the official CompTIA Security+ exams, and it is not a dump site. It is a simulated testing environment that tries to replicate the performance-based questions and multiple-choice format that show up on the real thing. The platform itself runs in a browser and gives you a sandbox lab environment for the PBQs. You interact with firewalls, configure ACLs, analyze logs, and troubleshoot services rather than just picking A or B. That distinction matters more than most candidates realize going in.
A3 Testout Security Pro Certification Practice Exam
People ask me constantly whether this practice exam is worth the money. The honest answer depends on what you are trying to do. If your goal is to pass the CompTIA Security+ SY0-701 or the SY0-601 version, Testout's Security Pro track maps closely enough to those objectives that it covers roughly seventy to eighty percent of the material you will see. The rest comes from official practice tests and hands-on repetition. I used this platform during my last study cycle and ran into a specific edge case that most guides ignore. The PBQ scoring for the firewall configuration questions does not give partial credit for a rule that is syntactically correct but placed in the wrong position in the rule order. I lost points on a NAT and ACL ordering question because I had configured the permit rule correctly but placed it after a deny-all entry that would have caught the traffic first. The platform did not flag that in the feedback summary. It just showed my answer as wrong. I had to manually trace through the rule table to see the ordering issue, which took about eight minutes of scratching my head. After that, I started double-checking rule sequence separately from syntax before submitting any PBQ. That single experience changed how I approach these questions going forward. Testout does not walk you through the logic of why your answer is wrong in many cases. It shows the correct configuration and moves on.
What the Exam Covers
The content breakdown follows CompTIA's official objectives pretty closely. General security concepts take up about twenty-five percent. Network security covers another twenty percent. Identity management and access control sit around fifteen percent. Cryptography and PKI come in near twelve percent. Risk management and the rest round out the remainder. Within network security, expect questions on subnetting, VLANs, port protocols, Wireshark analysis, and common defense mechanisms like IDS versus IPS placement. The PBQs often ask you to select the correct port for a given service or interpret a pcap snippet. In risk management, they lean heavily on qualitative versus quantitative risk analysis, SLA definitions, and business continuity terminology. The cryptography section is where most people stall. It is not as deep as Security+ has made it seem recently, but you need to know the difference between AES modes, when to use RSA versus ECDSA, and what a certificate chain actually looks like in practice. I have seen candidates who can configure TLS properly in a lab but still fail a question about certificate revocation methods. That gap exists because the exam tests terminology and procedure, not just technical operation.
Get the Full Details
How to Use It Effectively
Do not take the full practice exam cold on day one. You will misjudge your baseline and either panic or get complacent. Run a diagnostic test first just to see where you sit. Then spend two to three weeks targeting weak domains before you attempt a full timed run. When you review your results, do not skip the PBQ explanations even if you got them right. Testout sometimes marks an answer correct for the wrong reason, or it accepts a valid alternative configuration that your actual work environment would never produce. I once selected a perfectly legal hardening method on a server config PBQ, and the system marked it correct. When I tried that same method in a real Windows Server environment, it broke the application pool because of an undocumented dependency on the default cipher suite order. The platform does not teach you real-world constraints. It teaches you what the exam wants. Here is a practical routine that works. Complete one domain at a time. Do the multiple-choice questions first, then the PBQs. Review every missed item before moving forward. Track your scores by domain, not by total percentage. A sixty percent overall score hiding a forty percent in identity management is a worse situation than a fifty-five percent score with evenly distributed weak areas. The evenly distributed one is fixable in two weeks. The first one will sink you on exam day.
For the PBQs specifically, budget about twelve minutes per question. If you finish in five, you are either rushing or you already know it by heart. Either way, verify your answer one more time before submitting. I count configuration steps aloud under my breath. It sounds ridiculous. It works because it forces you to slow down and check rule order, syntax, and scope separately instead of treating the question as a single blob of information.
Common Pitfalls
The biggest mistake people make is treating these practice questions as facts to memorize rather than scenarios to reason through. The exam changes variables constantly. You might see a question about a brute force attack, then the next one about credential stuffing, then another about session hijacking, all framed within the same security domain. If you only memorized one definition per term, you will struggle when the wording shifts slightly. Another pitfall is ignoring the negative phrasing. Questions like "which of the following is NOT recommended" appear frequently, and candidates lose points by reading past the word NOT and selecting the plausible answer. I highlight or mentally flag those words every time I encounter one. It adds two seconds per question and saves me from careless errors. There is also the issue of answer choice similarity. Testout and the official exams both use choices that look identical but differ by one key term. Selecting "non-repudiation" when the scenario clearly describes "integrity" is a classic trap. Non-repudiation requires a digital signature or certificate that binds an action to a specific identity. Integrity just means the data has not changed. They are related but not interchangeable, and the exam rewards people who know the difference.
Limitations of This Practice Exam
The platform has real weaknesses. The PBQ lab environment does not include every tool you might need for a real-world scenario. You will not find advanced SIEM consoles or enterprise identity federations here. It stays within the CompTIA scope, which means it is useful for certification but incomplete for job readiness. If you want production-level experience, you need additional hands-on labs like TryHackMe, PentesterLab, or actual cloud sandbox environments. The multiple-choice questions also skew toward recall rather than analysis. Some items are straightforward definitions dressed up in scenario text. That is fine for certification prep, but it does not train you to think like someone defending an actual network. Pair this practice exam with case studies or incident response walkthroughs if you want deeper reasoning skills. Finally, the pricing model favors bundled purchases. A single exam attempt is not cheap relative to some alternatives, and retakes inside the subscription window can feel restrictive if your schedule gets interrupted. I recommend committing to a study calendar before you pay, so you do not waste access on days when you cannot focus.
What I Would Do Differently
If I were starting over, I would run through the entire A3 Testout Security Pro Certification Practice Exam once before studying anything. That baseline tells me exactly which domains to prioritize. Then I would study using official materials and supplemental hands-on labs, returning to Testout for timed mock exams in the final two weeks. I would also print out or annotate the exam objectives and check each one off manually after every practice run. Visual confirmation of coverage reduces the chance of skipping a domain entirely. The exam itself is challenging but fair. It tests whether you can apply knowledge under time pressure, not whether you can recite a textbook. Treat the practice exam as a diagnostic and rehearsal tool, not a crystal ball, and you will avoid most of the traps that catch other candidates.