Why Scanning Alone Won't Save You
I spent years running vulnerability scans and handing off PDFs that nobody read past the executive summary. The reports were technically accurate. They were also practically useless for anything beyond a compliance checkbox. What changed my approach wasn't a new tool. It was realizing that vulnerability assessment and penetration testing aren't alternatives. They serve different purposes and when you run them together properly, you get actual signal from the noise. A vulnerability assessment is automated discovery. You point a scanner at an asset, it fingerprints services, matches them against known CVE databases, and generates a list of findings with severity ratings. It's fast. It's broad. It misses context entirely. Penetration testing is manual exploitation. A human tries to chain vulnerabilities together, pivot through the network, and prove actual business impact. It's slow. It's expensive. It can't cover everything.
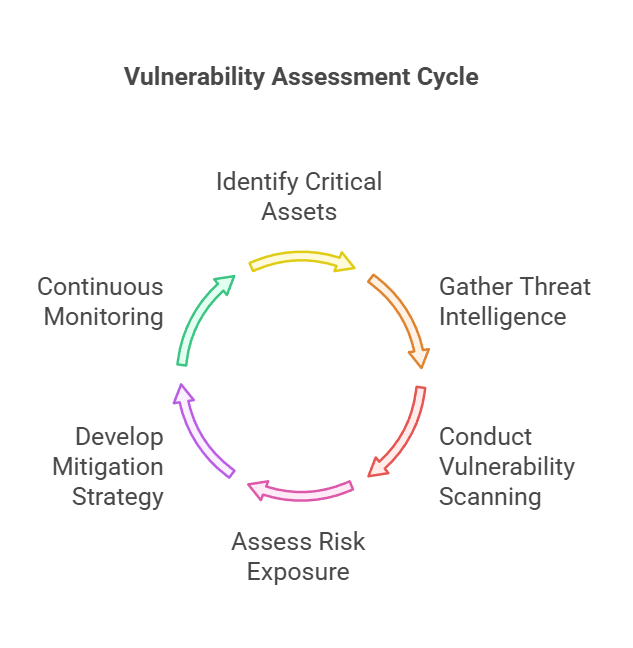
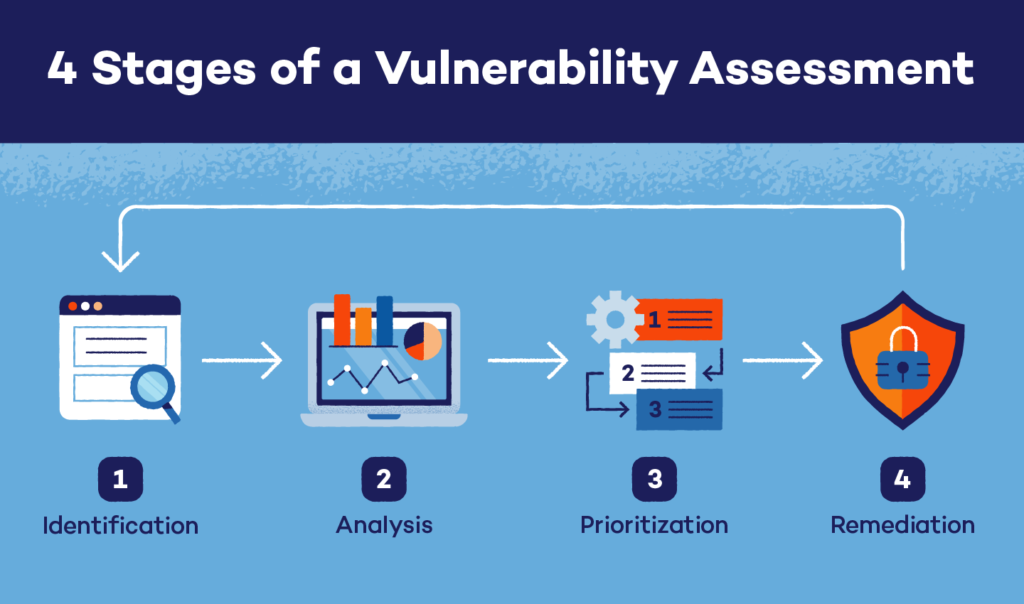
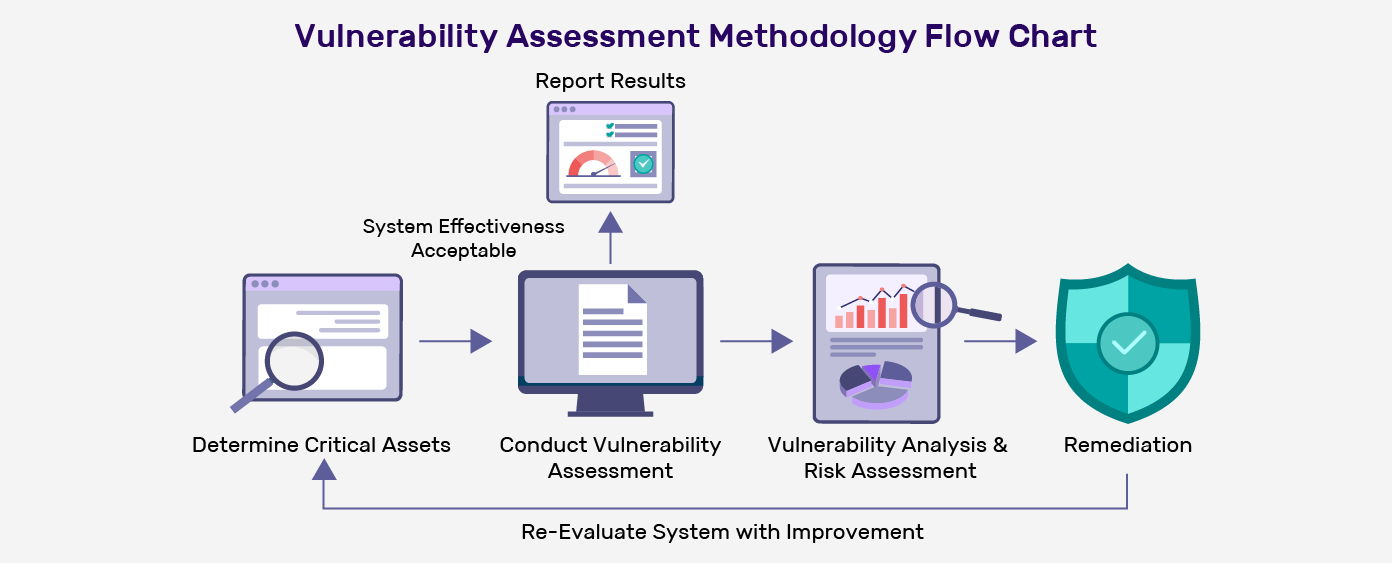
When you combine them, the assessment feeds the pentest with leads. The pentest validates whether those leads are real attack paths. The scanner then re-runs to confirm remediation. This is the loop that actually works in production environments. The workflow I use looks like this. First, run the vulnerability scan across your entire attack surface. Don't skip the external side. Most teams scan internally and forget about exposed assets. Second, take the top twenty findings and prioritize them by exploitability, not just CVSS score. A CVSS 9.0 that requires authenticated access inside a VLAN means something different than a CVSS 6.5 that's publicly exploitable with a scripted tool. Third, build your pentest scope around those prioritized findings. Fourth, document everything the pentester confirms or dismisses. Fifth, rescan after remediation to close the loop. I once worked with a team that skipped the rescan step. Their pentester found a SQL injection, they patched the application code, and moved on. Three months later, a different developer introduced the same vulnerability pattern in a new module. The scanner would've caught it. Without the rescan, nobody knew.
What Most People Get Wrong About Combining These
The biggest mistake I see is treating the combination as sequential rather than iterative. Run scan. Run pentest. Done. That's wrong. The value is in the feedback loop between the two. Another mistake is using the same scanner configuration every time. My team used Nessus for years and got comfortable with the default policies. Then we migrated to a new cloud environment and the scanner kept flagging AWS metadata service calls as high severity findings. They were false positives from the scan tool's perspective. The real issue was that the scanner was running from an internal subnet that could reach the metadata endpoint, which meant we had an unrestricted lateral movement path. The scanner reported it correctly. Nobody connected the dots between the finding and the cloud architecture. The workaround was simple but non-obvious. I configured the scanner to exclude the metadata service IP range from its credential checks and added a manual test where someone attempted to curl the metadata endpoint from every subnet. If it returned tokens, that became a confirmed finding regardless of what the scanner said. That manual validation step is the part that makes the combination work.
Get the Full Details
Practical Implementation Details
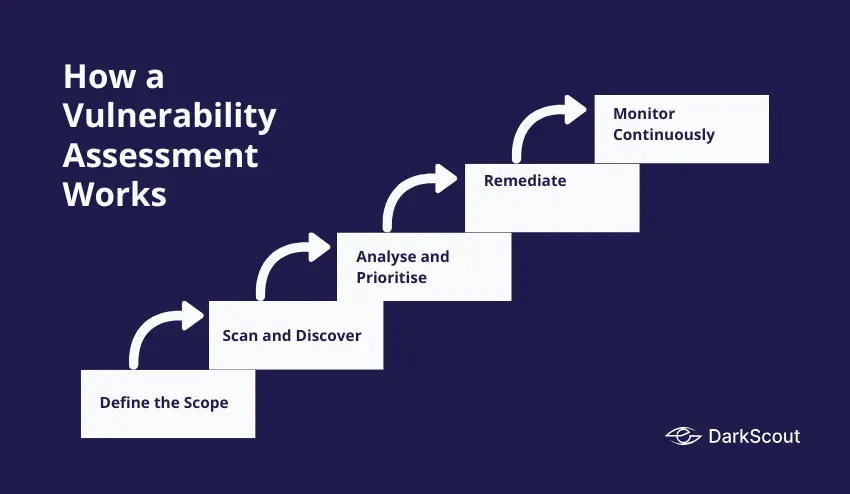
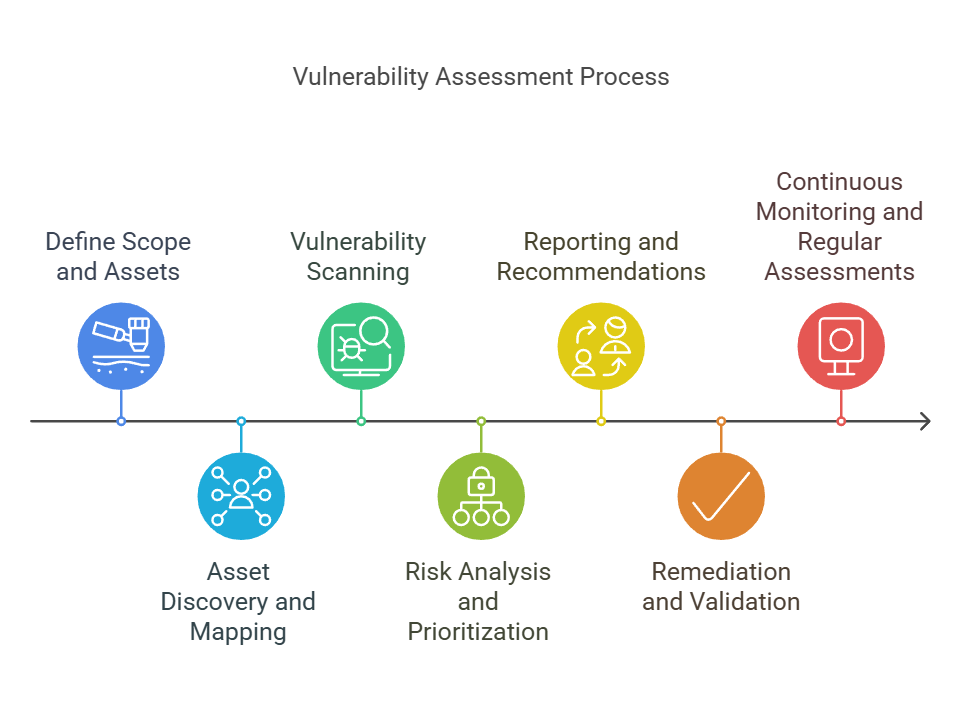
Here's what the actual process looks like on a typical engagement with a mid-size environment. You're looking at roughly two weeks from start to finish if you do it right. Days one through three go to the vulnerability assessment. I run credentialed scans where possible. Uncredentialed scans miss half the relevant findings on Windows environments. You need domain credentials or local admin access to see installed software versions, patch levels, and registry misconfigurations. If you don't have credentials, you're flying blind for about forty percent of what actually matters. Days four through five are analysis and prioritization. This is where most people fail because they hand the raw scanner output directly to the pentester. Do not do that. Filter out the duplicates. Remove the findings that apply to deprecated systems you already decommissioned. Group related vulnerabilities by asset. A server with fifty related CVEs on the same open-source library should be one ticket, not fifty.
Days six through twelve are the penetration testing phase. The pentester should have the filtered findings report in front of them. They should also have freedom to explore beyond those findings. Sometimes the most interesting path isn't in the scanner results. It's in a misconfigured API endpoint or an outdated admin panel that the scanner didn't know how to check. Days thirteen and fourteen are documentation and rescan preparation. Every confirmed finding from the pentest needs a remediation recommendation tied to the original scanner ID. This makes the rescan meaningful. If you can't map the fix back to the original vulnerability, you're just generating more noise.
Where This Approach Falls Apart
I should be honest about the limitations. This combined approach requires coordination between teams that often don't talk to each other. Security operations runs the scanners. Penetration testers are usually contractors or a separate team. If your org structure creates friction there, the feedback loop breaks and you're back to two independent activities with no integration. It also doesn't scale well for very large environments without significant tooling investment. Scanning a few hundred hosts is manageable. Scanning ten thousand hosts with credentialed access requires careful scheduling or you'll take down systems. I've seen teams accidentally restart services because the scanner queried WMI on machines that were already under load during business hours. Schedule scans during maintenance windows or use passive scanning where available. There's also a cost factor. Penetration testing at a level that meaningfully validates scanner findings isn't cheap. A proper engagement with a qualified team costs anywhere from ten to fifty thousand dollars depending on scope. The scanner license is a fraction of that. If budget is tight, at minimum run the scanner monthly and do a pentest annually. Don't skip either for extended periods.
What Actually Moves the Needle
The metric that matters isn't how many vulnerabilities you find. It's how many you confirm as exploitable and then track to remediation. I stopped caring about raw scan counts three years ago. What I track now is the ratio of confirmed exploitable paths to total findings, and the mean time to remediate confirmed paths. Our current numbers are roughly thirty percent of scanner findings confirmed as exploitable during pentests, with a mean remediation time of eighteen days for critical findings and forty-five days for high severity. Those aren't great numbers but they're measurable and we're improving them quarter over quarter. The tools I rely on most are Nessus for scanning, Burp Suite Professional for manual testing, and a simple internal dashboard that maps pentest findings back to scanner IDs so nothing falls through the cracks. The dashboard is mostly Google Sheets with conditional formatting. It's not fancy but it works because everyone on the team can access it and update it without special software.
If you're starting from scratch, begin with the scanner. Build a baseline. Then bring in a pentester who understands your stack and gives you a report that references specific scanner findings rather than generic vulnerability descriptions. That single requirement alone will separate useful engagements from the ones that sit unread on someone's desk.