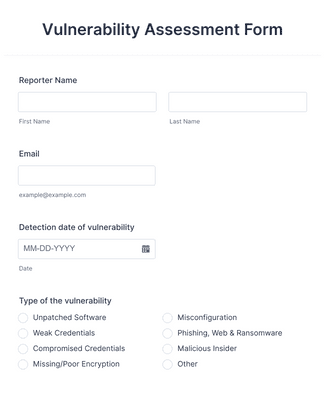
Why Your Vulnerability Assessment Template Is Probably Wrong
I've seen way too many teams ship a PDF template they downloaded from a security vendor and call it done. The problem isn't the template. The problem is treating it like a checklist you fill out once a year and pretend the risk went away. Here's how I learned this the hard way. In 2023 my team inherited a legacy environment with twelve microservices, none of them documented, running on infrastructure we didn't fully control because half the boxes were in a cloud account managed by a vendor who had left the building. We ran a vulnerability assessment using a standard And Vulnerability Assessment Template that outlined the usual categories: asset inventory, threat landscape, likelihood scoring, impact analysis, and remediation tracking. Within forty-eight hours of kicking it off I realized the template was mapping perfectly to nothing in front of me. The template assumed clear ownership boundaries between infrastructure and application, but our environment split those differently. The risk scoring grid assumed a single criticality rating per asset, but the same database server hosted both a customer-facing portal and an internal payroll system that nobody told IT about.
What Makes an And Vulnerability Assessment Template Actually Useful
A template is a skeleton. It holds the shape of a process. But the shape only matters if your data fits inside it without forcing yourself to lie about what you actually know. The core sections every real assessment needs are straightforward: Scope definition. This isn't just listing systems. It's documenting what's included, what's explicitly excluded, and why the exclusion exists. I've watched teams skip the exclusion list because they didn't want to look negligent. That's how you get a finding six months later that you already knew about and chose not to score.
Asset inventory with context. Name, owner, location, data classification, exposure level, and dependencies. The dependency piece is where most templates fail. A web server sitting alone is easy to assess. A web server that another application silently calls over an internal API without any firewall rule between them is a different problem entirely. You need a field for lateral movement paths, not just a box listing each asset in isolation. Threat identification. This section should read like a story, not a taxonomy dump. Instead of writing "external attacker" as a threat source, write "authenticated user on Partner X's network can reach port 443 through our DMZ proxy, which has no WAF configured." Specificity forces you to confront reality. Generic labels let you sleep. Vulnerability mapping. Link each threat to concrete weaknesses. CVSS scores help but they're not sufficient. A CVSS 9.8 means something when the vulnerability is exploitable remotely with no authentication. It means something completely different when the same score applies to a local privilege escalation path that requires a compromised account first. I always add a column for "prerequisite conditions met in our environment: yes/no/partial" next to the score. That column changed the outcome of three assessments last year where high-severity findings dropped to medium once I accounted for the fact that the required condition was already patched or physically impossible.
Get the Full Details

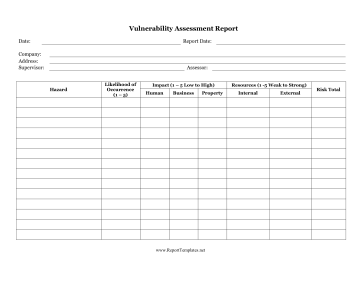
Likelihood estimation. This is where people get sloppy. Likelihood isn't probability based on external statistics alone. It's probability based on what you actually observe in your environment. If your logging shows zero exploitation attempts against that particular flaw in the last two years, and your access controls are tight, the likelihood is low regardless of what the vendor says. Conversely, if you have a known attack pattern repeating weekly in your threat intelligence feed, the likelihood is high even if the CVSS score is mediocre. I use a simple three-tier scale here: frequent, occasional, rare, with a one-line justification for each rating tied to observable evidence. No justification means you guessed, and guessed wrong. Impact analysis. Financial, operational, reputational, regulatory. Each category needs a number or a range, not a qualitative adjective. "Significant" means nothing to a budget committee. "Estimated $42,000 in lost revenue per day of downtime based on current transaction volume" means something. If you don't have revenue data, use worst-case scenario modeling with clearly stated assumptions. I typically spend two hours on impact numbers that would have taken five minutes with good data. That's a process problem, not a template problem. Risk calculation. Multiply likelihood and impact, or use a risk matrix if your organization requires it. The output is a risk score. The score itself is less important than the discussion around it. A score of 18 versus 20 doesn't change the remediation plan. A score that triggers a mandatory board-level review does. Know your thresholds before you calculate.
Remediation plan. This section needs four fields per finding: the recommended action, the owner, the target date, and the acceptance criteria. "Patch the vulnerability" is not an action. "Apply vendor security update KB-2024-0847 and verify via post-install scan showing zero vulnerable signatures" is an action. I've seen remediation plans stuck at "pending" for six months because the acceptance criteria were never defined, so nobody could prove the fix actually worked. Residual risk acceptance. Some risks won't be fully mitigated. Document who accepted the residual risk, under what conditions, and when the acceptance expires. I learned this the hard way when a vulnerability we'd accepted as residual due to compensating controls was exploited six months later after those controls were decommissioned during a routine infrastructure refresh. Nobody updated the acceptance record. Nobody even knew the controls were gone. The template had a field for this, but we treated it like paperwork.
Common Pitfalls I See Repeatedly
Pitfall one: treating the template as complete when it's just a starting point. Every environment has quirks. A SaaS-heavy stack looks different from an on-prem legacy one. A regulated healthcare environment has different compliance drivers than a fintech startup. Adapt the template, don't force-fit the environment into the template. Pitfall two: using stale data. A template populated with information from last quarter's scan is worse than no template. I've seen assessments generate false confidence because the inventory section listed thirty-two servers when only twenty-four actually existed. The other eight had been decommissioned but nobody updated the asset register. Stale data propagates through every downstream section. Make data freshness a gate criterion before you start. Pitfall three: separating technical vulnerability from organizational risk. A CVE might be technically severe but organizationally irrelevant if the vulnerable component is air-gapped and unreachable. A low-severity misconfiguration might be organizationally critical if it grants admin access to a system that holds PII. The template should force you to think about both dimensions separately, then synthesize them.
Pitfall four: no feedback loop. After remediation, verify. Run a follow-up scan. Check whether the fix introduced new issues. I always schedule a forty-eight-hour retest window after remediation because that's when new vulnerabilities surface most often. A patch can break existing functionality or expose internal endpoints that were previously hidden behind a failed service.
What This Template Won't Do For You
An And Vulnerability Assessment Template will not replace continuous monitoring. It will not catch zero-day exploits that haven't been disclosed yet. It will not fix poor coding practices. It will not substitute for security architecture reviews. It will not make your compliance auditor happy unless you actually follow through on the remediation plan. If you want something that addresses continuous risk, look into threat intelligence integration, automated scanning pipelines, and security orchestration platforms. If you want to catch architectural flaws, invest in threat modeling sessions before deployment, not after. The template is a point-in-time snapshot. It's useful precisely because it forces discipline into that snapshot, not because it claims to represent ongoing reality.
How to Actually Use One Without Going Crazy
Start small. Pick one environment, one owner, one realistic timeframe. Fill out the template completely for that scope. Then compare the output against actual incidents your team has handled in the past year. The gaps between what the template captured and what actually happened are where you learn what to adjust. Don't try to assess everything at once. A partial assessment with honest gaps is more valuable than a comprehensive one with fabricated certainty. I always mark uncertain entries with a confidence level next to them. High confidence, medium confidence, low confidence. When the confidence is low, flag it as a data gap requiring further investigation. That flag becomes the agenda for the next assessment cycle. Share the draft with the people who actually run the systems, not just the security team. The developer who wrote the authentication module will tell you in five minutes something your template might take three hours to surface. I once spent an entire afternoon documenting a vulnerability class that the lead engineer pointed out took five lines of code to fix. The template worked fine. The process of filling it out without talking to the right person was the waste.
Update it quarterly at minimum. Asset changes, configuration drift, new deployments, team turnover — any of these invalidate assumptions made during the last assessment. A template that hasn't been touched in six months is a historical document, not a risk management tool. There's no universal download link that will solve this. The best template is the one you've adapted through repeated use in your own environment. Start with something reasonable, break it, fix what broke, repeat until it hurts less to fill it out than to skip it. That's the point where you've actually built something useful.