How The Windows Kernel Actually Sits In Memory
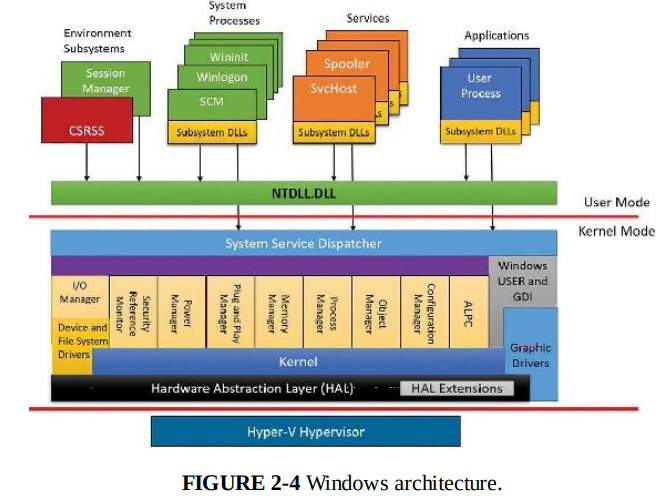
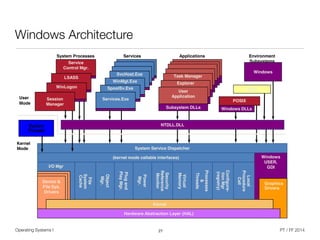
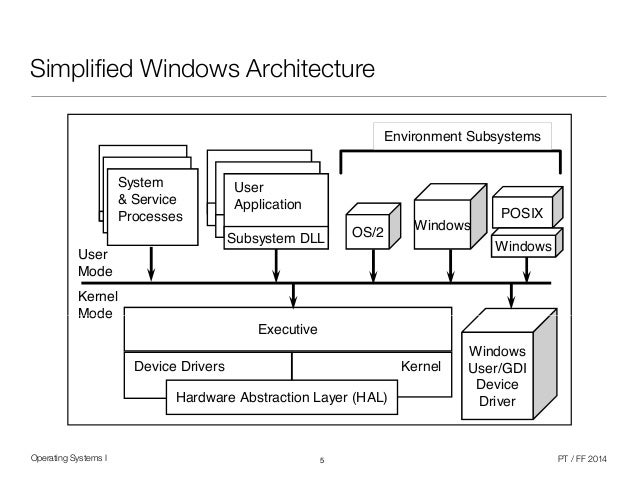
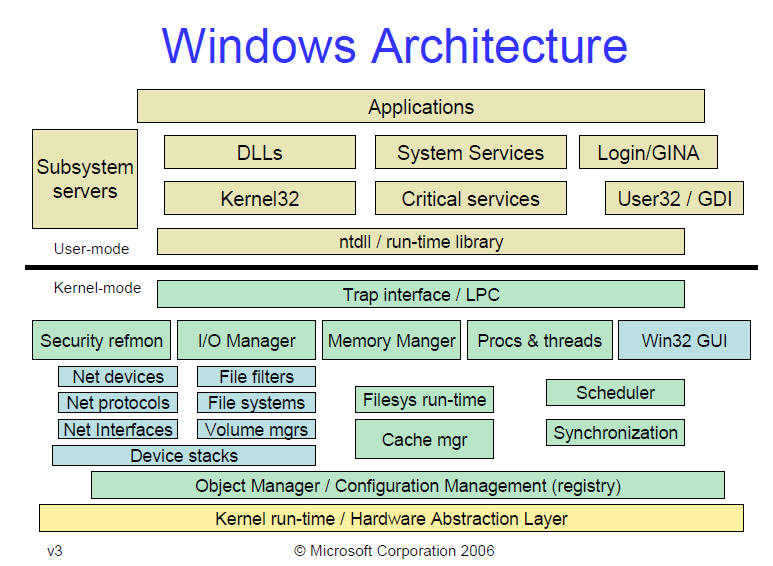
The Architecture Of Windows Operating System is a hybrid microkernel design that has evolved enough over decades that calling it anything simple is misleading. It runs on a monolithic core for performance but isolates certain services in user mode. That middle ground is what makes Windows neither fully monolithic nor truly microkernel. I spent about four years reverse-engineering kernel-mode drivers before I stopped being surprised by BSODs. The thing nobody tells you when they start studying Windows internals is that the kernel is not the system. The kernel is only one component inside a much larger subsystem stack. If you treat them as interchangeable, you will misdiagnose problems constantly. The executive is where most of the actual work happens. It includes the object manager, the registry, the security reference monitor, the process and thread managers, and the virtual memory manager. These sit between the kernel and user-mode applications. The executive handles requests that look simple on the surface but involve serious cross-boundary coordination underneath. A single CreateFile call can trigger dozens of internal function calls across multiple executive layers before the disk even gets involved.
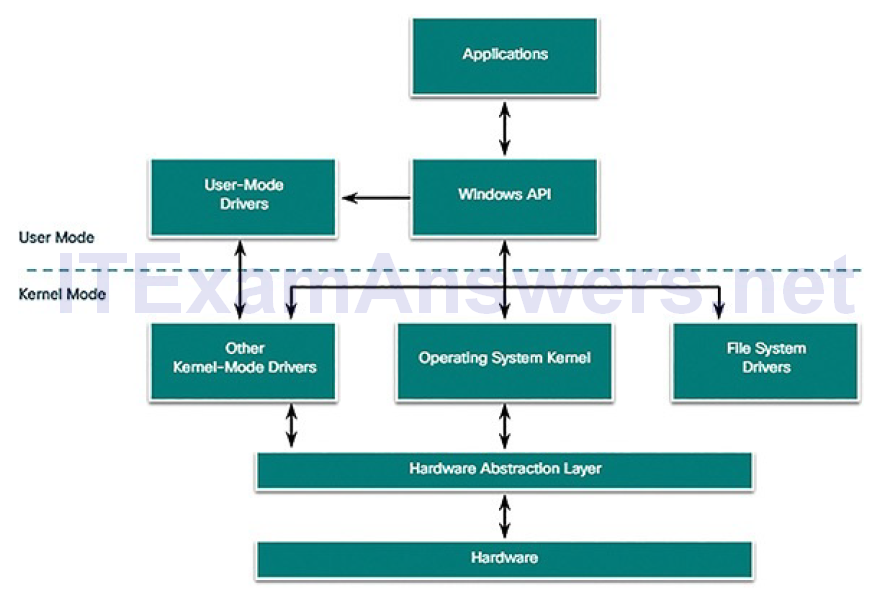
The kernel itself is smaller than people expect. It handles thread scheduling, interrupt handling, and inter-processor synchronization. It does not manage files. It does not handle networking. It does not parse the registry. Those are all executive responsibilities running at the same privilege level but in separate code modules. Hardware abstraction sits above the kernel through the HAL, or Hardware Abstraction Layer. This layer shields the kernel from raw hardware differences. The same kernel binary can run on an Intel Xeon, an AMD EPYC, and an ARM-based Surface device because the HAL translates the hardware-specific calls. This is why Windows can maintain binary compatibility across wildly different silicon while keeping the core kernel code relatively stable. Device drivers occupy their own space in this model. Kernel-mode drivers run at ring 0 alongside the executive and kernel. User-mode drivers exist too and are becoming more common, especially after Microsoft pushed for Windows Hello and certain driver categories to move out of kernel space starting with Windows 10. The security benefit is real. A buggy user-mode driver crashes the service that owns it, not the entire system. A buggy kernel-mode driver takes everything down with it.
I ran into a specific issue with a custom kernel driver on Windows 11 that caused intermittent PAGE_FAULT_IN_NONPAGED_AREA bugs. The problem was not in the driver logic itself. It was in how the driver interacted with the system's IRP (I/O Request Packet) processing under heavy memory pressure. The workaround was to implement a completion routine that checked for active memory compression before queuing the IRP. Without that check, the system would compress the driver's working set and the IRP would get paged out at the wrong moment, hitting nonpaged memory it had no business touching. This cost me about two weeks of debugging through WinDbg before I found the root cause. The subsystem layer is what lets Windows run software written for older versions. Win32 is the main one. NT subsystem handles native API calls. POSIX support existed at various points but got deprecated. These subsystems translate application requests into the internal format the executive understands. When you call MessageBox, you are going through the Win32 subsystem first, then the executive, then the kernel. Each layer adds overhead but also adds structure and security checks. Mission-critical services like the Session Manager (smss.exe), the Service Control Manager (csrss.exe), and the Local Security Authority (lsass.exe) run as user-mode processes. This is intentional. If a critical service crashes, Windows can restart it without a full reboot. The kernel maintains enough awareness of these processes to handle failures gracefully, though some services are protected and require elevated privileges to terminate or replace.
Get the Full Details
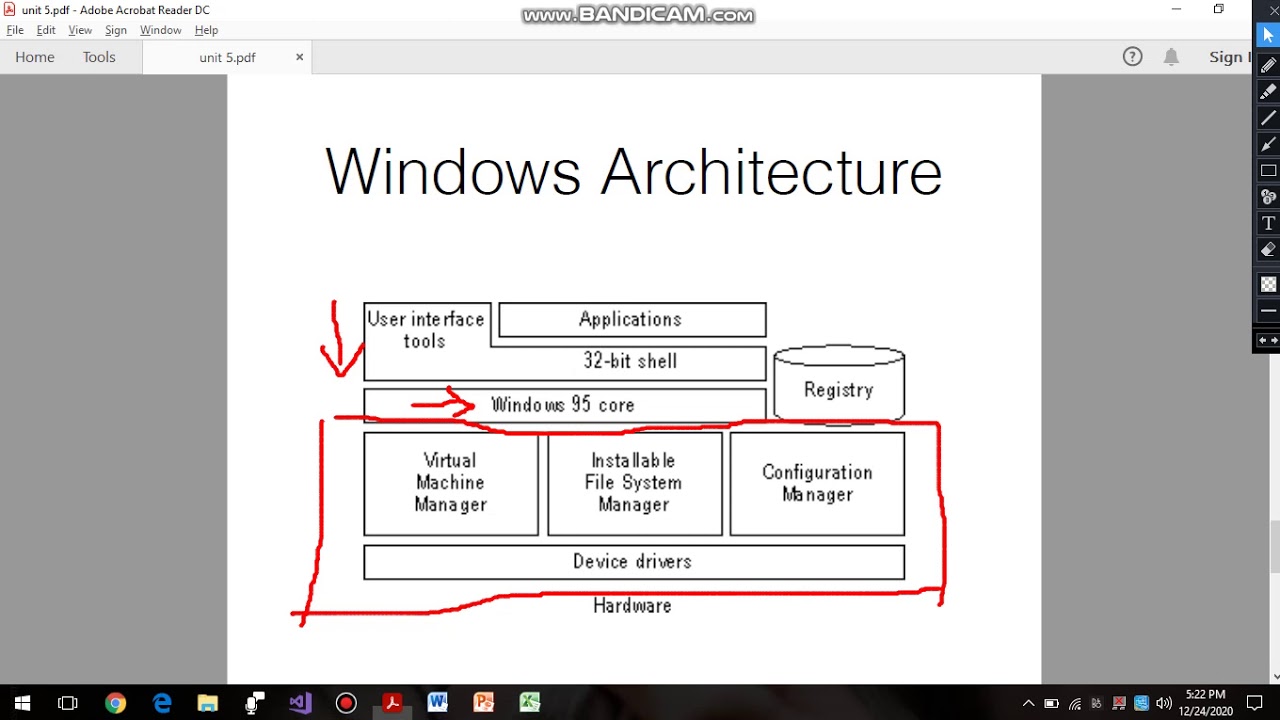
The registry is not part of the kernel. It lives in the executive as a hierarchical database managed by the registry manager component. It stores configuration data that the executive and drivers consume at runtime. Most performance issues people blame on the registry are actually about registry bloat or overly deep key hierarchies slowing down lookups. A healthy registry on a modern system with thousands of entries still responds in microseconds. Problems arise when software installs poorly and leaves orphaned keys, or when enterprise group policies create massive policy trees that every login has to process. One counter-intuitive thing about Windows architecture is that more isolation does not always mean better performance. User-mode drivers, for example, reduce crash risk but add context-switching overhead. Kernel-mode drivers are faster but riskier. The balance shifts depending on your workload. For a gaming PC, kernel-mode audio and GPU drivers make sense. For an enterprise workstation handling sensitive data, user-mode drivers reduce the attack surface significantly. Windows 10 and 11 have been moving in that direction intentionally. Another thing beginners miss is that the executive and kernel share the same address space. They are separate logical components but they do not have separate memory protection boundaries between them. This means a buffer overflow in any executive component can compromise the kernel directly. This is why secure boot, patch guard, and kernel DPC randomization exist. They make exploitation harder even though the architectural boundary between kernel and executive is porous by design.
The memory manager deserves its own attention. It handles virtual memory, physical memory, page file management, and memory-mapped files. Windows uses a demand-paging approach where pages are loaded only when first accessed. The working set manager aggressively trims idle process memory to keep free memory available for file caching. This is why a freshly booted Windows machine often uses 2 to 4 GB of RAM even when you have not launched anything. Most of that is file cache that gets released immediately when an application needs it. If you are troubleshooting memory pressure, do not assume high RAM usage is a problem. Check the Modified Page List and Standby Cache. These show how much data Windows is caching. If these are large and your applications are still performing well, the system is working as designed. If these are large and applications are stalling, you have a different problem, likely a driver holding onto pages or a memory leak in user space. Security features are layered throughout the architecture. Kernel Patch Guard prevents modification of critical kernel structures. Structured Exception Handling Overwrite Protection (SEHOP) prevents heap corruption exploits that target exception handlers. Control Flow Guard protects against code-reuse attacks. Virtualization-Based Security creates an isolated secure environment using hardware virtualization extensions. These are not bolted on as an afterthought. They are integrated into the executive and kernel at the design level.
The scheduler is another area where the architecture shows its age and its strength simultaneously. Windows uses a priority-based preemptive scheduler with dynamic priority adjustment. Base priorities range from 0 to 31, with adjustable ranges for real-time threads. The scheduler considers cache affinity, quantum expiration, and priority boost from I/O completion or window activation. It is not the most efficient scheduler in academic terms, but it is predictable and well-understood. Decades of driver authors have tuned their code around its behavior. One practical limitation of the Windows architecture is that kernel debugging requires a second machine or special boot configurations. You cannot attach a debugger to the running kernel without potentially destabilizing the system. WinDbg with kernel debugging over USB, FireWire, or network is the standard approach. This means troubleshooting kernel-level issues demands extra hardware or a virtual machine setup. There is no clean way around this if you need to inspect live kernel state. The overall Architecture Of Windows Operating System is not elegant in a textbook sense. It carries decades of backward compatibility constraints, hardware diversity requirements, and security additions layered on top of each other. It is pragmatic rather than pure. That is why it works on everything from embedded industrial controllers to server farms to consumer laptops. The design choices were driven by market requirements, not academic ideals, and that shows in both its resilience and its complexity.