Getting ClearPass up and running
The appliance ships as a virtual machine image or you can use the ISO to install it on bare metal hardware. For most deployments, the virtual deployment is the practical choice. Download the image from the Aruba Support site using your account credentials. The file is typically in OVA format for VMware or Hyper-V, or an ISO if you're deploying to a hypervisor that requires it. Size runs around 4 to 6 gigabytes depending on the version, so budget your storage accordingly. Once you have the image, import it into your hypervisor. Assign at least 8 vCPUs and 16 gigabytes of RAM minimum for anything beyond a lab environment. A single ClearPass node handling five thousand endpoints will start struggling if you under-provision the CPU. The storage allocation should be at least 100 gigabytes, though the actual usage depends heavily on logging volume. If you plan to store authentication logs for ninety days or run Endpoint Security Profiles at scale, you'll want to provision significantly more.
Aruba Clearpass Installation Guide
The initial setup wizard walks through network configuration, time synchronization, and license activation. You'll set the management IP, subnet mask, gateway, and DNS servers. Getting this right matters because ClearPass needs outbound access to Aruba's licensing servers during activation, and it also needs to reach your RADIUS clients and policy managers once it's running. I once skipped configuring DNS properly during a rush deployment and spent three hours debugging why the built-in web portal couldn't resolve internal NTP servers, which caused the appliance to fail certificate validation checks on every policy endpoint. After the wizard completes, log into the web manager using the default credentials and change them immediately. The system will prompt you to activate your license, which requires an internet connection to Aruba's licensing infrastructure unless you've arranged an offline activation. The offline route involves generating a request file on the appliance, uploading it through a browser to the Aruba support portal, and downloading the response file back to the appliance. It adds about twenty minutes to the process but it's the only option for air-gapped environments.
What ClearPass actually is
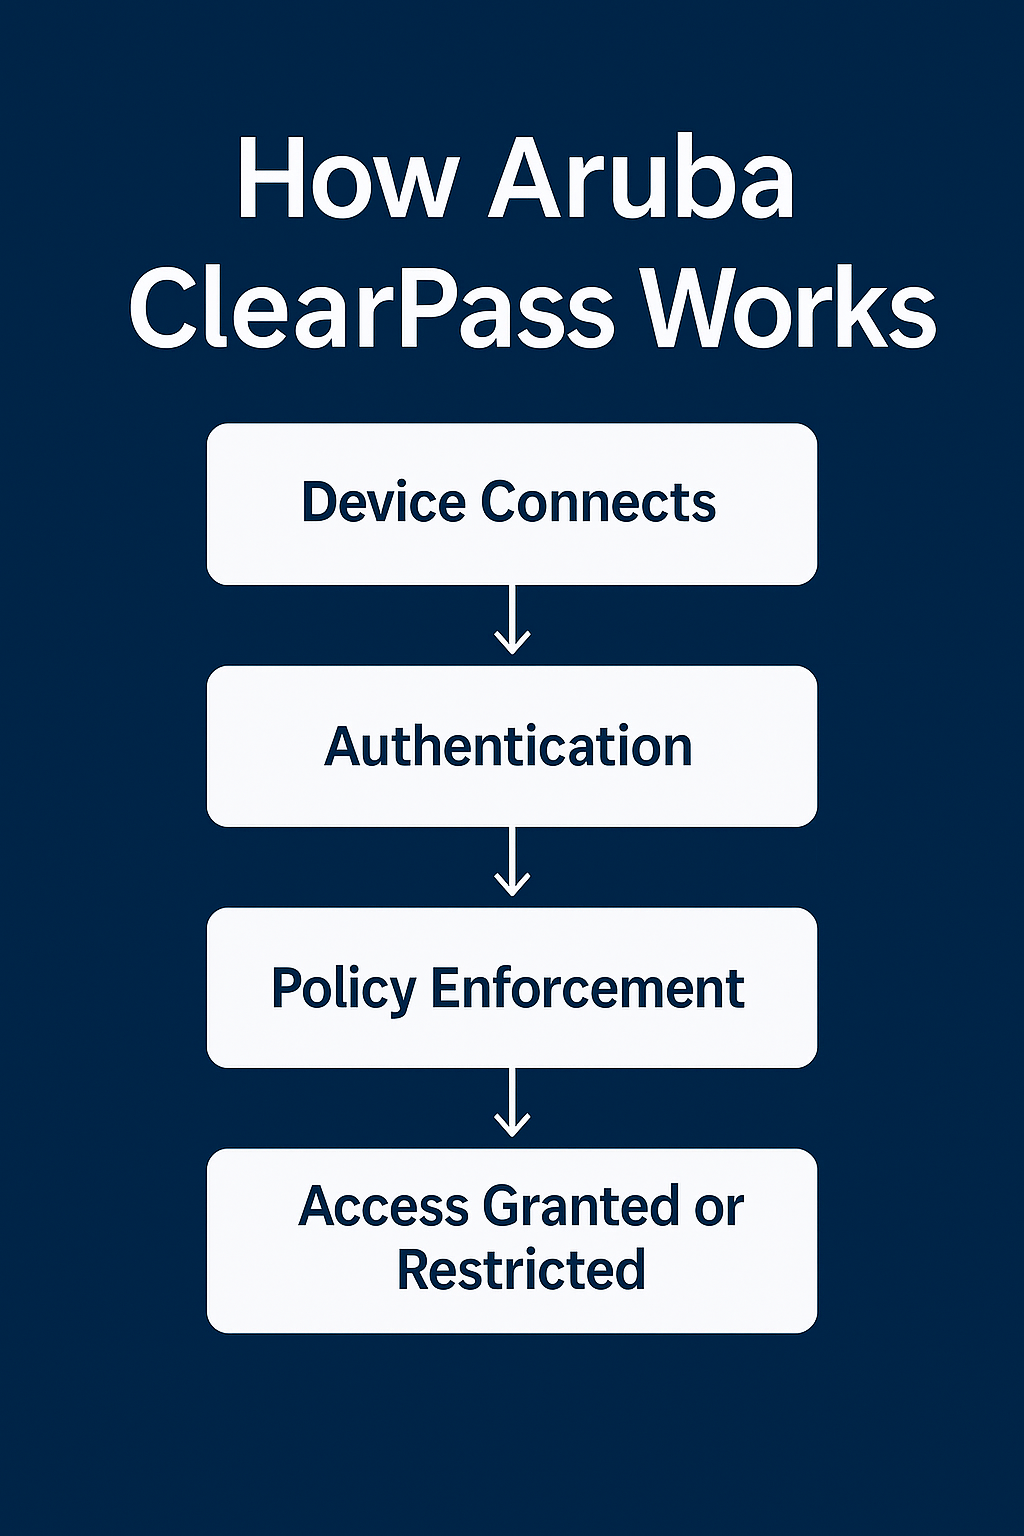
ClearPass Policy Manager is Aruba's policy enforcement platform. It handles authentication, authorization, and accounting for wired and wireless networks. It integrates with RADIUS, TACACS+, and LDAP directories, and it can enforce endpoint compliance checks through Network Access Defense. The policy engine uses a visual Policy Builder where you construct rules based on attributes like device type, user role, location, and certificate status. These rules evaluate against conditions you define and return actions such as allow, deny, or quarantine into a specific VLAN. The common misunderstanding is that ClearPass is just a RADIUS server. It's more accurate to call it a policy decision point that happens to speak RADIUS. The real differentiation comes from Policy Finder, which attempts to auto-generate policy templates based on your network devices and use cases, and from Endpoint Analytics, which fingerprints devices by their 802.1X EAP behaviors and DHCP fingerprints. This matters because without proper profiling, a visitor phone and a corporate laptop both look like generic supplicants to a basic RADIUS backend.
Get the Full Details

Post-installation configuration
After the appliance boots and licenses are active, the first thing to configure is your authentication sources. At minimum you'll connect ClearPass to an Active Directory domain or an LDAP directory. Use the built-in test function in the Administration menu to verify connectivity before proceeding. The test pulls user attributes and confirms that the service account has sufficient read permissions. If you skip this and move straight to policy configuration, you'll waste time troubleshooting policies that fail because the source itself isn't returning the attributes your rules expect. Next, register your network devices as service policies under the Services menu. Each AP, switch, or WLC becomes a NAS device entry with a shared secret. The shared secret must match what's configured on the network device exactly. I've seen deployments where the secret was correct but stored with trailing whitespace in ClearPass, causing RADIUS packets to reject the shared secret on every attempt. The debug logs show a vague "invalid credentials" message that sends you down the wrong rabbit hole for an hour. Time synchronization is another detail people don't think about until it bites them. Configure NTP to point at your internal time servers, not public ones. Certificate validation across your entire infrastructure depends on accurate time, and when ClearPass drifts even a few minutes from your controllers, you'll see intermittent authentication failures that make no sense in the logs. Set the timezone correctly too. The appliance defaults to UTC, and if you leave it there while your network devices report timestamps in local time, your incident response timeline becomes useless.
Common pitfalls
The most frequent issue I encounter is insufficient partition sizing on the internal database. ClearPass embeds a PostgreSQL database, and the default configuration assumes moderate logging volume. If you're processing ten thousand authentications per hour with full attribute logging enabled, the database partition fills up faster than you'd expect. The symptom is sporadic failures to write to the event log, which then cascades into policy evaluation slowdowns. I resolved this on a client engagement by splitting the log retention policy: keeping full event detail for seven days and compressing older entries into a summary format. That reduced daily write volume by roughly sixty percent and extended the partition lifespan from about forty days to over two hundred. Another counter-intuitive detail is how certificate enrollment works for 802.1X deployments. You might assume you need a full PKI infrastructure to deploy EAP-TLS, but ClearPass can act as its own certificate authority for smaller environments. The catch is that each endpoint still needs to trust the root certificate, which means distributing it through your MDM or login script. I managed a deployment where we skipped the distribution step because the team assumed the appliance handled it automatically. Three hundred and fifty devices failed certificate validation on day one. The fix took a morning of pushing the cert through Intune, but the real cost was the outage window and the ticket volume from confused users.
Licensing and scaling
ClearPass licensing is endpoint-based, not user-based. Every device that authenticates through the system counts toward your licensed capacity, regardless of whether it's a laptop, IP phone, printer, or IoT sensor. The license tiers are Performance, Enterprise, and Advanced, and each unlocks different feature sets. Performance includes basic RADIUS authentication and profiling. Enterprise adds Policy Finder and some reporting features. Advanced includes Device Insight and full network access defense capabilities. If you're evaluating licensing, count your endpoint population including dormant devices. Empty conference room cameras and unassigned desk phones still authenticate when they power on, and they count against your license. For high availability, Aruba supports Active/Standby clustering where one node handles traffic and the other stands ready to take over. Failover typically completes in under thirty seconds for RADIUS sessions, though existing connections drop. This is fine for authentication events but problematic if you're relying on ClearPass for RADIUS change of authorization triggers during live sessions. There's also a symmetric active-active mode that balances traffic between nodes, but it requires more careful load calculation and introduces complexity around session state synchronization. Most organizations stick with Active/Standby unless they have a demonstrated need for the extra throughput.
When ClearPass isn't the right tool
ClearPass is not designed for simple environments with fewer than two hundred endpoints and no segmentation requirements. A basic switch with port-based authentication and a shared RADIUS secret against Active Directory handles that scenario faster and with less operational overhead. ClearPass adds value when you need conditional access based on device posture, when you're managing mixed vendor network equipment, or when compliance requirements demand detailed audit trails of every authentication event. For a small office with one WiFi SSID and one switch, deploying ClearPass is like using a crane to hang a picture frame. It will work, but you'll regret the effort. The software downloads directly from the Aruba Support website at support.arubanetworks.com after you log in with your customer credentials. Keep the version current. Aruba patches security vulnerabilities in ClearPass at a regular cadence, and running an unsupported version in a production authentication environment is a liability most organizations can't afford. The installation itself is straightforward. The configuration and ongoing maintenance is where the actual work lives.