How to Build an Audit Risk Assessment Checklist That Doesn't Become Paperwork
Most audit risk assessment checklists I see are garbage. They're either copy-pasted from some generic template or they're so detailed that nobody actually uses them after the first audit. The ones that work are boring, specific to your environment, and get updated every time something goes wrong. Here's how you build one that actually does something. The process starts with risk identification, then moves into assessment, then controls testing, and finally documentation. That's the order. A lot of people reverse it—they try to document everything first or start with controls testing before they know what risks actually exist in the area they're auditing. Don't do that. Identify the risk, assess its likelihood and impact, figure out what controls should be there, test whether those controls work, and then document it all.
Audit Risk Assessment Checklist Essentials
Every checklist needs five components at minimum. First, the assertion being tested—whether it's completeness, existence, valuation, rights and obligations, or presentation and disclosure. Second, the risk level you're assigning to each assertion. Third, the specific control or procedure you'll use to address that risk. Fourth, the sample size and selection method. Fifth, the conclusion field where you actually record whether the control worked or failed. I learned this the hard way during a revenue recognition audit at a manufacturing company. The client had shifted from periodic billing to milestone-based billing halfway through the fiscal year, but the auditor who did the prior year's work had just carried forward the old checklist items verbatim. Every single line item referenced periodic billing procedures. None of them addressed milestone billing at all. We ended up missing a cutoff error that inflated revenue by about 8 percent for that year. After that, I started requiring a formal change narrative every time I pulled a prior-year checklist. If anything in the business model, process flow, or system changed since the last audit, the old checklist is useless regardless of how good it looked before. Here's something most people don't think about when they're building these lists: materiality thresholds should cascade through your checklist, not sit at the top level. Set an overall materiality for the financial statements as a whole, then set performance materiality at roughly 75 percent of that, and then assign specific materiality to each major account or transaction cycle. If you're auditing accounts receivable and the overall materiality is 5 million while accounts receivable is 12 million, your specific materiality for that cycle might be around 900 thousand to 1.2 million depending on risk. This determines your sample sizes. A higher specific materiality means smaller samples, which saves time but increases detection risk. You need to document that tradeoff explicitly in your working papers.
Another counter-intuitive thing—higher risk doesn't always mean more testing. Sometimes it means different testing. When you're dealing with management override risk or complex estimates, pulling a bigger sample of transaction-level tests often misses the actual problem. The risk here is structural, not statistical. In those situations, I tend to do deeper procedural work on the assumptions behind the estimate rather than testing a larger number of individual entries. It's slower per hour but catches issues that volume sampling will never find. The PCAOB has made this clear in their inspection observations for the last several years, and firms that ignore it keep getting called out. The biggest bottleneck in this whole process is usually not the checklist itself. It's the transition from risk assessment to the actual audit program. You spend two or three days identifying risks and designing responses, then you realize the response procedures are too vague to execute. Things like "evaluate the adequacy of controls surrounding X" sound professional until you have to tell a junior auditor exactly what steps to perform. Every checklist item should be readable by someone who has never seen this client before and should describe the exact procedure, not just the objective. "Inspect three samples and verify cutoff dates match shipping documents" is an audit step. "Evaluate cutoff procedures" is not. Sample size calculation deserves its own section because this is where a lot of checklists fail in practice. Attribute sampling for controls testing uses a formula based on tolerable rate, expected population deviation rate, and desired confidence level. If you're using monetary unit sampling for substantive testing, you need the population book value, tolerable misstatement, and expected misstatement. Most people I work with just grab a table from Auditing Standard 2301 or use the default values in their audit software and move on. That works until the population has unusual characteristics like skewed distributions or known anomalies. When that happens, you adjust the sample size upward or switch to stratified sampling. Document the adjustment reason in the checklist notes.
Get the Full Details
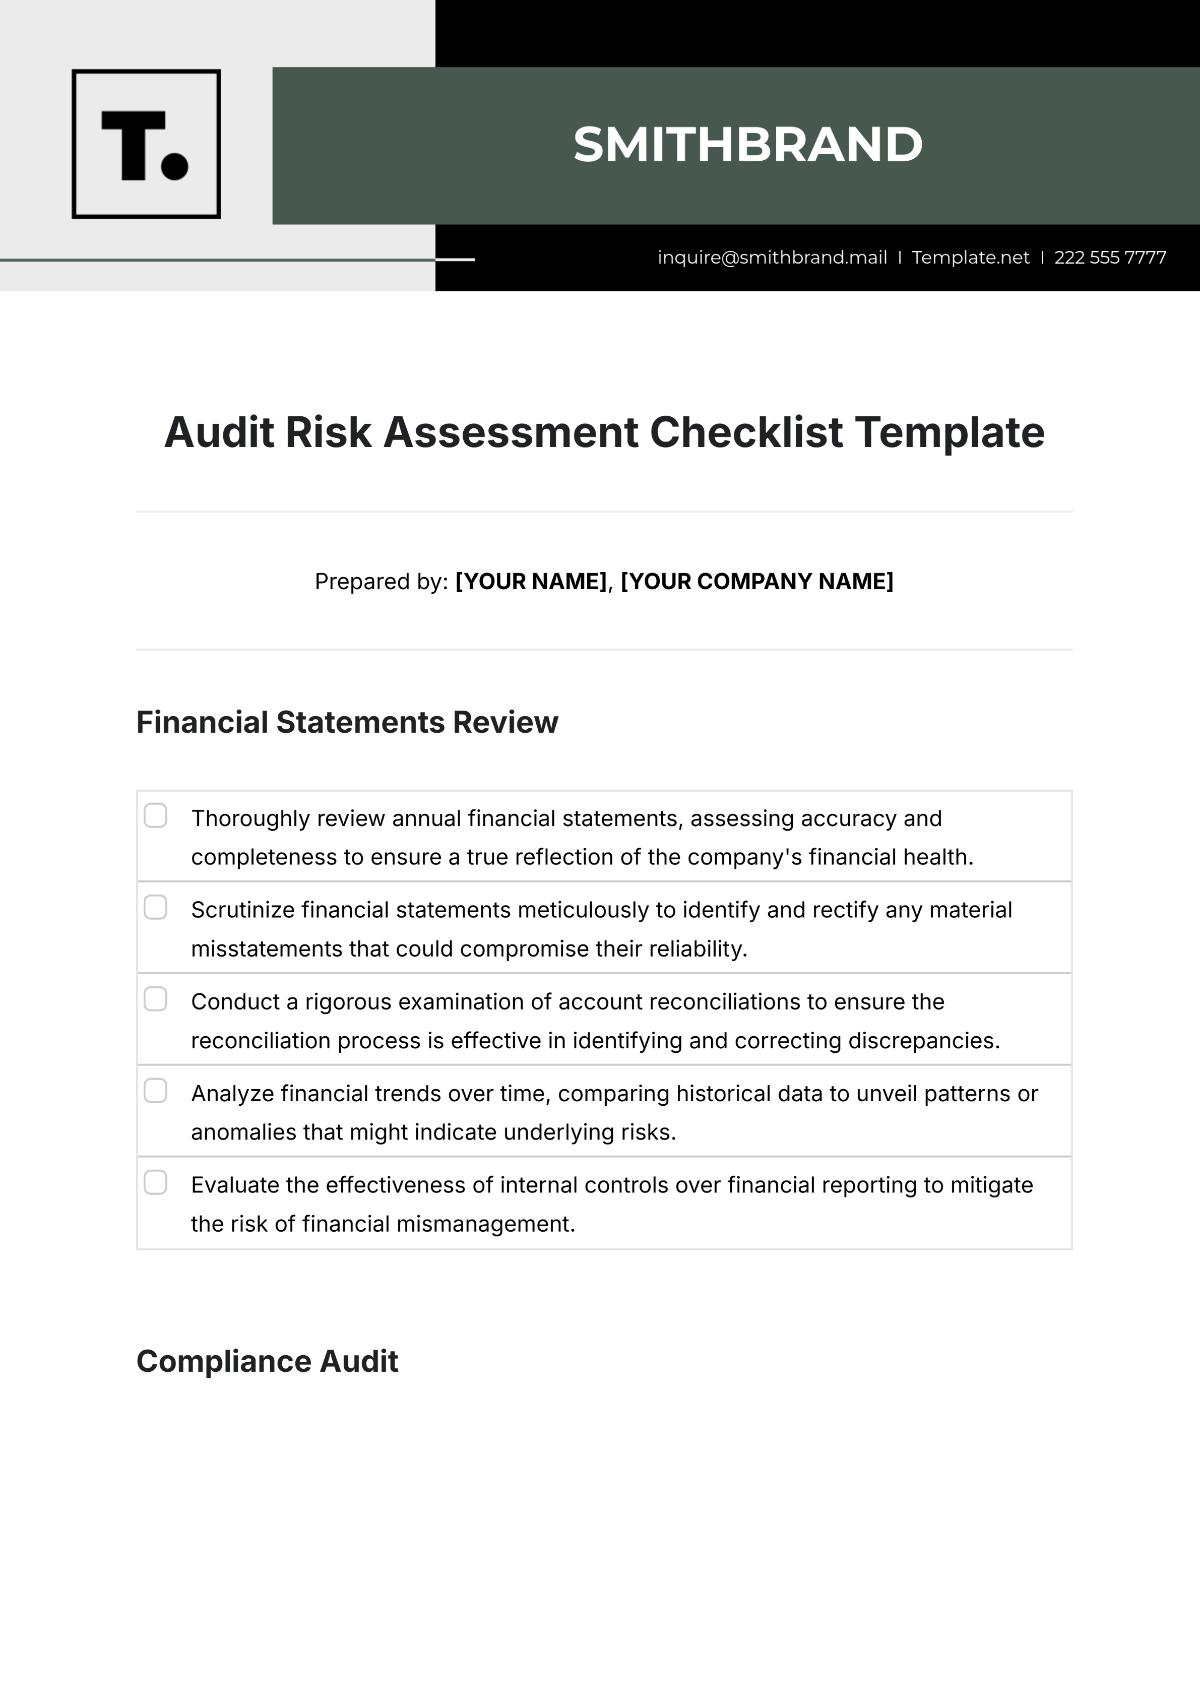
There are honest limitations to this approach that nobody likes to admit. A checklist cannot replace professional skepticism. If you go through the motions of checking every box without actually questioning whether the answers make sense, you've created a compliance exercise, not an audit. I've seen this repeatedly in engagements where the team marked every control as operating effectively because the design was documented, even though the evidence showed the control was either bypassed or applied inconsistently. The checklist said effective. Reality said otherwise. The second problem is that checklists create a false sense of completeness. They suggest the work is done when you've only covered what you anticipated, not what might actually be wrong. That's why I always add a wildcard section at the end of every checklist—an open field for risks or findings that weren't on the original list. It forces the team to acknowledge what they didn't plan for. For the technical side, I recommend building your checklist in a structured format rather than a freeform document. Excel works if you're careful about it, but a proper audit management tool with version control and cross-referencing between risk areas saves hours during fieldwork. The checklist should link directly to your working paper index so that every risk and every test has a clear trail. When you're doing the assessment, I'd suggest running through it in this sequence: review prior year findings first, map the current process to identify changes, assess inherent risk at the assertion level, evaluate control design and implementation, test operating effectiveness if you're planning to rely on controls, determine substantive procedures based on your assessed risk, calculate sample sizes, perform the procedures, document results, and then summarize exceptions. Each step should feed directly into the next. If you finish step six and realize you haven't completed step four, that gap will show up during inspection every time. The downloadable version of this checklist covers the standard cycles—revenue, purchasing, payroll, fixed assets, and financial reporting—with assertion-level risk matrices pre-populated for typical scenarios. It includes fields for inherent risk, control risk, and detection risk calculations along with sample size recommendations based on AICPA and PCAOB standards. The wildcard section and the change narrative requirement are built in. You can find it through your firm's document management system or request a copy from the quality assurance team. It's not going to make your job easy, but it will at least make sure you're not auditing the last client's risks instead of this client's.