How to actually build something useful instead of another generic spreadsheet
Most people approach audit risk assessment by grabbing a template from some consulting firm's website and filling in the boxes. It looks professional. It passes most reviews. And it also misses half the real risks because the template was designed for someone else's environment. I've reviewed enough of these to know exactly where they fall apart.
The actual process starts before you touch any document. You need to understand what makes your specific audit population unique. A manufacturing company has inventory obsolescence. A SaaS business has revenue recognition timing issues. A nonprofit has grant compliance buried under three different funding streams. The template doesn't know this. You do.
I once worked with a client who had a perfectly formatted Audit Risk Assessment Template sitting in their system. Inherited it from a prior auditor. The risk ratings were all "low" across the board. When I dug into the sub-ledger activity, I found that the accounts payable team had gone through two mergers in eighteen months, vendor master files were consolidated without reconciliation, and approximately forty percent of active vendors had duplicate payment addresses. The template had nothing about vendor master integrity because nobody had thought to include it. I added a specific risk node for duplicate vendor identification with a materiality threshold tied to our quarterly payment volume. That single addition doubled the sample size for our AP testing cycle.
Using an Audit Risk Assessment Template Without Losing Your Mind
Here's what I actually use. It's not complicated but it requires discipline.
Start with the risk register. This is your list of every area where something could go wrong. Don't start with financial statement line items. Start with processes. Walk through the actual workflow from initiation to reporting. Where are the manual interventions? Where does data cross between systems? Where does judgment enter the equation? Those three things are your risk sources. Everything else is noise.
For each risk area, assign three numbers. Inherent risk, control risk, and detection risk. Inherent risk is what the danger level would be if nobody tried to prevent anything. Control risk is how well your existing safeguards actually work. Detection risk is the chance your testing misses something anyway. Most people skip detection risk or treat it as an afterthought. It shouldn't be. Detection risk is where your audit methodology lives.
The formula most people use is Audit Risk equals Inherent Risk times Control Risk times Detection Risk. That's textbook. Here's what the textbooks don't tell you: this formula assumes independence between the risk components. They're not independent. Strong controls reduce inherent risk expression. Weak detection procedures make control risk look worse than it actually is. When you see a high composite risk score, the first question isn't which risk component is driving it. It's whether the components are conflating each other.
I keep a separate column for risk drivers. These are the specific conditions that push a risk up or down. Things like key person dependency, system changes in progress, regulatory shifts, staff turnover rates. This column is usually more useful than the risk scores themselves when you're explaining your conclusions to a review partner or a audit committee.
Where templates fail and what to do instead
The biggest problem with off-the-shelf templates is that they're backward-looking. They capture risks that existed last year. Risk environments change faster than templates update. I've seen situations where a company switched ERP systems mid-year and the template still reflected the old system's control landscape. The risk assessments were technically accurate for the wrong environment.
Another failure mode is aggregation bias. When you roll individual risks up into department-level scores, the variation gets smoothed out. A department might have one critical risk and twelve minor ones. The average looks fine. The actual exposure is concentrated in that one area and that's where you'll get surprised. I always calculate both the aggregate score and the maximum individual risk score for each area. The gap between them tells you where the concentration risk sits.
Quantification helps. Instead of writing "moderate risk" you should be able to say "this risk has a estimated material impact of approximately $200,000 based on prior year error rates multiplied by current transaction volume." You don't need perfect precision. You need defensible approximation. Numbers force you to think about the actual mechanism of failure rather than settling for vague descriptors.
For detection risk specifically, tie your assessment directly to your sampling strategy. If you're assigning a high detection risk to an area, that should automatically trigger larger samples, more substantive testing, or alternative procedures. If it doesn't change your testing approach, the risk rating is decoration.
A practical workflow that takes about three hours instead of three days
First, pull the prior year's risk assessment. Not to copy it. To see what changed. Mark any new processes, removed processes, and altered controls. This takes twenty minutes.
Second, sit with the process owners. Not to interview them formally. To walk through their actual day. Ask what keeps them up at night. Ask where the manual workarounds are. Ask what broke last year and how it was fixed. This is where you find the risks that never make it into the template. Budget two hours for this.
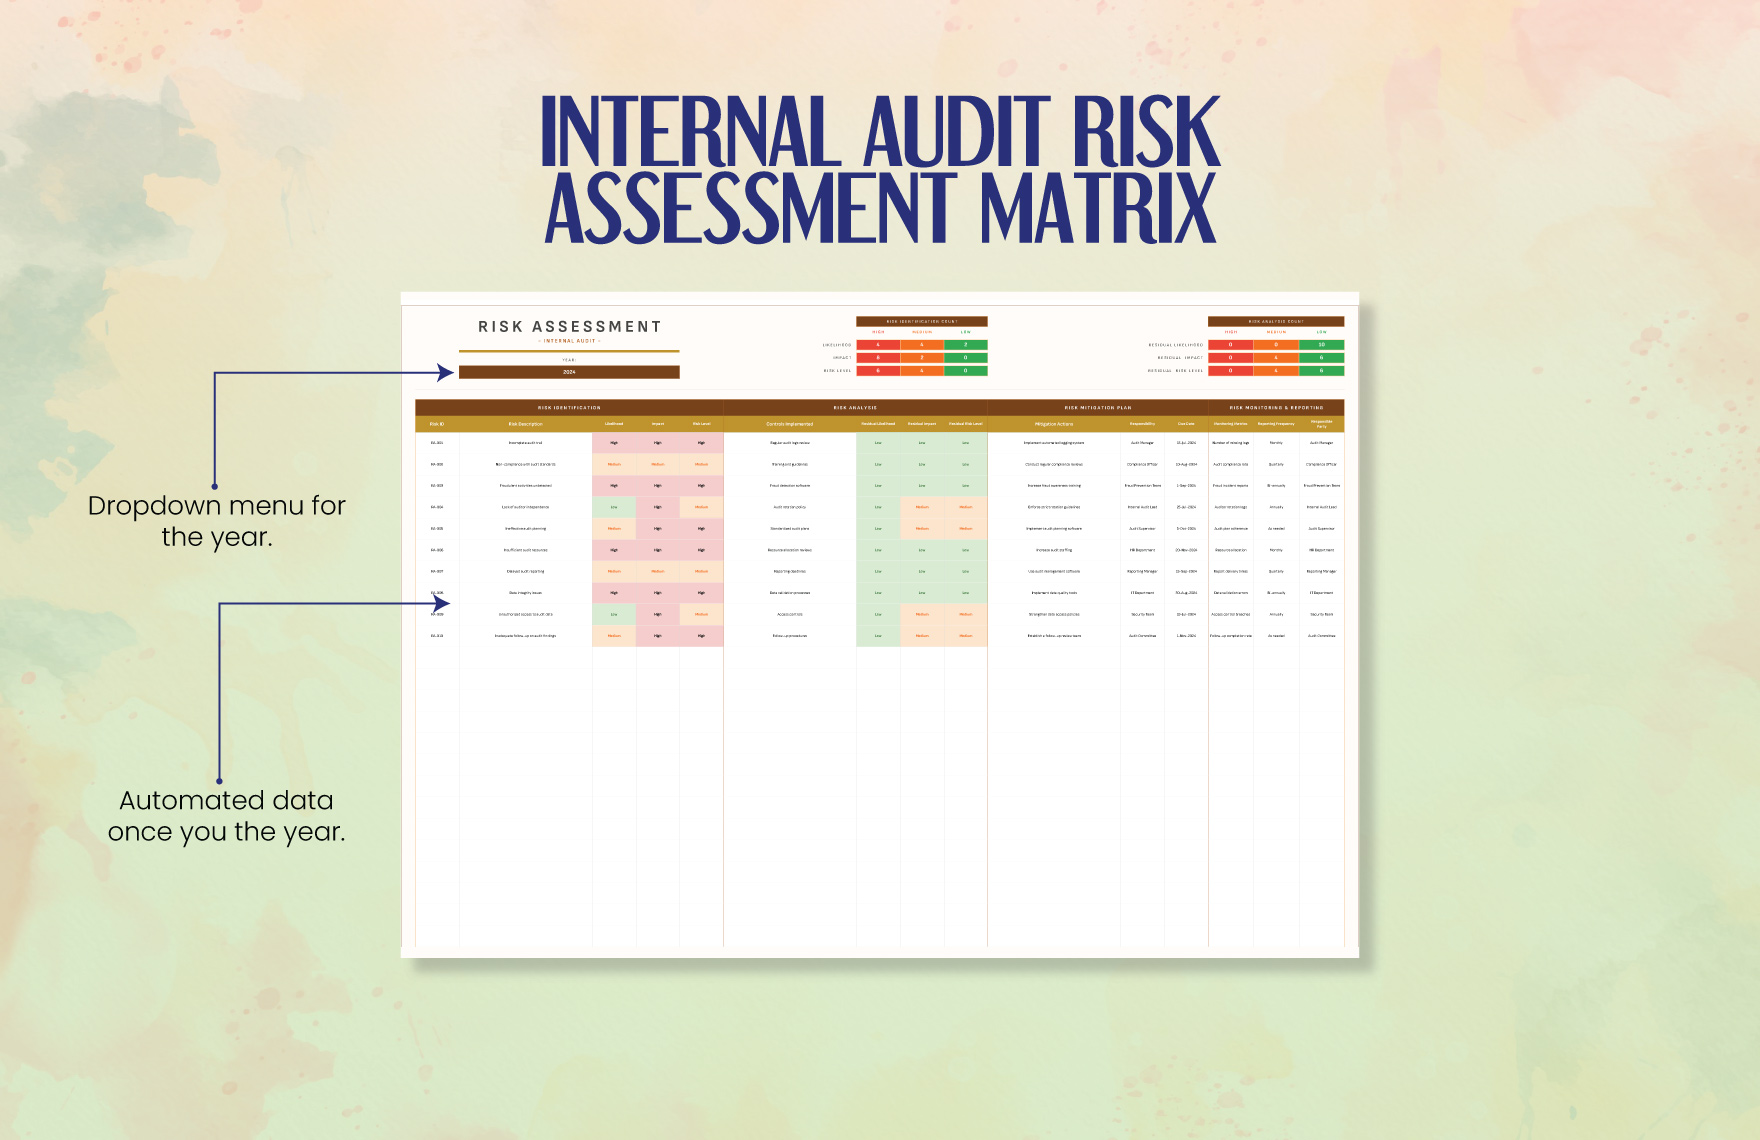
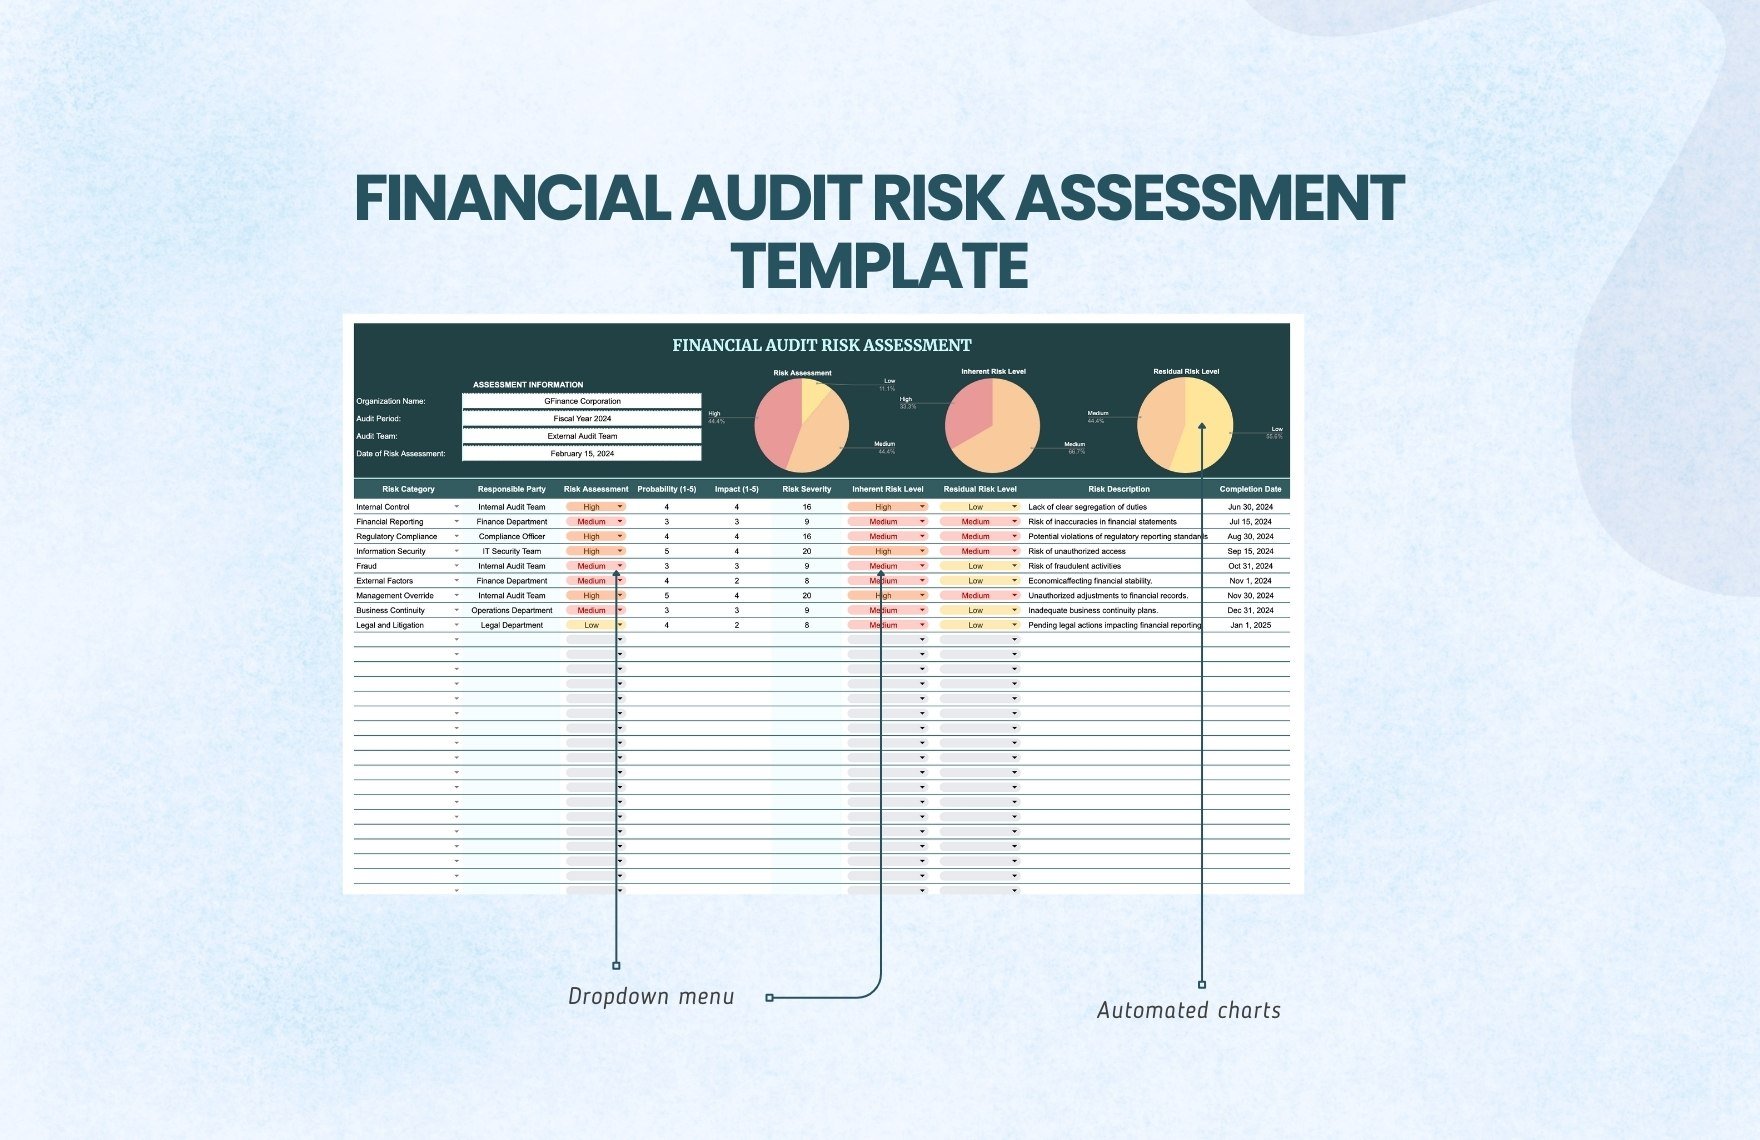
Third, populate your spreadsheet with the structured fields. Risk description, inherent risk rating, control environment assessment, detection risk rating, risk driver notes, recommended audit response, and current audit procedure alignment. That's it. Six columns. Anything beyond that is usually vanity.
Fourth, review the output for concentration patterns. Look for clusters of high inherent risk, areas where control risk is high but detection risk is also high (meaning you're not testing adequately), and any risks that depend on a single control working correctly.
I use conditional formatting to flag areas where the composite risk score exceeds a threshold I set based on materiality. Red for critical, yellow for watch, green for acceptable with monitoring. The colors aren't the point. The point is that the visual clustering helps you spot patterns during review meetings.
What to include in your actual document
A functional Audit Risk Assessment Template needs these sections. Background and scope, risk identification methodology, individual risk assessments with supporting evidence references, aggregation and concentration analysis, risk tolerance thresholds, and linkage to audit plan procedures.
The evidence references section is where most templates are weak. Every risk rating should point to something. A prior year finding. A control test result. A process documentation page. A management representation. If you can't point to why you rated something the way you did, your rating is an opinion and opinions get challenged.
Risk tolerance thresholds should be explicit. Not "we consider anything above moderate to be significant." That means nothing. Use actual numbers tied to your materiality framework. If overall materiality is $5 million, then any risk that could individually exceed $500,000 gets elevated treatment. If a control failure could cascade across multiple assertions, the threshold drops further.
The linkage to audit plan procedures is non-negotiable. Each assessed risk should map to one or more specific audit procedures. If a risk has no corresponding procedure, either the risk assessment is wrong or your audit plan is incomplete. Both are problems.
The thing nobody talks about
Risk assessment is iterative. The version you produce in November isn't the version you should be using in March. Mid-year events matter. A key controller leaves. A system goes live. A regulation changes. Your risk assessment should have a revision log that tracks changes with dates and reasons. I've seen review teams discount risk assessments because there was no evidence they'd been updated after a major event. The assessment looked thorough but stale.
Also, remember that risk assessment is a communication tool as much as it's an analytical one. Your template needs to be readable by someone who wasn't involved in the assessment process. A reviewer should be able to look at your documentation and understand both your conclusions and your reasoning without calling you on the phone. If they can't, simplify the language and add the context.