What You Actually Need to Know About Cloud Service Maps
I've spent years bouncing between AWS and Azure environments, and one of the most useful things I've found is a solid Aws And Azure Services Cheat Sheet. Not the marketing versions, but the kind that actually helps you figure out which service does what when you're in the middle of a migration at 2 AM. Most people treat these like reference documents you read once. That's not how they work. They're search tools. You open them when you need something specific, and if yours isn't organized well, you've wasted twenty minutes flipping through pages that don't help. The real value isn't in memorizing the services. It's in having a quick way to cross-reference equivalent services between the two clouds. I spent three weeks helping a team move a legacy .NET application from Azure VMs to AWS. Every time someone asked "what replaces Service Bus?", we had to look it up. If we'd had a decent cheat sheet, that would've taken five minutes instead of three weeks of back-and-forth confusion. The same goes the other way around.
Aws And Azure Services Cheat Sheet
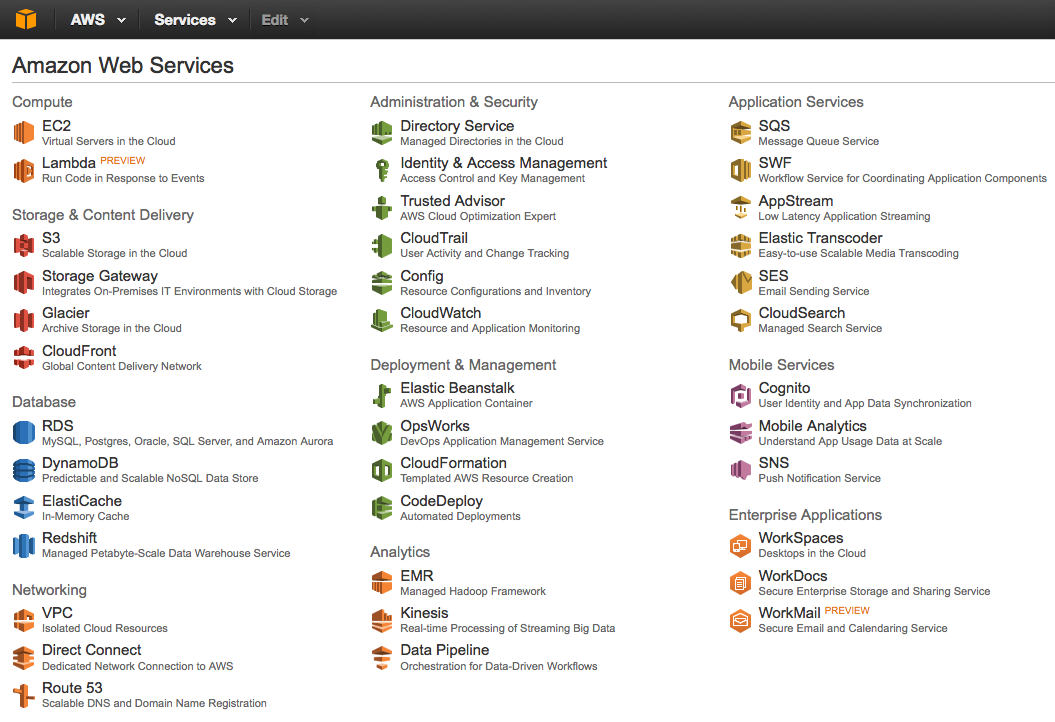
Here's how I approach building one that actually survives contact with real work. Start by listing the core categories: compute, networking, storage, databases, identity, monitoring, and serverless. Within each category, map the primary services side by side. Keep it to one page if possible. Two at most. Anything longer becomes useless because nobody reads it anymore than three screens deep. For compute, EC2 maps to Virtual Machines. Lambda maps to Functions. ECS and EKS are your container options, corresponding to Container Apps and AKS respectively. Simple enough on paper. In practice, the differences in how each handles scaling, billing granularity, and cold starts matter more than the name mapping. When I moved a high-traffic API from Azure Functions to Lambda, the billing structure alone cut our costs by 40% but required rewriting the timeout handling. The cheat sheet tells you what replaces what. It doesn't tell you what breaks when you switch. Networking is where most teams get tripped up. VPC and VNet are similar but not identical. NAT Gateway and Azure NAT Gateway exist, but the routing table behavior differs enough that you can't just assume parity. I learned this the hard way when a subnet configuration that worked perfectly in Azure threw routing loops in AWS because of how route tables propagate across availability zones. Our workaround was to audit every network security group rule individually rather than relying on the cheat sheet mapping.
Storage needs a separate section because the naming is deceptive. S3 and Blob Storage both hold objects, but the consistency model, replication options, and access tiering work differently. S3 Standard-IA has a minimum duration charge. Blob Storage's cool tier charges for read operations differently. If you're moving petabytes of data, understanding these differences before you architect matters more than knowing which service corresponds to which. I've seen teams migrate terabytes between storage tiers and get hit with $12,000 in unexpected egress fees because they treated the services as interchangeable. Databases are another category where the cheat sheet is only a starting point. RDS and Azure SQL Database are the obvious pairings, but Aurora has no direct Azure equivalent—it's closer to a PostgreSQL-compatible option mixed with some proprietary features. DynamoDB and Cosmos DB both do NoSQL, but DynamoDB's capacity modes (on-demand versus provisioned with autoscaling) require different planning than Cosmos DB's consistent throughput model. We had a team recently try to replicate a DynamoDB single-table design in Cosmos DB and discovered that the change feed feature they depended on didn't translate directly. They ended up using the AWS AppSync resolver pattern instead, which the cheat sheet won't tell you about because it's not a service-to-service mapping. Identity and access management deserves its own section even though it's often skipped. IAM in AWS and Entra ID (formerly Azure AD) in Azure handle authentication and authorization differently enough that you can't just copy policies. IAM uses resource-based policies alongside identity-based ones. Entra ID leans heavily on role-based access control tied to conditional access policies. I spent an entire sprint mapping an organization's IAM roles to equivalent Entra ID enterprise applications because the permission boundaries simply didn't align. The cheat sheet will show you the service names. It won't save you from that mess.
Get the Full Details
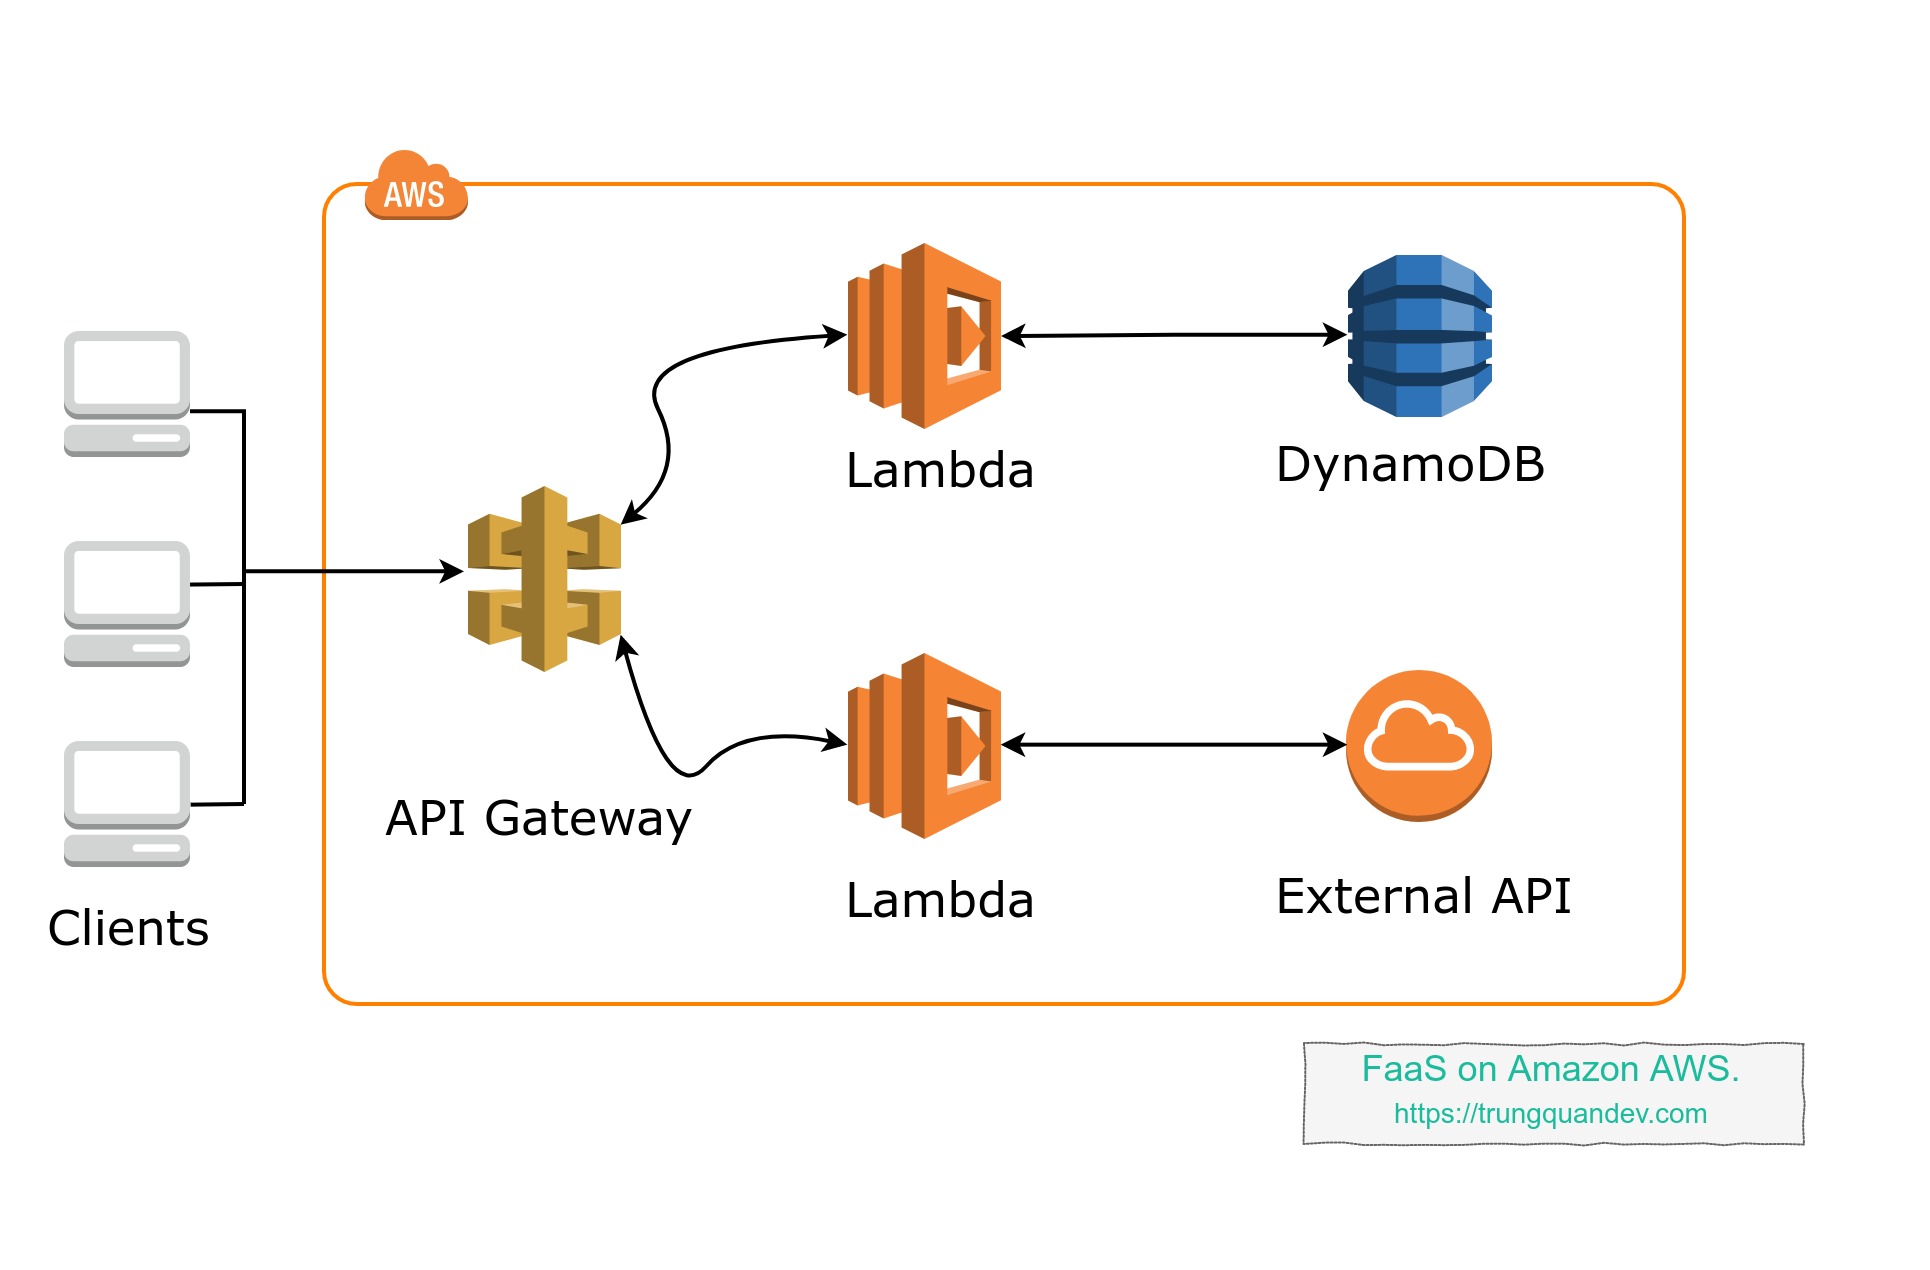
Monitoring is where the cheat sheet becomes almost mandatory. CloudWatch and Monitor are analogous, but CloudWatch Logs Insights and Log Analytics queries use different syntax. CloudWatch Alarms trigger actions through SNS, while Azure Monitor uses Action Groups. I keep a small section at the bottom of my cheat sheet for query examples—just the most common patterns. A basic metric filter, a log search with regex, an alert rule. These take twenty seconds to look up each time if you don't have them handy, and twenty seconds adds up fast when you're debugging production issues. Serverless services are the trickiest to map. API Gateway and Azure API Management aren't the same thing—APIM is an enterprise gateway with developer portal features that API Gateway doesn't offer without additional services. Step Functions and Logic Apps both handle workflows, but Step Functions integrates natively with more AWS services and Logic Apps has better prebuilt connectors for enterprise SaaS products. I had a situation where a client needed approval workflows that pulled data from Salesforce, and Logic Apps won immediately because of the native connector. The cheat sheet lists both as equivalents, but the actual decision depends on what external systems you need to talk to. Here's the honest part about cheat sheets: they become outdated quickly. AWS releases new services constantly. Azure renames things (Service Fabric became part of other offerings, Azure Functions formerly known as Azure WebJobs, etc.). A static document has a shelf life of maybe six months before it starts containing misleading information. I keep mine in a version-controlled repo and update it when something breaks in production, not on a schedule. If a service mapping causes an issue, I add a note about what actually works. That note is worth more than the original mapping.
Download links for existing cheat sheets are everywhere, but most of them are either too detailed to be useful or too simplified to be accurate. The best approach is building your own based on your actual work. Start with the categories I mentioned. Fill in the services you use daily. Add notes about the edge cases you've encountered. This takes about two hours the first time, and it pays for itself the first week you use it in a real incident. I've never found a third-party cheat sheet that included the specific gotchas that matter—the kind of thing that only shows up when you're at 3 AM trying to fix a deployment that works in one account and fails in another. One thing most people miss: the cheat sheet should include cost classes, not just service names. I put a simple column next to each service marking it as free tier eligible, pay-per-use, or subscription-based. This information lives in the documentation, but it's scattered across different pages. Having it in one place saves time during architecture reviews. When someone asks if they can run this in a proof-of-concept without billing surprises, the answer is immediate rather than requiring a visit to the pricing calculator. Another thing that helps: include the region availability indicator. Not every service runs in every region. SNS and SQS are region-specific. Global services like Route 53 and CloudFront behave differently. I add a quick note next to services that have limited regional availability so teams don't assume parity when designing for multi-region deployments.
The cheat sheet format I use is a simple table with columns for service name, category, equivalent in the other cloud, and a notes field. Nothing fancy. Plain text or a shared spreadsheet works fine. The one I currently maintain has about 60 service pairs and fits on three pages. When I need to onboard someone to a new cloud environment, I hand them this document and let them fill in the gaps as they encounter them. It becomes theirs over time, which is exactly what you want from a working reference.