What actually happens during an AWS security assessment
An Aws Cloud Security Assessment is a structured review of your Amazon Web Services environment to find misconfigurations, overly permissive IAM policies, exposed data, and compliance gaps. It is not a single tool you run once. It is a process that combines automated scanning, manual policy review, and evidence gathering across your accounts. Most teams start by enabling CloudTrail across all regions, turning on S3 access logging, and configuring Config with rule evaluation. That gives you the raw data you need before anything else. Without it, you are just guessing. I set up assessments for clients all the time. The first thing I do is check whether they actually have multi-account organization structure in place. If they do not, you are going to spend twice as long hunting for resources. I had one engagement where someone had created twenty-seven standalone accounts over three years with no centralized logging. It took me four hours just to map which accounts were still active and which had been abandoned. I used a simple API call chain combining organizations.list_accounts with cloudtrail.trail_status checks to identify orphaned accounts. Then I cross-referenced with cost explorer to confirm no billing activity in six months. Those got flagged for decommissioning immediately.
Here is what most people miss about doing this properly. Automated scanners will give you a list of findings, but the real value comes from understanding context. A publicly accessible S3 bucket might be a critical finding, or it might be a static asset hosting for a marketing site with no sensitive data. You need to know which is which before you escalate anything. The core methodology I use breaks down into three phases. First, reconnaissance and data collection. Second, rule-based evaluation against known benchmarks. Third, manual validation of high-severity findings. For reconnaissance, I pull resource inventories using config.get_resource_config_history and resource-explorer-2. I also export IAM policy documents directly rather than relying on the console UI, because the console hides a lot of inherited permissions. The IAM policy generator is useful, but it does not show you conditions that apply at the org level. I wrote a Python script that pulls every IAM policy document, resolves inline policies against managed policies, and flags any statement with Action: "*" on Resource: "*". That catches a surprising number of problems in medium-sized deployments.
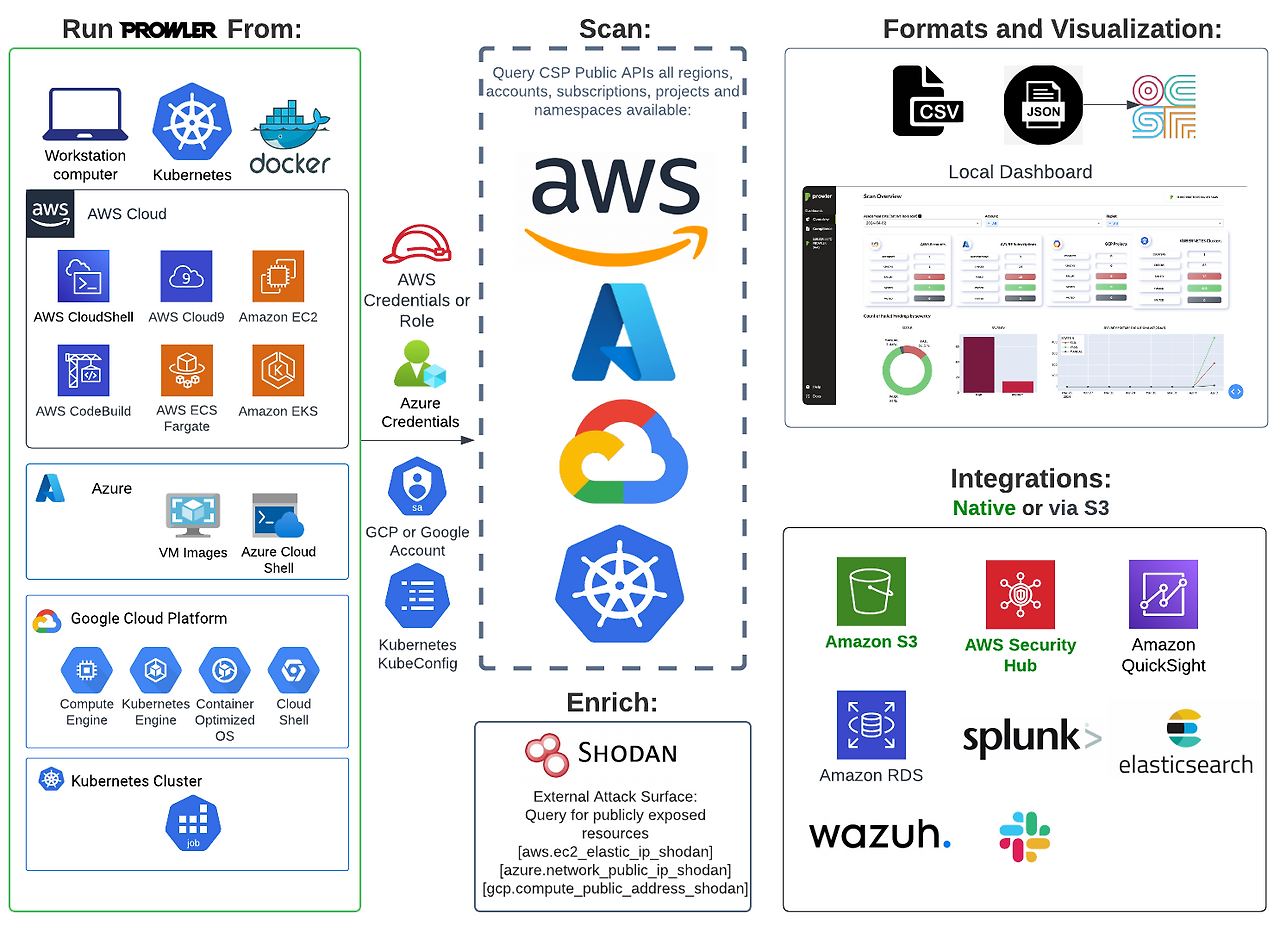
For evaluation, I run rules against the CIS AWS Foundations Benchmark and the AWS Well-Architected Framework security pillar. You can do this with AWS Security Hub if you have it enabled, or you can run open-source tools like Prowler or Scout Suite. I prefer Prowler in production environments because it gives you detailed output with remediation guidance for each finding. Scout Suite is faster but less thorough on IAM. I encountered a tricky edge case once where an RDS instance had PubliclyAccessible set to false in the main configuration, but there was a modified DB parameter group applied that included a custom endpoint binding. The instance was not directly reachable from the internet, but it was accessible through a bastion host that had no access logging enabled. I caught this by checking rds.describe-db-instances alongside ec2.describe-network-interfaces to trace the actual connectivity path. Most assessments would have marked this as secure based on the RDS attribute alone. The manual validation phase is where you separate real risks from noise. Automated tools will flag things like an S3 bucket without server-side encryption when encryption is actually handled by an IAM policy condition or KMS key policy. You need to read the actual policy documents, not just the banner findings.
Get the Full Details

I also check for common misconfigurations that tools sometimes overlook. VPC flow logs disabled on production subnets. EC2 instances with public IP addresses assigned through elastic IPs that are not explicitly tracked. Lambda functions with overly broad event source mappings. DynamoDB tables with default encryption disabled. These are the things that cause incidents, not the flashy zero-day vulnerabilities. Here is another thing people get wrong. They treat compliance frameworks as checkboxes. The NIST 800-53 controls and ISO 27001 requirements overlap significantly with AWS security best practices, but they are not identical. Mapping findings to a framework manually takes time, and it is easy to miss control gaps because the tool output does not align cleanly with the standard. I keep a mapping spreadsheet that tracks which AWS Config rules and Security Hub findings correspond to each control. It saves hours during audit season. The main limitation of automated assessment tools is that they cannot understand business logic. They will tell you a security group allows inbound traffic on port 22 from 0.0.0.0/0. They will not tell you whether that particular security group belongs to a jump box in a DMZ or an internal database server. You have to add that context manually. Another limitation is that many tools do not properly handle AWS Organizations service control policies. An IAM policy might look permissive on its own, but an SCP at the organizational level could be restricting it further. I always check SCPs before finalizing any finding.
If you need a practical starting point for tools, Prowler is available on GitHub under a Apache 2.0 license and runs via pip install. Scout Suite is also open source and available through pip. AWS has built-in capabilities through Security Hub and Config rules if you want to stay within the AWS console. There is no single download link that covers everything because this is not a monolithic product. It is a combination of services, scripts, and manual review. The most reliable approach I have found combines automated scanning with a structured manual review checklist. Run Prowler or Scout Suite first to get the broad picture. Then manually validate the top twenty findings by severity. Then check for the edge cases that automated tools miss, particularly around shared responsibility boundaries, cross-account roles, and network path analysis. Then map your validated findings to the relevant compliance framework. That process usually takes a small team about three to five days for a mid-size AWS environment with five to fifteen accounts. Larger environments scale roughly linearly, though the manual review portion tends to grow faster than the automated scanning portion because there are more edge cases to investigate. I also recommend running assessments on a regular cadence rather than as a one-time event. AWS configurations change constantly. New instances spin up, IAM policies get modified, security groups get opened. A monthly assessment cycle catches drift before it becomes an incident. I have seen teams skip assessments for six months and then find that someone had attached a wildcard IAM policy to a role that several applications assumed. That role had write access to S3, RDS, and Lambda across multiple accounts.
One advanced nuance that is worth mentioning. When assessing Lambda functions, do not just look at the execution role. Look at the resource-based policy attached to the function itself. I found a case where the execution role was properly scoped, but the function had a separate resource policy allowing invocation from any account in the organization. The assessment would have missed this if we only reviewed IAM roles. Similarly, when reviewing ECR repositories, check whether lifecycle policies exist and whether the repository allows unauthenticated pull access. An unauthenticated ECR repository is effectively a public container image store, and it is easier to find than you might expect in environments where teams iterate quickly on container deployments. The bottom line is that a proper Aws Cloud Security Assessment requires both tooling and human judgment. The tools get you to eighty percent coverage quickly. The remaining twenty percent, the part that actually prevents incidents, comes from understanding how your specific environment is configured and where the gaps between automation and reality exist.