Setting Up Behavioral Analysis in Your SOC
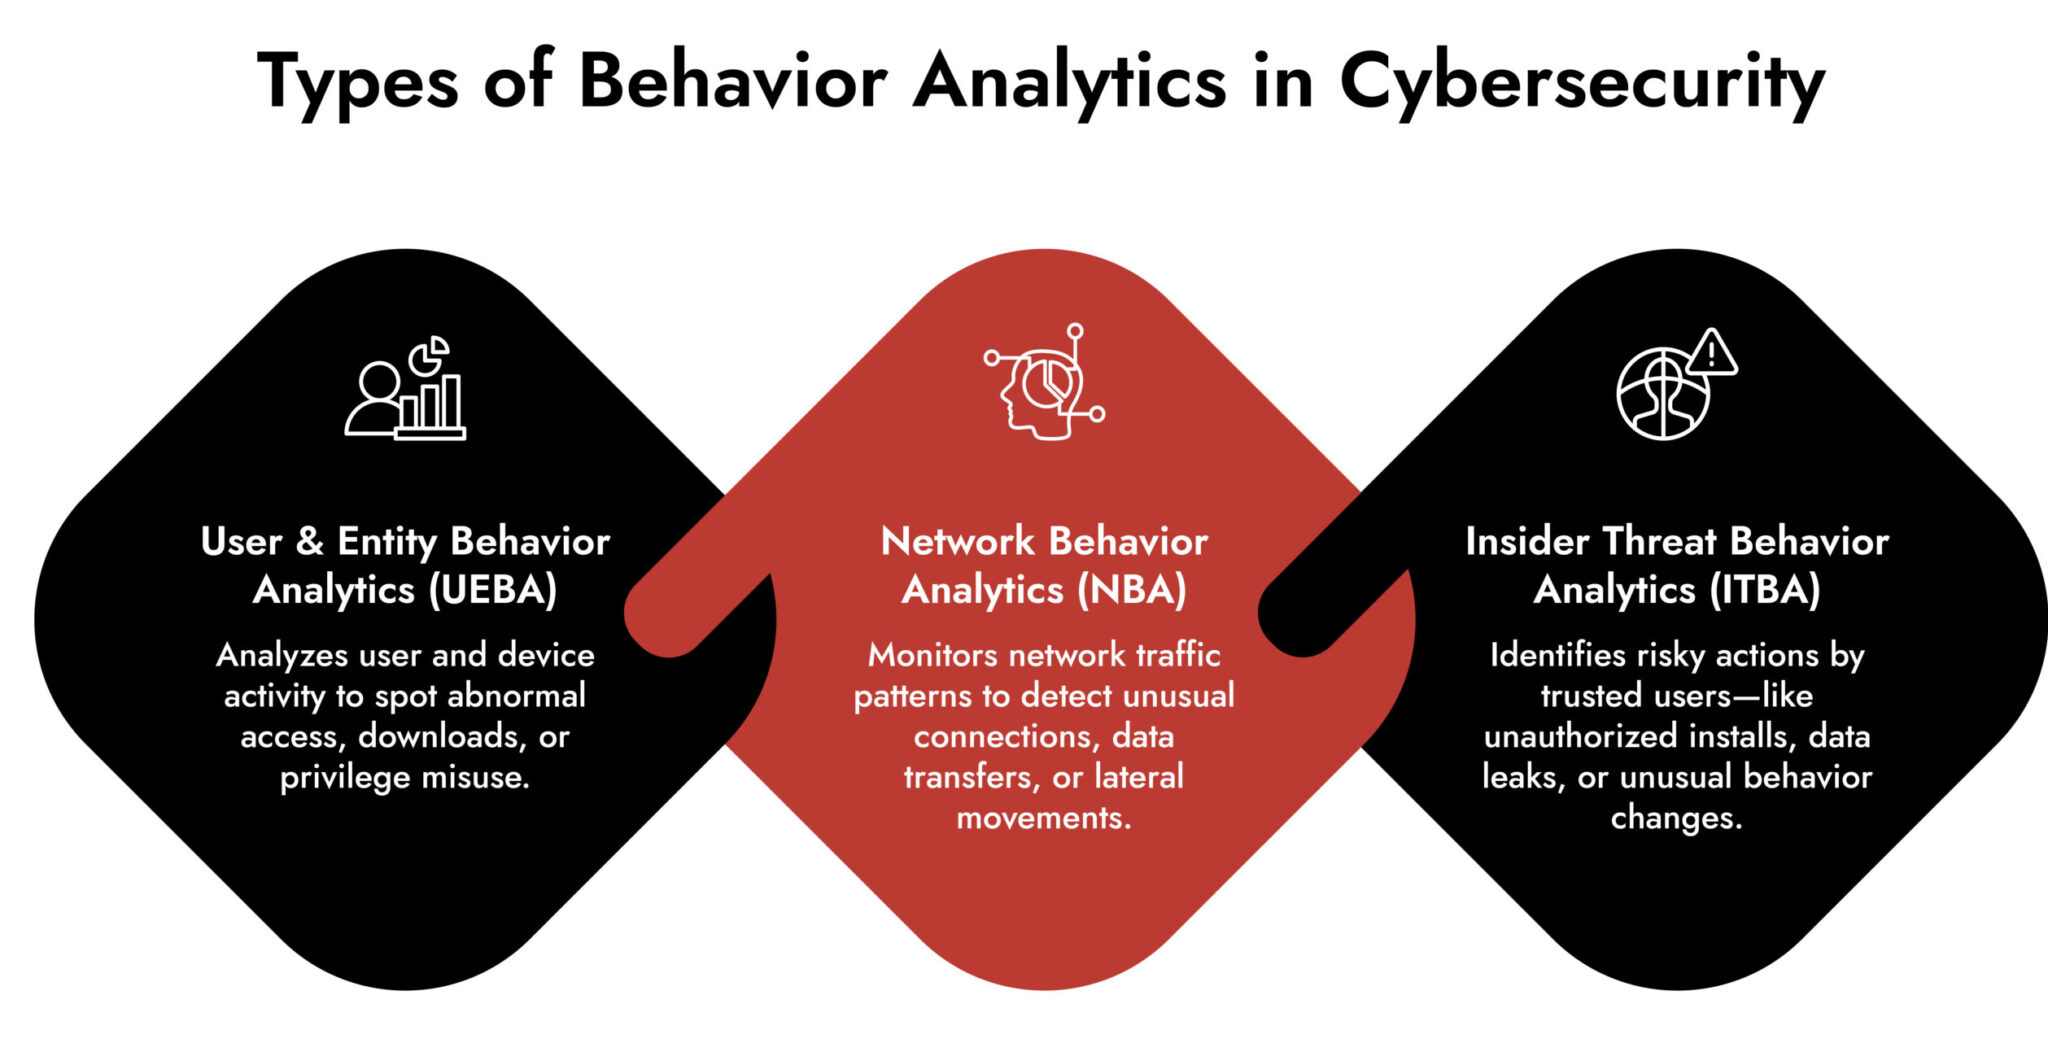
Most teams deploy behavioral analysis tools and immediately get swamped with false positives. The initial baseline is noisy because everything looks like an anomaly when you haven't established what normal looks like for your environment yet. I spent about three weeks watching my SOC team struggle with this before I figured out the right approach. The core problem wasn't the tool. It was that nobody understood how to calibrate it properly for their specific network. Behavioral analysis in cyber security refers to methods that detect threats by monitoring deviations from established patterns of user and system behavior rather than relying solely on known signatures or indicators of compromise. This approach operates on the premise that attackers often behave differently from legitimate users even when they use valid credentials. The concept isn't new. It goes back to the late 1980s when Gerald Wyner published work on anomaly detection in intrusion detection systems. Modern implementations are far more sophisticated, typically using machine learning models to create dynamic baselines and flag statistically significant departures from those baselines. The two main categories are user behavior analytics and entity behavior analytics. UBA focuses on people. EBA looks at devices, applications, and network connections. Most mature deployments combine both into a single platform. The combination matters because a compromised account often shows up first as unusual login behavior, and then the attacker's lateral movement shows up as anomalous device behavior downstream.
How to Get It Working Without Burning Through Your Budget
Start by picking three to five key users and one to two critical servers. Configure your behavioral analysis tool to monitor those specific entities for at least two weeks before you enable any alerts. During this quiet phase, the system builds a baseline profile. You're not trying to catch anything here. You're letting it learn what routine access patterns look like for each entity. This period directly determines how many false positives you'll deal with later. Skimping on baseline collection time usually means the tool flags everything from normal off-hours VPN use to legitimate batch processing jobs. Once the baseline is established, configure your first alert rule to trigger only on high-confidence deviations. I recommend setting the threshold to require a deviation score above 0.8 on the platform's anomaly scale before sending anything to your SIEM. This keeps your initial alert volume manageable while you fine-tune. A typical mature deployment generates anywhere from 20 to 60 behavioral alerts per day for a mid-size organization. If you're seeing hundreds, your threshold is too low or your baseline is still too thin. Next, correlate behavioral alerts with existing log data from your identity provider, endpoint detection and response platform, and network telemetry. Behavioral analysis alone rarely tells you the full story. What it does tell you is which investigation path to prioritize. Anomalous login from a new geographic location paired with privilege escalation on a domain controller warrants immediate attention. The same anomalous login without additional signals is worth a flag but not an all-hands incident.
A Real Edge Case That Broke My Workflow
I once ran into a situation where a senior developer's account triggered repeated behavioral alerts over three consecutive days. The anomaly scores kept climbing. The alerts showed access patterns that deviated significantly from his historical baseline. I initially suspected credential compromise and pushed for immediate account lockout. But when I dug into the data more carefully, I noticed the access pattern wasn't random. It was a deliberate shift to a new development environment that had recently been provisioned. The developer was running integration tests through a VPN gateway that had a completely different IP range than his usual office connection. The behavioral tool had no context for this change because the environment migration wasn't documented anywhere. The workaround was straightforward but tedious. I created a specific exception policy for that developer's account tied to the new VPN subnet and the development server range. I also added a note to the behavioral platform's whitelist with the reason code and the expected duration of the anomaly window. After that, the alerts stopped. The moral of the story is that behavioral analysis treats all new patterns as potentially malicious until proven otherwise. Documented organizational changes are a blind spot if you don't feed that context into the system. You need a process, preferably automated through your IT service management tool, that flags environment changes, role transfers, and infrastructure migrations directly into the behavioral platform's configuration.
Get the Full Details

Common Pitfalls That Wreck Most Deployments
One thing most beginners miss is the feedback loop between your analysts and the model. Behavioral analysis tools learn from labeling actions as benign or malicious. If your SOC team never marks whether a flagged behavioral event was a real threat or a false positive, the model stops improving. It just keeps generating the same noise. I've seen platforms where the labeling rate dropped below ten percent after the first month. Within six months, those platforms were producing zero value because the algorithm couldn't distinguish signal from background variation. Another pitfall is treating behavioral anomalies as incidents by default. A behavioral alert is not an incident. It's a hypothesis. The hypothesis is that something unusual is happening. Your job is to test the hypothesis, not assume it's true. The time I spent investigating behavioral alerts that turned out to be nothing is substantial. But the one time a behavioral alert caught a live lateral movement attack that signature-based tools missed completely made that investment worthwhile. The balance is in how you triage. There's also the issue of insider threats who know how to operate within normal parameters. Behavioral analysis struggles against patient insiders who deliberately mimic legitimate patterns. This is sometimes called low-and-slow behavior. The deviations are small enough to stay below detection thresholds. Detecting this requires combining behavioral analysis with data loss prevention controls and access pattern analysis across longer time windows, usually ninety days or more. A single month of baseline data is insufficient for identifying deliberate insider threats.
Tools and Where to Get Them
Commercial options include Splunk User Behavior Analytics, Microsoft Sentinel's built-in UEBA capabilities, and Palo Alto Cortex XSOAR with its behavioral modules. There are also open-source approaches using Elastic Stack with the Machine Learning module, which gives you anomaly detection without the licensing cost. The Elastic option works well if you already have an Elasticsearch deployment and have the staff to tune the models yourself. It's not a point-and-click solution. You'll spend time configuring jobs, interpreting results, and adjusting thresholds. For organizations looking to experiment before committing to a commercial product, I'd recommend starting with the open-source Elastic Stack approach. You can deploy a basic cluster in a few hours and begin ingesting authentication logs within a day. The learning curve is steep, but the flexibility is high. Once you understand what your behavioral data looks like, moving to a commercial platform becomes a much easier decision because you'll know exactly which features matter to your operation.
When Behavioral Analysis Simply Won't Work
Let me be clear about what this approach cannot do. It will not protect you against attacks that use stolen certificates and operate within normal network communication patterns. It will not reliably detect threats that move slowly enough to stay within established behavioral bounds. It will not replace proper patch management, strong access controls, or basic network segmentation. Behavioral analysis is a detection layer, not a prevention layer. You should think of it as catching what your other controls missed, not as your primary defense. The most honest assessment is that behavioral analysis cyber security is useful when your environment has enough volume and variety of log data to build meaningful baselines. Small organizations with fewer than fifty endpoints may find that the false positive rate remains unacceptably high even after proper tuning. In those cases, focusing on endpoint detection and response tools with basic anomaly features might give you better returns on your limited SOC time. The approach scales well with complexity. It struggles with simplicity.