How to actually use a Behavioral Threat Assessment Checklist without wasting everyone's time
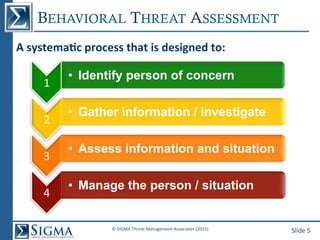
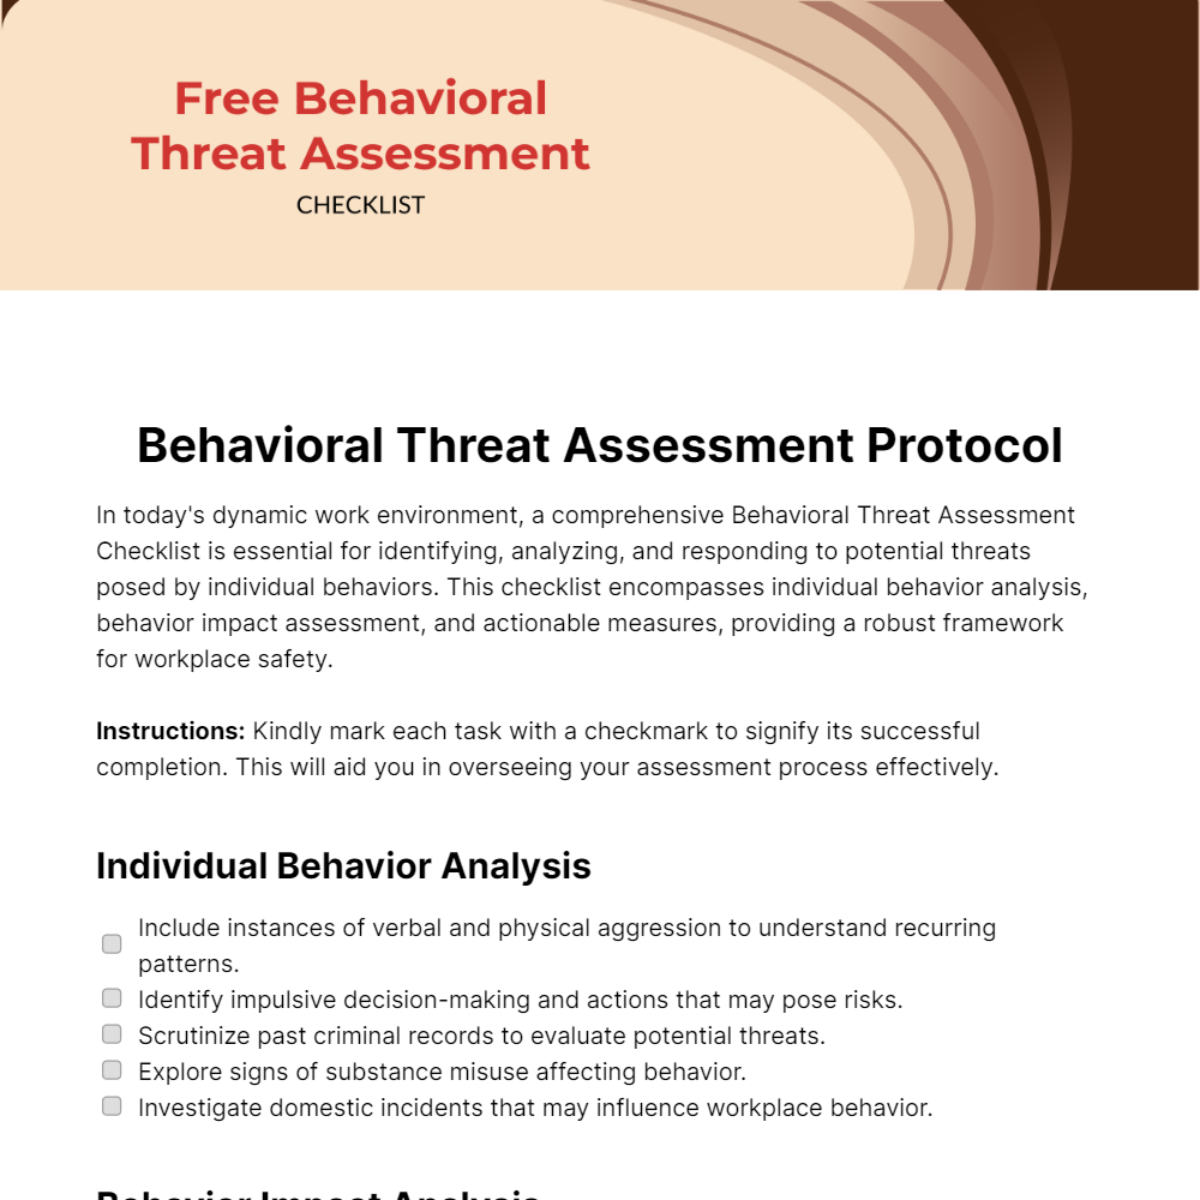
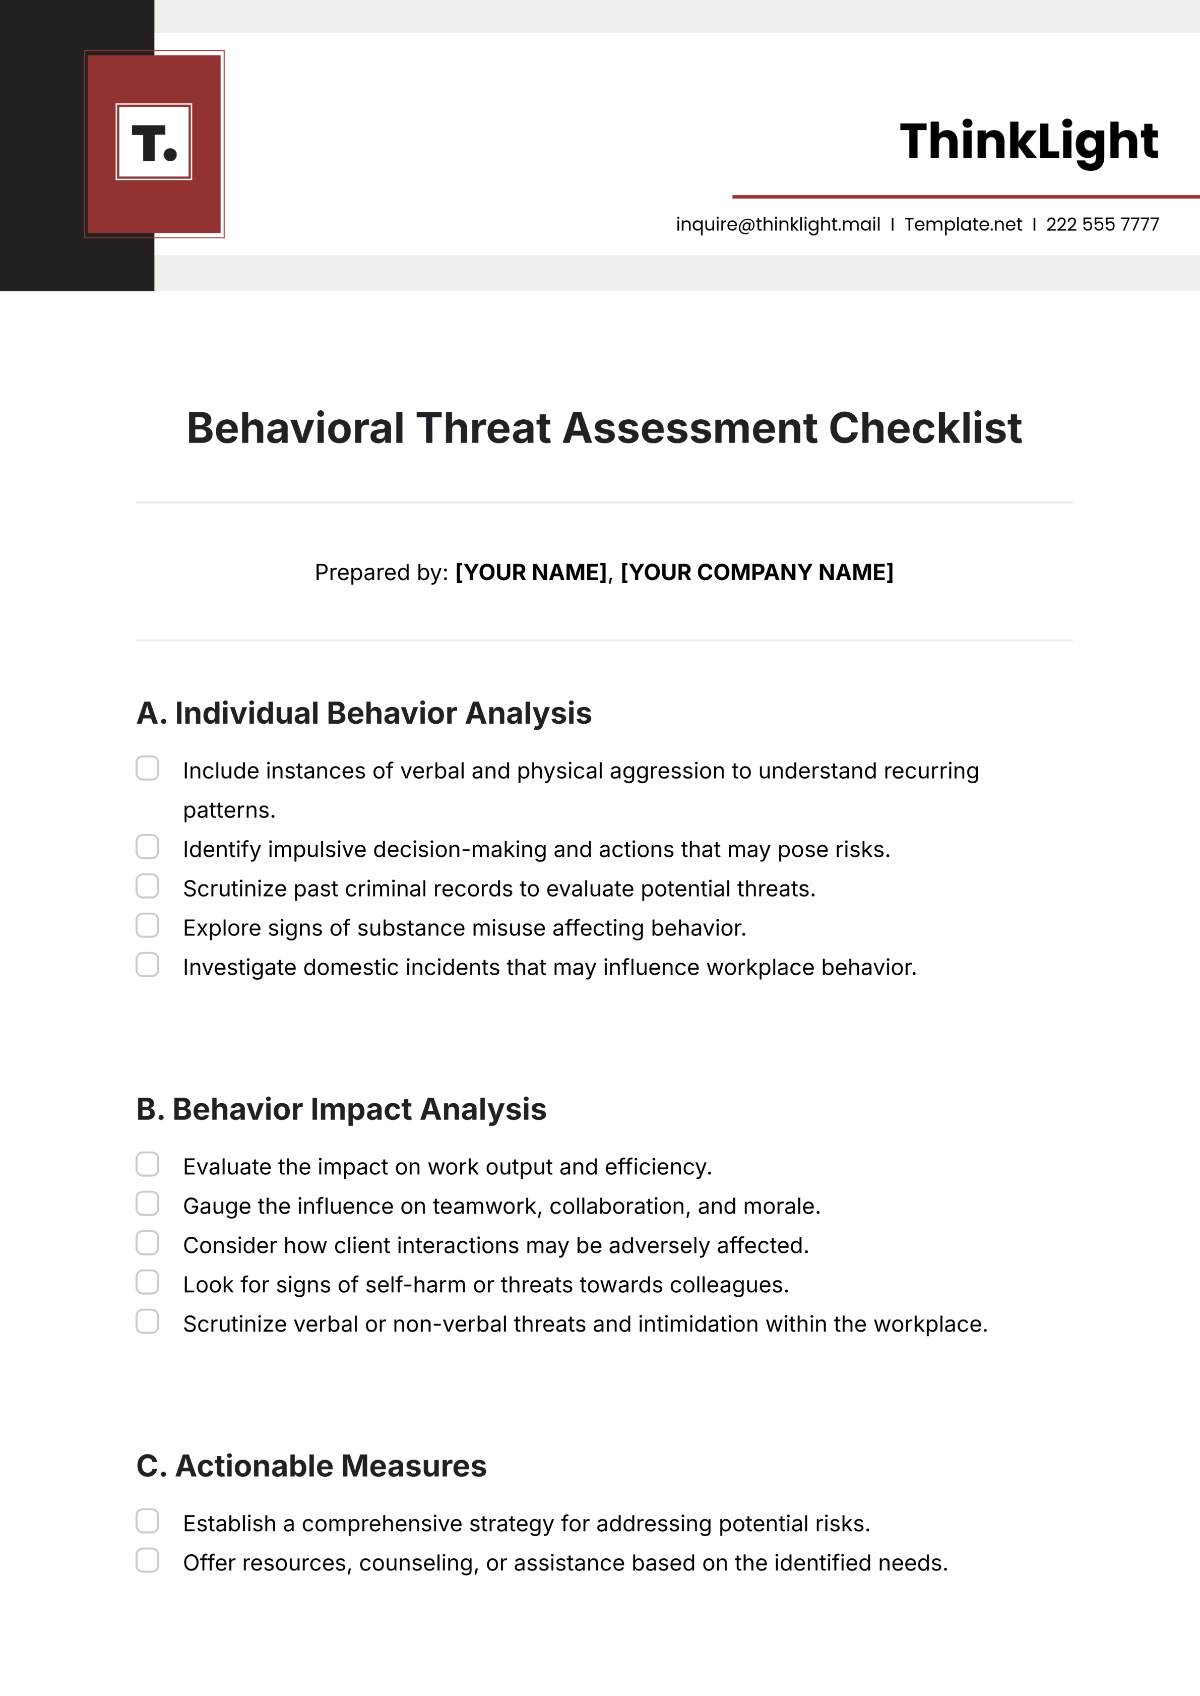
I spent about three years building and refining threat assessment procedures for a mid-sized university system before I realized most people were using checklists wrong. They treat them like compliance forms to stamp through, which defeats the whole purpose. A checklist should be a thinking scaffold, not a completion exercise. The Behavioral Threat Assessment Checklist is most useful when you understand what it actually does: it forces assessors to consider patterns rather than isolated incidents. That distinction matters more than most teams realize. Start with what you're trying to catch. Most checklists I see are built around a single theoretical threat type. That is a mistake. Real-world behavioral threats look different depending on the environment, the population, and the timeframe. A checklist designed for K-12 schools will fail in a corporate setting. One for higher education will miss nuances in a healthcare facility. You need to map your specific risk landscape first, then build the checklist around the actual behavioral indicators you would see. The core structure I use has four sections, and I put the method before the definitions because that is how the work actually flows. You encounter the behavior first, then you evaluate it, then you categorize, then you document. Here is what each section should cover.
Section one: Observable behavioral indicators. This is the raw data. You are listing concrete things you can see, hear, or verify. Not hunches. Not rumors. Concrete behaviors such as repeated uninvited contact, explicit verbal threats, dramatic personality shifts, fixation on a specific person or group, gathering of materials consistent with harm, and violations of existing safety protocols. I once had a case where a team flagged an employee for "concerning email language" that turned out to be someone with severe OCD writing ritualistic messages. Without clear observable criteria in the checklist, we wasted two weeks chasing a ghost before the behavior context made the difference obvious. The fix was adding a verification step that required corroboration from at least two independent sources before anything moved past the intake phase. Section two: Contextual factors. This is where most checklists fall apart. A behavior in isolation means almost nothing. The same action can be benign or threatening depending on timing, frequency, escalation patterns, and environmental stressors. You need fields for duration of the behavior, any prior interventions, whether the subject responded to those interventions, and any contextual triggers. I have seen people skip this section because it takes longer. That is exactly when you miss the signal. Section three: Risk scoring and tiering. This is the part that gets contested. Assign a low, medium, or high risk rating based on the combination of behavioral indicators and contextual factors. The scoring should be collaborative, not solitary. One person's rating is a guess. Three people's ratings with documented reasoning is an assessment. I use a simple weighted system where escalation patterns carry more weight than isolated incidents, because escalation is the strongest predictor of actual harm in my experience.
Section four: Intervention mapping. A checklist without an intervention path is just a complaint form. Each risk tier needs predefined response options. Low risk might mean documentation and monitoring. Medium risk requires a formal meeting and resource referral. High risk triggers immediate security notification and possible removal of access. The key is having these options pre-agreed so you are not improvising during a crisis.
Get the Full Details

Where the standard approach breaks down
There are problems you will run into that no training manual covers. The biggest one is confirmation bias. Once a team labels someone as a threat, every neutral gets reinterpreted as confirmation. I had a case where a graduate student was flagged for "suspicious research interests" after an advisor made a casual comment. The Behavioral Threat Assessment Checklist caught it because section two forced us to document that the student had requested accommodations for anxiety, had a clean disciplinary record for five years, and had never interacted with the person who filed the concern. The checklist did not save us from the initial misstep, but it prevented the escalation. Another issue is checklist fatigue. After the fifteenth time you fill out the same form for something that turns out to be nothing, you start skipping fields. I stopped this by implementing a feedback loop where assessors report back on which fields actually produced useful information and which were just noise. After six months of that, our checklist shrank from forty-two items to nineteen. The ones that remained were the ones that consistently correlated with actual outcomes. You should also know what this does not do. A Behavioral Threat Assessment Checklist cannot predict an individual's actions with certainty. It can identify risk factors and patterns, but human behavior is too variable for any checklist to be universally accurate. False positives will happen. You will flag people who are not threats. The goal is not elimination of false positives, which is impossible, but reducing them to a manageable rate while catching the cases that matter. If someone tells you their checklist is one hundred percent accurate, they are either lying or they have never used it.
When the behavioral indicators point toward imminent harm, a checklist is the wrong tool. You need immediate security protocols, not structured assessment. The checklist works for situations that are concerning but unresolved, where you need to gather information and make a reasoned judgment. It does not work for active crisis situations that require instant intervention. The final piece most people overlook is the documentation standard. Every decision point on the checklist needs a brief written rationale. "Medium risk" is not sufficient. "Medium risk due to three documented escalation events over six weeks, subject declined offered mental health referral, and subject made specific statement about target on date X" is sufficient. The rationale becomes your defense if the assessment is ever reviewed, and it creates a pattern trail that helps future assessors understand the full picture without starting from scratch.