Building a Bsa Risk Assessment Matrix That Doesn't Collapse Under Real Workload
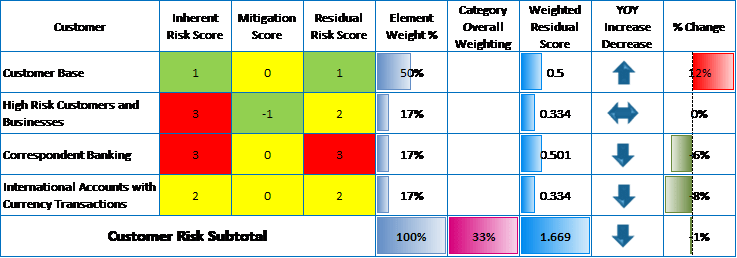
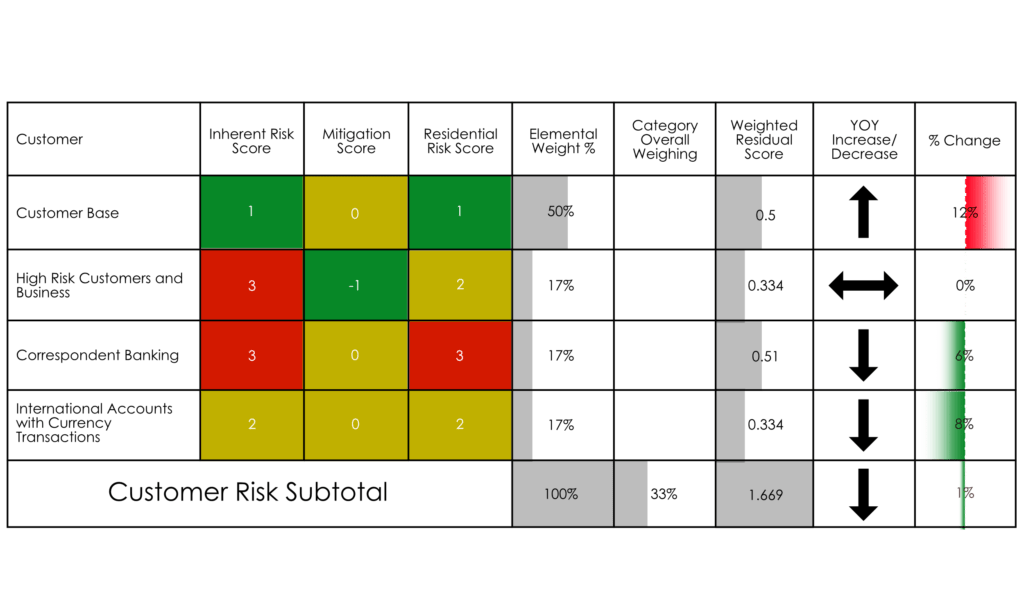
A risk assessment matrix is just a table that forces you to assign likelihood and impact scores to identified threats, then plots them into a grid. The Bsa Risk Assessment Matrix works the same way as any other version of this, but people tend to screw up the setup because they treat it like a compliance checkbox exercise instead of a working document. Here is how it actually functions. You start by listing your asset categories and the threats that apply to them. Then you score probability on a scale—typically 1 through 5—and impact on the same scale. Multiply those two numbers and you get a risk score. Anything above a certain threshold gets routed to your mitigation queue. That is the core mechanic. Everything else is just noise around it.
Practical steps to get a working Bsa Risk Assessment Matrix
I have built and maintained these for roughly a decade across different sectors. The process that actually sticks looks like this: Step one: Define your scope before you touch a spreadsheet. This is where most people fail. They open Excel, create columns, and start filling things in without deciding what the matrix is supposed to protect or evaluate. You need a clear boundary. Is this for vendor risk, operational risk, data security, or a combination? Write that down. A misdefined scope turns the matrix into a garbage collector for every complaint someone has ever filed. Step two: Identify your asset inventory. List everything the organization considers valuable enough to assess. Hardware, software, personnel, facilities, third-party dependencies, intellectual property. Be specific. "IT systems" is not an inventory. "Customer-facing SQL database hosted on AWS us-east-1 with three redundant copies" is an inventory item you can actually score.
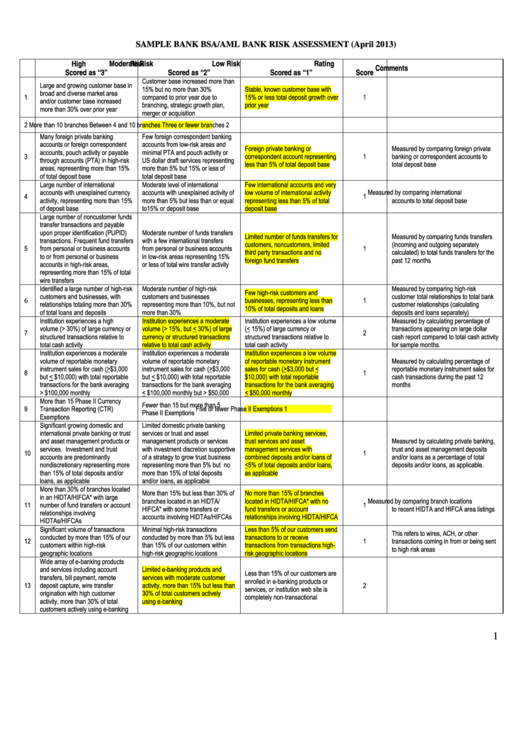
Step three: Catalog threats against each asset. Use threat taxonomies that already exist rather than inventing your own. NIST SP 800-30, MITRE ATT&CK, or your industry's equivalent framework. Cross-reference those against your asset list. You will find gaps immediately, and that is useful information in itself. Step four: Define your scoring criteria. Do not just say "1 is low, 5 is high." Write out what each level means. Likelihood score 3 should correspond to a concrete statement like "this event has occurred once in the past twelve months or three times in the past five years." Impact score 4 should say something like "operational disruption lasting between four and twenty-four hours with partial data loss." Without written definitions, two people will score the same threat completely differently and you will never know why. Step five: Score and calculate. This is the mechanical part. Assign likelihood and impact. Multiply. Log the result. Color-code the output for visual triage. Standard practice is red above 12, yellow between 6 and 12, green below 6. Adjust the thresholds to match your organizational risk appetite.
Get the Full Details
Step six: Route to treatment. Every risk score above your acceptable threshold needs an owner and a response type. Accept, mitigate, transfer, or avoid. This is the step that gets skipped most often, and it is the step that matters. A matrix with scores but no owners is just a fancy spreadsheet nobody reads. Step seven: Review and refresh on a schedule. Reassess quarterly at minimum, or trigger a re-review whenever a significant change occurs. New vendor, major platform migration, regulatory update. Static matrices are worse than useless. They give you false confidence because they look official.
Where people go wrong and how I fixed it
The biggest mistake I see is using arithmetic means for probability instead of empirical data. You will often hear someone say "the chance of a ransomware attack is medium" with zero supporting evidence. They are pulling that number from their gut. This inflates or deflates risk scores arbitrarily. My workaround was straightforward. For any threat where no historical data exists, I default to a midpoint score of 3 and attach a note flagging it as estimated. If the stakeholder pushes back, I require a written justification. Half the time they drop the score when forced to explain it. Another common failure mode is impact scoring that ignores cascading effects. People score the direct impact of a threat on a single asset and stop there. In practice, a compromised database server does not just cause data loss. It triggers incident response costs, regulatory notification requirements, customer churn, and reputational damage that extends well beyond the initial asset. I started using an extended impact column that captures secondary and tertiary consequences separately. The raw score alone becomes a minimum floor rather than the final number. I also encountered a situation where a Bsa Risk Assessment Matrix produced false negatives on cloud infrastructure risk. The scoring criteria were written for on-premises environments, so a misconfigured S3 bucket scored lower than a vulnerable physical server door. The issue was that cloud threat vectors have different probability distributions. I resolved this by maintaining separate impact and likelihood criteria for cloud versus on-premises assets and running both through the same matrix. It added complexity but fixed the blind spot.
Download and template access
Most organizations build their own matrix from scratch because off-the-shelf templates rarely match their scoring definitions. However, a solid starting template can save a few hours of setup. I use a structured format with these columns: Asset ID, Asset Name, Threat Category, Threat Description, Likelihood Score, Likelihood Rationale, Impact Score, Impact Rationale, Risk Score, Risk Owner, Mitigation Strategy, Treatment Type, and Review Date. Spread it across three tabs if you maintain separate likelihood, impact, and treatment registers, which I recommend because it keeps the calculation layer clean and audit-friendly. The template itself is straightforward. No macros, no VBA, just formulas for the multiplication and conditional formatting for the color bands. I distribute mine internally as a shared sheet because version control on local files causes more headaches than it prevents. If you need a file to begin with, search for "risk assessment matrix template" on your company's internal document portal or build the structure above from a blank workbook. The effort is minimal.
What this method cannot do
A Bsa Risk Assessment Matrix does not replace qualitative judgment. It quantifies your assessments after you have already made subjective calls. The matrix amplifies whatever bias you put into the scoring criteria. If your likelihood scale is vague, the matrix outputs false precision. If your impact definitions ignore regulatory consequences, the scores understate real risk. It also does not scale well beyond a few hundred threat entries without becoming unwieldy. I have seen teams push past that limit and end up with matrices so large that no single person can review them in a reasonable timeframe. At that point, the matrix becomes archival rather than operational. The workaround is tiered scoring. Run a coarse filter first to narrow candidates, then apply detailed scoring only to the items that clear the filter. This keeps the document manageable and focuses attention where it matters. Another limitation is that risk matrices flatten temporal dynamics. They capture a snapshot. A threat that is unlikely today may become highly probable next quarter after a regulatory change or a new attack campaign emerges. The matrix itself does not track velocity or trajectory. I handle this by adding a trend direction column and rescored dates. It costs about ten extra minutes per entry during review cycles but prevents stale assessments from sitting unchanged for months.
If you are looking for something more dynamic, a Bowtie analysis or fault tree approach may be more appropriate for complex operational scenarios. Those methods model causal chains explicitly instead of collapsing everything into a single risk score. I switch to those approaches when a threat has multiple interdependent failure paths rather than a straightforward cause-and-effect relationship.
Quick reference for common score definitions
Likelihood 1: Rare. Not expected within the planning horizon. Likelihood 2: Unlikely. Possible but not anticipated. Likelihood 3: Moderate. Might occur under normal operating conditions. Likelihood 4: Likely. Expected at some point. Likelihood 5: Almost certain. Will occur within the planning horizon. Impact 1: Insignificant. No operational disruption, no financial loss beyond trivial amounts. Impact 2: Minor. Limited disruption, contained financial impact. Impact 3: Moderate. Significant disruption, measurable financial loss. Impact 4: Major. Extended disruption, substantial financial loss, potential regulatory exposure. Impact 5: Catastrophic. Critical disruption, severe financial loss, regulatory action likely, reputational damage sustained. These definitions are a starting point. Adapt them to your context. The numbers themselves are arbitrary until your organization agrees on what they represent.
Bottom line
A Bsa Risk Assessment Matrix is a tool for making risk visible, not a tool for eliminating risk. It forces explicit thinking about likelihood and impact, which is valuable even when the underlying data is thin. Use it consistently, keep the scoring criteria written and accessible, route every high score to an owner, and refresh it regularly. Skip any of those and the matrix becomes decoration.