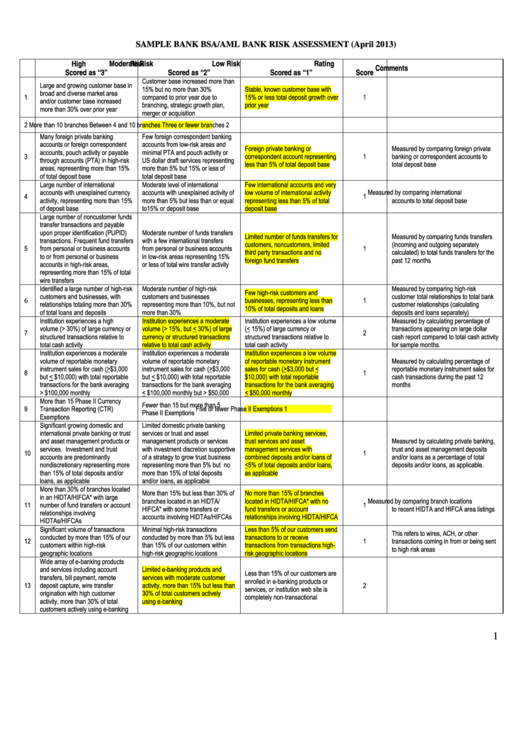
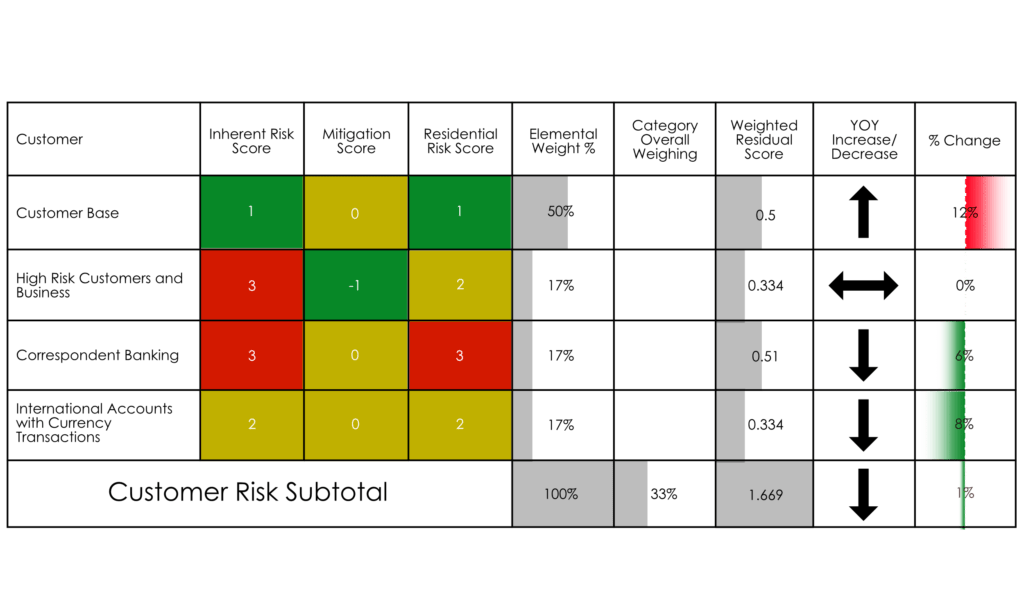
What a BSA Risk Assessment Template Actually Looks Like
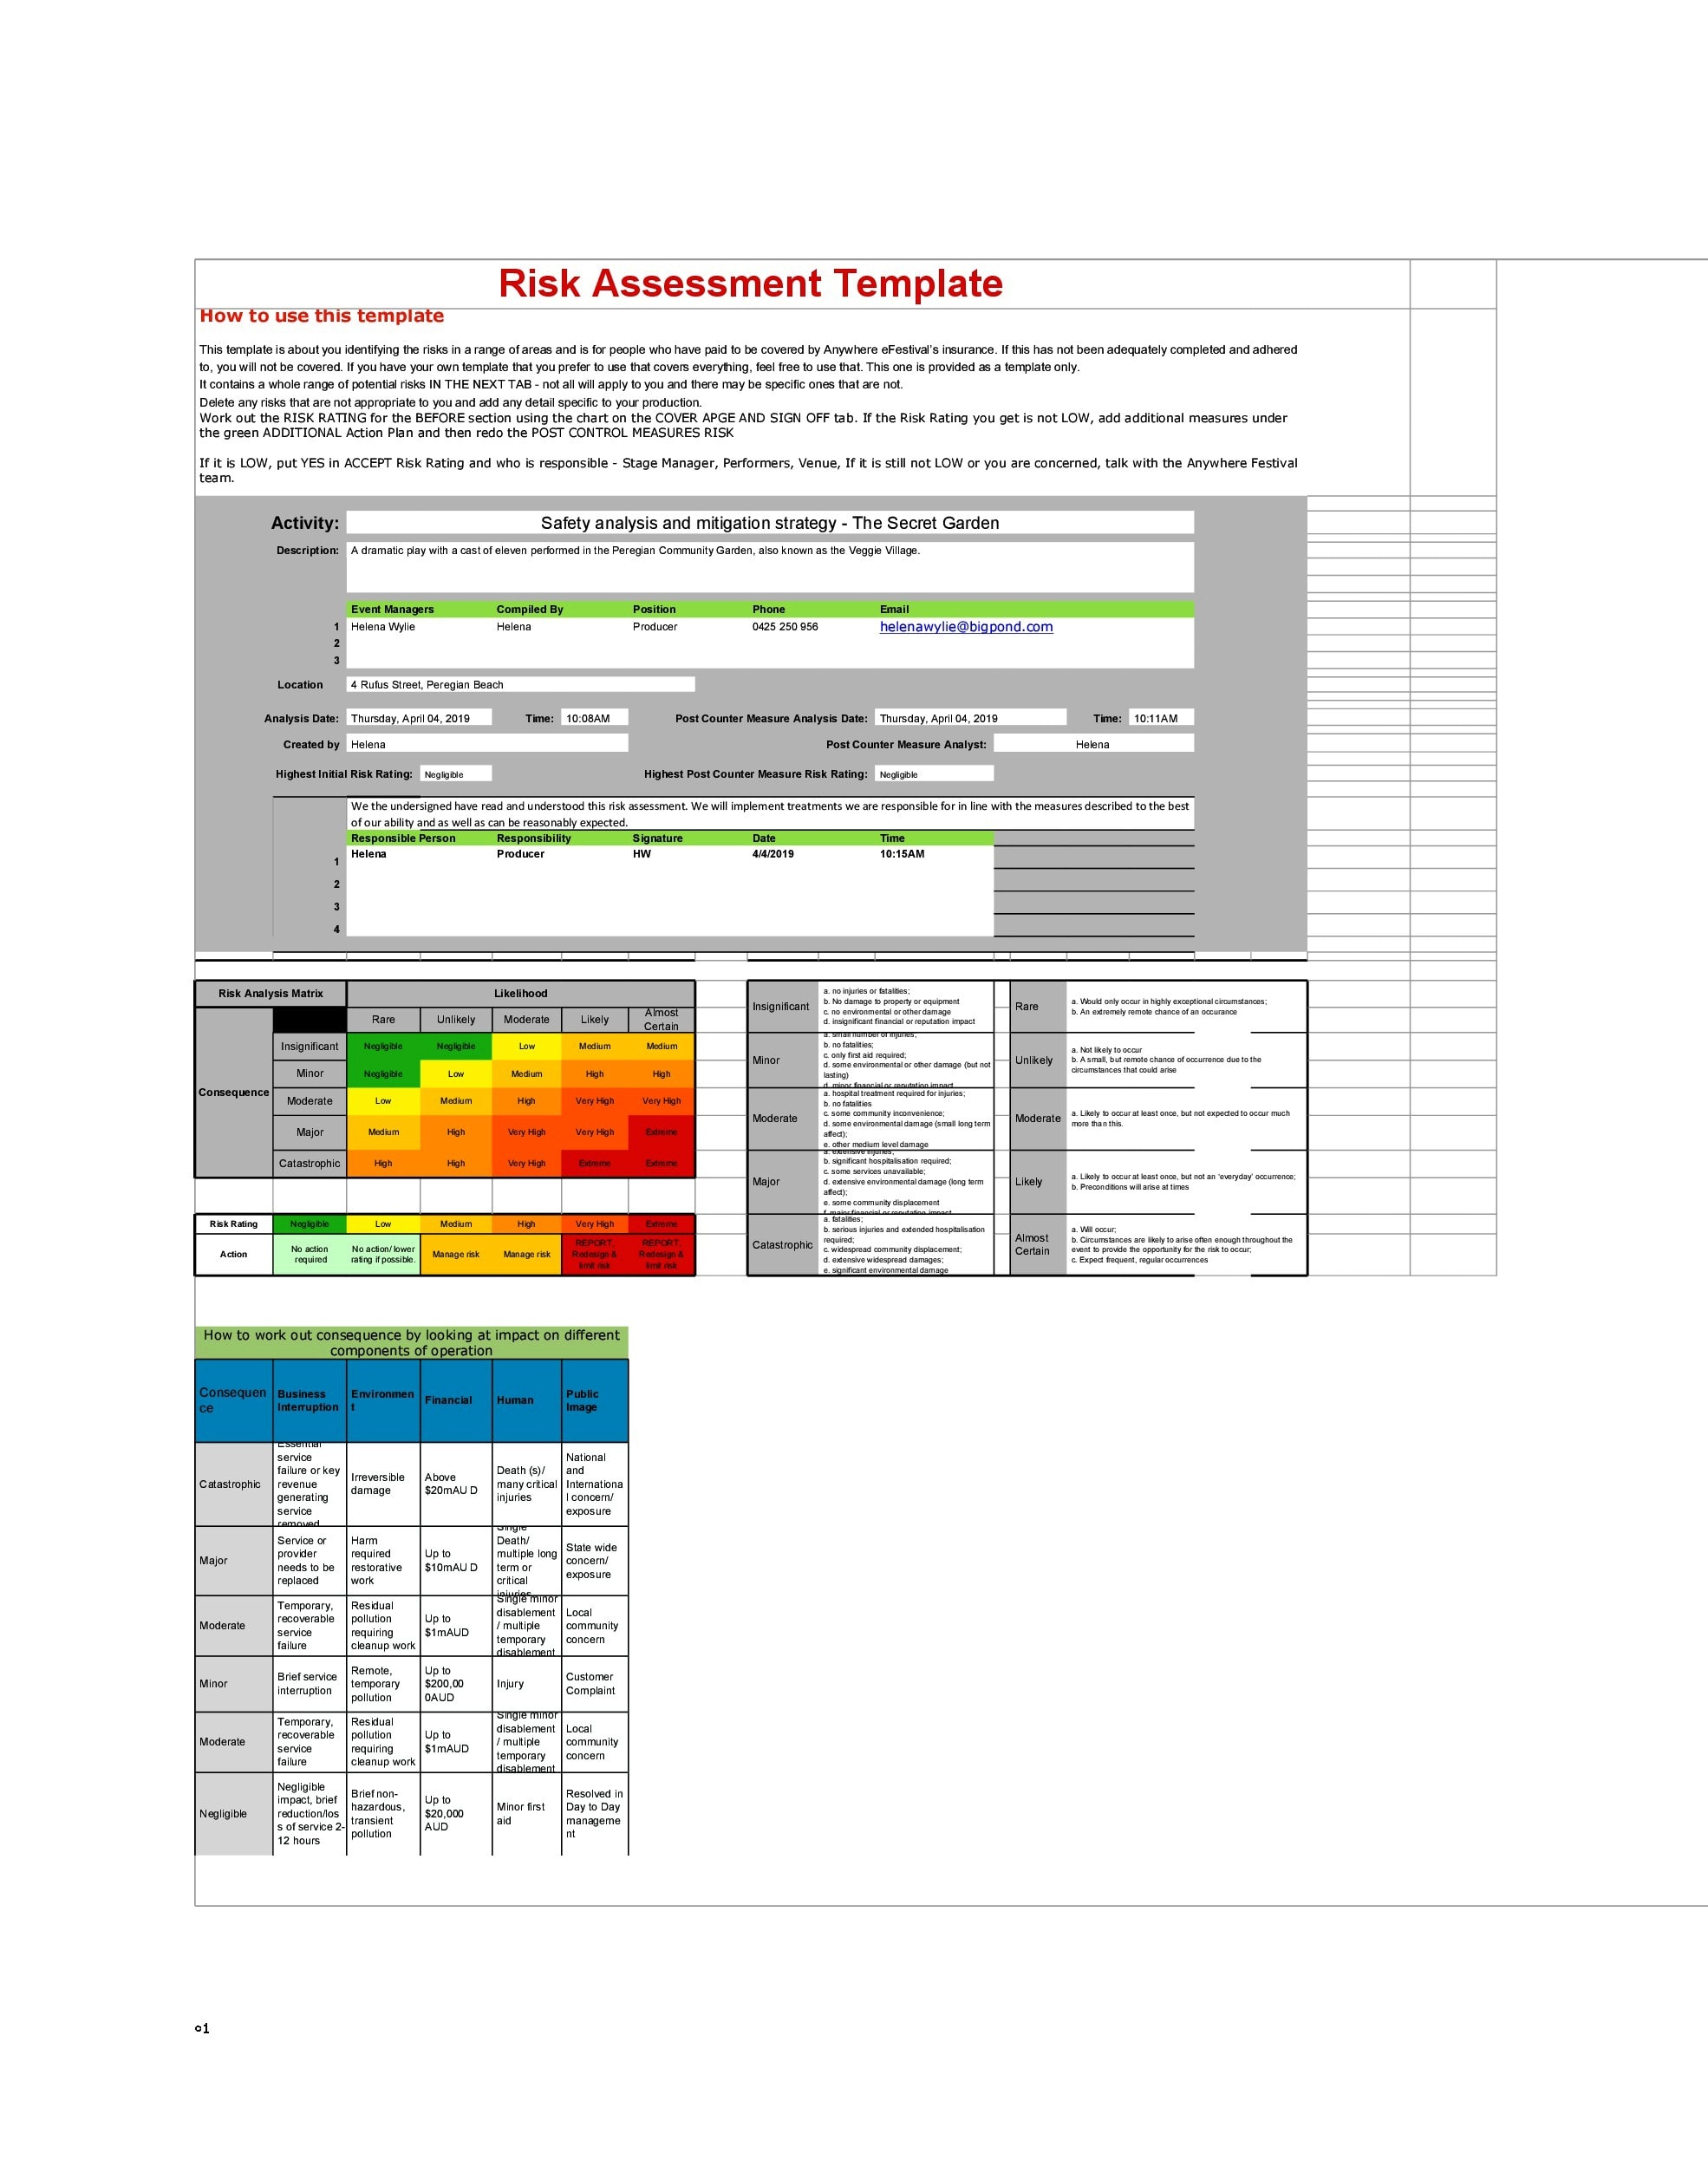
A BSA risk assessment template is a structured document used to identify, evaluate, and document risks within a business or organizational context. The BSA here generally refers to a Business Security Assessment framework, though some organizations apply it to Biometric Security Alignment or internal compliance reviews. The core idea is the same: you have a list of potential threats, you score them, and you decide what to do about each one. The template typically has columns for risk ID, threat description, affected assets, likelihood rating, impact rating, overall risk score, mitigation strategy, owner, and status. You fill it out row by row. Each row represents one identified risk. The scoring part is where most people waste time. Simple 1-to-5 scales work fine for most organizations. Multiply likelihood by impact to get your overall score. That number sorts your risks into accept, treat, transfer, or avoid buckets. I built a version of this for a mid-sized logistics company a few years back. We were dealing with supply chain disruption risks combined with data breach exposure from third-party vendors. The template itself was standard, but the problem was that half our risk entries had no identifiable owner. Finance owned some. IT owned others. Legal thought something else was theirs. Nobody owned the cross-departmental risks like a vendor contract changing without security review. My workaround was adding a "primary sponsor" column separate from "responsible owner." The sponsor is someone who has budget authority over that risk area, even if they aren't the person doing the work. That single column cut our stale risk items down by about 60% in the next review cycle because we finally had someone who could actually approve spending on mitigation.
How to Build One From Scratch
Start with your asset inventory. You can't assess risk against something you haven't identified. List your critical systems, data stores, processes, and physical locations. Then map threats to each asset. Common threat categories include unauthorized access, system failure, data loss, regulatory non-compliance, and supply chain dependency. Don't skip supply chain. It shows up in almost every assessment I have ever seen and gets completely ignored until something breaks. For likelihood scoring, use historical data where it exists. If you had an incident in the last two years, likelihood is at least a 3 out of 5. If you have no data, default to 2 and note that explicitly in the template. For impact scoring, consider financial loss, operational downtime, reputational damage, and regulatory penalties separately. Then combine them into an overall impact number. Most people just pick one impact number and miss that a low financial impact risk could still have catastrophic regulatory consequences. When you assign mitigations, be specific. "Improve monitoring" is not a mitigation. "Deploy SIEM alerts for failed login attempts exceeding 10 per minute from external IPs" is a mitigation. Vague language in your template creates vague accountability. Everyone reads it and assumes someone else is handling it.
Common Pitfalls That Wreck These Assessments
The biggest problem I see is static templates. People fill one out, print it, and file it. Risk assessments are living documents. If your template doesn't have a date field and a review frequency column built in, you are already behind. Set a quarterly review cycle for high-risk items and annual for everything else. Update it religiously or the whole thing becomes decorative. Another issue is over-scoring everything. When every risk is rated 4 or 5, nothing is a priority. I once reviewed an assessment where 87 percent of all identified risks scored above 12 on a 25-point scale. The board asked what they should fund first and the answer was literally nothing because everything looked equally urgent. Force-rank your risks after scoring. Take the top ten and ignore the rest for the current cycle. You can revisit the lower scores next quarter. A less obvious problem is assuming your template covers enough threat types. Standard BSA risk assessment templates focus heavily on information security threats. If your organization handles physical assets, human resources, or financial operations, those risk vectors need their own sections. A template built purely for IT risk will miss workplace safety issues, contractor misconduct, or cash handling vulnerabilities. Add custom threat categories for your specific industry. It takes about twenty minutes and prevents entire classes of risk from going unassessed.
Get the Full Details
Limitations You Should Know About
A risk assessment template is a documentation tool, not a risk reduction tool. It does not fix anything. It tells you what might go wrong and roughly how bad it would be. The actual mitigation work happens elsewhere, in budgets, in engineering tickets, in policy changes. Don't confuse having a completed template with having a safe organization. These templates also struggle with correlated risks. A single cyberattack might simultaneously trigger data breach risk, regulatory fine risk, customer churn risk, and system downtime risk. Your template will likely list these as separate rows with separate scores, which double-counts the impact. I handle this by adding a correlation flag column. When two risks share a common cause, you mark them and calculate a combined scenario score separately. It adds maybe five minutes per risk but keeps your overall risk picture honest. If your organization is small, like under fifty employees, a full BSA risk assessment template might be overkill. A simpler two-column list of top risks with basic mitigation notes often covers the same ground in a third of the time. The template format was designed for enterprises that need audit trails and regulatory compliance documentation. Smaller teams usually benefit more from speed than structure.
Where to Get a Usable Template
You can find free BSA risk assessment template files on several government and standards body websites. NIST publishes related frameworks that include downloadable templates. ISO 31000 resources also have risk register formats you can adapt. Commercial platforms like LogicManager and RiskWatch offer template libraries, but you do not need to pay for one to get started. A properly formatted Excel or Google Sheets document with the columns I described above will serve most organizations adequately for the first two or three assessment cycles. The columns you absolutely need are: risk ID, description, asset affected, likelihood, impact, risk score, mitigation strategy, mitigation owner, target completion date, current status, and last review date. Anything beyond that is optional and usually adds more work than value for smaller teams. Keep it simple. Update it regularly. Act on the results.