What Bug Bounty Program Pays You
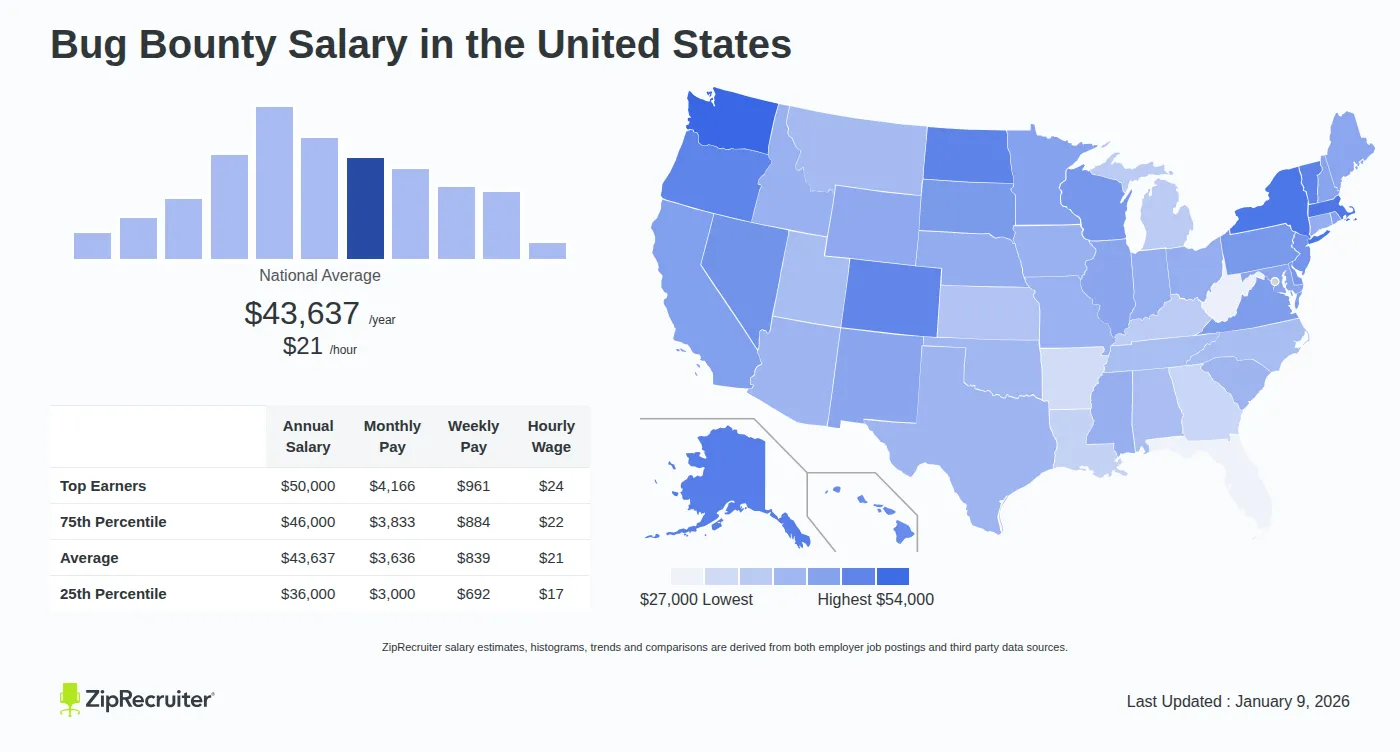
Most people coming into bug hunting think there is a fixed salary, like a W-2 job with health insurance and a 401k. That is not how it works unless you have somehow landed a full-time role at a company like Shopify, GitLab, or Google running an internal security team. The vast majority of bug hunters operate as freelancers on platforms like HackerOne, Bugcrowd, or Open Bug Bounty where income is entirely variable. I spent about three years doing this on the side before my day job made me redundant enough to go closer to full-time. What I wish someone had told me up front is that the median actually skews very low because of the long tail of people trying it out. If you look at the HackerOne public payout reports from 2023 and 2024, the numbers are brutal for beginners but very real for those who stick around. Most hunters report zero earnings in their first year. That is just the distribution.
Typical Bug Hunting Salary Breakdown
Let me break down what I actually saw in my bank account over roughly eighteen months of serious effort. Beginners can expect anywhere from $200 to $2,000 per validated finding if they find one, depending on severity. Critical bugs tend to pay between $3,000 and $15,000 on major programs. High severity usually lands in the $1,000 to $5,000 range. Medium bugs might get you $200 to $800 or sometimes nothing at all if the program filters them out. Low severity is pretty much donation territory. The problem is triage time. On a decent program I would spend maybe two weeks grinding for my first payout, then maybe another month before getting a second valid report accepted. Top tier hunters making legitimate six figures are outliers. They are the ones with specialized recon automation, prior experience in web exploitation, and probably dozens of hours a day to invest. They also tend to specialize in one vulnerability class rather than spreading thin across everything. I ran into a real issue early on where I submitted a critical XSS vulnerability to a well known fintech program on HackerOne and they marked it as N/A duplicate with barely any explanation. The submitters earlier had already reported a less refined version of the same issue. My workaround was pulling the original report metadata from the program page, downloading the duplicate evidence, and writing a rebuttal that mapped exactly where my exploit differed in terms of auth bypass combined with stored payload execution, while linking the prior submission timestamp. It took about twenty minutes of additional research but they ended up accepting the modified severity after review. It would have been an easy dismissal otherwise.
There are also a few things people consistently miss when they start calculating their potential earnings. One is triage turnaround time. A program can sit on your report for three weeks or three months before anything happens. During that waiting period your effective hourly rate can drop below minimum wage even on a paid finding. Some programs publish SLAs. Most do not. Another blind spot is triage quality variance. Different triagers within the same program can rate the same vulnerability completely differently. I have seen genuine cross-site scripting bugs move from critical to informationals between reviewers, and once you accept a lower rating, that becomes precedent for future submissions in that scope. You need to decide quickly whether appealing is worth the time cost or whether you should just move on. If you want more stable income, look at corporate bug bounty roles rather than pure freelance. Companies like Shopify pay starting around $90,000 to $120,000 for junior security engineers doing directed hunting, and senior roles go well beyond that. The tradeoff is you give up the flexibility and you answer to a manager. It is still more interesting than most dev jobs though.
Get the Full Details

There is also the hybrid path where you combine freelance payouts with penetration testing contracts, which is how I eventually funded the transition. Freelance bug hunting is real money if you treat it like a skill acquisition project for at least six months before expecting consistent returns. It does not pay well in months one through four for most people. The data supports that. Your skill ceiling is the only real constraint after that point.