What Actually Goes Into a Requirements Document
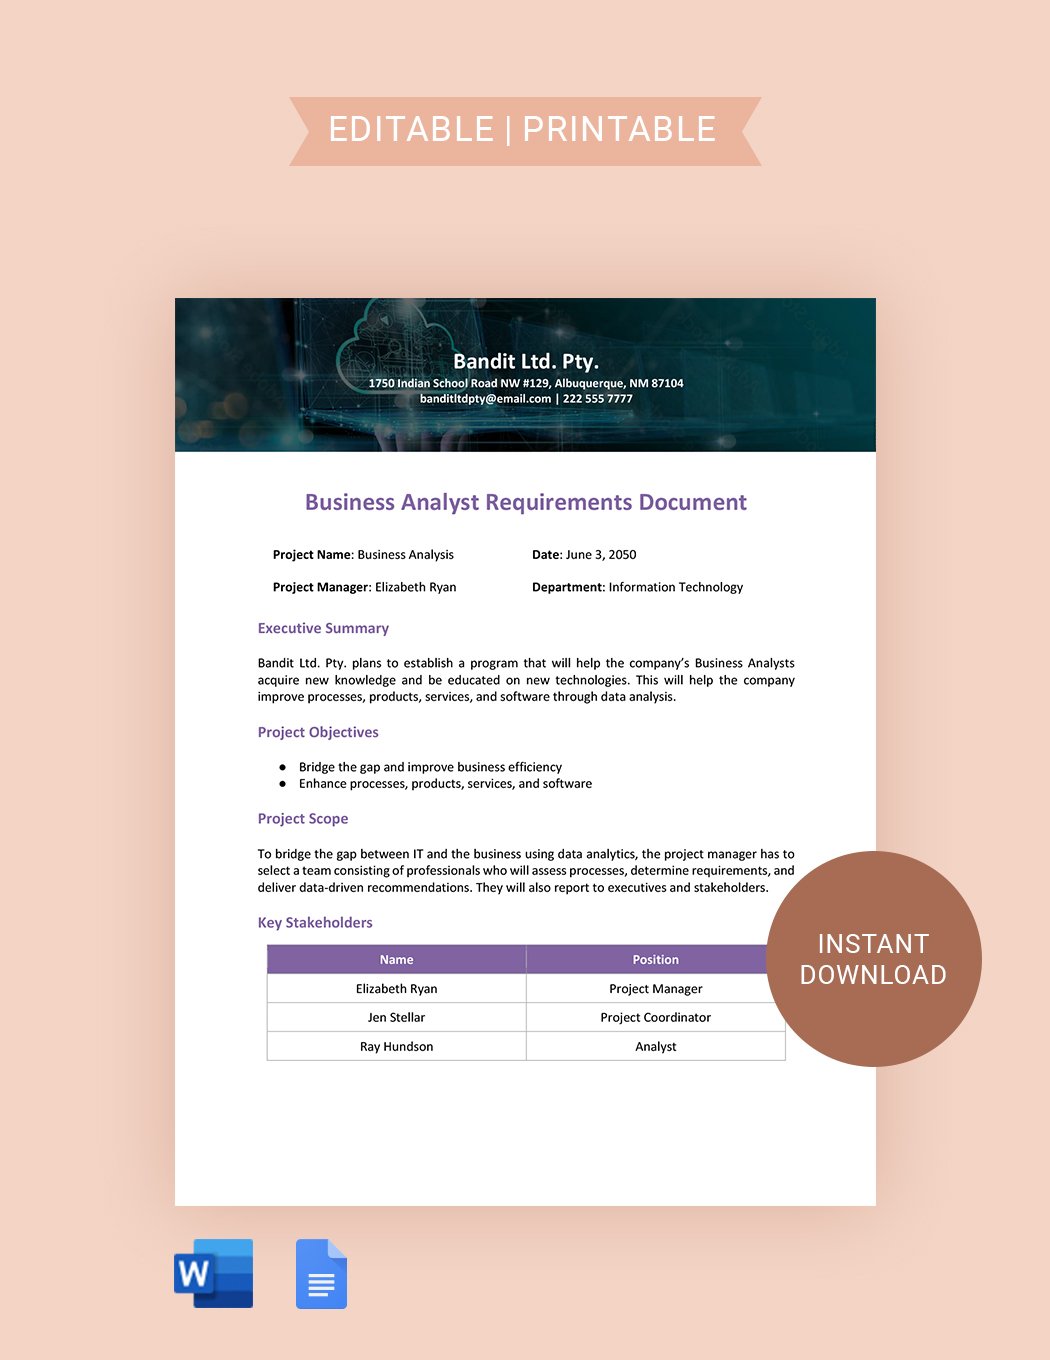
A Business Analyst Requirements Document Sample exists because stakeholders and developers keep talking past each other. You write the doc down so that when someone asks what the login page should do, you can point to a page number instead of guessing. That is the entire purpose. Everything else is noise. I spent three years watching teams treat these documents like compliance checkboxes. The real work happens when you stop writing them as if a machine will read it. Machines don't read. People do. And people skim. So you write for people who are tired and have fifteen minutes before their next meeting. Here is what I actually put in my documents. Not the textbook version. The version that survives contact with a real project.
Business Analyst Requirements Document Sample: A Practical Breakdown
Start with the functional requirements. These are the non-negotiable things the system must do. "The system shall allow users to reset their password via email link." Not "users should be able to recover access." Those are different sentences and they produce different products. I have seen teams build features based on vague language and then spend six weeks arguing about whether the original intent was met. It is cheaper to be specific upfront even if it takes longer to write. Then come the non-functional requirements. Performance, security, availability, scalability. These get ignored more often than anything else. A common failure I ran into involved an e-commerce platform where the functional specs were detailed to the pixel but nobody specified what happened when the checkout page loaded under five hundred concurrent users. The system slowed to a crawl during a flash sale. We had to add performance requirements retroactively, which is always more expensive and always creates political friction. Write the non-functional stuff before the functional stuff gets approved. Actually, write both at the same time in parallel sections. Data requirements matter more than most people think. Define the fields, their types, their constraints, and their sources. I once inherited a project where the requirements document said "customer address" without specifying whether that meant a single text field or structured fields like street, city, state, and postal code. The developers built it as a single text field. The marketing team needed to run geographic segmentation queries and couldn't. We spent two weeks migrating the data and rewriting the report layer. A five-minute decision in the requirements phase would have prevented that entire mess.
User roles and permissions belong in every serious document. Who can do what. Admin, editor, viewer, customer. List each role and what actions it can perform. I learned this the hard way on a healthcare analytics dashboard. The requirements mentioned "authorized personnel" as a permission level. Authorized by whom. Under what conditions. The developer implemented it based on department membership. The compliance team flagged it during the audit because it didn't match the actual authorization framework in place. Fixing permission logic after implementation is one of the most annoying tasks in this job. It always involves more meetings than the original requirement gathering did. Constraints and assumptions should be their own section. Technology constraints, budget constraints, timeline constraints, regulatory constraints. Then assumptions. If you assume something without writing it down, it is not an assumption, it is a landmine. I worked on a project where the assumption was that the existing CRM would support real-time data sync with the new platform. Nobody wrote that down. The CRM only supported batch imports at midnight. The go-live date moved by three weeks and half the team blamed the other half for it. Write the assumptions. Cross them out when they are proven wrong. Keep a record. Traceability is not glamorous but it prevents scope creep from destroying your timeline. Each requirement should have a unique identifier. FR-001, NFR-003, DR-007. When a stakeholder asks for something new, you map it to an existing requirement or create a new one with a new ID. This makes it obvious when someone is adding work without adjusting the timeline or budget. I used a simple spreadsheet with requirement IDs, descriptions, priority levels, and status columns. It took about ten minutes to set up and saved roughly forty hours of back-and-forth on a mid-size project. The alternative is the endless email thread where everyone agrees to something and then nobody remembers what was agreed to.
Get the Full Details
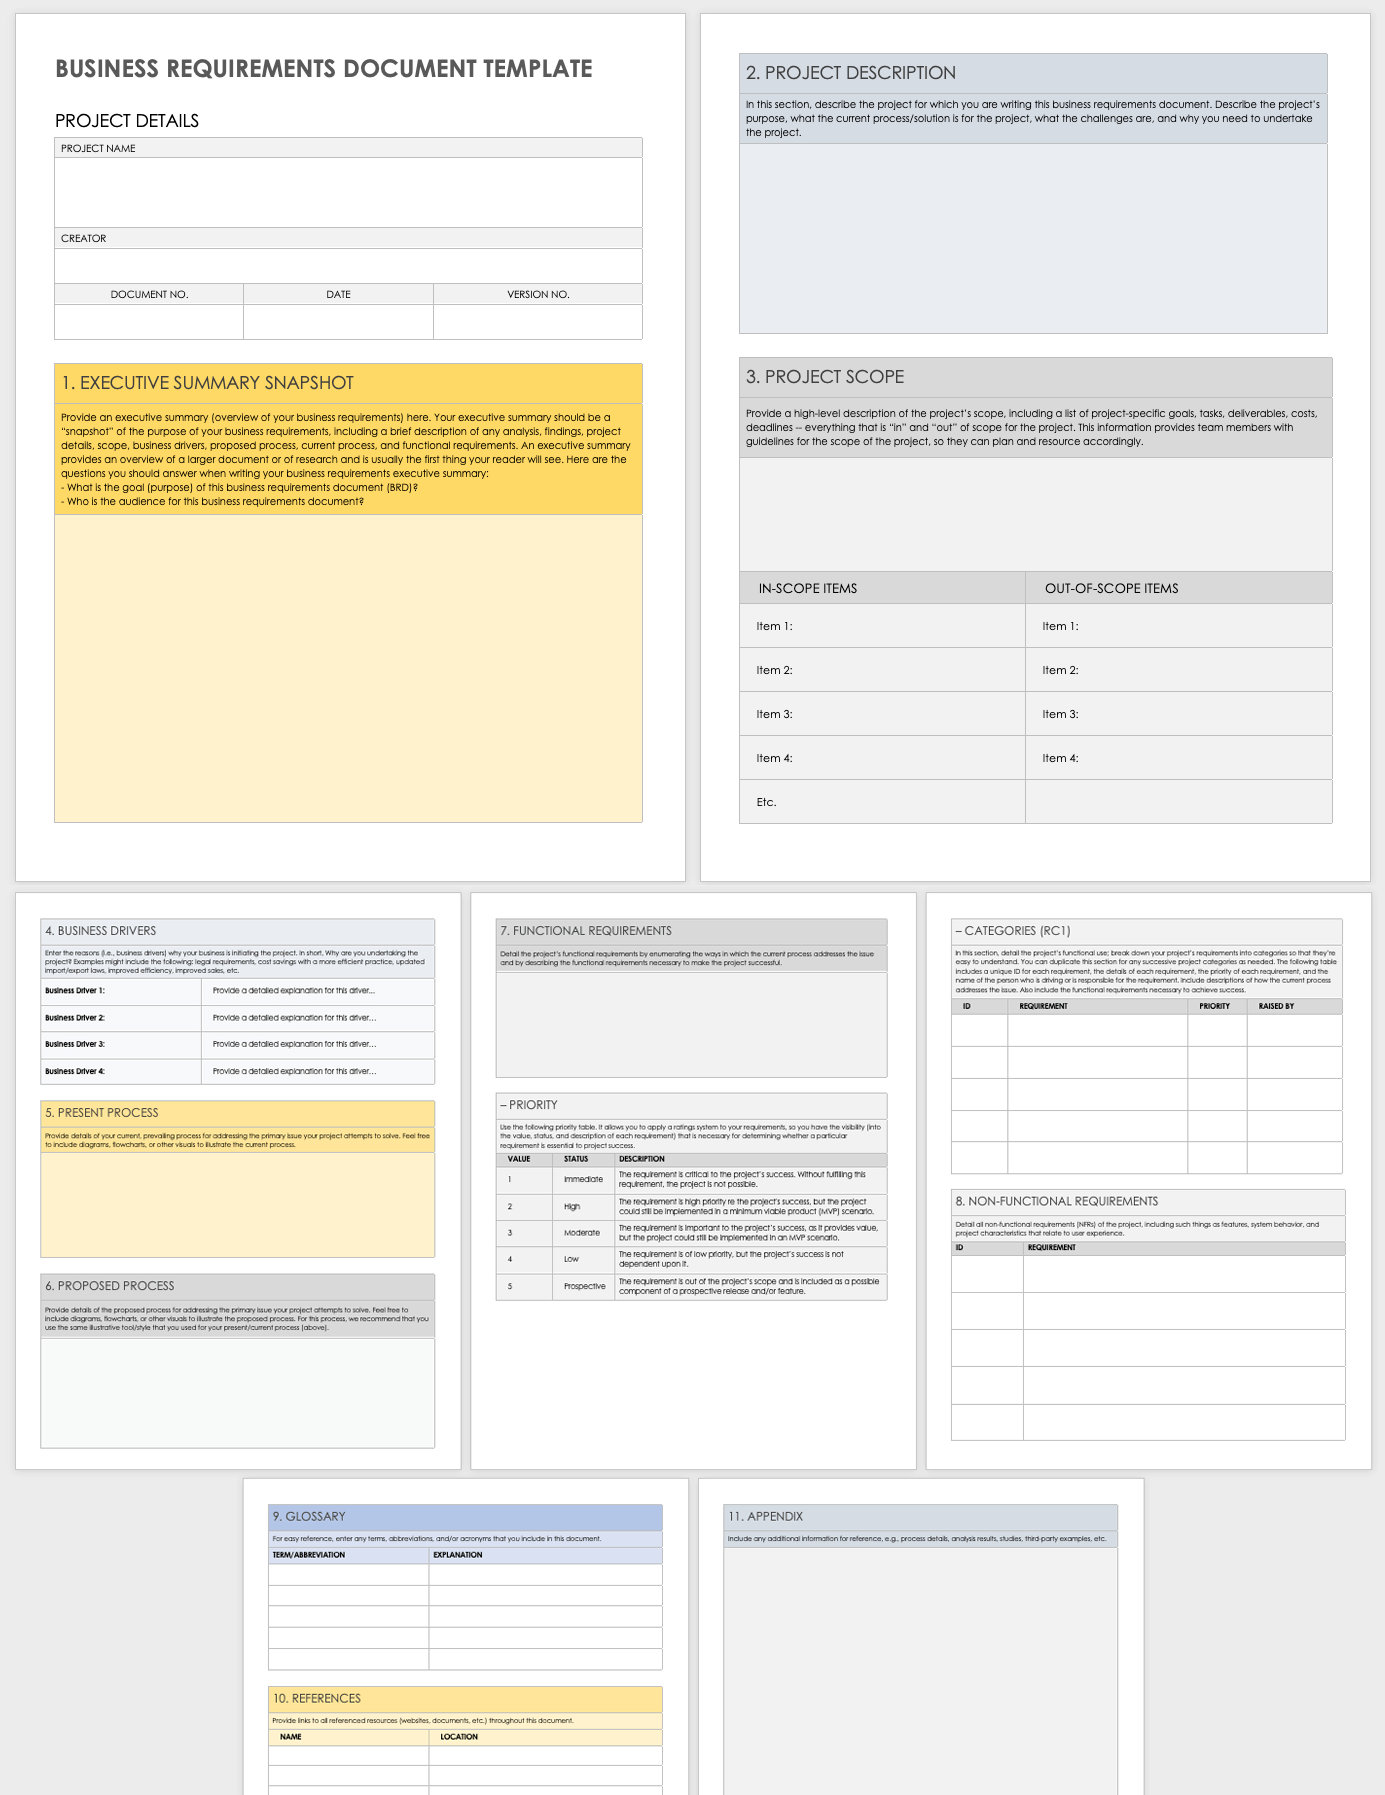
The acceptance criteria section is where most documents fall apart. Writers list what the feature does instead of what constitutes success. "The search function returns relevant results" is not an acceptance criterion. "When a user searches for 'blue running shoes size 10', the system returns at least three matching products within two seconds and displays them in order of relevance score" is. Testable. Measurable. Unambiguous. I once reviewed a document where the acceptance criteria for a reporting feature was literally "the report must be accurate." Accurate to whom. By what standard. Against what baseline. We rejected that document and rewrote it with specific tolerance thresholds and validation methods. It took two days instead of the three weeks we would have spent debugging disagreements later. Visual aids help. Wireframes, flowcharts, process diagrams. I prefer attaching them as referenced appendices rather than embedding them inline. Inline images get lost in formatting shifts and version differences. Appendix references stay stable across revisions. If you use a tool like Confluence or a shared drive, link to the artifacts and note the version number. Version numbers matter because requirements documents change. A lot. The version control is what keeps you from building against outdated specs. One counter-intuitive thing about these documents: shorter is usually better than comprehensive. A three-page document that covers the critical paths well beats a thirty-page document that tries to cover every edge case nobody will hit. I learned this from a senior BA who told me that requirements documents should fit on a single screen if possible. Not because detail is bad. Because unread documents don't influence decisions. If your stakeholders open a forty-page PDF and close it without reading past page three, you have wasted your time and theirs. Structure matters more than volume.
Here is another thing people miss. Requirements documents are living artifacts. They die the moment you mark them final and file them away. The best practice is to schedule a review before each major milestone. Six weeks in, twelve weeks in, right before QA begins. Update the document. Note what changed and why. The change log is as important as the requirements themselves. When someone asks why feature X works differently than documented, the change log tells you exactly when and how that divergence happened. The downsides of this approach are real. Requirements documents create a false sense of certainty. They make people believe the project is more predictable than it actually is. Stakeholders will treat the document as a contract even though it is a snapshot of understanding at a point in time. When reality diverges from the document, some teams blame the document instead of recognizing that divergence is normal. The workaround I use is to add a preamble that explicitly states the document represents current understanding and will evolve. It sounds defensive but it reduces the number of angry conversations about scope changes later. People respond better to transparency framed upfront than to damage control framed as emergency. Another limitation is that good requirements documents require good information from stakeholders. If your stakeholders don't know what they want, no amount of formatting will fix that. I have spent days refining the structure of a requirements document only to realize the underlying problem was that the product owner couldn't articulate the business objective clearly. In those cases, the document is doing cosmetic work on a structural problem. The fix is usually a workshop or a series of discovery sessions before you write anything. The document should reflect clarity, not create the illusion of it.
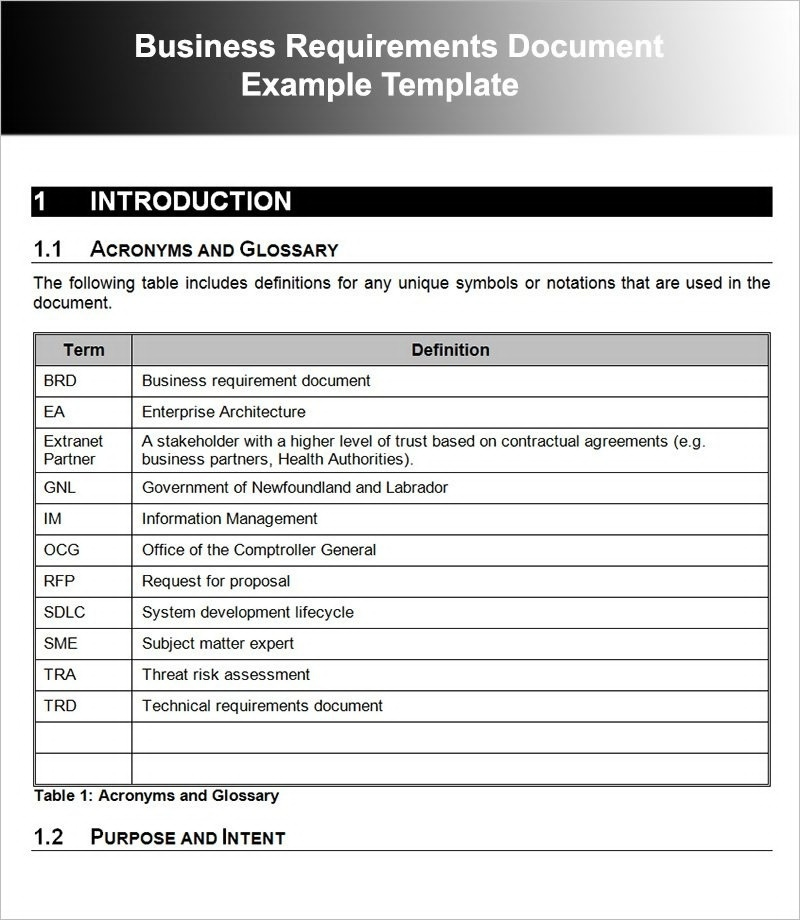
For a concrete example, here is a stripped-down version of a requirements section I wrote for a customer onboarding module last year. The functional requirement stated: "The system shall collect the following fields during registration: full name, email address, phone number, company name, job title, and password. The email field must be validated for format and uniqueness before submission. Invalid entries shall display an inline error message within one second of submission." The acceptance criterion stated: "A test account registration with a duplicate email address fails validation and displays the error 'An account with this email already exists' before any backend call is made." That specificity saved us from a bug where duplicate emails were accepted until the backend validation caught them, which created orphaned records in the database. Fixing that after deployment cost approximately two engineer-weeks. Writing the criterion precisely cost approximately forty-five seconds. If you want a template to start from, search for a Business Analyst Requirements Document Sample from reputable sources like the International Institute of Business Analysis or standard project management frameworks. Use them as starting points, not as templates to copy verbatim. Every project has different constraints and different stakeholders. A government compliance project needs different sections than a startup MVP. Match the document to the project, not the other way around. The most practical advice I can give is this. Write the document assuming the person reading it next month will not remember why you wrote anything the way you wrote it. Add context. Add rationale. Add the decision that led to a specific requirement. Five years ago I inherited a project where the requirements document explained that a particular field was required because of a downstream legacy system dependency. Without that explanation, future developers would have removed the field as unnecessary technical debt. The rationale survived across three project leads and two years. That is what makes a requirements document useful beyond the immediate project cycle.
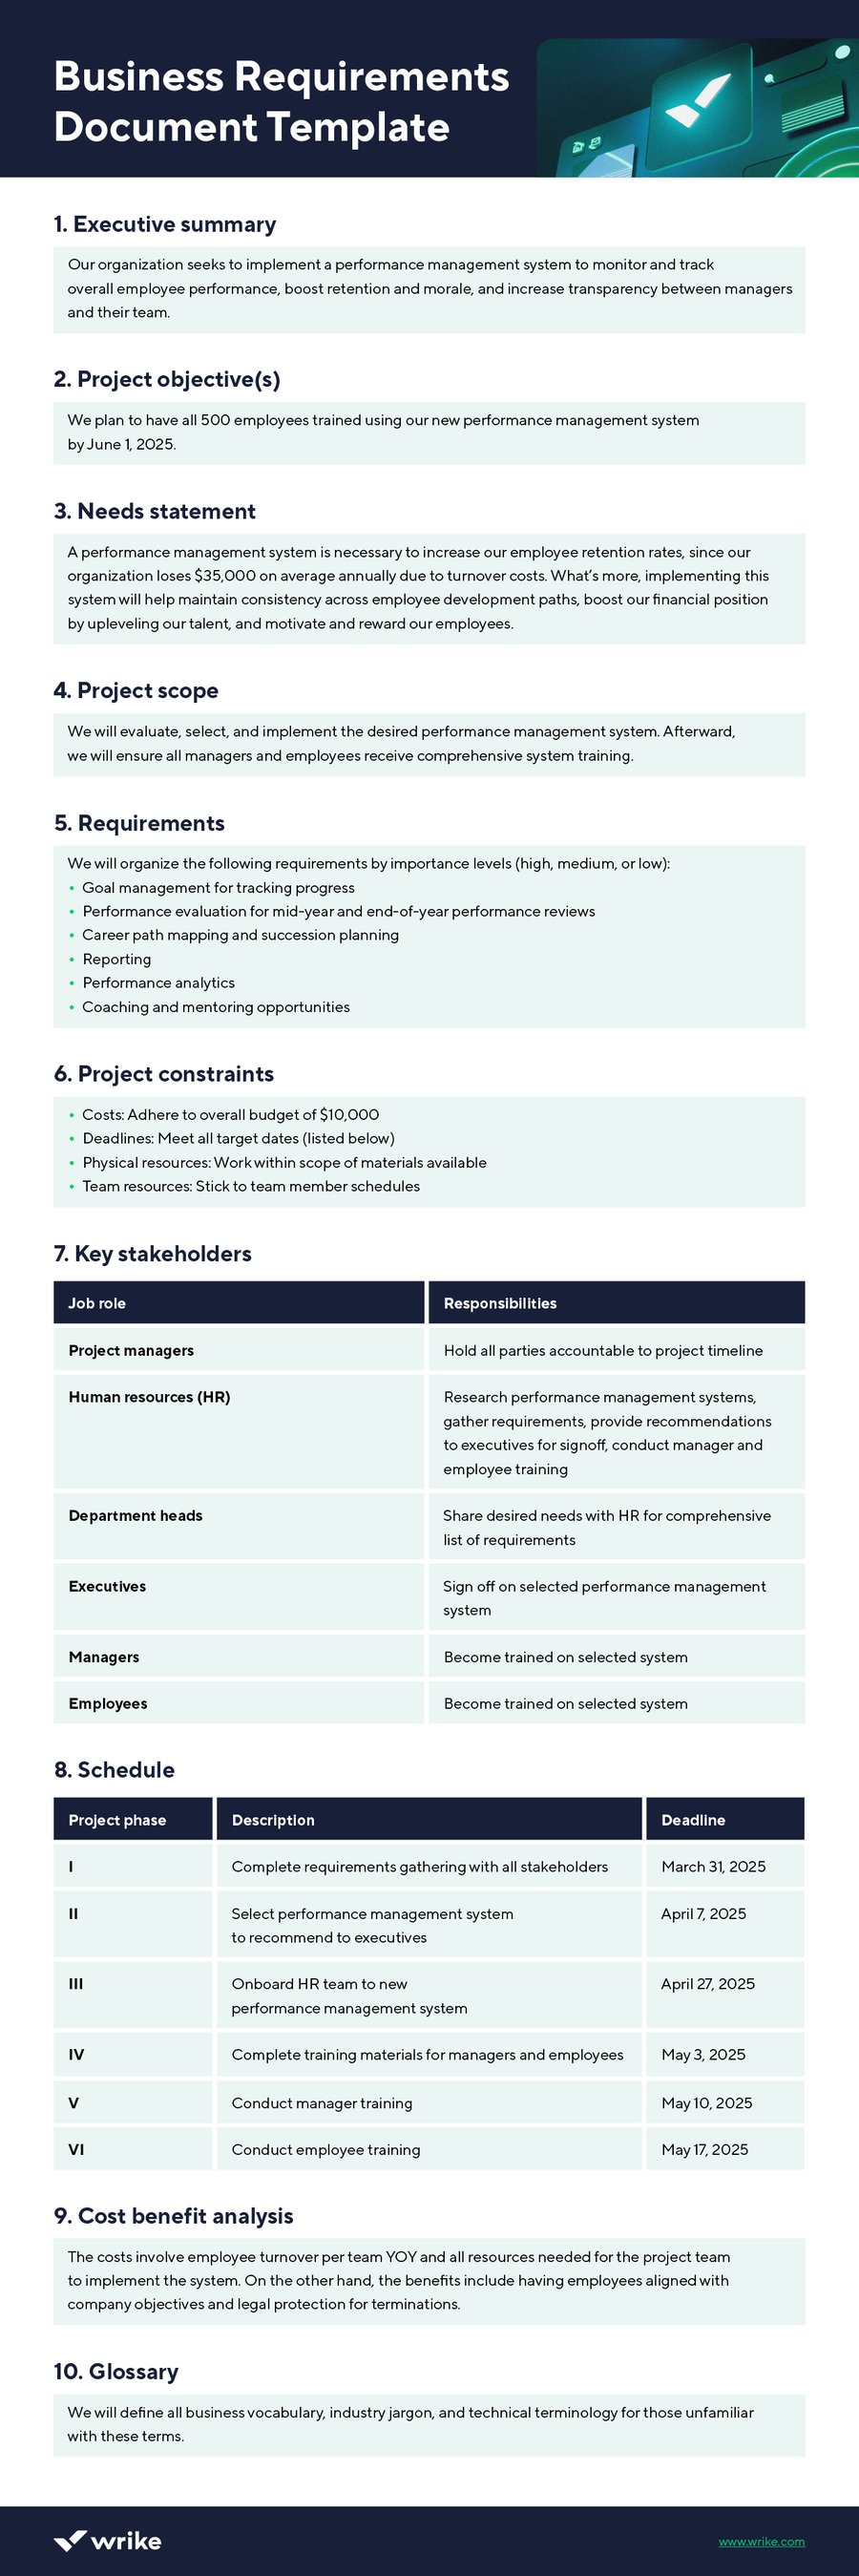
Keep the document updated. Keep the change log current. Keep it short enough that people actually read it. And stop treating it as the final word on what the system should do. It is the best available summary of what the team agreed to build at a point in time. That is all it ever needs to be.