Understanding the Difference Between Business Risk and Audit Risk
Most people conflate these two terms because they overlap on paper. In practice, they're treated completely differently by auditors and management. Business risk is the chance that a company fails to achieve its objectives or that external events impair its operations. Audit risk is the risk that the auditor delivers the wrong opinion on financial statements. One lives in the boardroom. The other lives in the audit file. I used to think mapping business risk to audit risk was straightforward. It isn't. The framework sounds clean until you're actually doing it on a live engagement with incomplete data and a client who treats documentation like a personal insult.
Why Business Risk And Audit Risk Matter Together
They matter because audit risk can't be properly assessed without understanding business risk first. ISA 315 requires you to identify and assess the risks of material misstatement, and that assessment starts with business risk. If you skip that step, you're auditing backwards. You'll find a lot of low-value transactions and miss the one entry that actually matters. Here's how I actually approach it in practice. I start with the entity and its environment. I review the latest annual report, the board meeting minutes, any regulatory correspondence, and the prior year audit file. Then I interview the CFO and the operations lead separately. You'll get different answers from each. That's useful. The gaps between those answers often point directly to where business risk is hiding.
The Practical Framework
Let me walk through the process without dressing it up. First, identify the business risks. These fall into categories: strategic, operational, financial, and compliance. A manufacturing company might face supply chain disruption as a strategic risk. A fintech firm deals with regulatory change as a compliance risk. You list them out before touching a single financial statement line item. Second, assess whether each business risk could lead to a material misstatement. This is the bridge. Not every business risk becomes an audit risk. Only the ones that could affect the numbers in the financial statements matter for the audit. Everything else is noise for your purposes.
Get the Full Details
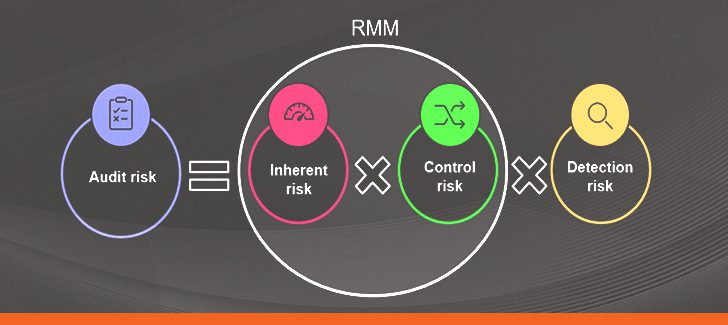
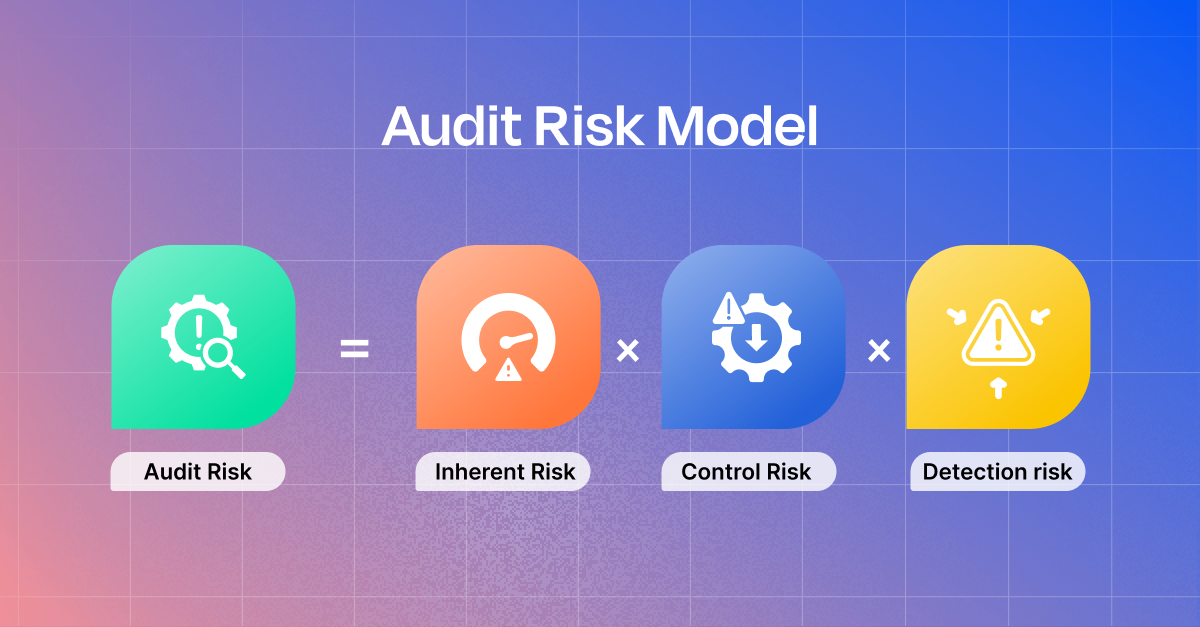
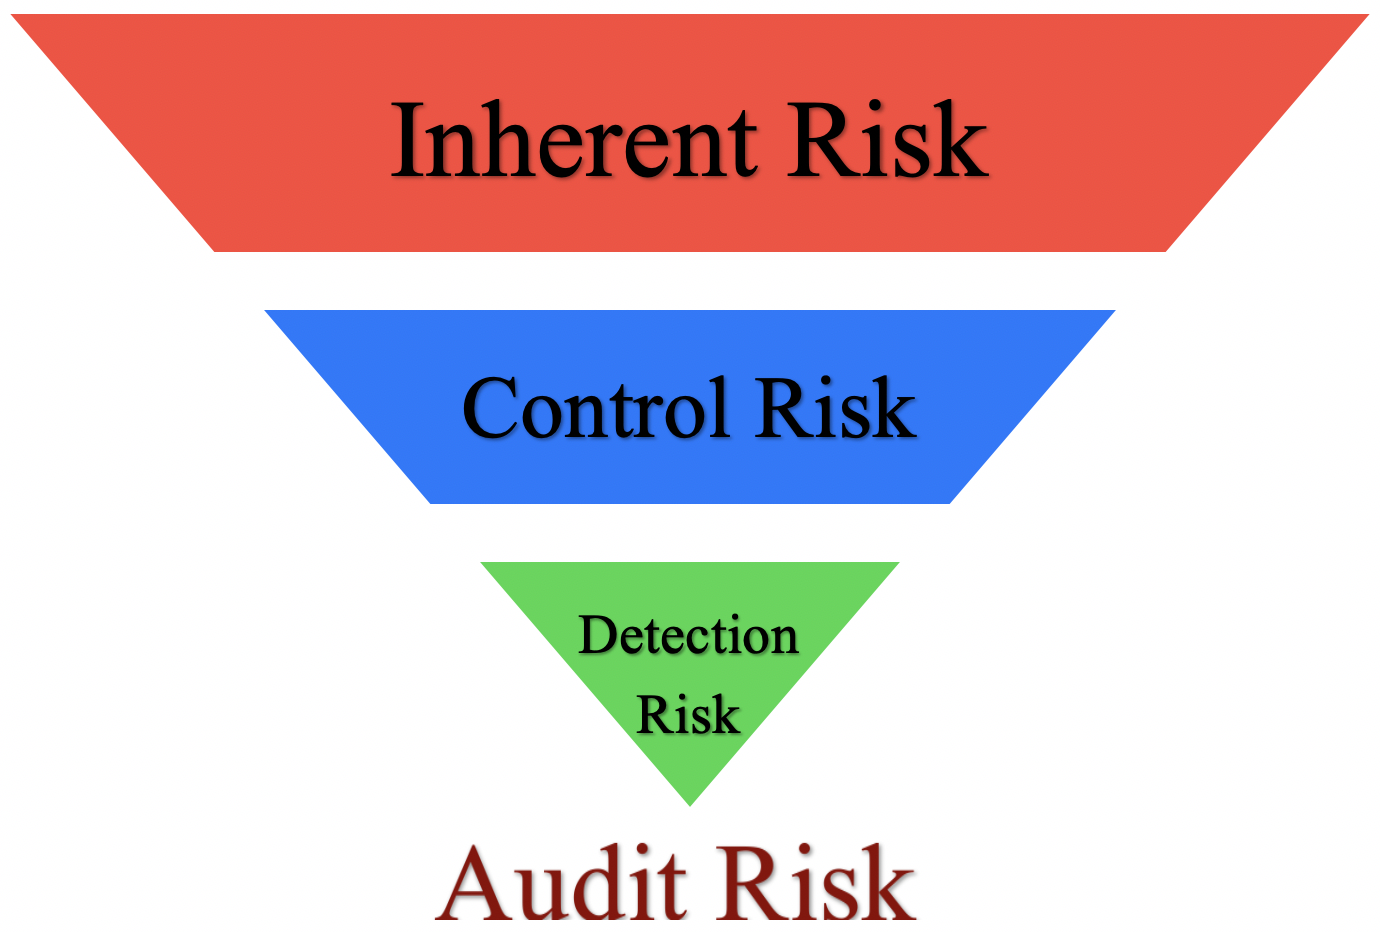
Third, determine the inherent risk and control risk for each bridged item. Inherent risk is where the error could naturally occur. Control risk is whether the company's safeguards are strong enough to prevent or detect it. I usually rate these on a simple three-tier scale: high, moderate, low. It's not fancy but it works when you're under time pressure. Fourth, calculate detection risk. This is what the auditor controls. If your assessed risk is high, you need more extensive substantive procedures. If it's low, you can rely more on controls testing. The formula is technically Detection Risk = Audit Risk / (Inherent Risk × Control Risk), but writing it down doesn't help you decide how many samples to pull. Here's a specific example from my own work. I was auditing a mid-market logistics company. Their business risk assessment flagged fuel price volatility as a significant strategic risk. The audit risk wasn't obvious at first because the financial statement impact seemed distributed across multiple line items. What I found was that the company was using long-term fuel supply contracts with fixed pricing, but they hadn't properly assessed whether those contracts still met the hedge accounting criteria under IFRS 9. The business risk was real. The audit risk was that the hedging instruments were misclassified and the related derivatives were either over- or under-valued on the balance sheet. I ended up pulling every active fuel contract, checking the original hedge designation documentation, and reperforming the effectiveness tests for two years of data. That took three weeks of a six-week engagement. But it caught a misstatement that would have been a material weakness in internal control if it had surfaced later.
Common Mistakes That Waste Time
Auditors frequently make two mistakes here. The first is treating business risk assessment as a checkbox exercise. They fill out a template from the previous year, update the dates, and move on. This is dangerous. Company circumstances change. A client who had stable margins last year might be facing margin compression this year due to a new competitor or a supply shock. The business risk profile shifts. Your audit approach has to shift with it. The second mistake is failing to document the link between business risk and audit risk clearly enough for a peer reviewer to follow. I've seen files where the connection was implied but not written down. When a reviewer asks why a particular account was deemed high risk, you need to point to a specific business risk and show the reasoning chain. "Management told me it was risky" doesn't survive inspection. Another thing nobody mentions enough: business risk assessment is often done by the senior on the team, while the audit risk assessment is done by the manager. The handoff is usually a quick email or a verbal summary. Information gets lost. I started requiring that the same person who writes the business risk assessment also drafts the initial audit risk response memo. It costs one extra hour of their time but eliminates the translation errors that show up later.
Tools and Templates
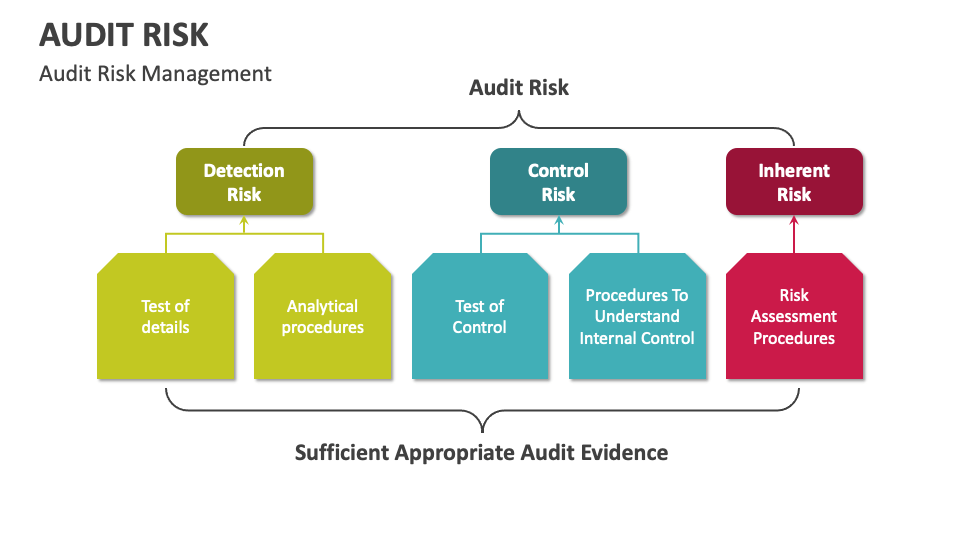
There are several widely used templates for documenting business risk and audit risk linkage. The Big Four firms have their own versions, and so do the professional bodies. I tend to use a hybrid approach: I start with a standard risk identification matrix from the audit methodology, then add a separate column for the audit risk bridge. This keeps the two assessments visible side by side. For smaller firms without access to expensive audit software, a well-structured spreadsheet works fine. You need columns for: risk category, specific risk, affected financial statement assertion, inherent risk rating, control risk rating, detection risk strategy, and the corresponding audit procedure. Five rows per major account is usually enough to cover the material risks without turning this into a full-time job. I don't have a download link to share because most proper templates are proprietary to the firms that make them. But you can build a functional version in an afternoon using the structure I described above. Just make sure it ties back to the relevant ISA standards so your documentation is defensible.
When This Approach Breaks Down
The framework I just described assumes you have adequate information from the client. In reality, clients sometimes withhold documents, delay responses, or provide sanitized explanations. When that happens, your risk assessment becomes speculative. You can't assess what you can't see. In those situations, the proper response is to document the limitation, expand your scope where possible, and consider whether the inability to assess risk adequately affects your overall audit opinion. I've had to qualify opinions because the client wouldn't provide sufficient evidence on revenue recognition practices for a new business segment. That's an ugly outcome but it's the correct one when the client blocks the process. Another scenario where this framework struggles is with emerging risks. Climate risk, cyber risk, and geopolitical instability don't fit neatly into traditional risk categories. They require a different mindset. You can't just check a box for "regulatory compliance" and move on when you're dealing with something like a new carbon tax that will affect valuation assumptions across half the balance sheet. I've found that bringing in a specialist consultant for these edge cases is worth the cost, even on smaller engagements.
The Bottom Line
Business risk and audit risk are connected but distinct concepts. Understanding the connection is what separates a competent auditor from a competent one. The process is methodical but not mechanical. You need to think critically about each client's situation rather than copying last year's file. The documentation has to be clear enough to defend. And when the framework doesn't cover your situation, you need to know when to escalate rather than force a square peg into a round hole.