So You Need To Actually Buy Python Software And Not Regret It
I spent about three years watching my team evaluate Python tooling, licensing, and services. We went through a bunch of expensive mistakes before we actually started doing it right. That's why I ended up writing this Buyer Guide For Python Checklist internally at first. It's now something I share openly because honestly, the same questions come up no matter what company you're at. Start with your runtime environment. This sounds obvious but nobody checks it properly. Python 3.11 versus 3.12 versus 3.13 matters more than most buyers realize. I once watched a team commit to a commercial package because it looked good on paper, only to discover two months later that the package had no wheel built for their target Python version. They were stuck running 3.9 on production while everything else was on 3.12. The workaround I eventually used was wrapping the package in a compatibility layer with venv isolation, but that cost us six weeks of engineering time I should never have lost in the first place. Before you look at a single product, write down your minimum and maximum Python versions. Write down your operating systems. Write down whether you need ARM support or just x86_64. This takes twenty minutes and saves you from buying something that won't run where you need it.
Next thing on the checklist: licensing. This is where people get hurt the most. Commercial Python packages come in flavors that aren't always obvious. MIT and Apache 2.0 are fine. BSD is fine. But GPL, AGPL, and even some LGPL variants can completely invalidate your commercial product depending on how you link or distribute it. I've seen a startup lose an entire funding round because they discovered their core dependency chain included a GPL-3.0 package they'd never audited. They had to rewrite the feature from scratch.
What To Look At When You're Actually Evaluating
Check the dependency graph. Most buyers look at one package and stop. Run pipdeptree or use pip-audit and look at what that package pulls in transitively. A package with zero dependencies is rare. A package with fifty is not automatic death but you need to understand why. Each transitive dependency is a potential security vulnerability, a licensing landmine, or a version conflict waiting to happen. Look at release cadence, not just recency. A package that released a patch every three weeks for two years is more trustworthy than one that released aggressively for six months and then went silent. Check the commit history on GitHub or whatever source host they use. Are there merges without reviews? Is the maintainer responding to issues? I keep a tab open in my browser with the last hundred commits of any package I'm considering for production use. It tells you more than any marketing page ever will. Documentation quality matters more than you think. Bad documentation usually means bad code or an unmaintained project. I once spent four hours reading docs for a commercial monitoring agent before realizing the examples in the docs didn't match the API the package actually exposed. The repo issues had three people flagging it. The maintainer never responded. We switched to a different tool and moved on.
Get the Full Details

Python Ecosystem-Specific Things Everyone Forgets
C-extension compatibility. If a package uses C extensions or compiled binaries, verify it supports your platform out of the box. Some packages work fine on Linux x86_64 but require source compilation on macOS ARM chips or Windows. Source compilation means you need a working build toolchain, which means your deployment environment has more moving parts. Docker solves this partially but adds its own complexity. I learned this the hard way when a CI pipeline started failing after a dependency update that removed pre-built wheels for arm64. NumPy and scientific stack compatibility. If you're doing any data work, Python version changes can break binary compatibility with NumPy, Pandas, and related packages. This is less of an issue than it used to be with modern Python, but it still bites people. Check the package's CI configuration or setup.py to see what NumPy versions it declares compatible with. Security audit trail. pip-audit, safety, and trivy are your friends here. Run them before you buy anything. The output you get will tell you immediately whether a package has known vulnerabilities in its dependency tree. I recommend making this a mandatory step in your evaluation process and keeping a record. You'll need it for compliance anyway.
The Cost Question Nobody Answers Honestly
Commercial Python tools often advertise per-seat pricing that sounds reasonable until you count everyone who actually needs access. A monitoring tool at $50 per developer per month looks cheap until you have thirty developers and five ops people. That's $1,750 a month. Annual cost is $21,000. Now compare that to a self-hosted alternative that costs maybe $2,000 a year in infrastructure and some engineering time to maintain. Open source doesn't mean free either. The total cost of ownership for open source tools includes your team's time to install, configure, secure, update, and debug them. I've seen teams pick "free" tools that ended up costing more in engineering hours than a commercial license would have. Be honest about your team's capacity. If you don't have someone who can maintain a self-hosted solution, budget for the commercial one or don't use it at all.
Red Flags That Should Make You Walk Away
No clear upgrade path from version to version. Python packages that don't document breaking changes between minor versions are a debt trap. You'll upgrade one day and everything breaks. Look for packages that follow semantic versioning and actually publish changelogs. If the changelog is just "bug fixes and improvements" across twelve releases, that's a warning sign. Single maintainer with no backup. This isn't always a dealbreaker but it's a risk factor. I once worked with a critical internal tool built entirely around a package maintained by one person who worked at a company that could lay him off at any time. We spent six months building an abstraction layer so we could swap the underlying package if needed. We never had to, but having that safety margin mattered. Pricing changes without notice. Some vendors raise prices quietly. I've had two separate tools do this within a year. Read your license agreement carefully. Look for clauses about price adjustment and termination rights. If you can't find the terms online, ask before you buy.
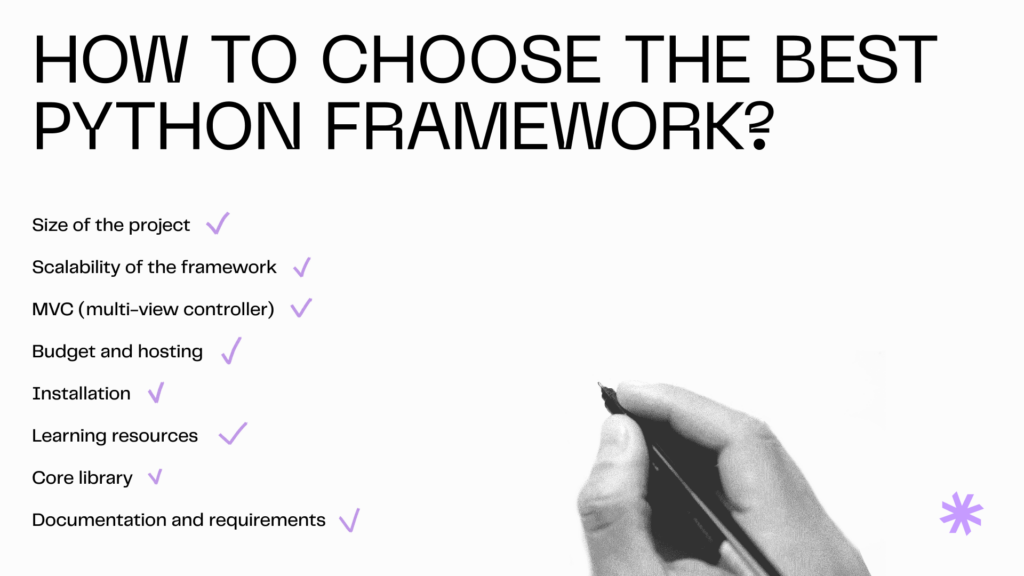
I keep a Google Sheet with every Python tool we've evaluated over the last few years. Columns for version, Python compatibility, license type, dependency count, known issues, and cost. It's boring and nobody else on the team uses it, but when I need to explain to a manager why we're switching tools, the sheet is usually enough. That's the real value of a Buyer Guide For Python Checklist — it's not the framework itself, it's the record you build by using it consistently.