Why Most Corporate Training Modules Fail at Compliance
I used to sit through mandatory privacy training every quarter that amounted to exactly thirty minutes of watching HR recite a script, click Next nine times, and sign off on a compliance checkbox. It was performative garbage that protected no one. Then I spent three years building actual training programs after a small breach exposed just how blind our teams were to basic data handling rules. The difference between a real program and a checkbox exercise is not content quality. It is behavioral design. Effective training needs to teach workers how to recognize when personal information enters their workflows, what they can do with it, and how to trigger the right internal processes when a consumer request lands on their desk. The standard approach is an annual e-learning module with a quiz at the end. That works for regulatory awareness but fails when someone gets a real request from a California resident asking for deletion of their purchase history. Nobody clicks the button because they do not know the request arrived at a general inbox instead of the privacy team's queue. I learned this the hard way. We had a legitimate training record on paper. A customer submitted a verifiable request through our support channel. Our frontline agent forwarded it to a random Slack thread instead of the designated privacy pipeline. By the time we caught it, the thirty-day window had expired. The agent had completed every required training module that year. They simply had no contextual guidance on request routing because our program treated everything as general compliance rather than role-specific procedure.
After that incident, I rebuilt the training around decision trees instead of policy documents. An engineer learns data mapping requirements and retention boundaries. A sales representative learns what to do when a prospect asks for their own records. A warehouse associate learns which shipping labels constitute personal information and how to redact before forwarding to a marketing team. The same foundational material applies to everyone, but the operational content diverges based on where people actually touch data. The counter-intuitive part is that more training often creates worse outcomes. I have seen organizations roll out fifteen hours of annual compliance content and watch incident rates climb. People absorb nothing from marathon sessions. Two focused hours per year with monthly micro-modules covering specific scenarios produces dramatically better retention. Workers remember what they practice, not what they passively consume. Another thing nobody talks about is the verification problem. Your training should cover how to authenticate a consumer request without creating friction that drives legitimate claimants away. I built a checklist that guides employees through the three verification steps required under CCPA: identity confirmation, authorization proof for representatives, and reasonable inquiry about the data subject's relationship to the records. The checklist prevents both over-verification, which delays responses and creates legal exposure, and under-verification, which opens you up to fraudulent requests. It is a narrow path and most programs skip it entirely.
There is also the scope question. CCPA covers personal information, which means any identifier that can be linked to a household, not just an individual. I trained a team to initially focus on individual data points like names and email addresses. We then expanded to IP addresses, device IDs, and location data after auditors pointed out we were treating household-level records as outside the framework. Training needs to reflect that household definition from day one, not as an addendum after someone catches a gap. One limitation I want to be honest about: no training program can fully cover every edge case your organization will encounter. A training module designed for a SaaS company dealing with digital service contracts will not translate to a brick-and-mortar retailer processing point-of-sale transactions with physical receipts. If your business model has unusual data flows, the best approach is scenario-based workshops rather than generic modules. Bring real request letters from actual customers into the room. Have people work through the verification and response steps using the real artifacts they will face. Measurement is another area where most programs fail. Tracking completion rates tells you nothing about competency. I started testing knowledge after each micro-module with short situational quizzes. Did the trainee route the request correctly? Could they identify which data categories applied? Were they aware of the opt-out mechanisms available? This takes about twenty minutes per quarter and gives you actual evidence that workers retained something from the training.
Get the Full Details
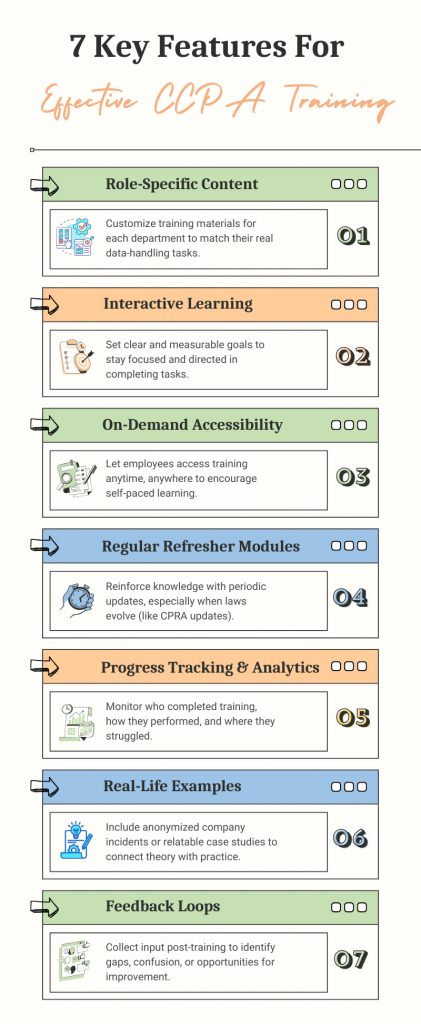
Record keeping matters more than you think. Regulators and auditors want to see dated training records with participant names, topics covered, and assessment scores. If you cannot produce that documentation within a reasonable timeframe, the training effectively did not happen regardless of what you delivered. Set up an automated archival system that backs up completion records and keeps them for at least four years. The biggest practical mistake I see is treating privacy training as an IT problem. It is an organizational behavior problem. People who interact with customer data daily need repeated, contextual reinforcement. Someone who handles returns once a month forgets the process faster than someone who receives consumer requests every day. Match the training cadence to the frequency of exposure. Daily users need monthly check-ins. Quarterly users need just-in-time refreshers when they are likely to encounter a relevant situation. If you are building a program from scratch, start by mapping every role that touches personal information. Interview those people about their actual workflows. Identify the moments where they make decisions about data handling. Build training content around those decision moments. Skip the policy recitation. Workers do not need to hear the full text of the statute. They need to know what to do next when a situation arises.
The cost of a well-designed program is not trivial. Budget roughly three to five hours of professional development time per employee annually, plus the internal hours required to create and maintain role-specific materials. For a mid-size company, that is a significant investment. But a single unresolved consumer request or a regulatory action costs far more in legal fees and reputational damage. I recommend pairing your training program with a simple internal reporting mechanism where employees can flag confusing situations without penalty. The goal is to surface edge cases before they become compliance failures. When someone encounters a request that does not fit the standard workflow, they should be able to escalate it quickly and get a clear answer documented for future reference. That documentation then feeds back into the training materials, keeping the program current without requiring a complete rebuild every time regulations evolve.
Building the Program Around Real Workflows
Stop designing training around what the law says and start designing it around what employees actually do. The gap between those two things is where compliance failures live.