What Actually Goes Into a Change Management Policy Template
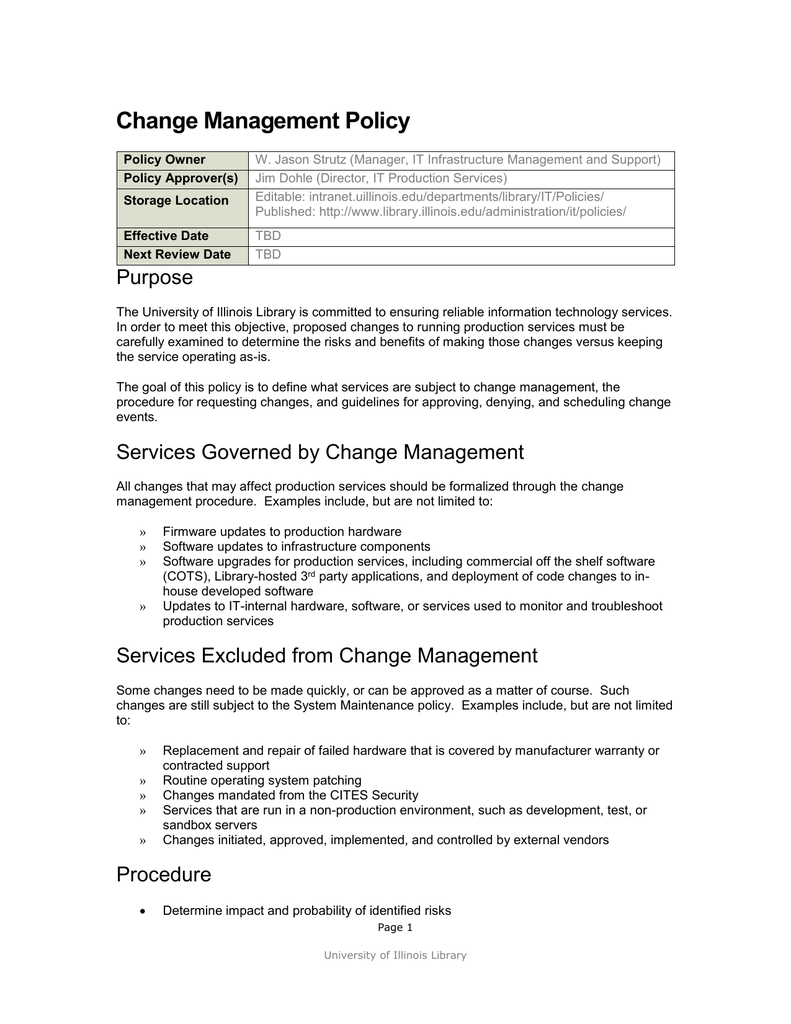
A change management policy template is a structured document that defines how an organization handles modifications to systems, processes, or infrastructure. It sounds straightforward, but getting it right requires more than filling in a few blanks. The policy needs to establish clear ownership, define risk tiers, lay out approval workflows, and set expectations for documentation and communication. Without those pieces, the template is just paperwork that nobody follows. I spent years watching teams build these documents from scratch, and the ones that actually got used shared a common trait. They were written by people who had been through a failed rollout and understood exactly where things broke down. A template should reflect real process friction, not an idealized version of how change management is supposed to work.
How to Build a Functional Change Management Policy Template
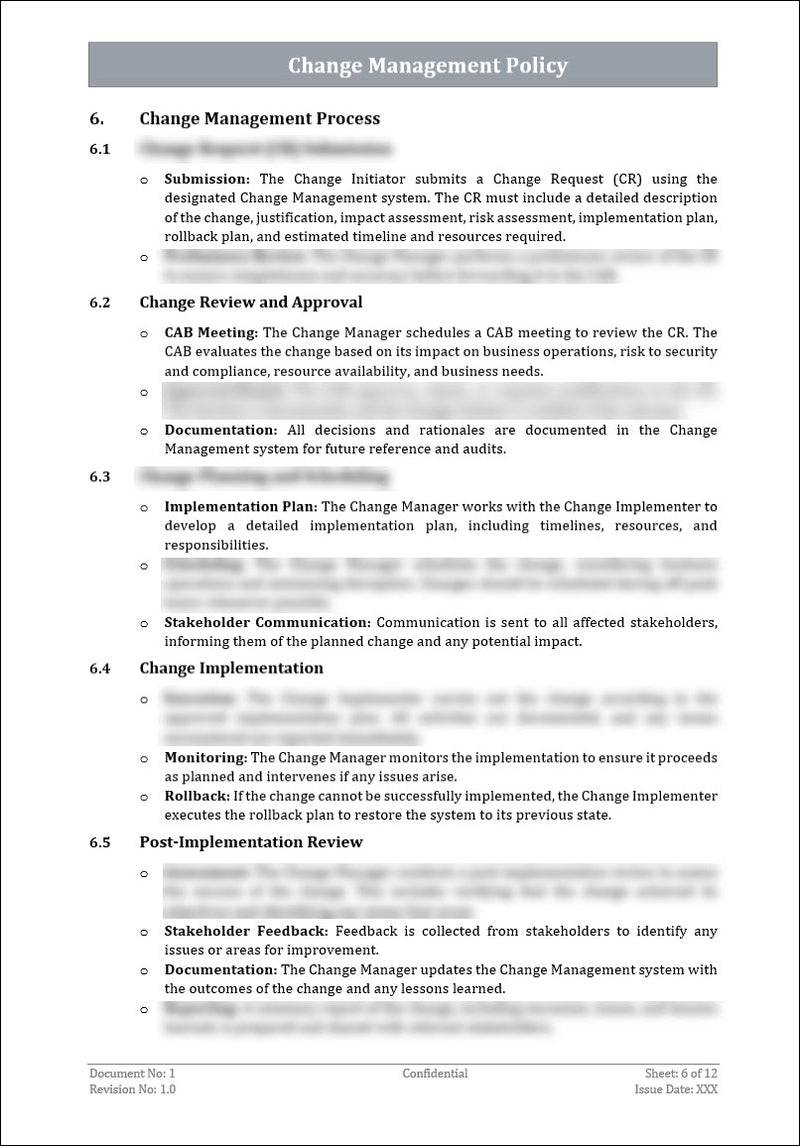
Start with the scope. Define what types of changes fall under this policy and what falls outside it. Standard changes like password resets or routine patch deployments are usually excluded from full review. Major changes like database migrations or core infrastructure overhauls require the most scrutiny. The middle ground is where most problems live. Network configuration updates, application deployments, and process adjustments need clear criteria for when they escalate to a full change advisory board review versus a simplified approval path. Next, map out the approval chain. Every change type needs a designated approver or group of approvers. In practice, this means identifying who actually has the authority and domain knowledge to approve a change. A senior developer should not be approving network changes. A network engineer should not be signing off on application deployments. Cross-domain approvals add friction, which is intentional, because the goal is to catch issues before they hit production. When I worked on a migration project, we learned this the hard way when an application owner approved a backend change without consulting the infrastructure team. The change went through fine on paper. It caused a cascading failure in staging that took six hours to resolve. After that, we required all cross-functional impacts to be documented in the change request itself. The template should include sections for risk assessment, implementation steps, rollback plans, and post-implementation review. Risk assessment is where most organizations do the bare minimum. They select a risk level without documenting the reasoning. A properly filled risk assessment section records the potential impact on availability, security, compliance, and business operations. It forces the change requester to think through failure scenarios before they happen. Rollback plans are equally neglected. I have seen change requests with no rollback procedure at all. When a deployment fails mid-way, the team is left improvising. A rollback plan should specify the exact steps to revert the change, the estimated time to complete it, and who is responsible for executing it. This usually adds about twenty minutes of prep time to a change request, but it can cut recovery time from several hours down to thirty minutes or less.
Common Pitfalls That Undermine Change Policies
The most common mistake is creating a policy that is too complex for the average team member to follow. When a change request form has forty fields and half of them are optional, people will either skip them or fill them with placeholder text. Keep the form focused. Require only the information that actually influences the approval decision. Everything else can be gathered during the review process if needed. Another pitfall is treating the policy as static. Organizations evolve, and the change management process should evolve with them. If your infrastructure has shifted from on-premise servers to cloud services, your policy should reflect that. Legacy approval chains that route everything through a data center manager make no sense in a cloud-native environment. I updated a client's policy to remove the physical server access requirement from their change forms and replace it with a section for cloud resource dependencies. That single change reduced the average approval time from three days to eight hours because the new approvers were already involved in the relevant discussions. There is also a tendency to over-index on compliance documentation at the expense of actual process adherence. Auditors love well-formatted change requests with complete signatures. But a perfectly formatted change request that skips technical review is worse than nothing. It creates a false sense of security. The policy should prioritize substance over appearance. If an approver signs off without reviewing the technical details, the policy has failed even if the paperwork looks clean.
Get the Full Details
Practical Considerations and Where This Approach Falls Short
A change management policy template works well in structured environments where changes are infrequent and planned. It is less effective in fast-moving development teams that push multiple deployments per day. In those contexts, the overhead of formal change requests can slow delivery without meaningfully reducing risk. Continuous integration and automated testing provide a different kind of safety net. For those teams, a lighter-weight change notification process may be more appropriate than a full change management framework. The template also depends on organizational culture. If leadership treats the policy as a bureaucratic hurdle rather than a risk mitigation tool, compliance will be minimal. People will rush through change requests to avoid delays. The policy only functions when there is genuine buy-in from management and when stakeholders understand the rationale behind the process. Training and communication matter as much as the document itself. One edge case that is worth noting involves emergency changes. The policy should have a defined path for urgent changes that cannot wait for the standard approval process. In practice, emergency changes are often used as a workaround for teams that find the regular process too slow. The distinction between emergency and standard changes needs to be clearly defined and enforced. I encountered a situation where a team was filing emergency change requests for routine updates simply because the standard approval queue was backed up. We addressed this by setting a maximum backlog threshold that triggered staffing adjustments instead of allowing emergency changes to become the default path. Emergency changes should also have a mandatory post-implementation review to ensure that the bypass was justified and that no shortcuts compromised the outcome.
Sample Structure for a Change Management Policy Template
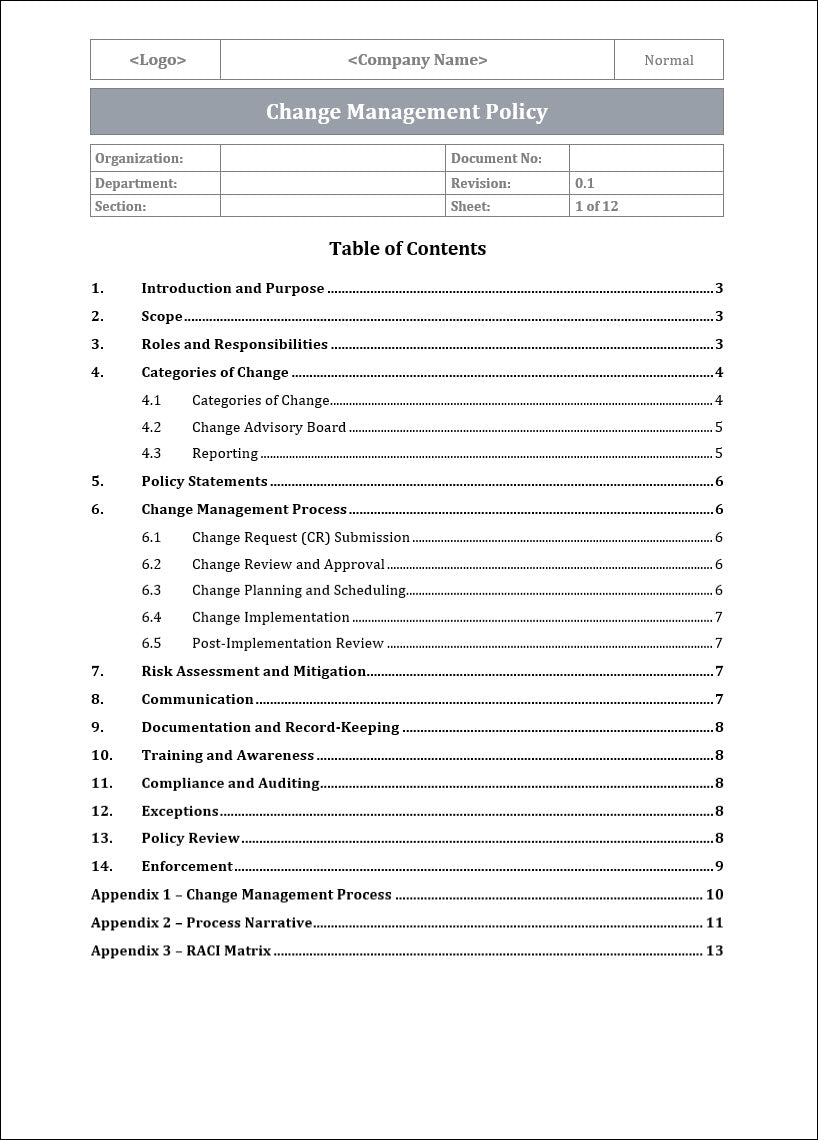
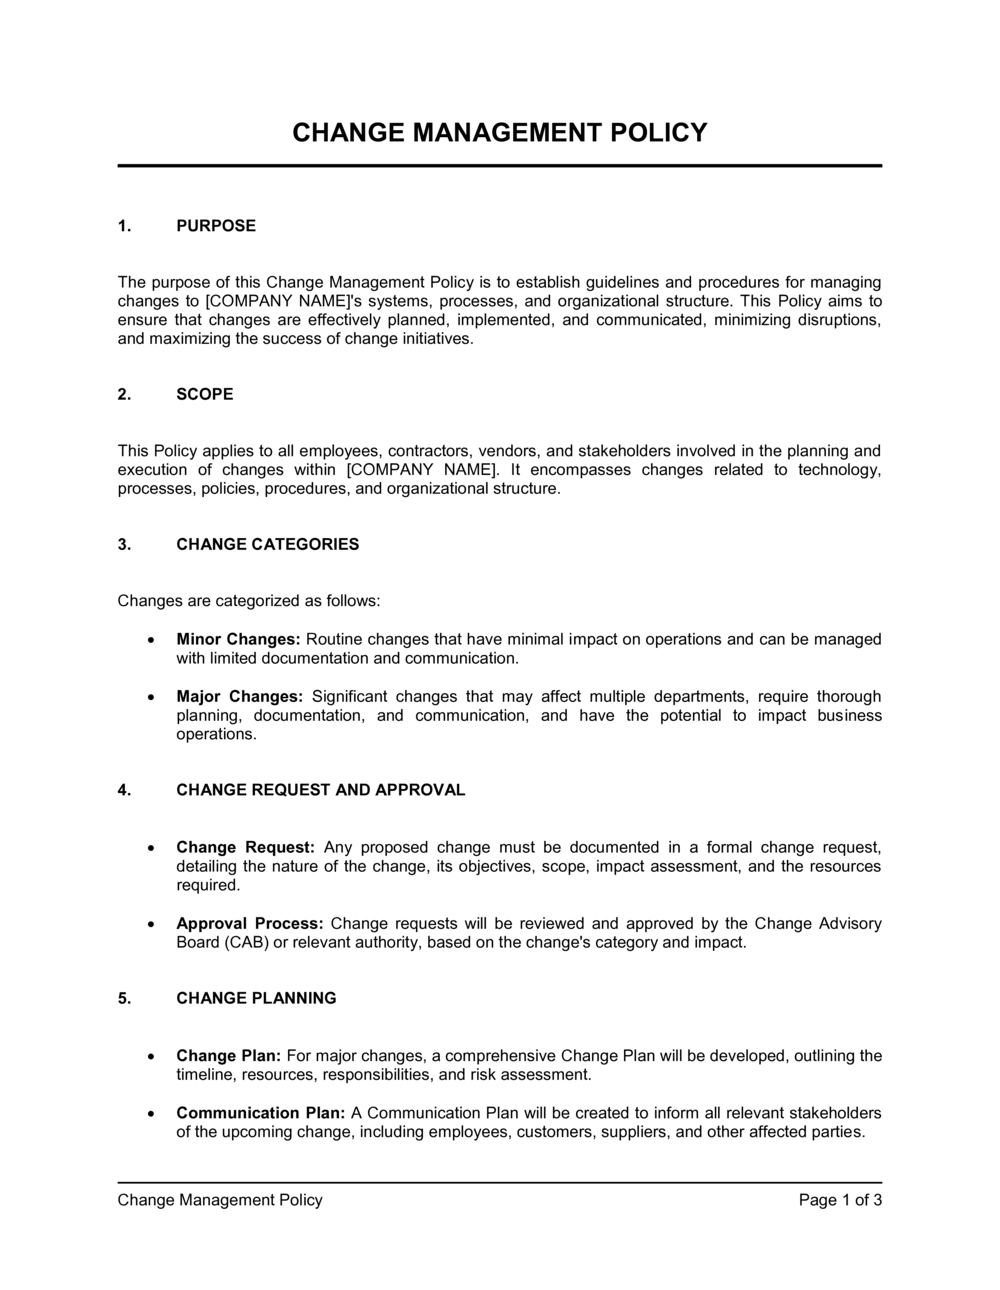
A functional document typically includes the following sections, though the exact format will vary depending on organizational needs. The purpose section states why the policy exists. The scope section defines what is covered and what is excluded. The roles and responsibilities section identifies who raises changes, who approves them, and who executes them. The change classification section establishes risk tiers with specific criteria for each level. The request process section describes how a change is submitted and what information is required. The approval workflow section maps the review and authorization steps for each change tier. The implementation and monitoring section outlines execution procedures and success criteria. The rollback section specifies recovery procedures. The review and audit section defines when and how changes are evaluated after implementation. The emergency change section addresses urgent modifications and their special handling requirements. The template should also reference supporting documents such as change request forms, risk assessment checklists, and rollback procedure guides. These supplements make the policy actionable rather than theoretical. Without them, the policy exists in isolation and is harder to enforce consistently. Downloadable versions of change management policy templates are widely available from IT governance frameworks and professional organizations. The quality varies significantly. Some are comprehensive and aligned with industry standards. Others are superficial and lack the operational detail needed for real-world use. It is worth comparing multiple sources and adapting the template to your specific environment rather than adopting one document verbatim. A generic template will not account for your particular infrastructure, regulatory requirements, or team structure. The best results come from starting with a solid reference and tailoring it to your context.
Building and maintaining a change management policy is not a one-time task. It requires periodic review, stakeholder feedback, and adjustments based on what the organization learns from actual change implementations. The teams that treat their policy as a living document tend to see better compliance and fewer incidents. The teams that set it and forget it usually end up either ignoring it completely or rewriting it under pressure after something goes wrong.