What Actually Works in Compliance Training Programs
Most organizations build their compliance training around a checklist mentality. They assign a dozen e-learning modules, take attendance screenshots, and file a completion report for the audit board. The problem isn't that this approach is entirely useless. The problem is that it teaches people to recognize compliance as something they pass rather than something they practice daily. I watched a mid-size fintech company go through exactly this cycle for three years straight. Their compliance officer treated annual training as a box-ticking exercise. Then a routine transaction flagged for suspicious activity wasn't escalated properly because the person who ran it had never encountered that particular pattern during their training. The program had covered AML concepts in broad strokes but never walked through edge-case transaction flows that didn't fit neatly into any single module. Effective Chief Compliance Officer Training has to be built around scenarios, not definitions. Someone learning about conflicts of interest should sit through a realistic negotiation simulation where the conflict isn't obvious. A person learning about data privacy protocols should work through a simulated incident where a junior analyst receives a request from law enforcement that technically exceeds what standard policy covers. These are the moments where the actual risk lives, and generic training misses them entirely.
Chief Compliance Officer Training: The Real Curriculum
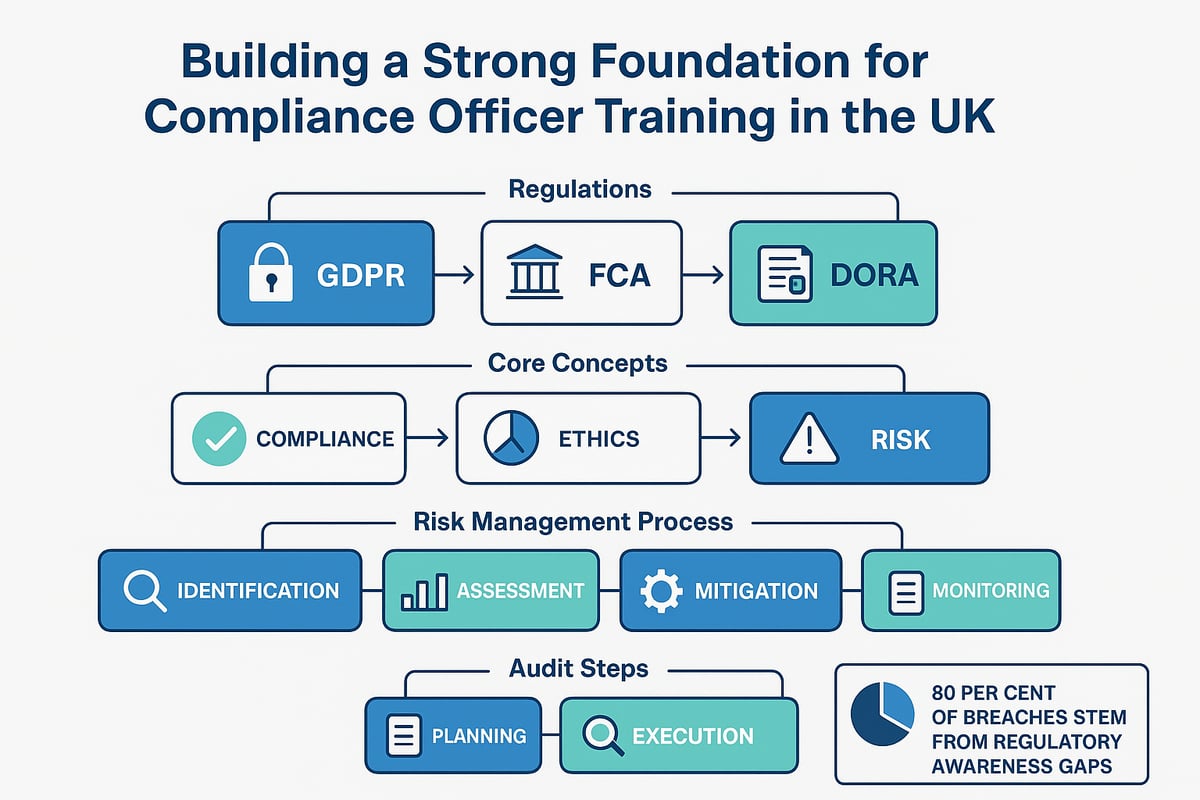
There are a handful of subjects that every solid program covers, regardless of industry. Regulatory fundamentals and jurisdiction-specific requirements form the baseline. Anti-money laundering and know your customer procedures come next, followed by data protection and privacy regulations. Code of conduct and ethics training is standard. Anti-bribery and corruption protocols, insider trading rules, and conflict-of-interest management round out the core modules. But the subjects that most programs skip are the ones that actually matter in practice. Incident response workflows are rarely trained properly. People learn what the policies say in isolation but never practice what happens when an incident occurs at 3 PM on a Friday, the primary contact is unreachable, and the initial assessment needs to happen before anyone has reviewed the full documentation. Escalation procedures follow the same pattern. You can read about escalation hierarchies all day. That doesn't prepare you for the moment when your direct supervisor is the subject of the investigation. Documentation standards represent another major gap. I've audited programs where staff could recite the compliance policy backward but had no training on what acceptable documentation actually looks like when a regulator asks for it. They'd write narrative explanations instead of structured records, miss timestamps, or use informal language that creates ambiguity under scrutiny. This is usually something you catch after the fact during an actual review, not something you can teach effectively through passive reading.
Where Standard Programs Break Down
The biggest failure mode I've seen in compliance training is the assumption that one program fits every role. A front-line sales employee needs different compliance touchpoints than a mid-level product manager who designs features touching customer data, who needs different training than a senior executive making go-to-market decisions. Most companies assign the same thirty-minute module to everyone and call it sufficient. Role-specific training depth is where most programs fall short. Finance teams need transaction monitoring drill-downs. Engineering teams need secure development lifecycle compliance checks. HR teams need hiring and termination protocol training that aligns with regulatory requirements. The generic module approach wastes time for people who already understand their domain's compliance obligations and fails to reach people who need specific guidance. Another structural problem is the timing. Training tends to happen at onboarding and then annually. Real regulatory changes don't respect those schedules. When a new data privacy amendment passes, the affected employees shouldn't have to wait twelve months to learn how it changes their daily work. The best programs I've encountered maintain a continuous update pipeline where targeted micro-training gets pushed within days of significant regulatory shifts rather than waiting for the annual cycle.
Get the Full Details

Assessment quality is a third weak point. Multiple-choice quizzes with four options and a sixty percent passing score create a false sense of competence. Someone can guess their way through a hundred questions and still not know what to do when facing a genuine compliance dilemma. Scenario-based assessments where the trainee has to make a decision and see the consequences of that decision in a simulated environment produce measurably better outcomes. I've seen programs that replaced their quiz-based assessments with branching scenario exercises and immediately saw a thirty percent reduction in compliance incidents over the following year.
A Real Problem and How I Fixed It
Three years ago I was dealing with a training gap that I couldn't solve through the existing program structure. We had a clear policy requiring escalation of any client interaction that involved a political exposure, but our training covered the definition of politically exposed persons without covering the operational reality of identifying them during live client meetings. People knew the term. They didn't know how to spot the warning signs in a conversation. The workaround was building a decision tree that mapped common conversation patterns to escalation triggers. Instead of asking people to memorize regulatory definitions, we gave them a flowchart that started with basic questions like whether the client or their close associates held public office and worked downward through increasingly specific scenarios. We paired it with recorded role-play sessions where trainers played clients dropping subtle hints about political connections, and the trainees had to navigate the conversation and decide when to escalate. This took two weeks to develop and deploy, but it addressed the actual gap in our training program that the standard modules were missing.
What to Look For and What to Avoid
If you're evaluating or building a Chief Compliance Officer Training program, start by asking about scenario frequency rather than topic coverage. A program that covers fifty topics through videos and quizzes is less valuable than one that covers twenty topics through interactive scenarios. The depth of practice matters more than the breadth of content consumption. Check whether the program includes refreshers triggered by regulatory changes, not just calendar-based annual requirements. Look for role-specific tracks rather than one-size-fits-all modules. Verify that assessments measure decision-making ability, not content recall. Ask about documentation training specifically, since that's almost always underdeveloped and almost always creates the most problems during audits. On the other side of the ledger, if a program relies exclusively on third-party video libraries with no customization for your industry or jurisdiction, treat that as a warning sign. If the only assessment method is a multiple-choice test with a low passing threshold, the program is measuring completion, not competence. If there's no mechanism for updating training when regulations change between cycles, the program is already behind the curve.

The most practical step you can take is to map your actual compliance incidents from the past two years against your training curriculum. Any incident type that isn't represented in your training materials represents a gap you need to fill, regardless of what the industry-standard curriculum claims to cover. Regulations set the floor. Your incident history should set the ceiling.