How Adaptive Authentication Actually Works in Practice
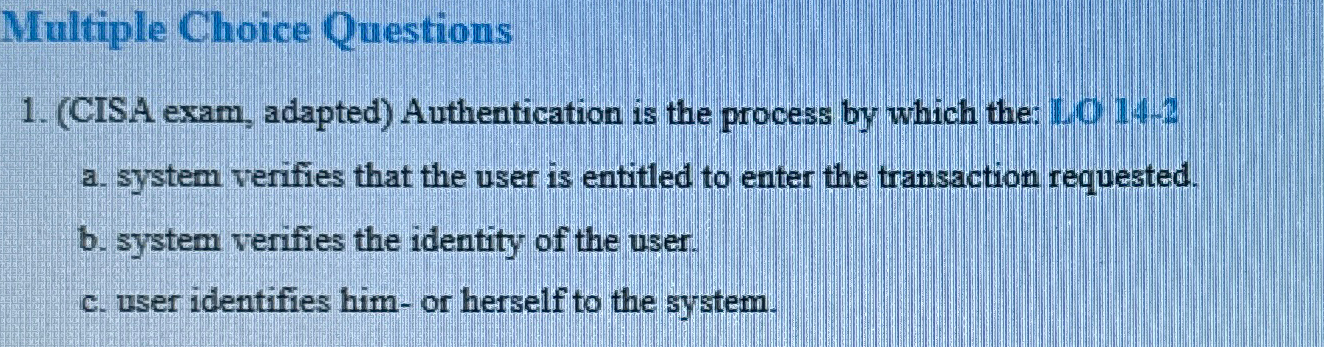
When you're studying for the CISA exam, adaptive authentication comes up because it is one of those controls that sounds straightforward on paper but gets messy the moment you try to implement it. Adapted authentication is the process by which the system dynamically adjusts the level of authentication required based on contextual risk signals. It is not a single technology. It is a framework that combines risk scoring, behavior analysis, and conditional access policies. The exam will phrase it exactly like that because they want you to recognize that adaptive authentication is fundamentally about continuous, context-aware evaluation rather than a one-time login check. The key word is adaptive. Static authentication asks once and trusts forever. Adaptive authentication keeps asking, "Is this session still trustworthy?" and adjusts accordingly. Here is how the mechanism works in the real world. When a user attempts to access a system, the authentication engine evaluates multiple risk factors simultaneously. The device being used has never been seen before, the login is coming from an unusual geography, the time of access falls outside normal patterns, or the user is attempting to reach a resource with elevated sensitivity. Each of these factors feeds into a risk score. That score then determines the authentication challenge. Low risk might mean the existing session holds. Medium risk triggers a second factor. High risk blocks the session entirely and routes it to manual verification.
I ran into a specific problem with this a few years back while configuring adaptive authentication for a financial services client. We had set up risk-based conditional access through Azure AD, and it was working fine until we onboarded a field operations team that regularly logged in from cellular networks with rotating IP addresses. Every single login was being flagged as suspicious because the geolocation kept changing rapidly. The risk score was essentially stuck at maximum, and the users were getting locked out constantly. The workaround was to create a device-based exemption policy that recognized their MDM-enrolled corporate phones as trusted regardless of network origin, while still requiring step-up authentication when they accessed high-sensitivity applications. This reduced false positive blocks by about eighty percent without weakening the actual security posture. One thing the exam tries to test is whether you understand the difference between adaptive authentication and simple multi-factor authentication. They are not interchangeable. MFA adds a second credential. Adaptive authentication adds intelligence to decide when MFA is needed, when it can be skipped, and when access should be denied outright. A common pitfall is assuming that deploying MFA satisfies adaptive authentication requirements. It does not. You can have MFA everywhere and still have zero adaptive risk evaluation happening. Another counter-intuitive point is that more data does not always mean better adaptive authentication. I have seen implementations where teams piled on too many risk signals and ended up with a system that was essentially random. The risk model became so complex that it started producing inconsistent results. A lean model with three or four well-calibrated signals typically outperforms a bloated one with dozens of weak indicators. Calibration matters more than volume. You need historical baseline data to tune the thresholds properly, and most organizations skip that step entirely.
The technical components you need to evaluate include a risk engine that aggregates signals, a policy engine that maps risk scores to authentication actions, and an identity provider capable of enforcing conditional access. These three pieces must communicate in real time. Latency in that chain directly affects user experience. If the risk evaluation takes more than two or three seconds, users notice. They complain. They find workarounds. And then your security team ends up disabling the control because of friction complaints. For the CISA exam specifically, focus on the audit perspective rather than the implementation details. They want you to know how to evaluate whether an adaptive authentication control is designed effectively and operating as intended. Key audit questions include whether risk factors are appropriate for the environment, whether the risk scoring model is validated and calibrated, whether the policy decisions are logged and auditable, and whether there is a documented process for reviewing and adjusting thresholds over time. An adaptive authentication system that has not been reviewed in six months is probably degrading in effectiveness. One limitation worth noting is that adaptive authentication does not solve identity theft on its own. If a threat actor has compromised both the primary credential and the secondary factor, the risk model may still grant access if the behavioral signals align closely enough with the legitimate user pattern. This is why adaptive authentication should be layered with anomaly detection and user behavior analytics, not treated as a standalone solution. It reduces risk significantly but does not eliminate it.
Get the Full Details

The exam also likes to test your understanding of session management within adaptive authentication. A session that starts with low risk can escalate to high risk if the user's behavior changes mid-session. Accessing a payroll system from a marketing user's session should trigger re-authentication even if the initial login was routine. Make sure you understand that adaptivity applies across the entire session lifecycle, not just at the point of entry.