The uncomfortable truth about CISA exam prep most people ignore
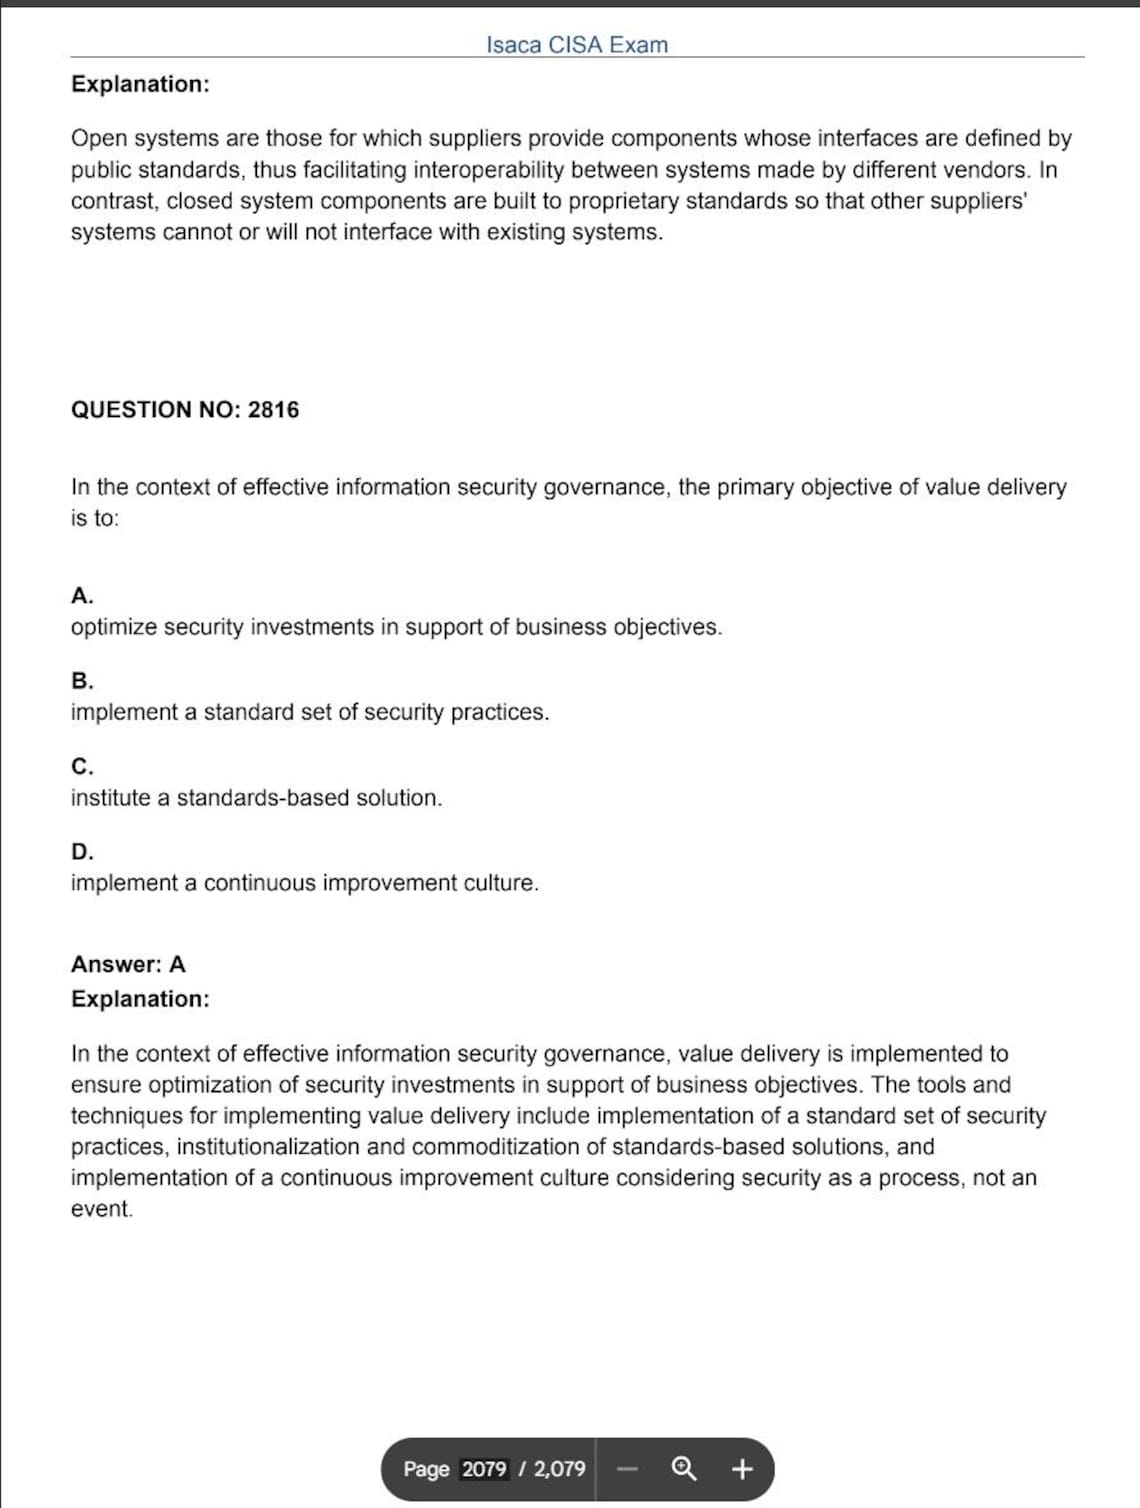
Most candidates treat CISA practice questions as a checklist exercise. You open a bank, answer forty questions, note the score, move on. That approach leaves roughly 60% of people failing on their first attempt, sometimes more. The real problem isn't the volume of questions. It is how you interact with the ones you get wrong. The exam does not reward recall. It rewards a specific decision-making pattern that ISACA built deliberately into every question. I spent years working in audit governance before I ever sat for the exam. When I opened a random Cisa Practice Questions And Answers document online, the first thing I noticed was that the wording felt almost conversational. Then I realized that was the trap. ISACA writes questions to sound like a straightforward situation until you hit the answer choices. The right answer is rarely the one that sounds the most correct. It is the one that aligns with their four-phase model: assess risk, evaluate controls, determine impact, recommend action. Every single question maps back to that sequence, whether it is talking about cloud migrations, incident response, or change management.
How Cisa Practice Questions And Answers should actually be used
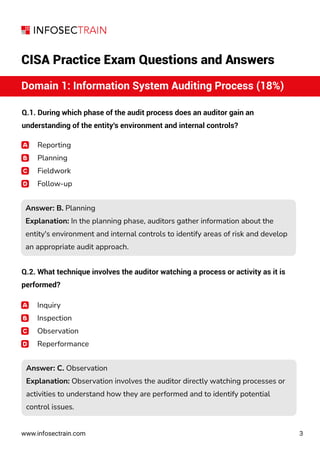
Start by doing a full timed section before you do any studying. This sounds obvious, but most people skip it and jump straight into passive reading. I scored 42% on my diagnostic. That number told me exactly which domains were bleeding points. ISACA divides the exam into five domains, but they are not weighted equally. Domain 1 (Audit Process) and Domain 3 (Information Systems Auditing) together account for nearly half the exam. If your practice questions show weakness there, nothing else matters until you fix those gaps. When you review wrong answers, write down why the correct choice is correct in your own words. Then write down why each distractor is wrong. The second part is where most candidates waste time. A distractor is not random. It is usually a real practice that sounds reasonable but belongs to a different phase of the audit lifecycle. For example, recommending a new tool is never the right first step in an ISACA question. The first step is always understanding the existing environment and the control gaps. If you can identify which phase a wrong answer violates, you start recognizing patterns across every domain. Use questions that mimic the actual exam format. That means scenario-based stems with four options where one is clearly right and three are plausible. Avoid question banks that use true/false or multiple-select format unless they explicitly label them as supplemental material. ISACA does not use those formats on the actual exam. Spending twenty hours on true/false questions gives you zero return on your time investment.
A specific problem I ran into and the workaround
During my second prep cycle, I kept missing questions about vendor risk assessments. The scenario would describe a company outsourcing its payment processing to a third party, and I would pick the answer about conducting a full internal audit of the vendor first. Every time. The correct answer was always to review the existing contract and SLA terms before doing anything else. I realized my brain was defaulting to a traditional auditor mindset. ISACA wants you to think like a risk assessor who reads documentation before taking field action. The workaround was painfully simple. I started annotating every wrong answer with a color code. Red meant I violated the assess-before-act principle. Blue meant I recommended a solution before evaluating the current state. Green meant I picked an answer that was technically correct but answered the wrong question entirely. After two weeks of this, my error patterns shifted from domain-specific mistakes to fundamental reasoning mistakes, which are much easier to fix because they follow the same rule across every question type.
Get the Full Details
Common pitfalls that sink otherwise prepared candidates
Timing is one of the quiet killers. The exam gives you about three minutes per question on average, but certain question types drag longer. Scenario clusters, where one case study feeds four or five questions, will eat your buffer if you overthink them. I learned to flag and move on within ninety seconds if I was between two answers. Returning later with fresh context usually resolves it. The alternative is running out of time on Domain 5 questions at the end, which is brutal because those are often the easiest questions on the test. Another trap is over-relying on acronyms and industry jargon in practice questions. Some question banks copy-paste language from frameworks like COBIT, NIST, or ISO without clarifying which framework the question assumes. ISACA references COBIT implicitly in many questions, especially in Domain 1 and Domain 2. If you answer using NIST SP 800-53 logic on a COBIT-framed question, you will pick the wrong answer every time. Read the question for framework signals. Words like control objectives, governance framework, and maturity models point toward COBIT. Words like threat landscape, mitigation strategies, and security control families point toward NIST. There is also the false confidence problem. Candidates who score 70% or higher on practice exams routinely underestimate the actual exam difficulty. Practice exams often lack the subtle wording shifts that ISACA uses to differentiate between strong and weak candidates. A 70% practice score might translate to a 55% to 60% equivalent on the real exam. Treat any practice score above 75% as a best-case scenario, not a guarantee.
Where CISA practice materials fall apart and what to use instead
Not every question bank is equal. Some are accurate but outdated, still referencing on-premises infrastructure as the default assumption rather than cloud environments. ISACA has adjusted its exam to include cloud auditing, container security, and DevOps practices, but many third-party question sets have not caught up. If your practice questions do not touch on AWS or Azure audit considerations, Sarbanes-Oxley implications for SaaS contracts, or continuous monitoring concepts, you are studying for a version of the exam that no longer exists in its entirety. The official ISACA CISA Review Manual and Question Bank is the only resource I trust completely. It is expensive, and the questions sometimes feel dry, but they reflect the actual exam philosophy accurately. Supplement it with the CISA Handbooks for each domain, published annually. Those handbooks are shorter and more focused than the manual, and they explain the reasoning behind each domain without padding. If you need additional practice, the ISACA Community forums have experienced candidates who share real exam themes, not actual recalled questions, which is important because sharing real questions violates the non-disclosure agreement. Study groups also help, but only if you vet them carefully. A study group where everyone shares the same outdated question bank reinforces the same misunderstandings across five people instead of one. The best groups I have seen combine the official manual, recent ISACA webinars on exam updates, and peer discussion focused exclusively on why wrong answers are wrong. Time spent arguing over a question is time well spent if it is structured correctly. Time spent confirming each other's biases is wasted.
One more thing people overlook: the exam is adaptive in certain delivery formats. If you are taking the computer-based version through a testing center or the remote proctoring option, the difficulty of subsequent questions adjusts based on your performance. Getting the first batch of questions right pushes you into harder material. Getting them wrong makes the exam easier, but scoring well on easy questions does not compensate for missing hard ones. Your final score depends on how you handle the challenging questions, not how quickly you breeze through the straightforward ones. This is another reason practice questions that are uniformly easy or uniformly hard both fail to prepare you properly. You need a balanced set that mirrors the adaptive distribution.