Getting the Basics Right
Cisco ASA firewall configuration is one of those things that looks straightforward until you actually have to do it under pressure. I've spent years dealing with these boxes, and the thing I notice most is that people skip the fundamentals because the CLI looks simple. It's not simple. It's just deceptively simple. The ASA operates on a security level model. Every interface has a number between 0 and 100. Traffic flows from high security level to low security level by default. It does not flow the other way unless you explicitly permit it. This seems obvious in theory but I still see engineers confused when return traffic gets dropped and they can't figure out why. There's also the concept of inspection. The ASA inspects traffic at Layer 7 for common protocols like FTP, HTTP, and SIP. By default, the ASA enables inspection for a bunch of protocols. This is usually a good thing but it causes problems when you're running applications that embed connection information in payloads. The ASA modifies those payloads to make the stateful inspection work, and sometimes it breaks things that shouldn't be broken.
I once had a client running a VoIP system over SIP. Every incoming call worked fine. Outgoing calls failed silently. We spent three hours troubleshooting NAT before I realized the ASA was rewriting the SDP payload incorrectly. The fix was dropping the default SIP inspection and writing a manual inspect rule with the correct parameters. Standard troubleshooting procedure at that point was disabling inspection protocol by protocol until the problem stopped, which is actually a valid debugging technique.
Interface Configuration
You start with interfaces. You assign names, IP addresses, and security levels. This sounds trivial but the order matters. If you configure the outside interface last and make a typo, you can lock yourself out of the box because the management access might be bound to an interface you just misconfigured. Always configure the inside interface first. Then the outside. Then anything else. Use the no nameif command to clear a mistake before reapplying it rather than trying to overwrite existing configuration. The ASA does not always behave well when you reapply a modified nameif command without removing it first.
Get the Full Details

Basic Interface Setup
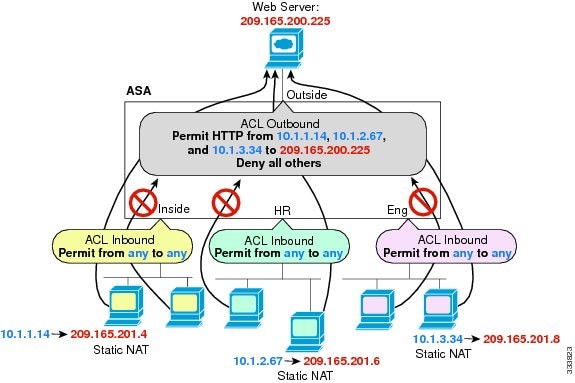
Here's what a standard setup looks like. You enter global configuration mode, then interface configuration mode for each port. You assign an IP, give it a name, and set the security level. Below is a realistic example using a typical dual-homed deployment. That write memory command is important. The ASA does not save configuration automatically. If the box reboots before you run that command, everything you just typed disappears. I know this sounds stupid but I've lost entire configurations because someone walked away thinking the changes were persistent. They are not. ACLs on the ASA are different from what you might be used to on routers. The ASA uses stateful ACLs. When you permit inbound traffic, the return traffic is automatically allowed without needing a corresponding outbound rule. This is because the ASA tracks connection state. This simplifies configuration significantly compared to stateless firewall platforms.
However, there are nuances. The ASA evaluates ACLs from top to bottom. The first match wins. This means placement order matters more than most people realize. A broad deny rule at the top of an ACL will block everything below it, even if those entries look like they should permit traffic. I ran into a situation where a vendor sent us a list of ACL entries to "just add to the bottom." We added them to the bottom. Nothing worked. The top of the ACL had a permit statement from any to any that was catching all their traffic before the new rules ever got evaluated. It was a remnant from an old design someone never cleaned up. We spent forty minutes tracing the rule order before finding it. Always review the full ACL before appending to it.
Standard ACL Pattern
access-list OUTSIDE_IN extended permit tcp any host 203.0.113.10 eq 443
access-list OUTSIDE_IN extended permit tcp any host 203.0.113.10 eq 80
access-list OUTSIDE_IN extended deny ip any any log
The log keyword on that deny rule is deliberate. You want to see what traffic is being blocked. Without logging, you're flying blind. The downside is that logging generates traffic and can fill up your syslog server if you're not careful. Set a reasonable log interval. I use log-interval 60 on broad deny rules to throttle the output. NAT on the ASA has gone through multiple redesigns across versions. The modern approach uses the object-based NAT syntax introduced around version 8.3. If you're working with an older setup, you might encounter the old syntactical format. Both work. Both are confusing in different ways. The object-based approach is cleaner. You define network objects first, then reference them in NAT rules. This makes the configuration readable and maintainable. The old approach buried network definitions inside NAT statements, which made troubleshooting a nightmare.

Here's how you'd set up a basic static PAT for a server behind the ASA:
object network SERVER_INT
 host 192.168.1.100
 nat (inside,outside) static 203.0.113.20 service tcp 443 443
This maps the internal server at 192.168.1.100 to the outside address 203.0.113.20 on port 443. Traffic hitting that external address gets translated and forwarded to the internal server. The service keyword handles port translation if needed. The catch with NAT is that you need to think about both directions. NAT on the ASA translates source addresses for outbound traffic and destination addresses for inbound traffic. But the ACL still references the original addressing scheme, not the translated one. This trips people up constantly. The ACL on the outside interface checks the destination address as it appears after NAT translation, not the original internal address.
Common Pitfalls
One issue that causes a lot of headaches is the implicit deny. The ASA denies all traffic by default unless explicitly permitted. This is correct behavior but some organizations migrate from perimeter firewalls that used a default-allow model. When they move to ASA, their applications break because nothing is permitted anymore. You need a migration plan that identifies all required traffic flows before applying the new ruleset. Another problem is ASDM vs CLI inconsistency. The Adaptive Security Device Manager GUI sometimes shows different information than the CLI. I've seen the ASDM display an ACL as active when the running config showed it was removed. Always verify through the CLI. The ASDM is convenient for quick changes but it is not always authoritative. Version compatibility is another factor. The ASA runs different feature sets depending on whether it's in Routed mode, Transparent mode, or Single AS mode. Routed mode is the default and what most people use. Transparent mode makes the ASA act like a bridge. You don't configure IP addresses on the data plane interfaces in transparent mode. This is useful when you need to drop a firewall into an existing network without readdressing anything, but it adds complexity and not all features are available in transparent mode.
Logging and Monitoring
Syslog configuration is essential. You need a syslog server. The ASA generates a lot of events and you want them going somewhere useful. Configure the syslog server with logging host and set the appropriate trap severity level. Informational is too verbose for most environments. I typically set the trap level to notifications or errors depending on how much detail I need. Connection logging is also useful for auditing. You can enable logging on deny rules and on specific permit rules when you need to track particular traffic patterns. The log keyword on ACL entries is your primary tool here. Pair it with a syslog server and you have basic visibility into what's happening. The ASA has limitations. It doesn't scale well beyond a certain throughput threshold. If you're doing more than a few gigabits of inspected traffic, you'll feel the pain. The hardware architectures change across models too, and migrating between different series sometimes requires complete configuration rewrites because the syntax differences are significant.
For high-throughput environments, Cisco's own Next-Generation Firewall line is generally a better fit. The Firepower series handles deep packet inspection and application-layer filtering more efficiently. The ASA is still a capable perimeter firewall for moderate sizes, but it's showing its age. If you're starting a new deployment at scale, evaluate the NGFW options first. For smaller deployments under 500 Mbps of typical traffic, the ASA remains solid. The feature set is mature. The documentation is extensive. The main downsides are the licensing model for advanced features and the fact that Cisco has effectively moved past it as their flagship product. Support will continue but innovation has shifted elsewhere. If you're maintaining an existing ASA estate, the Cisco Asa Firewall Configuration Guide documentation from Cisco covers the specifics you need. The key takeaway is understanding how the stateful model differs from stateless approaches, getting the NAT rules right on the first pass, and building your ACLs with the evaluation order in mind. Those three areas account for the majority of configuration mistakes I see in production environments.