
Configuring Cisco ASA Firewalls When You're Already Behind
Most people come to Cisco ASA configurations when something is already broken. That is not ideal. The adaptive security appliance has been around long enough that documentation exists in abundance, but it is also scattered across dozens of version-specific PDFs, old forum threads, and Cisco's own outdated knowledge base articles. I spent about two weeks last month trying to get a 9.16 ASA to properly route traffic between two VLANs while also applying an IPS policy. The problem was not the ACLs. It was that ASDM was lying to me about what policies were actually deployed. Cisco publishes official configuration guides, but they are written for people who need reference material at their desk, not for someone who is on-call at 2 AM and needs to know why NAT is failing. A well structured Cisco Asa Guide that actually walks through the decision trees you face in production is worth more than forty chapters of feature documentation. The difference is context. The official guides tell you every command that exists. They do not tell you which ones to use first or in what order they conflict with each other. I keep a local Cisco Asa Guide that I have been building since around 2019. It started as a collection of notes from customer deployments and grew into something I actually rely on when I am troubleshooting. If you want to download a solid starting point, you can find community versions on GitHub that most people update regularly. Search for "cisco asa configuration guide github" and look for repos with recent commits and open issue threads. The ones with zero activity are usually just copy-pasted from old Cisco documents.
Core Concepts You Actually Need to Understand First
Before you touch a single access-list or NAT rule, you need to understand how the ASA evaluates traffic. It is not a generic firewall with a standard allow-by-default-or-deny-by-default model. The ASA uses a stateful inspection engine with multiple enforcement points, and the order in which those enforcement points trigger matters more than anything else in the entire configuration. Here is the actual order for inbound traffic on an interface:
- Route lookup happens first. If the ASA cannot determine where the packet should go, everything else is irrelevant.
- NAT and policy NAT are evaluated before any access control.
- Access-lists on the ingress interface are applied after address translation.
- The security level check between interfaces comes into play for inter-VLAN routing.
- Finally, the connection table is checked for established sessions.
This order changes slightly depending on whether you are using failover, transparent mode, or multi-context. Most guides gloss over this. I found out the hard way when a perfectly valid ACL was silently dropping traffic because a policy NAT rule was rewriting the source address before the ACL could match it. The traffic looked correct in the ACL hit counts but never reached the destination. NAT on the ASA has been through several rewrites across versions. The 8.3+ syntax is vastly different from the pre-8.3 static NAT commands, and the 9.x versions introduced object-based NAT that further changed the syntax. If you are migrating from an older box or reading legacy documentation, you will encounter conflicting information. The most common mistake I see is mixing dynamic and static NAT for the same source subnet on the same interface. The ASA does not merge these gracefully. It prioritizes one over the other based on configuration order, and the behavior is not always intuitive. I had a situation once where two different engineers had pushed NAT rules on a clustered pair, and the active node was translating addresses differently from the standby. The active-passive failover did not catch it because both nodes had the right configuration, but the routing path caused the active to prefer one NAT rule over the other due to a hash-based session distribution quirk.
Get the Full Details

The workaround was to consolidate all NAT statements under a single NAT policy object and explicitly set the precedence. That eliminated the ambiguity. Always verify your NAT rules with show nat and show xlate detail after any change. Do not assume the configuration you see in running-config matches what is actually being enforced.
Access-Control Lists and the Hidden Behavior
ACLs on the ASA are application-aware. That means the ASA can inspect Layer 7 protocol traffic within the permitted flows. This is powerful, but it introduces a behavior that trips up even experienced administrators. When you enable inspection for a protocol, the ASA dynamically opens a pinhole in the ACL for the return traffic. If you then remove or modify the ACL entry, the inspection engine may continue to allow the connection based on the dynamic pinhole, creating a gap between what your ACL says and what is actually happening. I encountered this when I was tightening up a DMZ ACL and removing a broad permit statement. The traffic kept flowing anyway because the FTP inspection engine had opened temporary openings for active-mode data connections. The fix was to also adjust the inspection policy with no inspect ftp on that interface, then reapply the ACL. Without touching the inspection policy, the ACL change appeared ineffective. Another thing most people miss: the implicit deny at the end of every ACL is not the only implicit rule. The ASA also implicitly denies any traffic that does not match a static or dynamic NAT rule. This means you can have a perfectly permissive ACL and still see traffic dropped because there is no matching translation. Always verify with show access-list and show xlate together when debugging drops.
ASDM vs CLI: Knowing When to Use Which
The ASDM GUI is convenient for initial setup, but it is also where a lot of configuration drift comes from. ASDM sometimes generates different CLI commands than what you see in the interface. For example, creating a NAT rule through ASDM might result in a grouped NAT policy, while the CLI equivalent would use individual nat and static commands. When you push configurations through version control or automation, this discrepancy causes issues. My preference is to use the CLI for everything after the initial network topology setup. The CLI gives you deterministic output, clearer error messages, and easier rollback capability. I have seen ASDM silently accept configurations that the running config does not reflect accurately, especially in multi-context mode. In one deployment, the ASDM showed three contexts configured correctly, but one of them was actually sharing the physical interface allocation with another context due to a licensing restriction that ASDM did not flag at the time of creation.

Troubleshooting Commands You Should Memorize
When something is not working, these commands will get you further than any guide: packet-tracer is the single most useful command on the ASA. It simulates a packet through the entire inspection pipeline and shows you exactly where and why it gets dropped. The output is verbose but structured. I use it constantly, and it has saved me from pulling hair out on numerous occasions. The trick is to run it from the correct perspective. Always specify the ingress interface and the actual source and destination IPs you are testing with, not generic placeholders. show conn detail gives you the full state of active connections. Use this when traffic seems to be passing but applications are not responding. You will see whether the connection is established, tearing down, or stuck in some intermediate state.
debug packet is powerful but dangerous. It generates significant CPU overhead and can fill up logging space quickly. Use it only when packet-tracer does not give you enough information, and always set a filter so you are not debugging every packet on the interface. I once ran a bare debug packet on a high-traffic edge ASA and took the box down because the CPU spiked to 95 percent within thirty seconds.
Version-Specific Gotchas
The ASA codebase has diverged significantly across versions. Version 9.1 introduced significant changes to the routing and NAT behavior, and version 9.16 brought even more. If you are following a guide written for 9.8 on a 9.16 box, some commands will work and others will produce errors that do not clearly indicate what changed. The release notes are your friend here. Read them before upgrading, and pay particular attention to the "Changes to Existing Behavior" sections. One specific issue I dealt with on 9.16 involved the object-group network syntax. Older guides show object groups defined inline within ACL statements. In 9.16, Cisco deprecated that inline syntax in favor of explicit object-group definitions. The old syntax still works but generates a warning in the config and may not behave consistently across failover pairs. Migrating to explicit object-groups resolved the inconsistency.
Failover Considerations
Active-standby failover on the ASA is generally reliable, but there are edge cases that basic guides do not cover. The failover link carries configuration synchronization, health checks, and session state replication. If the failover link degrades or drops, the secondary unit continues operating but stops receiving session updates. This means that after a failover event, you may see intermittent connectivity issues because some sessions were not fully synchronized. I recommend testing failover regularly with failover lock and failover active commands in a maintenance window. Do not rely on the automated failover mechanism being tested for you. In one engagement, the failover link was flapping due to a bad SFP in the switch port, and the primary ASA was constantly stepping down and back up. The monitoring alerts fired for interface failures, but nobody connected the dots to the failover instability until a customer reported dropped VPN sessions.
VPN Configuration: Where Things Break Most Often
Site-to-site IPSec on the ASA is straightforward when it works. It breaks most often due to mismatched phase 1 and phase 2 parameters, NAT traversal conflicts, or incorrect crypto ACLs. The crypto ACL defines which traffic is encrypted, and it must match on both ends. A common error is using the wrong interface IP as the source in the crypto ACL on one side but not the other. For remote access VPN, the most frequent issue is DNS allocation. The ASA hands out internal DNS servers to clients, and if those DNS servers are not reachable from the VPN subnet, clients appear connected but cannot resolve internal names. Verify DNS reachability from the ASA itself before telling a customer the VPN is misconfigured. SSL VPN is another area where guides often skip over the practical details. The webvpn configuration involves certificate management, AAA integration, and tunnel-group settings. If you are using external RADIUS or TACACS+, make sure the ASA can actually reach the auth server before spending time on SSL VPN client settings. I have seen support teams troubleshoot SSL VPN for hours only to discover the RADIUS server was unreachable due to a routing change that happened weeks earlier.
Logging and Monitoring
The ASA generates a lot of log messages, and most of them are noise. Configure logging to send to a centralized syslog server and set appropriate severity levels. The default logging level is informational, which includes a lot of useful connection tracking data but also a lot of routine messages. Level 6 (informational) is usually sufficient for production. Level 3 (errors) alone is too sparse for debugging. I typically set it to level 5 (notifications) during active troubleshooting and revert it afterward. Enable the connection log with logging message 106014 to track connection establishment and teardown events. This gives you visibility into session lifetime without enabling full packet debugging. Pair this with periodic show conn count snapshots to detect abnormal connection accumulation, which is often a sign of an attack or a misconfigured application hammering the firewall.

What This Guide Does Not Cover
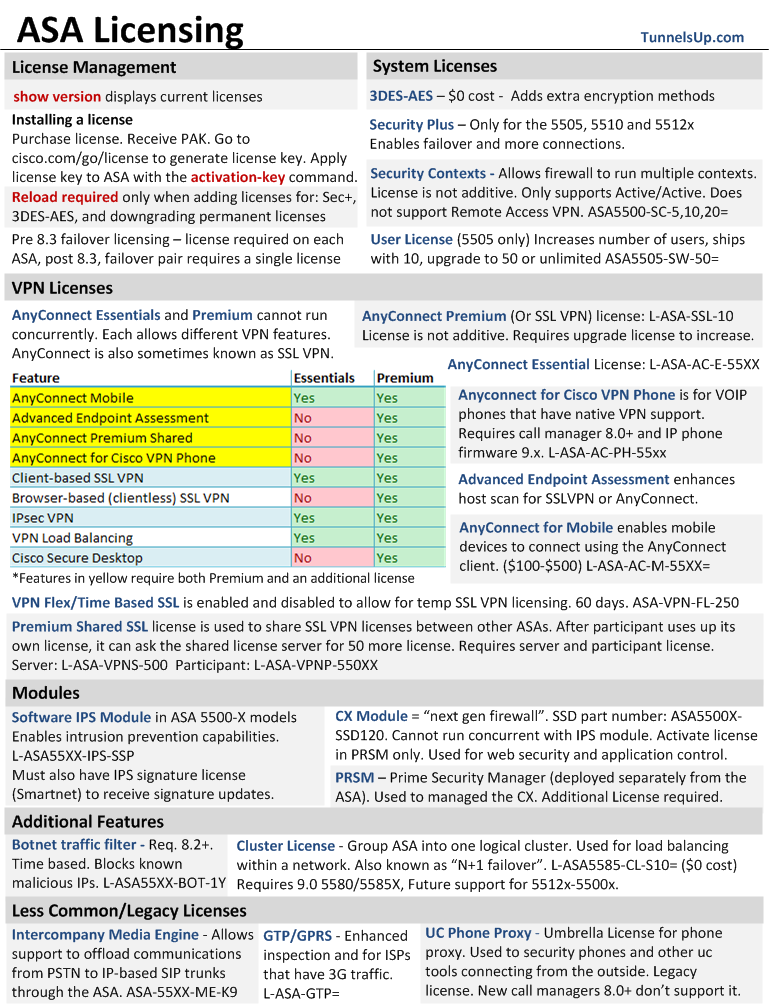
There are topics I am not covering here because they require dedicated attention: advanced threat protection with Cisco Firepower integration, content filtering, URL filtering, malware defense, and the newer Threat Grid sandbox integration. Those are separate subsystems with their own licensing and configuration models. The ASA base firmware handles routing, NAT, ACLs, VPN, and basic application inspection. If you need next-generation firewall features, you are looking at a different product line or an add-on module that changes the operational model entirely. The ASA is also reaching end-of-sale status in many regions. Cisco has been pushing Secure Firewall platforms as replacements. If you are starting a new deployment today, the ASA may not be the right choice depending on your requirements. But if you are maintaining existing ASA infrastructure, which most organizations still are, understanding how it actually behaves in production is more valuable than reading the feature list.
Final Notes on Practice
The best way to learn ASA configuration is to build a lab. GNS3 or EVE-NG can run ASA images, and the behavior in the emulator is close enough to real hardware for most configuration practice. I spent a weekend spinning up a pair of ASAs in EVE-NG with a couple of virtual routers and switches, then broke things intentionally. Failed NAT rules, misconfigured ACLs, broken failover scenarios. Each failure taught me more than any guide chapter. If you are working in production, make a configuration backup before every change. The ASA does not always roll back cleanly from a bad config, and a simple write erase followed by a reload from a known good image is faster than trying to surgically remove a bad line from running-config. Keep your backups versioned. I have a simple script that tags each backup with the date and the change ticket number, and it has saved me more than once when I needed to figure out what was different between two config versions after an incident.

