Getting IPSec Site-to-Site VPN Working on a Cisco ASA
Most people mess up the crypto ACL the first time. I've lost count of how many tickets I've seen where the tunnel won't come up and it's just a mismatched access-list or a NAT exemption that got removed during some "routine" change window. This guide will walk you through the full configuration for an IPSec site-to-site VPN on a Cisco ASA, including the parts most documentation skips over. Before touching the CLI, make sure you know your topology cold. Two sites, each behind their own ASA, each with a different public IP. Inside subnets that won't overlap. If the inside subnets overlap, you're doing double NAT before the tunnel even starts, and it makes debugging a nightmare. I had a client once trying to build a hybrid cloud link where both sides used 10.0.0.0/8 internally. Took me three hours to figure out that none of the crypto diagnostics were pointing at the real issue. The foundation of any working VPN is getting the ISAKMP policy right. This is the IKE Phase 1 negotiation. The ASA needs matching transform sets on both ends, or the tunnel just won't establish. Let me lay out a standard configuration.
Phase 1 - ISAKMP / IKE Setup
You start by defining what encryption and hashing the tunnel will use for the key exchange. This is the policy that both sides must agree on. On ASA 1: isakmp enable outside
isakmp policy 10
authentication pre-share
cipher aes-256
hash sha256
group 14
lifetime 86400
On ASA 2, mirror these settings exactly. The pre-shared key goes into a key string under the same policy number on both ends. If the policy numbers don't match, or the encryption doesn't match, the Phase 1 negotiation fails silently. You won't see an error on the surface. You'll just see no tunnel. I once spent two hours troubleshooting a tunnel that wouldn't come up between two ASAs. Turned out one side had been upgraded and the default ISAKMP policy had shifted. The other side was still running the old default. Matching the explicit policy numbers and parameters fixed it in about thirty seconds.
Get the Full Details
Phase 2 - IPsec Transform Set and Proxy
After Phase 1 establishes the secure channel, Phase 2 negotiates the actual data tunnel. This is where the IPsec transform set comes in. crypto ipsec security-association lifetime seconds 3600
crypto ipsec security-association lifetime kilobytes 4608000
crypto ipsec profile TUNNEL
set transform-set MY_TRANSFORM
set isakmp-profile ISAKMP_PROFILE The transform set itself defines the ESP encryption. Use aes-256 with sha256 for modern setups. The lifetime values matter too. Default IKE lifetimes of 86400 seconds are fine for most sites, but if you're pushing high throughput, kilobyte-based lifetime triggers renegotiation more frequently, which can add CPU overhead on lower-end hardware.
Here's something most guides don't emphasize enough: the crypto ACL. This isn't just any ACL. It's the proxy ID that tells the ASA which traffic should be encrypted. It needs to reference the local network on one side and the remote network on the other. The syntax trips people up constantly. access-list VPN_CRYPTO extended permit ip LOCAL_SUBNET REMOTE_SUBNET If you reverse these on the two ends, the tunnel won't come up. Each side sees the other's traffic as "interesting" based on its own crypto ACL. The ACLs must be complementary. Local subnet A on one end matches remote subnet B on the other, and vice versa. This is not optional. It's the #1 cause of "my tunnel won't build" complaints I see.
NAT Exemption
This is the step everyone forgets and then spends hours regretting. By default, the ASA will NAT traffic hitting the outside interface. Encrypted VPN traffic needs to bypass NAT entirely. You configure this with a NAT exception. object network LOCAL_NET
subnet LOCAL_SUBNET
nat (inside,outside) static INTERFACE Wait. That's wrong. You want to prevent NAT on VPN traffic. The correct configuration uses a nonat rule or a manual NAT exemption.
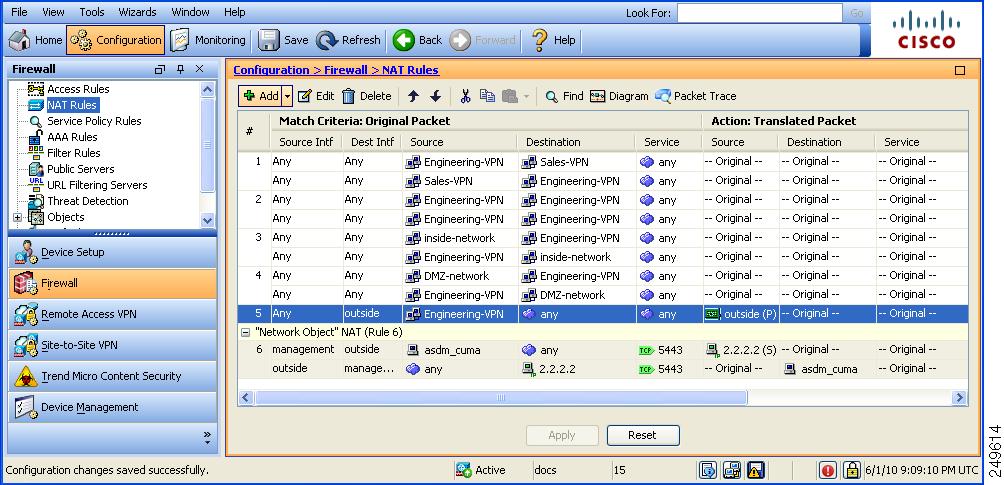
access-list NONAT extended permit ip LOCAL_SUBNET REMOTE_SUBNET
nat (inside,outside) source static LOCAL_NET LOCAL_NET destination static REMOTE_NET REMOTE_NET no-proxy-nat Or on older ASAs using classic NAT syntax: access-list NONAT permit ip LOCAL_SUBNET REMOTE_SUBNET
nat (inside) 0 access-list NONAT
Without this, the ASA translates the source IP before it hits the crypto engine. The remote end receives packets with a public source IP instead of the real private subnet, and the IPsec decryption fails because the payload doesn't match the expected proxy ID. I once walked into a production outage where a network engineer had migrated NAT rules and accidentally removed the VPN exemption. Every VPN flow started getting double-translated. Traffic from the remote site worked for ICMP but nothing else. took me about ten minutes to spot it in the NAT table, but the on-call person had been spinning for two hours beforehand.
Applying the Crypto Map
Once the transform set, ISAKMP policy, and crypto ACL are all in place, you tie them together with a crypto map. crypto map OUTSIDE_MAP interface outside
crypto map OUTSIDE_MAP 10 ipsec-isakmp
set peer REMOTE_ASA_PUBLIC_IP
set pfs group14
match address VPN_CRYPTO Perfect Forward Secrecy is important. Without PFS, an attacker who compromises the Phase 1 key can decrypt all Phase 2 traffic. Enable it with the PFS setting. Group 14 is the standard for most deployments. If both ends support it, group 19 or 21 give you stronger DH keys at a modest CPU cost.
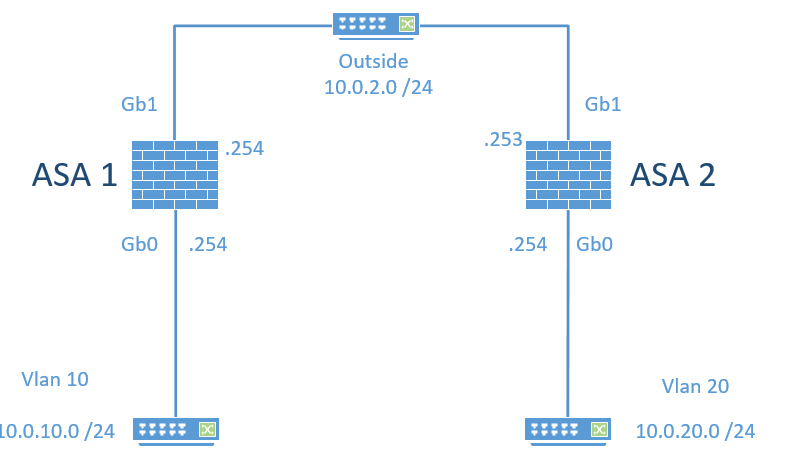
The crypto map gets applied to the outside interface. Traffic matching the crypto ACL gets encrypted and sent to the peer. Everything else takes the normal routing path.
Diagnostics and Troubleshooting
When the tunnel doesn't come up, don't guess. Use these commands in order: show ISAKMP SA - shows Phase 1 status
show crypto ipsec sa - shows Phase 2 status
show crypto map - shows the applied map
debug crypto isakmp - real-time Phase 1 packets
debug crypto ipsec - real-time Phase 2 packets
clear crypto sa - resets the Security Associations when stuck The debug commands are powerful but noisy. Run them on a low-traffic window. They generate a lot of output and can impact performance on busy interfaces. Clear the Security Associations with clear crypto sa if the tunnel is stuck in an odd state after a configuration change. It forces a fresh negotiation and resolves about 60% of "stuck tunnel" cases I've seen.
One edge case worth noting: asymmetric routing. If traffic leaves through one firewall and comes back through another, the IPsec tunnel won't work correctly. Both the initiator and responder need to see the same flow in both directions. I dealt with a hospital network where the VPN kept dropping because the return path routed through a different ASA that didn't have the same crypto map. Took a week to identify because the issue was intermittent and depended on which path the ISP chose at the time.
Common Pitfalls
Overlapping subnets between sites. This breaks the crypto ACL entirely. There's no workaround without double NAT, and even then it's fragile. Design your IP scheme to avoid this from the start. MTU issues. IPsec adds overhead. If your inside networks are using jumbo frames or large TCP MSS values, you'll get fragmentation issues. Set the MTU on the tunnel interface appropriately, or configure TCP MSS adjustment on the ASA to cap it at around 1350 bytes for IPsec traffic. ASAv vs. physical ASA differences. The ASAv (virtual appliance) has lower throughput compared to a 5500-X series. If you're running high-throughput site-to-site VPN on an ASAv in a cloud environment, you'll hit the vCPU limit before you hit the tunnel limit. Monitor CPU during peak transfer times.
Alternative Approaches
If you're building a large mesh of site-to-site connections, individual crypto maps become unmanageable quickly. At that scale, consider FlexVPN or DMVPN, which are supported on newer ASA firmware versions. They reduce configuration complexity dramatically when you have more than three or four sites. For a simple two-site connection though, the manual crypto map approach is straightforward and gives you full control. Another option worth mentioning: SSL VPN. If you need remote user access rather than site-to-site, the ASA's AnyConnect SSL VPN is the built-in solution. It's a completely different configuration path and uses port 443 instead of UDP 500. Don't confuse the two. They serve different purposes. The configuration itself takes about fifteen minutes on a clean ASA if you have the parameters ready. Most of the time people spend on VPN projects comes from troubleshooting NAT issues, ACL mismatches, or connectivity problems that have nothing to do with the crypto config at all. Get the underlying network right first, then the VPN is just a few commands.