Understanding the Cisco SD-WAN Design Guide as a Working Document
The Cisco SD-WAN Design Guide is an official resource that outlines architecture patterns, component interactions, and deployment recommendations for building SD-WAN environments with Cisco hardware and software. It covers vManage, vSmart, and WAN edge router roles, along with topology options like full mesh, hub-and-spoke, and hybrid deployments. The guide is maintained by Cisco and updated alongside new software releases. You can find it at https://www.cisco.com/c/en/us/td/docs/solutions/Enterprise/WAN_and_MAN/SD-WAN/sdwan_design.html. It is free to access without any login wall. The document is organized into chapters rather than presented as a single narrative, which means you will pick up the section relevant to your current design challenge and skip the rest. That is how most people actually use it. I have not read it cover to cover more than once.
Working Through the Cisco Sd Wan Design Guide in Practice
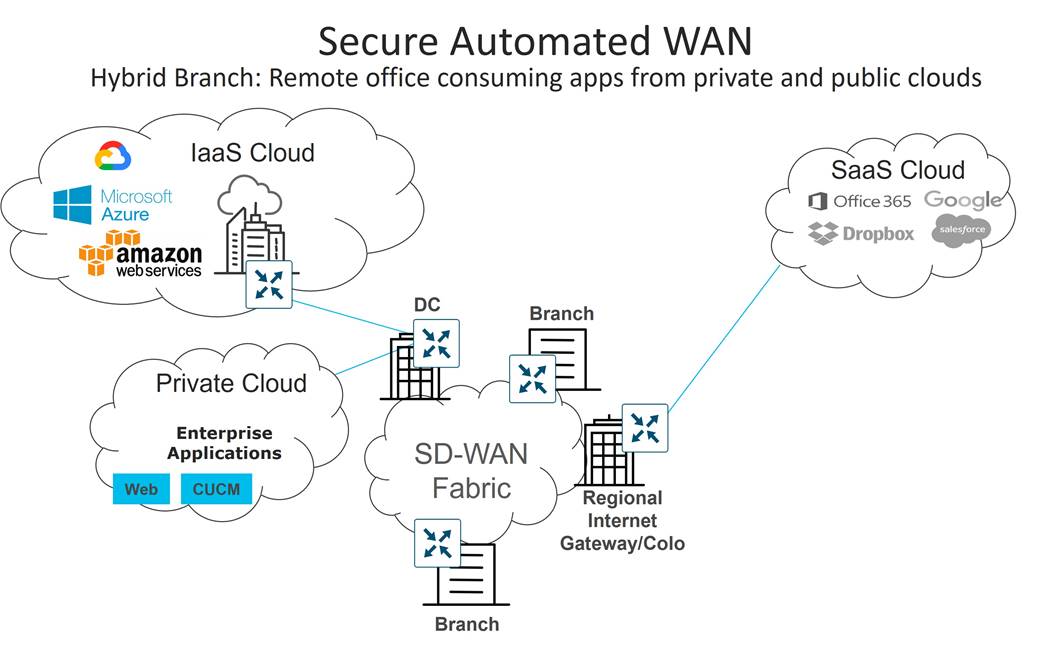
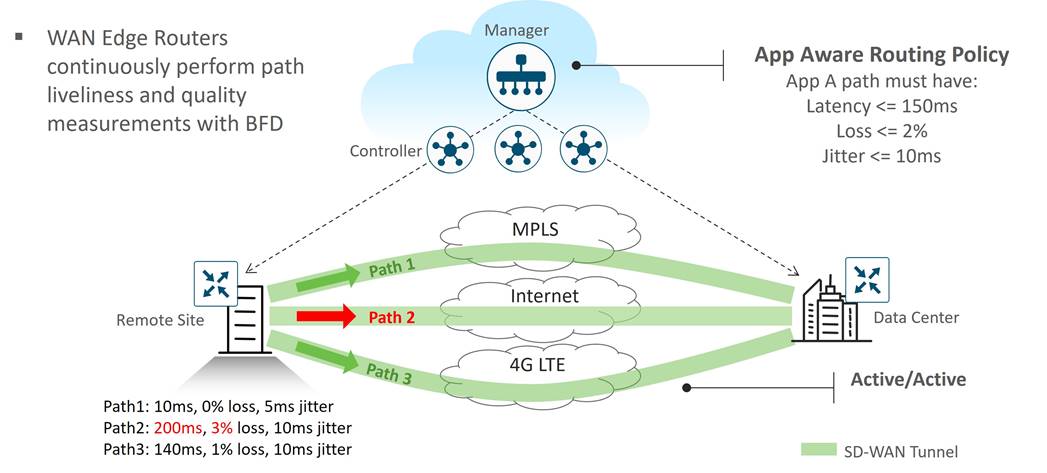
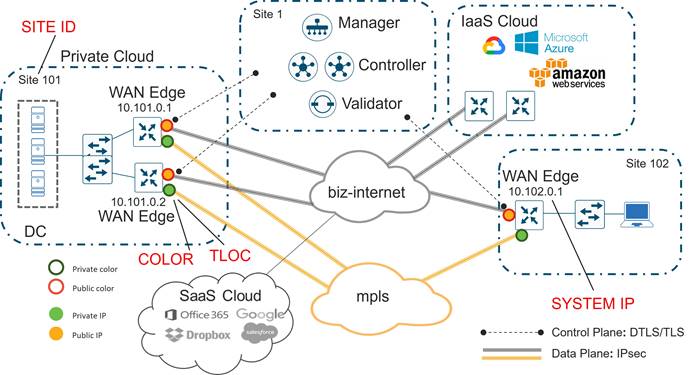
The guide describes control plane options including centralized and local routing, which sounds straightforward until you are actually configuring thousands of sites and realizing that vSmart controller placement directly affects convergence time after a link flap. The recommended split of controllers across geographies is not optional if you want predictable failover behavior. Cisco writes this in the guide but the numbers change with scale, and the exact thresholds are buried in configuration notes rather than in the main architectural diagrams. I ran into a specific issue last year when designing a hybrid connectivity scenario for a retail chain with roughly four hundred branches. The design called for combining MPLS and broadband at each site with IP SLA-based path selection. The guide recommends a particular way to structure the overlays using different colors for dedicated transport versus internet breakout. Everything looked correct on paper. In practice, two sites that had been migrated from a traditional WAN to SD-WAN started dropping traffic unexpectedly during peak hours. The issue was not with the tunnel itself. It was related to how TCP performance scaling interacted with the color-based forwarding table and the underlay asymmetry between MPLS and broadband interfaces. Cisco's documented behavior assumes symmetric path selection within a single underlay color, but when you mix underlays with significantly different bandwidth characteristics and the application-aware routing policy does not account for it, the overlay can choose a suboptimal next-hop path repeatedly. The workaround involved adjusting the OMP route filtering to prefer the dedicated transport color for latency-sensitive application flows, then explicitly overriding the default path selection behavior using policy-based routing at the WAN edge. It added about three weeks of testing before rollout because every change required validation across all four hundred branches through staged configuration deployment. The guide does mention underlay asymmetry as a consideration but does not walk through the exact combination of adjustments needed when MPLS and broadband coexist with heavy asymmetric utilization. That kind of detail comes from having seen the same failure mode multiple times across different customer environments.
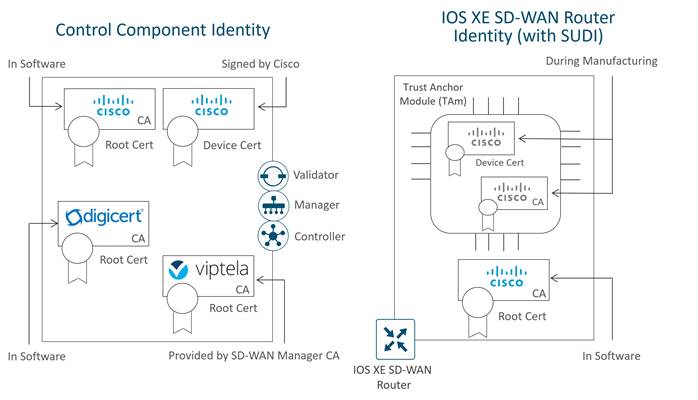
Another point the guide treats briefly but deserves more attention is the relationship between DTLS and TLS for control channel encryption. DTLS is still supported for legacy compatibility but TLS 1.2 and above is the default on newer vManage and vSmart versions. Some network teams deploy both simultaneously as a migration step, which works but introduces additional certificate management overhead. Certificate pinning misconfiguration is a common cause of vSmart controller unreachable errors in production, and the troubleshooting steps in the guide assume you are already familiar with OpenSSL debugging on the device CLI. If you are not, you may spend more time than expected.
Get the Full Details
Key Design Considerations Before You Start Deploying
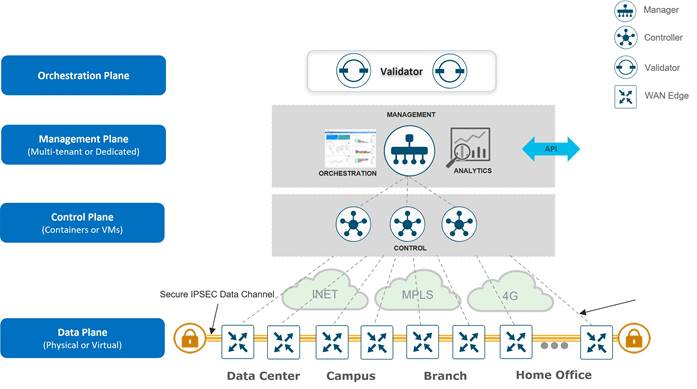
The guide breaks down several foundational elements. WAN edge devices handle the data plane. vManage acts as the management interface. vSmart controls the routing decisions. These components must communicate securely using certificates issued by a local or CloudPKI certificate authority depending on your deployment model. The choice between public cloud and private cloud vManage matters more than most teams realize because it affects high availability configurations and disaster recovery procedures. Running vManage in a high availability pair on-premises gives you control over data residency and reduces dependency on Cisco's public cloud infrastructure, but it also shifts the operational burden onto your internal team for patching, backup scheduling, and monitoring. Site onboarding is another area where the design guide provides clear steps but where real-world deployments often encounter configuration drift. Manual copy-paste of configuration snippets from the guide without validation against your existing network infrastructure is a frequent mistake. Cisco's CLI templates assume a clean environment. If you have overlapping VLAN ranges, pre-existing static routes, or custom DNS settings already in place, those defaults will conflict. The guide does note this but does not provide a comprehensive checklist for existing network remediation before SD-WAN deployment begins. Security segmentation is handled through flex connectors and service chaining in modern versions of vManage. The guide describes the concept clearly, and the visual topology editor helps map out how traffic should flow through inline services like firewalls and URL filtering. However, the performance impact of service chaining at scale is not always obvious from the documentation. A single vEdge router handling encrypted traffic and directing it through an inline firewall for fifty branches will consume significant CPU resources, especially if you are inspecting TLS-encrypted application traffic. This is not a problem unique to Cisco SD-WAN, but it is worth noting when sizing your architecture.
Common Pitfalls and Limitations
The design guide assumes a level of familiarity with traditional routing concepts and BGP behavior that not all engineers possess, especially teams transitioning from simple layer 2 WAN topologies. Overlay routing using OMP is conceptually similar to BGP but has enough differences to cause confusion during initial deployments. The guide covers these differences but the explanations can be dense for someone who has never worked with BGP route reflection or AS-path filtering. There is also a notable limitation when dealing with non-Cisco equipment at the branch level. While SD-WAN supports third-party edge devices through standard IPsec tunnels, the policy enforcement and application-aware routing features do not extend to those devices in the same way. The design guide acknowledges this but the practical implication is that non-Cisco endpoints will lack visibility into application-level metrics and path selection decisions. If your environment includes significant non-Cisco infrastructure, you should plan for a segmented monitoring strategy from the beginning rather than assuming a single dashboard will cover everything. Certificate lifecycle management deserves more emphasis than the guide gives it. Certificates expire. If you are managing hundreds of sites and have not automated certificate rotation, you will eventually experience outages caused by expired vSmart or vManage certificates. Cisco has improved automation in recent versions, but the design guide references capabilities that vary between software releases. Always verify which version of vManage you are deploying before following any certificate configuration example in the document.
What the Guide Does Well
The section on site discovery and zero-touch provisioning is well structured and reflects real deployment workflows. The step-by-step instructions for adding a new WAN edge device through vManage are accurate and reflect current software behavior. The topology diagrams for full mesh and hub-and-spoke deployments are clear and useful as a reference during design reviews. The guide also includes a dedicated chapter on IPv6 support, which is relevant given increasing regulatory requirements in certain regions. When used correctly, the design guide can reduce the initial design phase from approximately two weeks of research to around three to four days if you already understand the underlying networking concepts. Teams that skip directly to configuration without reading the relevant chapters often spend additional time troubleshooting issues that were already addressed in the documentation. I have seen this happen repeatedly across different customer engagements, and the pattern is consistent enough to warrant noting it here. The guide is most valuable when treated as a reference manual rather than a sequential tutorial. You will return to specific sections multiple times during a single project. Reading it straight through provides context but is not the most efficient use of time for experienced engineers. For newcomers, pairing the guide with hands-on lab work using Cisco's Virtual Topology System emulator or a personal GNS3 setup with EOS images is significantly more effective than relying on the document alone.