What actually happens when you sit down to study for CISSP
The first thing most people do when they're told they need to study for CISSP is search for "Cissp Exam Outline 2023" and land on some blog that links to an outdated PDF from 2018. Don't do that. The current version of the exam follows the Common Body of Knowledge that was updated in 2024, but the way people search for it hasn't caught up. You'll find references to the older five-domain structure mixed in with forums and prep sites, which is confusing as hell. I spent about three weeks prepping for my CISSP and I didn't get far because I was pulling material from three different versions of the outline simultaneously. Here's what I ended up doing that actually worked, and the specific traps I walked into.
Getting the Cissp Exam Outline 2023 correctly
The official ISC2 site lists the exam domains. Go straight there and ignore everything else until you've read the domain descriptions twice. The current breakdown has eight domains with approximate weightings that look something like this: Security and Risk Management — roughly 15 percent. This is where you answer questions about policy, governance, compliance, and that annoying section on cryptography that everyone memorizes and then forgets halfway through the exam. Professional ethics sits in here too, and I can tell you from experience that ISC2 expects you to choose the answer that aligns with their Code of Ethics even when it conflicts with what common sense tells you. Pick the code every single time. Asset Security — about 10 percent. Data handling, classification, retention, and protection. Straightforward but you need to know the difference between what you'd do personally versus what the org should have in policy.
Security Architecture and Engineering — 12 percent. This one tests whether you actually understand security controls or just know buzzwords. Physical security, secure design principles, cloud models, and cryptography again. The cryptography questions will kill you if you haven't practiced them. Know your symmetric vs asymmetric, know when to use which, and don't second-guess yourself on the math questions if they show up. Identity and Access Management — 13 percent. IAM is huge. Single sign-on, federated identity, OAuth, SAML, MFA, provisioning. This is the domain where having hands-on experience matters most. If you've never configured anything beyond basic Active Directory, you'll be guessing a lot here. Security Assessment and Testing — 7 percent. Vulnerability scanning, penetration testing, audit types, assessment methodologies. Small domain, but the questions tend to be very specific about process and methodology.
Get the Full Details

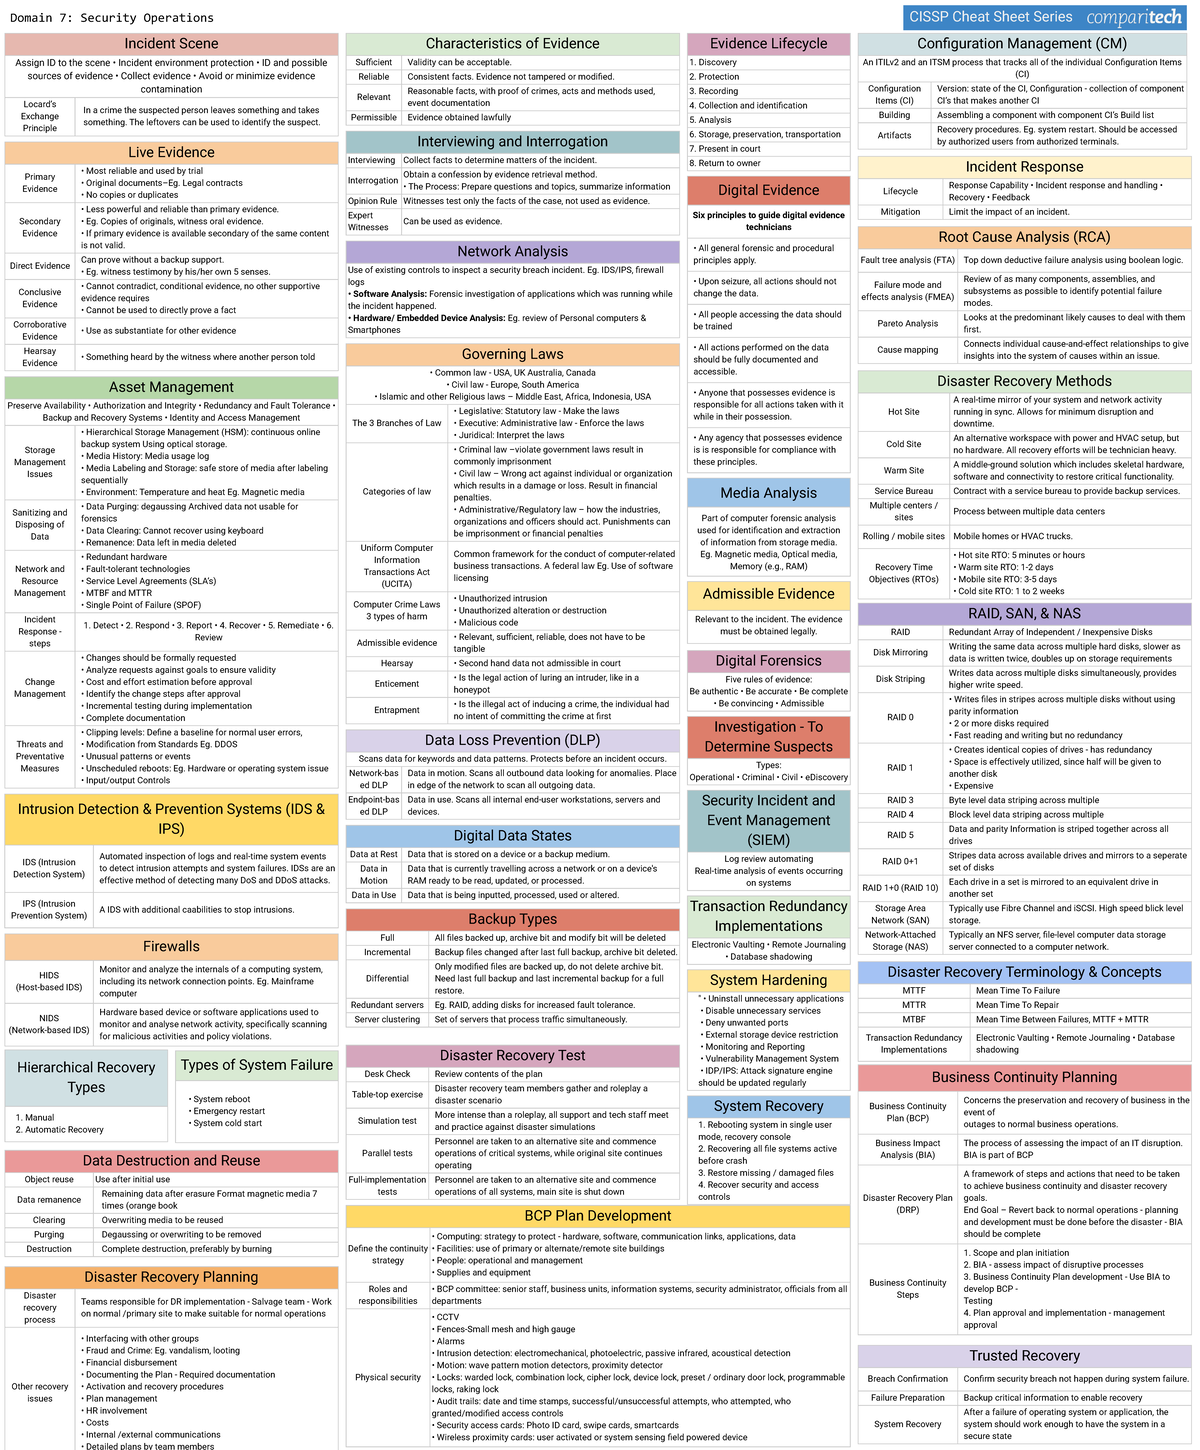
Security Operations — 15 percent. Incident response, disaster recovery, business continuity, forensic procedures, logging and monitoring. This is where my exam hit hardest. I got questions about what you do first during an incident that aren't obvious. Containment isn't always the right first step depending on the scenario. I learned that the hard way when I picked "isolate the network" on a question about a compromised server that was actively exfiltrating data, and the right answer was something more nuanced about preserving evidence and stopping the exfiltration at the application layer first. You have to think like a security manager, not a sysadmin. Software Development Security — 14 percent. SDLC, secure coding, app security testing, open source risks. If you come from a development background this will be easy. If you come from operations, it's going to feel foreign. Spend extra time here. That's the general shape of it. The percentages shift slightly between editions so treat them as approximations.
How to actually use the outline for studying
Download the official domain breakdown from the ISC2 website. It's free. Then cross-reference each domain with a study resource — the Sybex official study guide is fine for foundations, and the All-in-One book covers more breadth but you'll need something for depth. I used both. Budget about 150 hours total if you're starting from a moderate baseline. Not 50. Not 80. 150. Start with the domain you know least. That sounds obvious but most people start with their strongest area because it feels good. It doesn't help. You need to grind through your weaknesses while you still have motivation. Practice questions matter more than rereading the book. I did roughly 1,500 practice questions across the prep period, spread across the three weeks. Get the Pearson VUE practice test too — it's the closest thing to the real exam's question style, even though the content is slightly outdated. It teaches you the pacing and the adaptive feel.
The mindset problem nobody talks about
The CISSP isn't testing whether you can recite definitions. It's testing whether you think like a risk advisor. Every question is framed as a scenario where you're consulting for an organization, and you need to pick the best answer, not the technically correct one. That distinction is everything. For example, you might see a question about a vulnerability discovered on a production server. The technically correct answer is to patch it immediately. The CISSP answer depends on context — was it a zero-day in a public-facing service? Then patching is right. Was it an internal-only system with compensating controls already in place? Then the answer might involve risk acceptance or transfer first, not immediate patching. You have to evaluate the business impact before jumping to the remediation action. I learned this through painful repetition. I was scoring 65 to 70 percent on practice exams consistently because I kept choosing the engineer answer instead of the manager answer. Once I started reading every question twice and asking myself "what is this role actually responsible for right now," my scores climbed to the 75 to 80 percent range. That's the sweet spot you want before booking the exam.
A specific problem I ran into
During my prep, I hit a wall with the cryptography domain. Not the concepts themselves — I understood AES, RSA, key management, digital signatures, all of it. But the practice questions kept tripping me up because they blended crypto with compliance requirements in ways I hadn't seen before. One question asked about encryption standards for a company handling European customer data under GDPR, and the answer involved not just selecting the right algorithm but also considering key length, storage method, and whether hardware security modules were required by the regulation. The workaround was to stop studying cryptography in isolation. I started treating it as a cross-cutting concern that appears in multiple domains. Whenever I saw a crypto question, I forced myself to map it to the relevant compliance framework, then to the architectural decision, then to the operational procedure. It took longer but it stuck.
What the outline leaves out
The CBK domains don't cover a lot of the newer material that shows up on the exam. Cloud security maturity models, zero trust architecture implementations, supply chain risk management, and the latest threat intelligence frameworks all appear in questions but aren't prominently featured in the domain descriptions. You need supplemental reading for this. I used the Cloud Security Alliance guidance documents and the NIST SP 800 series papers for the gaps. Also, the outline doesn't reflect the adaptive nature of the exam. CAT means the difficulty adjusts in real time, which affects how you should approach the test strategically. Don't waste time on questions you're struggling with early on. Flag them, move forward, and come back if you have time. Your score on the first half of the exam has more weight in determining the difficulty of the second half.
Booking and logistics
Once you're consistently scoring above 75 percent on practice exams, book the test. Don't wait for 90 percent — that threshold is unreliable because practice exams don't perfectly model the real thing. Schedule it for six to eight weeks out so you have a deadline. The cost runs around $749, and you get three hours. You can cancel and reschedule up to 30 days before for free, but after that it gets expensive. The official ISC2 page for the exam is the only place you need to go for the current outline and registration. Everything else is supplementary. Don't let the number of prep books and courses paralyze you. Pick one primary resource, supplement with practice questions, and commit to the timeline.