What the CISSP Exam Actually Looks Like When You Sit Down
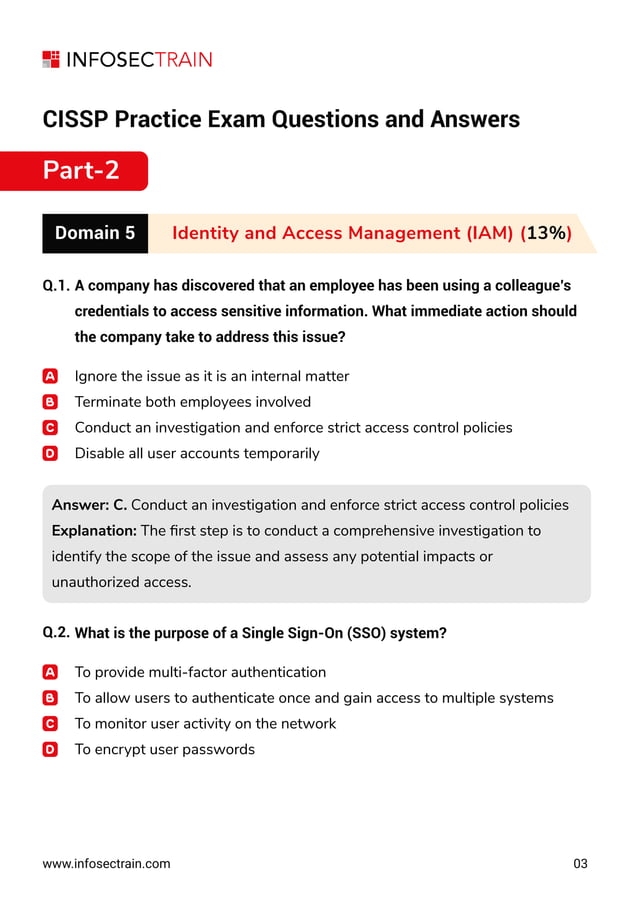
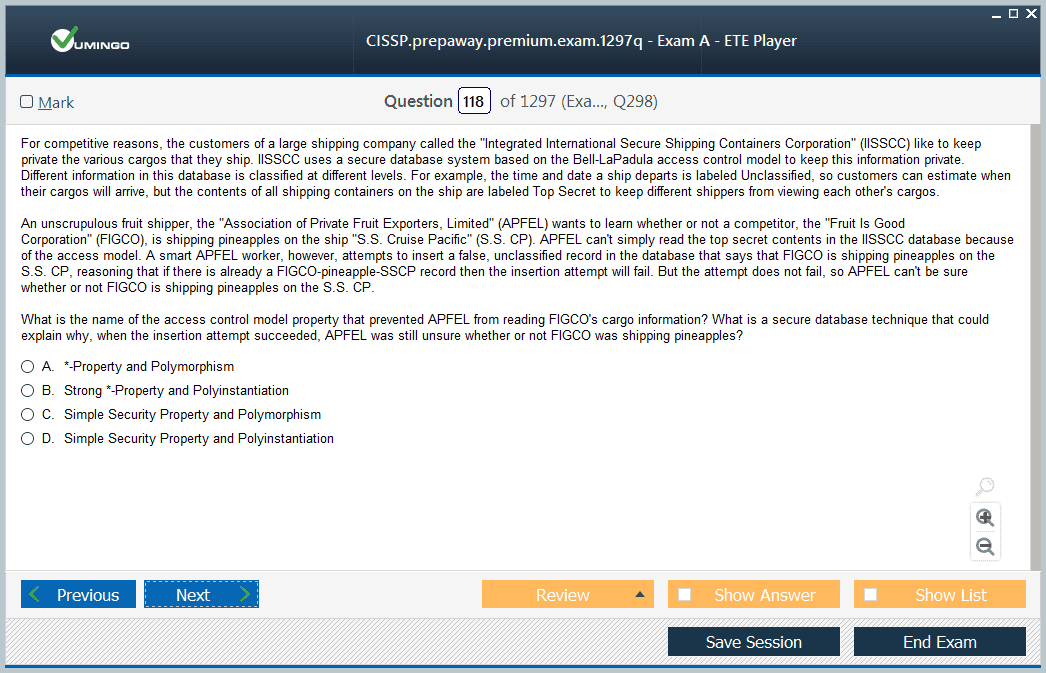
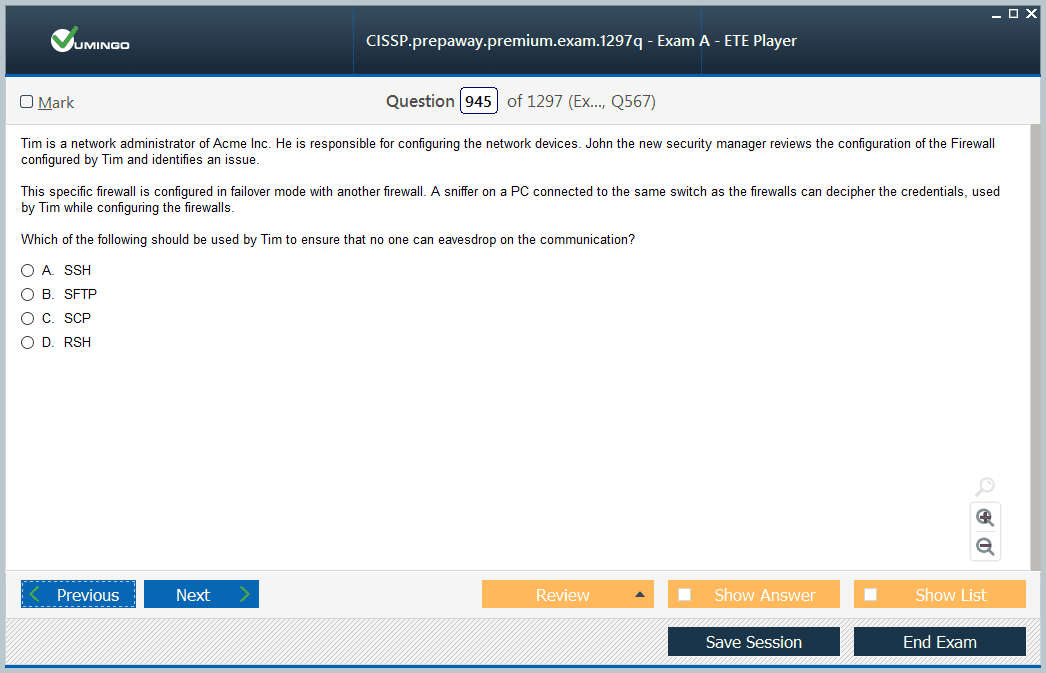
I spent about three months preparing for my CISSP, and the biggest mistake most people make is treating it like a memorization test. It isn't. The questions are designed to force you into a management-level mindset even if you came from an operations or engineering background. I learned that the hard way when I took my first practice exam and scored 58 percent. I kept picking the technically correct answer instead of the manager-level answer, and it cost me weeks of retakes. The question format changed significantly around 2024.ISC2 shifted toward scenario-based questions that don't have one obviously right answer. You will read a paragraph about a company's situation, then choose the best next step. Sometimes two answers look defensible. You have to pick the one that aligns with how a CISO or risk manager would actually respond, not how a sysadmin would fix it.
Cissp Real Exam Questions: What You Are Actually Being Tested On
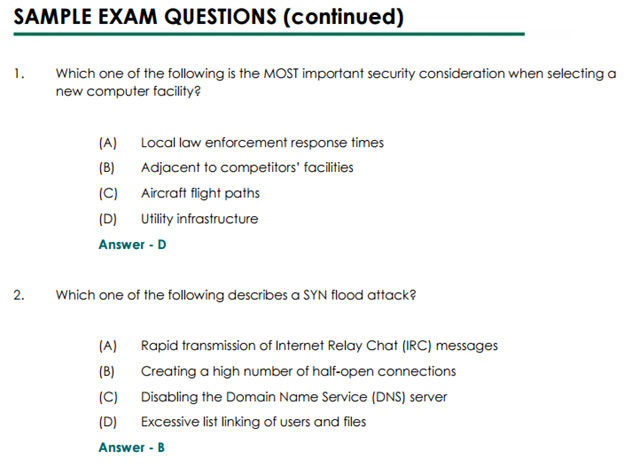
Let me be blunt about the exam structure. The current CISSP uses a CAT adaptive format with a minimum of 100 and a maximum of 150 questions. You get three hours. It covers eight domains, and the weight distribution is not even. Domain 1, Security and Risk Management, carries the most points at roughly 15 to 17 percent. Domain 8, Software Development Security is the lightest at about 10 to 12 percent. People assume they need to know every protocol detail and every cipher mode. You don't. You need to know when to use each one and what the tradeoffs are. For example, I have seen hundreds of candidates memorize the exact bit lengths of every encryption algorithm but still fail questions about key management lifecycle. The exam tests your judgment on when a control is sufficient versus when you need defense in depth. That distinction separates people who pass on the first try from people who go back after multiple failures. Here is a practical edge case I ran into during my own prep. I was working through a question set about incident response and one question described a scenario where a company's SIEM triggered an alert during off-hours. The correct answer involved following the documented incident response plan first, even though the more technically interesting answer was to immediately begin forensic acquisition of the affected systems. I kept second-guessing myself because the forensic approach felt more proactive and hands-on. It took me going back to Domain 7 study material and rereading the NIST SP 800-61 framework to understand why the exam wants you to follow procedure before jumping into technical actions. The workaround I used was simple. I started writing down the domain each question belonged to and the reasoning behind why the wrong answers were wrong. After about 40 questions like that, the pattern became obvious and my score jumped from the low 60s to the high 70s within two weeks.
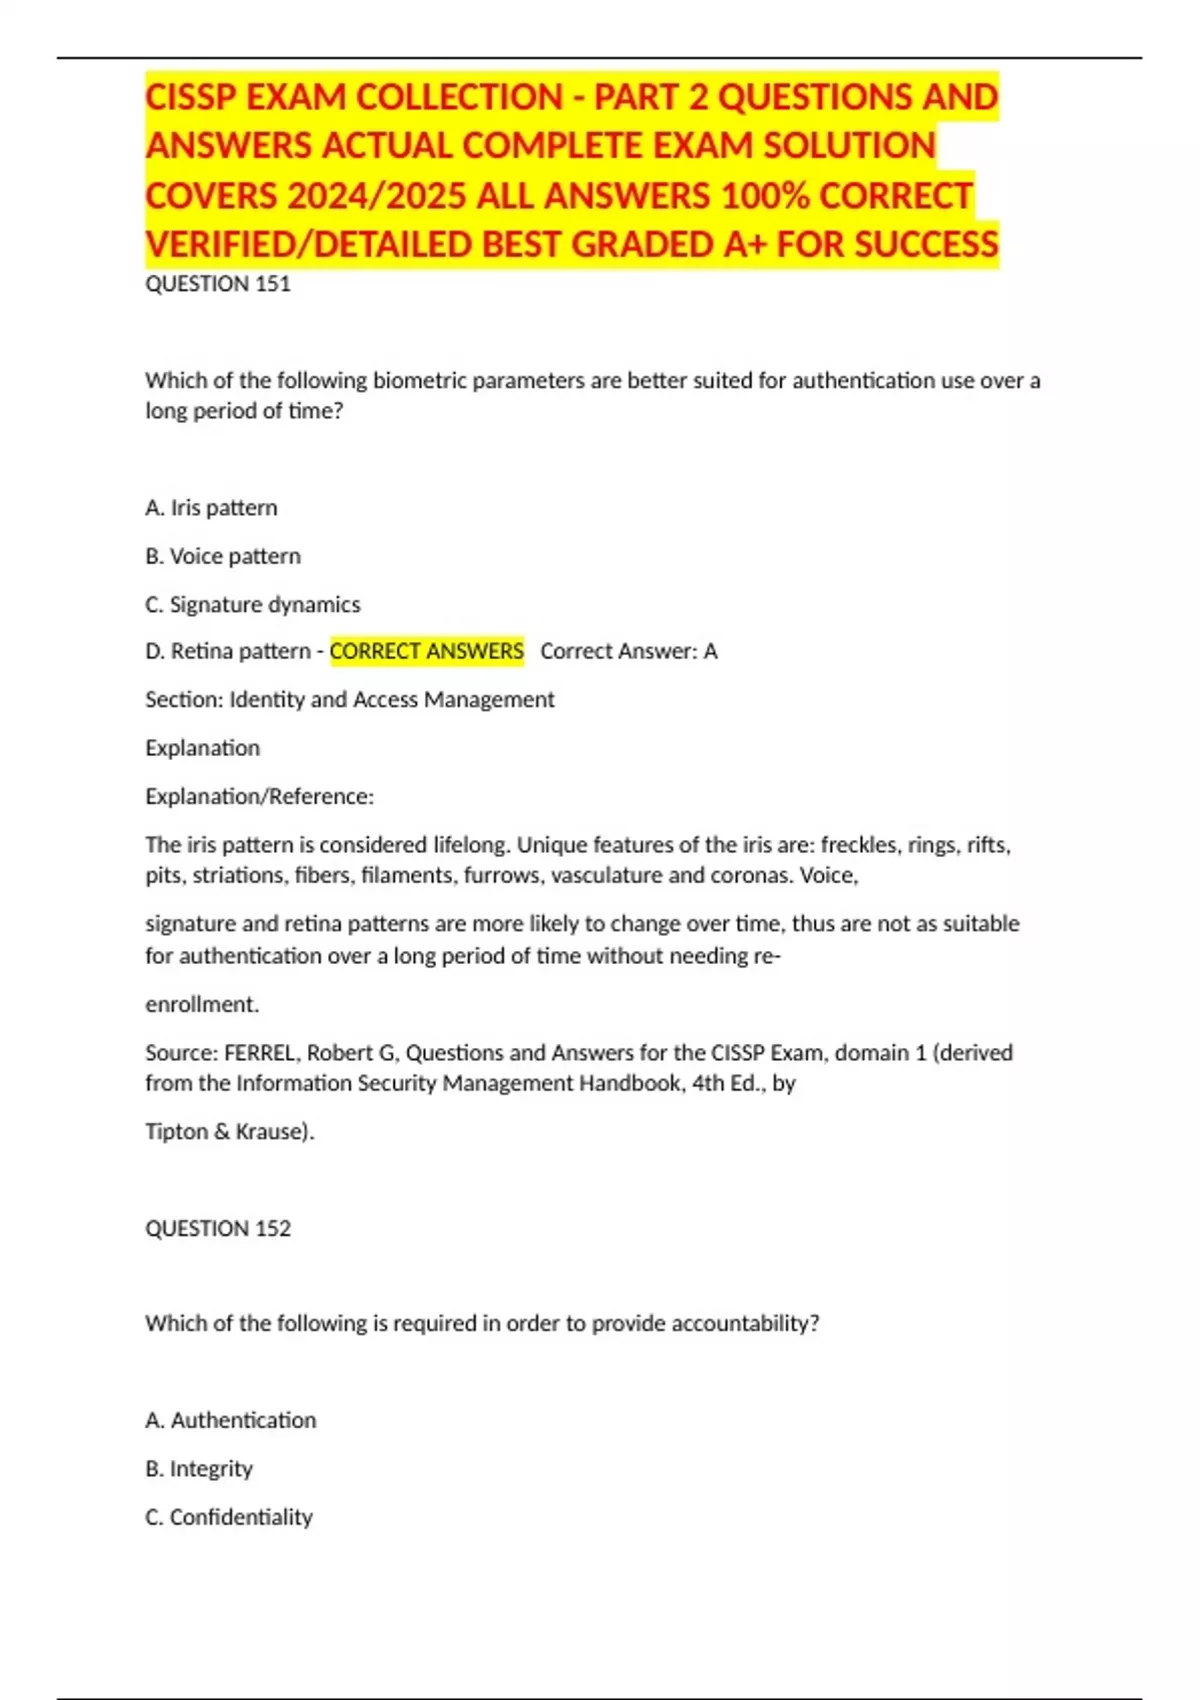
Now let me talk about something most prep providers won't tell you. The exam heavily favors ISO 27001 and NIST frameworks. If you are coming from a purely technical background and your experience is mainly with hands-on security tooling, you will struggle with the policy and governance questions. I had a colleague who was a senior penetration tester with ten years of experience and he failed twice before passing. He kept answering from an attacker perspective instead of a risk management perspective. The fix for him was spending more time on Domains 1, 2, and 3 than on the technical domains. He had to shift his thinking entirely, and that was harder than learning any new technical concept. Another counter-intuitive thing about the exam is that knowing less can sometimes help you. Questions about emerging technologies like zero trust, cloud security, and IoT often test whether you understand the principle behind the technology rather than the implementation details. For zero trust specifically, the exam expects you to know that it means never trust, always verify, and that identity is the new perimeter. It does not expect you to know every vendor's implementation of a zero trust architecture. Same goes for SASE, SD-WAN, and microsegmentation. Focus on the concepts and the risk implications, not the deployment diagrams. When you are hunting for Cissp Real Exam Questions to practice with, there are serious risks involved. Some sites sell dumps or brain dumps that contain questions stolen directly from the exam. Using those is a violation of the (ISC)2 non-disclosure agreement and can result in your certification being revoked if discovered. I am not recommending that path. The legitimate practice questions come from official (ISC)2 study guides, approved prep courses, and question banks from reputable publishers like Sybex, Weinberg, and Official (ISC)2 Practice Questions. Those cost money but they reflect the actual style and difficulty of the real exam far better than any free resource.
Get the Full Details
Here is a realistic timeline that works for most people. If you have a full-time job and 15 to 20 hours per week to study, plan for 10 to 14 weeks of prep. Start with a diagnostic test to identify your weak domains. Spend the first three weeks on Domains 1 and 2 because they form the foundation for everything else. Domains 3 through 6 are where most of the technical depth lives, and you should spend about five weeks on those combined. Domain 7 and 8 get about two weeks. Leave the final two weeks exclusively for practice exams and reviewing weak areas. Do not start taking full practice exams before week six. Your score will be artificially low and it will discourage you. Save the full simulated exams for the last two weeks when you can treat them like real test conditions. One practical tip that almost nobody mentions. The exam includes pretest questions. These are unscored questions that (ISC)2 uses to evaluate future exam items. You will not know which questions are pretest and which count toward your score. Some people report seeing questions about very niche topics like PGP encryption specifics or obscure compliance frameworks. Those might be pretest questions. Do not waste time studying for edge cases that may not even be scored. Stick to the core objectives in each domain and trust the framework. If you are considering alternatives to the CISSP, CISM is worth looking at if your role leans more toward audit and governance. CCSP is the natural choice if you specialize in cloud security. Each of those has its own question style and focus area. The CISSP remains the broadest generalist certification in information security, which is why it carries so much weight with HR filters and government contracts. But it is not the only path, and it is not always the best fit depending on your career trajectory.
I will leave it at that. The exam is tough but fair if you approach it with the right mindset. Study the domains, practice enough to recognize the question patterns, and stop overthinking the technical details. The management perspective is what they are testing, and once you internalize that, the rest becomes much simpler.