Why Your Current Risk Assessment Is Probably Wrong
Most teams treat a cloud security risk assessment like a checklist exercise. They run a tool, get a report, hand it to compliance, and move on. That's not an assessment. That's a noise generator. I learned this the hard way. About three years ago, I was leading a migration for a mid-size fintech company. We ran the standard tooling — CSPM scanners, config audits, the whole routine. The report came back green across the board. Two months later, during an actual penetration test, an attacker found a cross-account IAM role with no session restrictions. It existed in two of our ten AWS accounts. The scanner had flagged it as "informational" and buried it in appendix C. We would have been responsible for that breach.What a Cloud Security Risk Assessment Actually Is
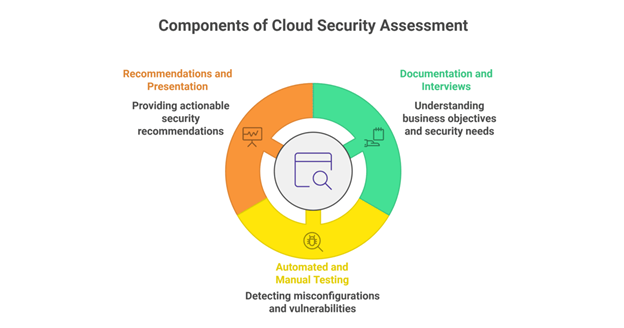
A real assessment isn't about scanning configurations. It's about understanding how an attacker would actually move through your environment, what assets they'd target, and where your controls fail. Configuration drift is a symptom. The root question is always the same: if someone bypassed your perimeter, what can they reach? The output should be a ranked list of risks tied to business impact, not a spreadsheet of "high," "medium," and "low" findings from a tool that has no idea what your company does.How to Actually Do This
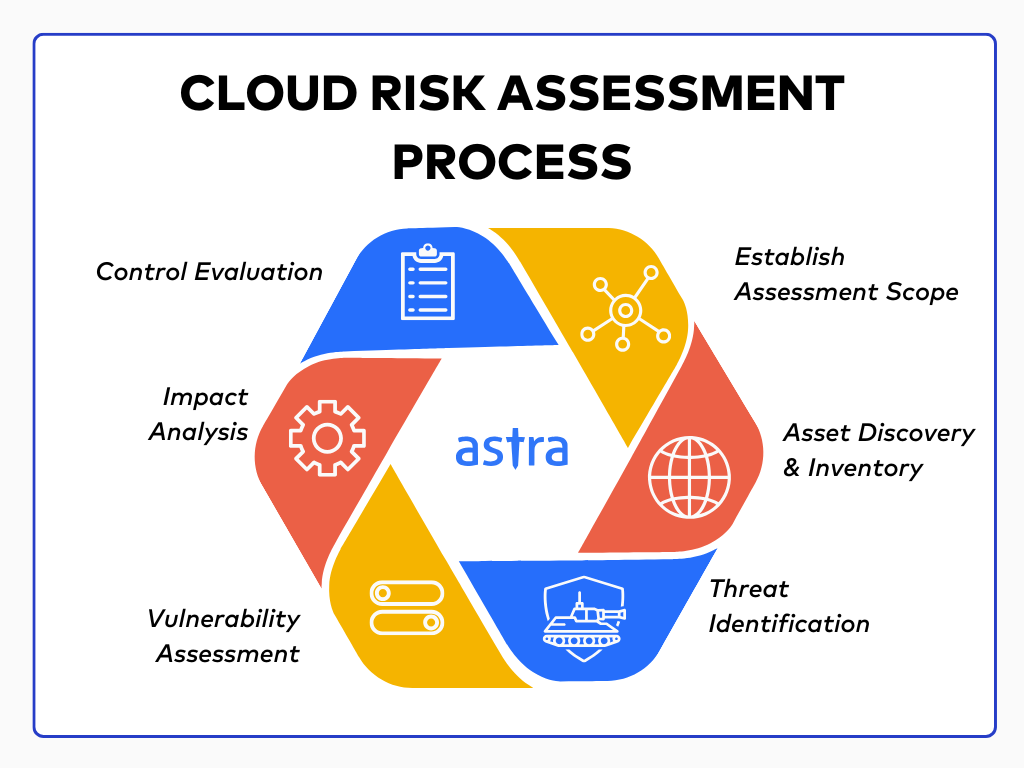
Start by mapping your data flow, not your infrastructure. Draw out where sensitive data lives, how it moves between services, and which team owns each segment. Do this on a whiteboard with people who actually work in those teams. Don't use Confluence. Don't use a diagram tool with pre-made shapes. A piece of paper forces you to think about things that diagrams hide. After the mapping, identify your crown jewels. Usually it's one or two databases. Sometimes it's an API gateway. Rarely is it everything, which is what every team tells me before they realize their classification system is empty. Then do threat modeling. Use something like ATT&CK or a simplified kill chain. Walk through a realistic attack path for each crown jewel. How would someone gain initial access? Lateral movement? Data exfiltration? Write down each step. Then check your controls against each step. The gaps are your risks. Run your configuration assessment tools — Prowler, QuickSecurityCheck, your CSPM — but treat the results as supplementary. They catch misconfigurations. They don't catch architectural decisions that create risk.Here's what most people skip: assessing the blast radius of a single compromised credential. I built a simple script that rotates a test IAM key across all accounts in an organization, uses assume-role to map what it can access, then calculates the total number of resources exposed. It takes about 45 minutes to set up and runs in under five minutes after that. I keep a baseline score and track it monthly. When the score spikes, that's a real signal. Tools that measure "number of findings" tell you nothing about whether any of those findings matter.
Common Pitfalls
The biggest one is treating remediation as the end state. You fix the ten highest-priority findings, close the ticket, and consider the assessment done. But risk is relative. If your top ten risks all belong to a legacy service that the business knows about and has accepted, you've assessed correctly. The problem comes when you fix low-impact issues and miss the one thing that actually matters. Another pitfall is assessing once per year. By the time the report is written, half your cloud environment has changed. I recommend a quarterly full review with continuous monitoring in between. Use a lightweight weekly check that runs your scanners and flags only new or escalated risks. This usually cuts the process down from about 40 hours per quarter to roughly 6 hours of actual review work.When This Approach Fails
If your organization has fewer than 50 cloud resources and a single engineering team, a full risk assessment is overkill. Run a basic configuration audit, have a senior engineer review the findings, and move on. The framework I described assumes complexity worth managing. It doesn't scale down gracefully. The assessment also breaks if leadership refuses to fund remediation. A risk list without a remediation budget is just a document. I've seen teams produce excellent assessments that went nowhere because the cost of fixing was higher than the perceived risk. In those cases, pivot to documenting residual risk formally and moving it to an executive sign-off process. That's still valuable, even if it feels like failure.Cloud Security Risk Assessment
The final piece is making sure your assessment is usable by the people who need it. Engineers want technical detail. Executives want a single number or a color code. Both are right. Structure your report with an executive summary first — three paragraphs, no jargon, what could go wrong, what could protect it, what it would cost to fix. Then append the technical findings with risk ratings tied to your attack path analysis. I use a simple three-tier rating system: critical means active exploit exists and data is exposed, high means a plausible path to data exposure with at least one missing control, medium means a control gap that would require significant effort to exploit. Everything below medium doesn't make it into the main report. It gets logged for tracking but doesn't distract from what actually needs attention.The best risk assessments I've produced were the ones where someone in the room pushed back hard on my assumptions. "Who would actually try to do that?" "That control is already in place, why did you miss it?" "This finding doesn't match our architecture." Those conversations are the whole point. The document is just the record of them.