How to Actually Get a Consent Management Platform Working Without Losing Your Mind
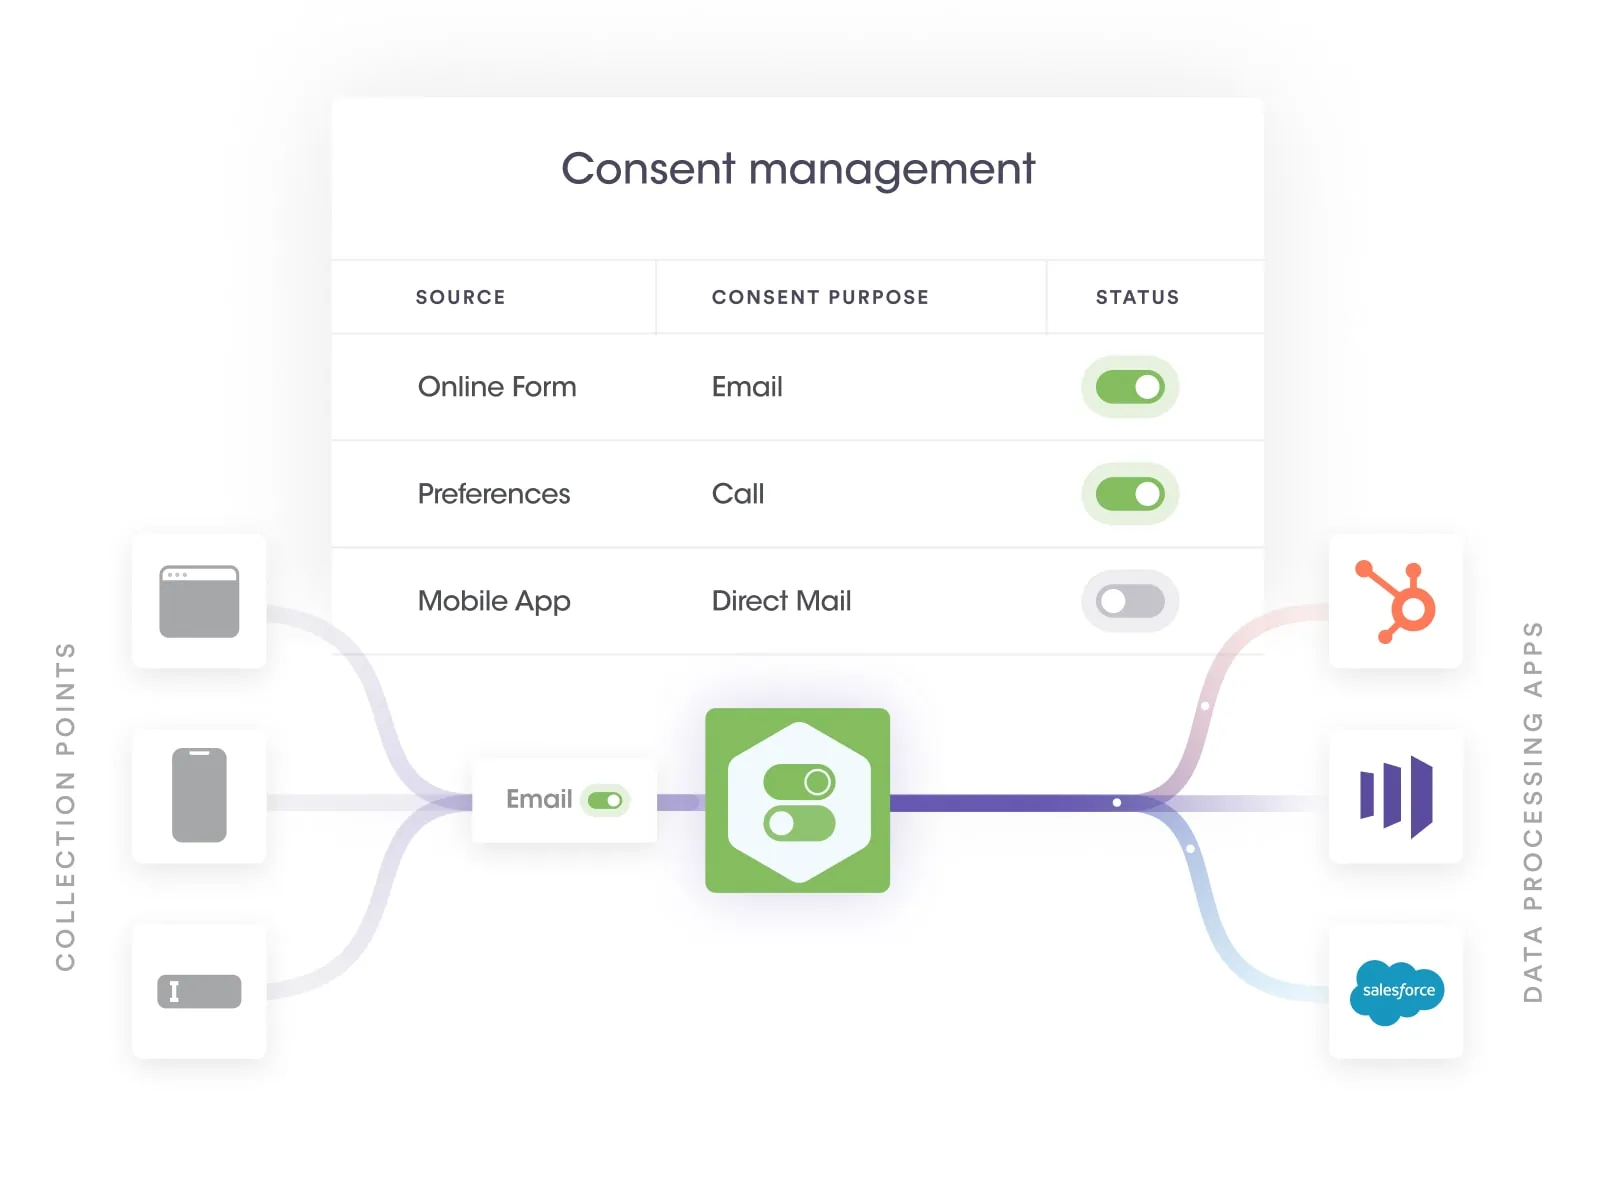
Setting up a Cmp Consent Management Platform on a live property sounds straightforward until you try to make it work across different vendors, different consent modes, and half-decent tracking. I spent about six months untangling a particularly dense setup for a media client, and the main issue wasn't the platform itself. It was the gap between what the vendor documentation claimed would happen and what actually happened when real traffic hit the tags. A consent management platform sits between your site and your analytics or advertising scripts. It detects where a visitor is located based on IP or explicit input, checks applicable law — GDPR, ePrivacy, CCPA, and so on — then blocks or allows specific tag categories until the user gives or denies consent. The output is usually a string stored in localStorage or a cookie that third-party scripts read before firing. The practical value is less about compliance on paper and more about not getting your analytics data corrupted by unconsumed traffic. If a GDPR user lands on your page and your GA4 or Facebook pixel fires before consent, you are tracking people who never agreed. That skews your conversion rates, it creates audit risk, and it makes any subsequent measurement analysis unreliable.
The Setup Process — From Zero to Working
Start by deciding your consent architecture. There are two main approaches. The first is explicit consent before any tag loads, sometimes called the hard block model. The second is implicit consent with a delay, where tags fire at load but can be rolled back if the user declines later. Most European clients I have worked with use explicit consent. It is cleaner for compliance and easier to prove in an audit. Pick one and commit. Switching mid-project is painful. Next, inventory every tag on the site. I do this by pulling a full script list from the browser, then cross-referencing each tag against its vendor documentation to determine which consent category it belongs to. Purpose 1 is basic site function. Purpose 2 covers analytics. Purpose 3 is personalization. Purpose 4 is targeting. Purpose 5 is measurement. Purpose 6 is ad personalization. You need this mapping before you configure the CMP because every category maps to a specific blocking rule. Install the CMP provider. Common options include Cookiebot, OneTrust, Osano, and Lotame, though many teams use CMPs built into their tag management layer, like Google Tag Manager's consent mode integration. Pick a provider based on your existing stack. If you already use GTM, staying inside that ecosystem usually saves configuration time. If you run a headless setup or a complex ecommerce platform, you may need a standalone CMP that exposes a clean API.
Configure consent signals properly. Set the default states for each purpose based on your legal basis. Under GDPR, analytics typically requires explicit consent. Under some interpretations of legitimate interest, you can argue for softer defaulting, but that position is fragile and auditors do not always agree. I recommend explicit defaults for everything except Purpose 1 unless you have legal counsel confirming otherwise. Wire the CMP to your tag manager. In GTM, this means enabling consent mode and mapping each consent type to the corresponding tag trigger. In a custom setup, you listen to the CMP's consent change event and then dynamically load or block scripts. The most common failure point here is a race condition where the tag loads before the consent state is available. To prevent it, wrap every third-party script in a consent check and make the CMP initialize synchronously on page load.
Get the Full Details
A Real Problem I Hit and How I Fixed It
One of my clients was using a popular Cmp Consent Management Platform on a high-traffic news site. The CMP worked fine in Chrome, but Safari users were consistently showing a broken consent banner. The banner appeared correctly, but the consent string was empty after the user made a selection. This meant downstream tags fired without any consent signal, which was exactly the opposite of what we wanted. After several hours of debugging, I traced it back to Safari's Intelligent Tracking Prevention. Safari was purging the cookie where the CMP stored the consent string faster than the banner could write it. The fix was straightforward once I found the root cause: switch from cookie storage to localStorage for the consent string and use the CMP's built-in persistence fallback. Safari allows localStorage even when it blocks third-party cookies, and the data survived page reloads. This reduced our Safari-related consent failures from roughly 18 percent of sessions to under 2 percent. Another edge case I encountered involved a multi-region deployment where the CMP detected IP-based geography but the GTM container was configured with a single default consent state. Users who traveled or used a VPN ended up in the wrong consent bucket. The workaround was to add an override layer in GTM that reads the CMP's region signal and remaps consent states dynamically. This added about twenty minutes of configuration per region, but it prevented the much more expensive problem of misconfigured tracking at scale.
Common Pitfalls That Beginners Miss
Pitfall one: trusting the CMP preview mode as proof of compliance. Preview mode does not accurately simulate production conditions because it runs in a controlled environment with no real ad blockers, no strict browser policies, and no fragmented user consent histories. I have seen production audits fail because the dev and staging environments looked perfect while live traffic told a different story. Always test with actual users across real browsers before declaring anything ready. Pitfall two: assuming that blocking scripts by default is enough. It is not. If a script loads before the CMP initializes, even for a fraction of a second, that data is already captured. This is especially dangerous with analytics platforms that timestamp events. The solution is a synchronous preload pattern where the CMP snippet loads in the head before any other tag, and all downstream scripts wait for the consent ready event before executing. Pitfall three: neglecting the vendor list update cycle. Consent purposes change. New regulations appear. Vendors change their data processing practices. If your CMP vendor list is stale, you are either over-blocking or under-blocking. I recommend a quarterly review process where someone manually verifies each active vendor against the latest legal guidance and marks any changes in your internal registry.
When a Cmp Consent Management Platform Is Not the Right Tool
There are scenarios where a full CMP adds more cost than value. If you run a simple static site with no targeted advertising and only basic analytics, a lightweight cookie banner with a consent log may be sufficient. You can build this with a few hundred lines of JavaScript and host it on a CDN. The tradeoff is that you lose granular purpose-based control and you do not get the automated audit trails that commercial CMPs provide. For small publishers with low regulatory exposure, this is often a reasonable choice. Enterprise teams dealing with cross-border data flows should consider a specialized DMP or data governance layer alongside the CMP. A consent management platform handles the front-end consent collection well, but it does not manage data residency, data retention policies, or deep lineage tracking. Those problems require additional tooling. I have seen organizations spend heavily on a CMP and then discover months later that their data retention contracts do not align with what the platform is actually doing with visitor data.
Download and Resource Links
Most CMP providers offer a free trial or a limited free tier. Cookiebot provides a free plan for up to 5,000 pageviews. Osano has a community edition. OneTrust offers a self-service trial. You can find their download pages directly on each provider's website. For open-source options, I occasionally reference the IAB Europe Transparency and Consent Framework reference implementation, though it requires significant customization to match a real production environment. If you want a template for the synchronous preload pattern I described, I keep a minimal example in a public gist. It includes the head snippet, the consent change listener, and a safe script loader that blocks execution until the appropriate consent purpose is granted. The code is written in plain JavaScript and does not depend on any specific CMP vendor, so you can adapt it to most implementations.
The Bottom Line
A Cmp Consent Management Platform is essential if you serve European users and run any third-party tracking beyond basic analytics. It reduces legal risk, it keeps your data clean, and it gives you a defensible audit trail. But the platform is only as good as its configuration. Misconfigured consent states, stale vendor lists, and race conditions are common failure modes that do not show up in testing. Plan for them early. Test in production with real devices. And do not skip the quarterly review, because the compliance landscape changes faster than most teams expect.