COBIT 5 and Risk Management: What Actually Happens When You Try to Implement It
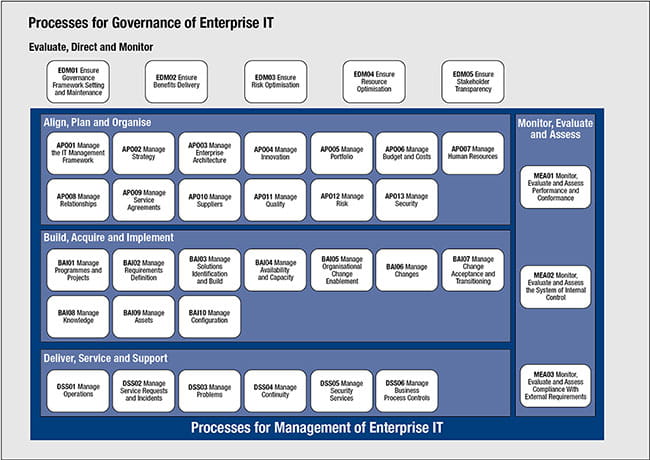
Most people grab COBIT 5 and immediately look at the risk chapter without understanding the surrounding architecture. They miss that COBIT 5 for Risk isn't a standalone document you can just "implement." It's one thread woven through all of the framework's 37 processes. Trying to bolt it on separately is why so many organizations end up with a binder full of risk registers that nobody updates. The core risk management process in COBIT 5 is APO12 — Manage Risk. That's the one you'll be auditing against. But it doesn't exist in isolation. EDM03 oversees risk optimization at the governance level, MEA01 monitors compliance, and DSS05 manages security and confidentiality from a risk lens. All of them intersect. If your risk team only operates inside APO12, you're going to have a messy implementation.
COBIT 5 For Risk Isaca Framework Overview
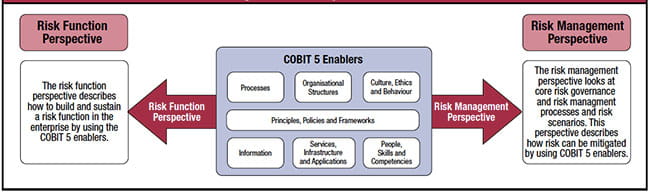
The ISACA approach to risk in COBIT 5 is built around the idea that risk management is continuous, not periodic. You're supposed to identify risks, assess them, treat them, monitor the treatment, and feed lessons back into identification. The model expects you to do this across the entire enterprise IT landscape, not just the security team's desk. Here's what that looks like in practice. COBIT 5 breaks risk management into stages that map to the plan-engage-monitor cycle. You start with understanding the risk context and defining your risk appetite statement. Then you move to risk assessment — which means scoring likelihood and impact using your organization's scale. After that comes risk response: accept, mitigate, transfer, or avoid. Finally, you monitor and report. The whole thing is supposed to loop back to the beginning on a regular cadence. I found the biggest gap in most implementations is that people skip the appetite statement entirely. They go straight to identifying risks and scoring them. Without a documented appetite, your scoring is arbitrary. One person's "high" is another person's "medium." We lost three weeks recalibrating risk scores because nobody had actually signed off on what the organization was willing to tolerate. The fix was straightforward once we realized the problem. We brought in the C-suite, spent two meetings agreeing on broad categories of risk they'd accept versus those requiring action, and wrote a one-page statement. It didn't need to be elegant. It just needed to exist and have someone with budget authority sign it.
The official COBIT 5 material is available through the ISACA store. You can find the COBIT 5 framework book and the separate risk management guide at isaca.org. There isn't a single free "COBIT 5 for Risk" download that covers everything. ISACA sells the core framework, and the risk-focused content is embedded within it rather than published as a standalone free resource. Some of the process descriptions and control objectives are available on their website for free if you search for individual process goals. A counter-intuitive thing about COBIT 5's risk framework that beginners consistently miss: the model assumes you already have governance in place before you do serious risk management. If your IT governance structure is weak — unclear roles, no steering committee, decisions made by whoever yells loudest — running APO12 will produce documentation that looks good but changes nothing. Risk ownership becomes meaningless when nobody can actually authorize a risk response. I've seen this play out in three different organizations. The risk register became a performance art piece rather than a management tool. The workaround was to delay the full risk assessment and spend two months first cleaning up the governance structure: define the risk owner roles, establish a risk committee with real decision-making power, and get it operational before opening the risk identification workshops. Another thing the framework doesn't emphasize enough is the tension between COBIT 5's comprehensive approach and the reality of smaller organizations. COBIT 5 was designed for large enterprises with dedicated governance staff. If you're a mid-size company with one person responsible for IT risk on top of everything else, the full APO12 process will consume 40 percent of your time in year one with diminishing returns. In those cases, I usually recommend starting with a simplified risk assessment aligned to COBIT 5's control objectives but using a lighter methodology like ISO 31000 for the actual risk assessment steps. COBIT 5 gives you the governance wrapper. ISO 31000 gives you the practical assessment engine. Combining them gets you closer to compliance without the overhead.
Get the Full Details

The monitoring aspect — MEA01 and the associated risk monitoring indicators — is where most audit findings come from. Not because the risk identification is wrong, but because the follow-through doesn't exist. You identify a risk, you assign an owner, and then you never check if the treatment actually happened. The framework calls for periodic status reviews of risk responses. In my experience, those reviews happen quarterly at best, and often only when something goes wrong. Set up a standing agenda item in your IT leadership meeting. Fifteen minutes a month checking the status of open risk treatments takes almost nothing and dramatically improves your audit results. If you're preparing for an audit against COBIT 5's risk management practices, the evidence they'll ask for is straightforward: documented risk appetite, a current risk register with ownership assigned, evidence of risk treatment decisions, and records showing monitoring and review activities. Keep it simple. Don't create elaborate documentation that you can't sustain. An accurate register updated monthly beats a perfect one sitting on a shelf.