What They Actually Do
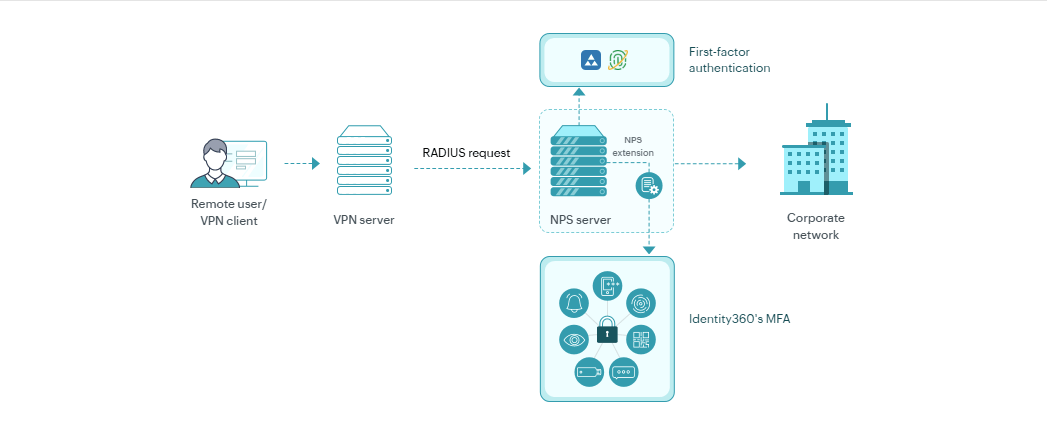
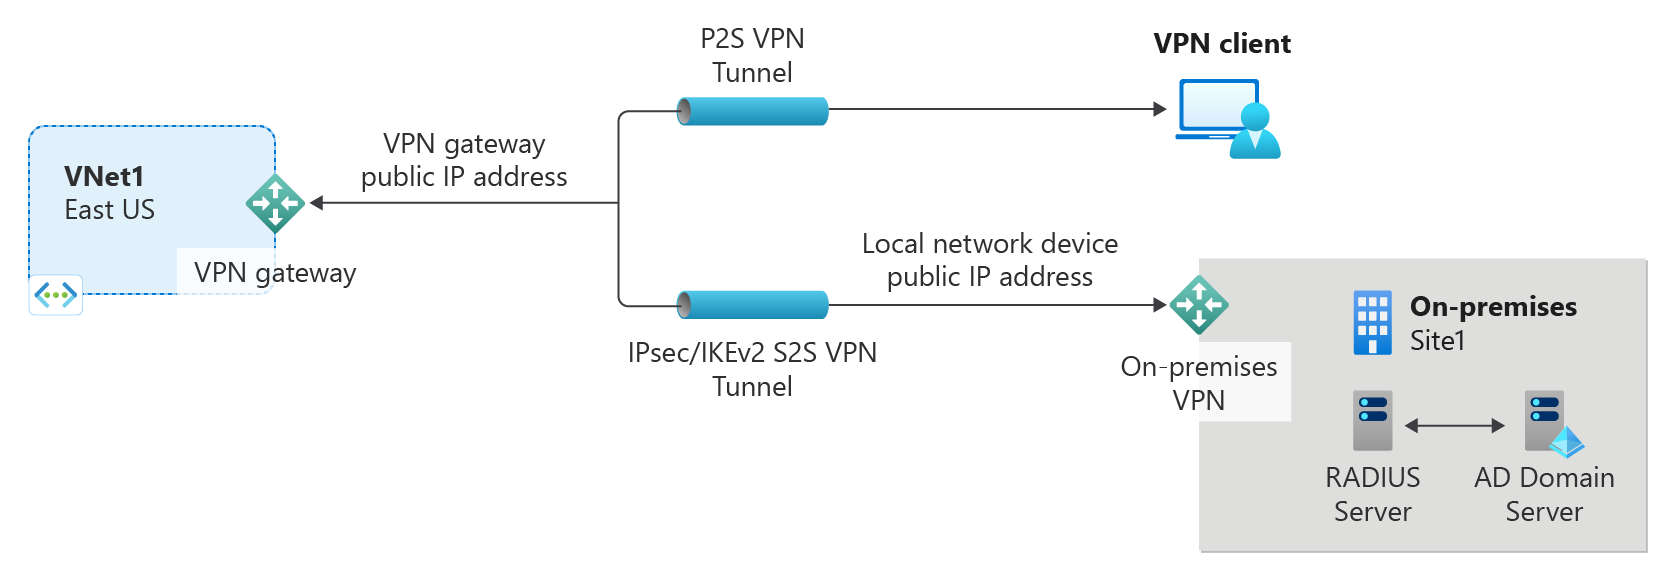
VPN and RADIUS solve different problems and often work together. People who are just getting into networking sometimes conflate them because both deal with authentication and remote access. They are not the same thing, and comparing them properly takes a bit of effort. I have spent years debugging situations where these two were incorrectly assumed to be interchangeable, and it always comes down to understanding the separation between transport and authentication. A VPN is a tunneling protocol. It takes your network traffic and wraps it so it can traverse an untrusted network like the public internet. You have your standard options: OpenVPN, WireGuard, IPSec, SSTP, L2TP. Each one encrypts the payload and creates a virtual interface on both ends. The traffic then flows through that encrypted pipe as if it were on a private LAN. That is the entire job of a VPN. It does not decide who gets in. It does not maintain user records. It moves packets from point A to point B securely. RADIUS is a completely different layer. It stands for Remote Authentication Dial-In User Service and it is an authentication, authorization, and accounting protocol. It does not create tunnels. It does not encrypt traffic at all on its own. What it does is answer questions like "who is this person, do they have permission, and what did they do while connected." When someone tries to connect to a VPN, the VPN server often hands off the credential check to a RADIUS server. That is where the two technologies meet in practice.
Compare Vpn Technology To Radius
The practical difference is that a VPN handles the connection itself while RADIUS handles the identity verification. If you strip it down to the most basic comparison, a VPN is the road and RADIUS is the toll booth that checks your pass before letting you on it. One moves data securely. The other manages who is allowed to move data. Here is where it gets messy for people who are trying to build or manage infrastructure. A lot of organizations run RADIUS alongside their VPN gateways, and in some setups like Cisco's AAA framework or FreeRADIUS acting as a backend for pfSense or FortiGate, the VPN server will offload authentication entirely to RADIUS. You might see references to RADIUS inside VPN documentation and assume they are the same category of tool. They are not. One is a transport mechanism. The other is a directory and policy engine. I spent about three weeks troubleshooting a case where our VPN setup was failing intermittent authentication for about ten percent of users. The logs showed successful tunnel establishment but then immediate disconnects. The RADIUS server was responding with access-challenge instead of access-accept for certain users, and the issue was that we had assigned different shared secrets between the VPN concentrator and the RADIUS backend for two subnets. The first subnet worked fine. The second subnet had the wrong shared secret baked into the NAS configuration. That mismatch caused the RADIUS server to reject the credentials silently, and the VPN client just saw a disconnect. Took me forever to track down because the VPN logs looked clean and the RADIUS logs just showed rejected packets without clear context. The workaround was to standardize the shared secret across all NAS devices and enable detailed RADIUS accounting to catch these mismatches earlier.
When you Compare Vpn Technology To Radius from a deployment perspective, the VPN side involves choosing a protocol, setting up certificates or pre-shared keys, configuring the tunnel endpoints, and managing encryption parameters. The RADIUS side involves maintaining a user database, setting up authorization profiles, configuring network access servers as RADIUS clients, and managing shared secrets between every device that talks to it. Each has its own failure modes and security considerations. VPNs can leak traffic if DNS resolution happens outside the tunnel. RADIUS servers can become single points of failure if not redundantly configured, and shared secrets are often stored in plaintext config files which is a real risk if your server gets compromised. There is also the matter of scalability. A well-tuned VPN concentrator can handle thousands of concurrent tunnels with moderate hardware. A RADIUS server under heavy load, especially one doing per-session accounting, can start dropping packets or introducing latency that makes the VPN connection feel unstable. I have seen RADIUS response times jump from under ten milliseconds to over two seconds when the backend database hit a locking bottleneck during peak hours. That directly impacts VPN user experience because every reauthentication or credential check goes through RADIUS first. One thing beginners usually miss is that RADIUS can authenticate things that are not VPNs at all. Wireless LAN controllers use it extensively. Network switches use it for port-based access control. SSH jump hosts sometimes route authentication through it. So narrowing your view to just VPN comparisons misses a big chunk of what RADIUS actually does in enterprise environments. Meanwhile, VPN technology has evolved into things like split tunneling, which changes how RADIUS authorization profiles need to be structured because you might want to authorize different routes for different user groups.
Get the Full Details
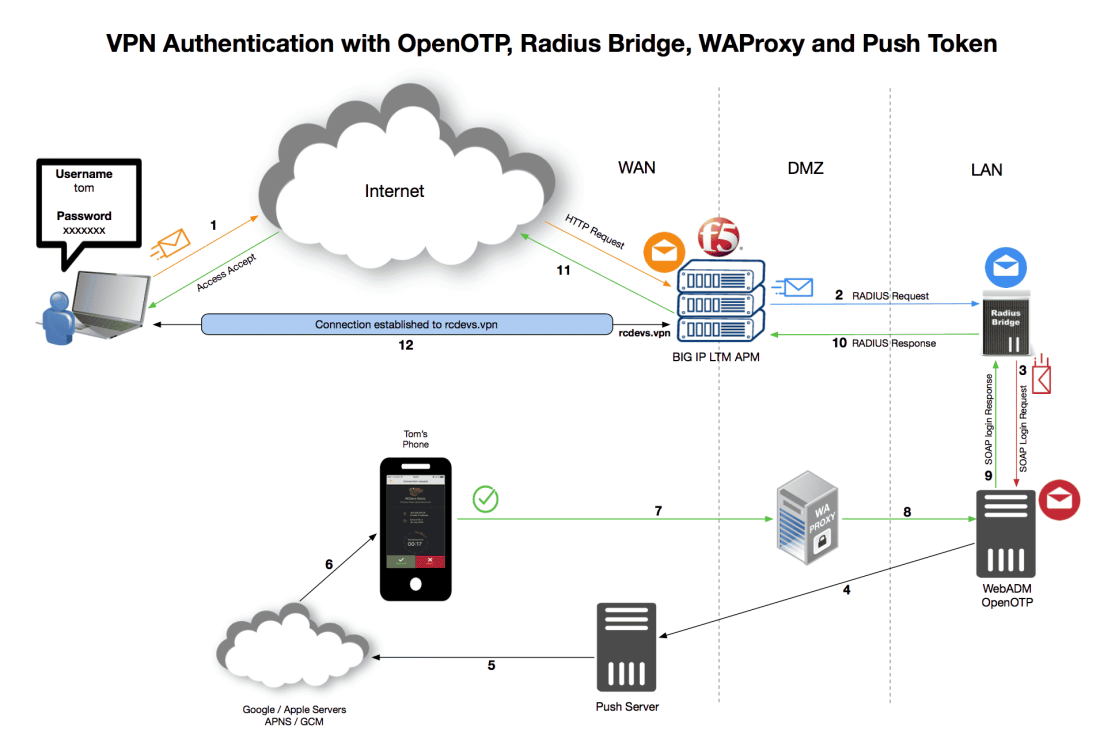
If you are trying to set up either system and you run into issues, start by checking the separation between the two. Make sure the VPN server is reaching the RADIUS server at all. Verify shared secrets match exactly. Check that the NAS IP address in the RADIUS client configuration matches the source IP the VPN server uses when it sends authentication requests. These three things account for probably sixty percent of the problems I see in production environments.