Why Your First Compliance Framework Will Feel Like Shuffling Cards
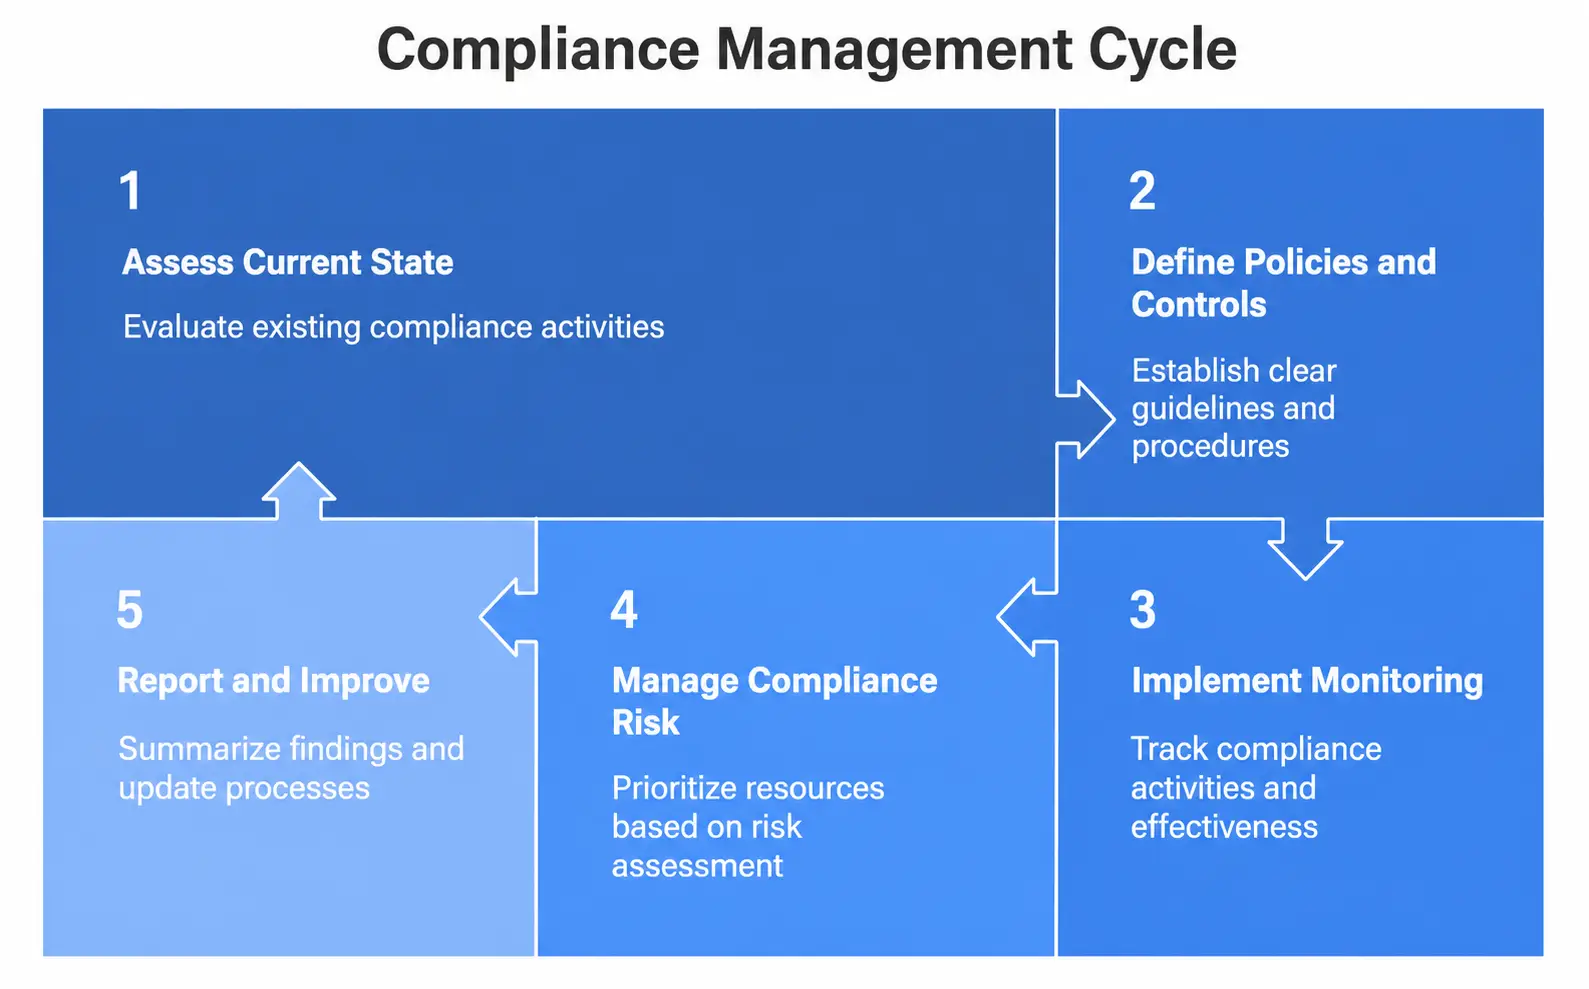
I spent three years building out a compliance management system for a mid-size fintech before I realized the problem wasn't the tooling. It was the mapping. Every regulation—GDPR, CCPA, SOX Section 404, PCI-DSS—uses different terminology for essentially the same control. "Data minimization" in one standard is "limiting retention" in another. When you first try to align them, you end up with a spreadsheet that has 400 rows and nobody can figure out which controls actually matter. The trick is to stop treating compliance as a checklist exercise and start treating it as a control taxonomy problem. You build a single source of truth for what your organization actually does, then map regulations to your reality instead of the other way around.
Compliance Management A How To For Executives Lawyers And Other Compliance Professionals
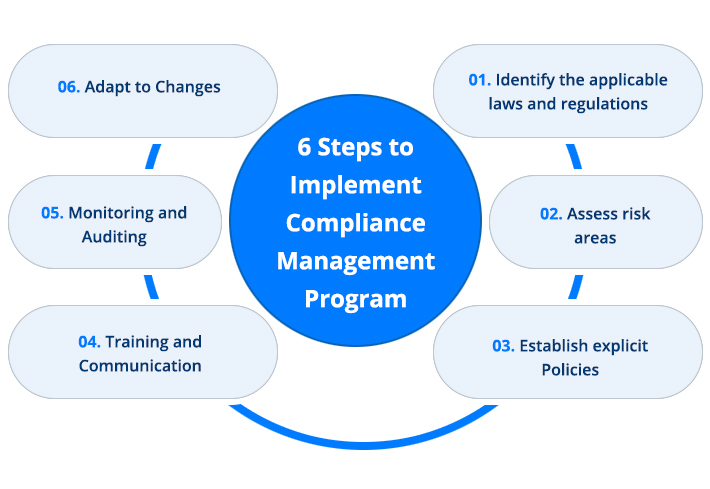
Here is how I actually set this up, not the textbook version. Start with the controls library. Before you write a single policy, you need to define what "adequate security" means for your organization in concrete terms. This usually takes the form of a control catalog—that might sound academic but it is the single most important document you will produce. I typically structure it around four layers: governance controls (who owns what), people controls (background checks, training, access reviews), technical controls (encryption, logging, MFA), and physical controls (badge access, server room procedures). Each control gets a unique identifier, a plain-language description, an owner, and a current status. Not "implemented" or "not implemented"—those categories are too coarse. I use four states: designed but not operating, operating with gaps, operating as intended, and optimized. The moment you create this document, every compliance conversation changes. Instead of arguing about whether you meet GDPR Article 32, you can open the control catalog and show exactly which controls address that requirement and how they are performing. Executives understand status tracking. Lawyers prefer it to narrative arguments.
After the control catalog comes the risk assessment methodology. This is where most organizations fail because they either skip it entirely or produce a document that sits on a shelf. A functional risk assessment uses the standard formula of likelihood times impact, but the critical detail is defining your likelihood and impact scales in business terms. "High impact" means a breach that would cost more than $500,000 in direct fines, remediation, and lost revenue. "Medium impact" falls between $100,000 and $500,000. "Low impact" is under $100,000. For likelihood, I use a five-point scale based on actual incident data from the past two years, not gut feelings. If you have no incident data, you use threat intelligence reports and industry benchmarks, but you document the source. When I conducted a risk assessment for a healthcare client last year, I hit a specific edge case that took me about two days to resolve properly. The organization had legacy systems running Windows Server 2012 that could not be patched because the original vendor no longer supported them. Standard risk methodology would classify this as unacceptably high risk. But the systems were air-gapped and only processed de-identified research data that never touched patient records. The workaround was to document a compensating control: network segmentation verified through quarterly penetration testing, strict change management procedures, and a monitored exception process with executive sign-off. The risk register showed the residual risk as acceptable because the compensating controls reduced the likelihood from "likely" to "possible" and the impact remained low since the data was non-identifiable. Without that documentation, any auditor would have flagged it as a critical finding regardless of the actual security posture. Policy development follows the control catalog. Most organizations write policies that are too long and too vague. A functional policy should be no more than two pages, written in plain language that an employee can understand after reading it once. The structure I use is purpose, scope, responsibilities, procedures, and enforcement. Purpose explains why the control exists in one paragraph. Scope defines who and what it applies to. Responsibilities name specific roles, not departments. Procedures describe the actual steps, ideally as a flowchart or numbered list. Enforcement states the consequences of non-compliance without threats.
Get the Full Details
Training and awareness is where compliance programs either work or fail, and it has nothing to do with the training content itself. The research from the Ponemon Institute consistently shows that organizations with annual compliance training have 40 percent fewer security incidents than those with one-time training, but the difference is not the curriculum. It is the frequency. I recommend quarterly micro-training sessions of 15 minutes focused on a single topic—phishing recognition in Q1, password hygiene in Q2, data handling in Q3, incident reporting in Q4. These sessions should be mandatory and tracked, but they should also be optional in terms of engagement. Allow employees to complete them during work hours without guilt. The organizations that treat compliance training as a punishment metric end up with employees who click through slides without reading them. Monitoring and measurement requires metrics that actually reflect compliance performance, not activity counts. "Completed 500 training sessions" is an activity metric. "Reduced phishing susceptibility from 28 percent to 9 percent over six months" is a performance metric. I track three categories of compliance metrics: coverage metrics (what percentage of controls are documented and assigned), effectiveness metrics (are the controls working as intended), and timeliness metrics (are we responding to findings within our stated SLAs). Coverage metrics should be reported monthly to leadership. Effectiveness metrics quarterly. Timeliness metrics weekly to the compliance team. Incident response is the test that reveals whether your compliance program has any substance. Most organizations have an incident response plan that has never been tested. When I review incident response documentation, I look for three things: clear escalation paths that actually exist, communication templates that are pre-approved, and post-incident review procedures that produce actionable changes. The communication templates are critical because during an actual incident, people revert to habit and habit is writing from scratch. Pre-approved templates for regulators, customers, and internal stakeholders reduce response time from hours to minutes.
Auditing and evidence collection is the part that consumes the most time in any compliance program. I recommend a continuous evidence collection approach rather than point-in-time snapshot collection. This means maintaining a shared repository where evidence is uploaded as it is generated, not compiled when an auditor asks for it. A simple SharePoint folder structure organized by control ID and month is sufficient. Each piece of evidence gets a metadata tag with the date, owner, and control reference. This reduces evidence gathering time from an average of 40 hours per audit cycle to approximately 6 hours. The biggest mistake executives make with compliance management is treating it as a cost center rather than a capability. This is particularly problematic when you are building a new program because the early stages feel expensive and unproductive. You will spend three to six months building control catalogs and risk assessments before you see any tangible benefit. The benefit is invisible until something goes wrong, at which point the program pays for itself ten times over. I have seen organizations skip this phase and jump straight to certification, which produces a certificate and a lot of technical debt that costs three times as much to fix later. Lawyers approach compliance differently than operations teams, and both approaches are necessary. Legal teams tend to focus on regulatory language and precedent. Operations teams focus on control implementation and business process integration. The friction between these approaches is normal and productive if managed correctly. I recommend establishing a compliance steering committee with equal representation from legal, operations, and executive leadership. This committee meets monthly and reviews the control catalog, risk register, and metric reports. The committee makes decisions about risk acceptance, resource allocation, and policy exceptions. Without this governance structure, compliance programs drift toward either legal caution or operational convenience, and neither position alone produces adequate results.
Vendor management is the compliance blind spot that catches most organizations. Your vendors become your compliance responsibility when they process your data or operate systems you rely on. I recommend a three-tier vendor risk assessment process: Tier 1 covers critical vendors who process sensitive data, requiring full due diligence and annual reviews. Tier 2 covers important vendors with limited data access, requiring questionnaire-based assessments every two years. Tier 3 covers commodity vendors with no data access, requiring only contract review. This tiering usually reduces vendor assessment workload by 60 percent while focusing resources on the vendors that actually matter for compliance. Technology selection for compliance management should prioritize integration over features. The best compliance platform in the world is useless if it cannot connect to your existing identity management, logging infrastructure, and ticketing systems. I recommend evaluating platforms on four criteria: API availability for automated evidence collection, reporting flexibility for custom metric dashboards, user adoption rate among non-compliance staff, and total cost of ownership including implementation and maintenance. The cheapest platform usually costs the most in implementation time and support hours. There are scenarios where compliance management frameworks completely fail, and it is important to recognize them. Small organizations under 50 employees typically cannot sustain a formal compliance program because the overhead exceeds the benefit. In these cases, a simplified control framework based on a single standard like NIST 800-53 Rev 5 or ISO 27001 Annex A is more practical than a multi-regulation alignment approach. Similarly, highly regulated industries like financial services or healthcare often face conflicting requirements where compliance with one regulation creates non-compliance with another. These conflicts require executive-level decision making documented in writing, because the alternative is trying to satisfy contradictory requirements and satisfying neither.

Another limitation of compliance management programs is the recency bias in risk assessment. Organizations tend to assess risk based on recent incidents rather than statistical probability. If a phishing attack occurred last quarter, phishing becomes the highest priority regardless of whether it is actually the most likely threat vector. I recommend using actuarial data and industry benchmarks to calibrate risk assessments, then adjusting for organization-specific factors. This approach usually produces risk priorities that differ significantly from instinct-based assessments, but they align better with actual probability distributions. The documentation requirements for compliance programs are substantial but necessary. Every control needs a design document explaining how it works, an operating document explaining how it is executed, and an evidence archive containing proof of operation. This triple documentation standard sounds excessive until you are defending a control during an audit and cannot find the evidence because it was stored in someone's personal drive rather than the centralized repository. I recommend establishing a documentation retention policy of seven years for all compliance records, which exceeds most regulatory requirements but provides adequate buffer for statutes of limitations and historical reference. Compliance program maturity follows a predictable five-stage model: initial, managed, defined, quantified, and optimizing. Most organizations operate at stage two or three. Stage one means no formal program exists. Stage two means policies are documented but inconsistently applied. Stage three means controls are consistently applied and measured. Stage four means the program uses statistical techniques to predict and prevent compliance failures. Stage five means the program continuously improves based on feedback from incidents and audits. Moving from stage two to stage three typically takes 12 to 18 months of dedicated effort. Moving from stage three to stage four requires investment in automation and data analytics that most organizations cannot justify immediately.
The ROI of compliance management is difficult to quantify in traditional terms because the primary benefit is avoided loss rather than generated revenue. I recommend calculating ROI using a risk-adjusted return model: the expected value of losses prevented minus the cost of the compliance program. If your annualized loss expectancy for a particular risk is $2 million and your compliance program costs $400,000 annually while reducing that loss expectancy by 75 percent, the program generates $1.1 million in net value. This calculation requires reasonable estimates of loss expectancy and risk reduction, but it produces numbers that executives understand better than abstract compliance benefits. Regulatory change management is the ongoing challenge that separates mature programs from immature ones. Regulations change constantly—new standards emerge, existing standards are updated, and regulatory interpretations shift. A mature compliance program includes a regulatory change management process that monitors relevant regulations, assesses the impact of changes on existing controls, and implements modifications within defined timeframes. I recommend assigning regulatory monitoring to specific individuals rather than treating it as a group responsibility, because distributed ownership produces no ownership. The monitoring individual should produce quarterly regulatory change reports for the compliance steering committee. Data mapping and inventory is the foundation that supports almost every compliance requirement. GDPR requires you to know what personal data you process and where it flows. CCPA requires the same for California residents. SOX requires you to know what financial data you process and who accesses it. A comprehensive data inventory that covers all regulated data types reduces duplication of effort and ensures that compliance activities build on shared infrastructure rather than parallel systems. I recommend using automated discovery tools where possible, but validating the results through manual sampling because automated tools consistently miss data stored in unexpected locations like shared drives, personal accounts, and backup systems.
Access management is the control category that intersects with the most regulations. Nearly every compliance framework requires some form of access control, but the specific requirements vary. GDPR emphasizes purpose limitation and data minimization. PCI-DSS emphasizes role-based access and least privilege. SOX emphasizes segregation of duties. A unified access management framework that satisfies the common requirements while addressing the specific variations reduces complexity and improves security. I recommend implementing quarterly access reviews for all privileged accounts and annual reviews for all standard accounts, with automated reminders and escalation procedures for overdue reviews. Encryption and key management is another critical control category with varying regulatory requirements. GDPR and HIPAA require encryption of protected health information and personal data at rest and in transit. PCI-DSS requires encryption of cardholder data. NIST guidelines provide detailed technical specifications. The common thread is that encryption without proper key management is worse than no encryption because it creates false confidence. I recommend implementing a key management system that centralizes key generation, storage, rotation, and destruction, with audit logging for all key operations. The system should support both hardware security modules for high-value keys and software-based solutions for lower-value keys, with appropriate controls for each tier. Logging and monitoring requirements vary significantly across regulations but share common principles. GDPR requires logging of access to personal data. PCI-DSS requires comprehensive audit trails for all system components. SOX requires logging of financial transactions and changes. A centralized log management system that collects logs from all relevant sources, retains them for the required periods, and provides search and alerting capabilities satisfies most regulatory requirements while providing operational security benefits. I recommend retaining logs for a minimum of one year online and seven years in archive, which exceeds most regulatory requirements but provides adequate coverage for investigations and audits.
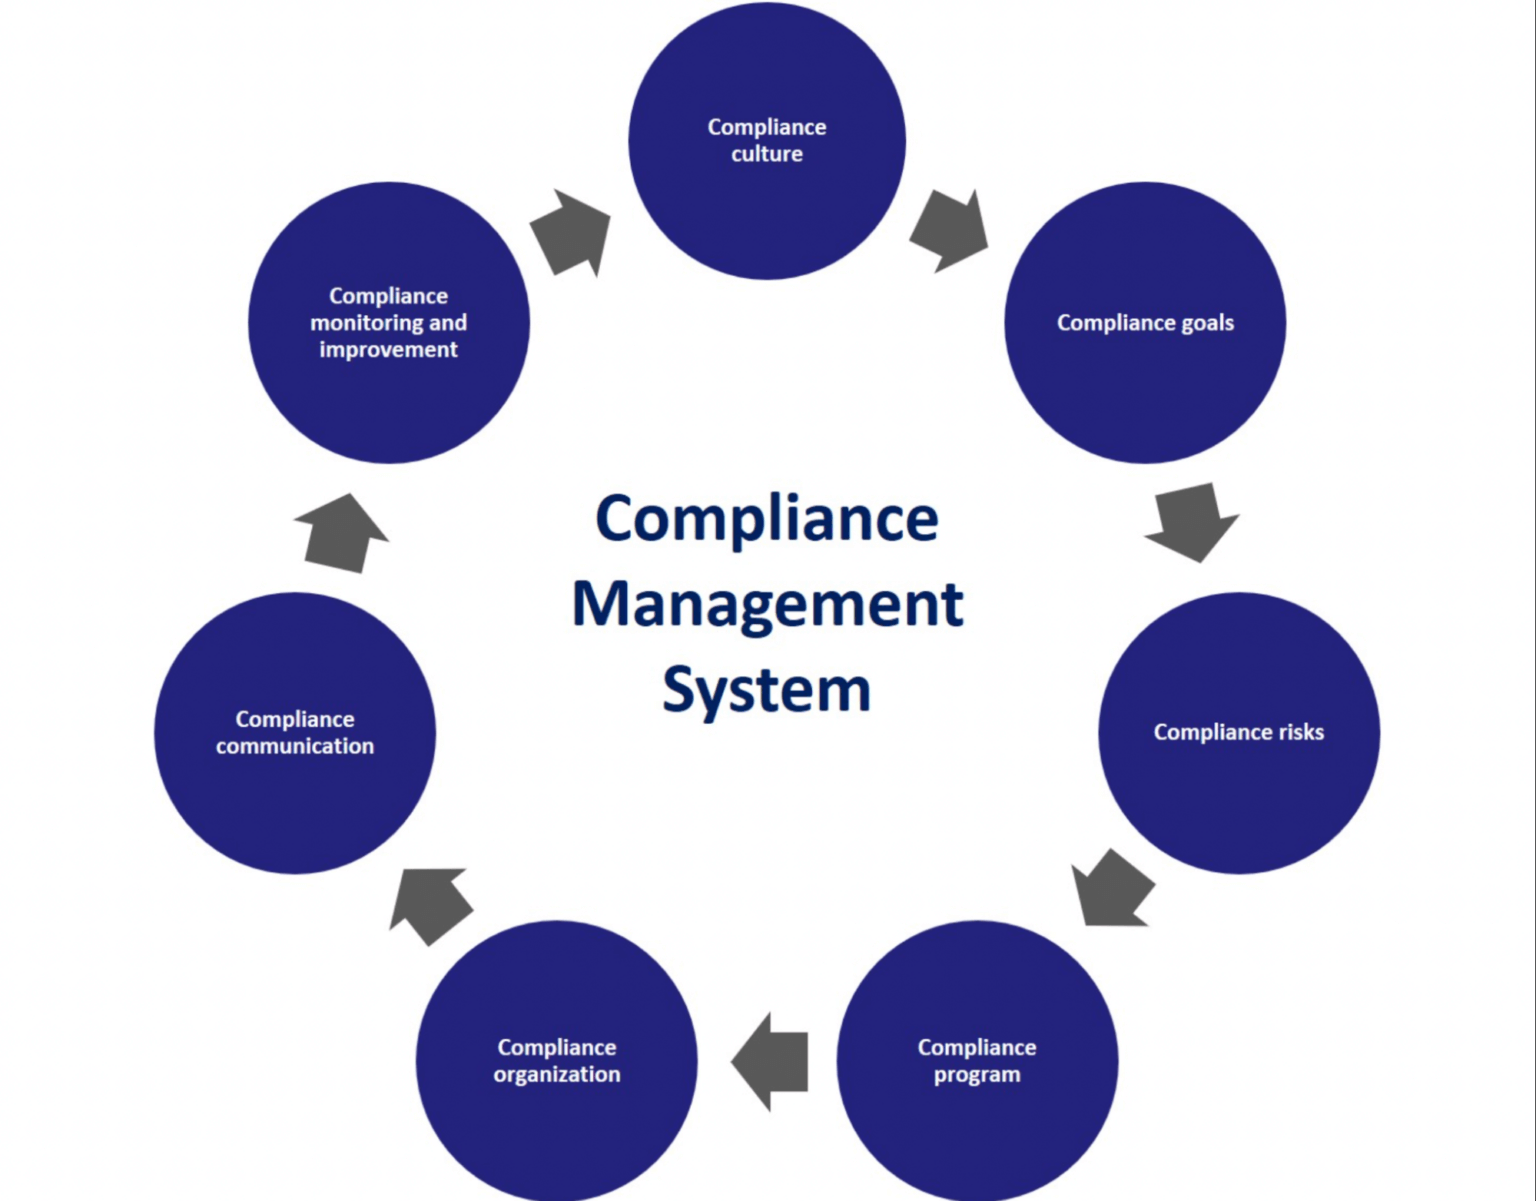
The human element remains the weakest link in almost every compliance program. Technical controls can be automated and monitored, but human behavior requires ongoing attention and cultural reinforcement. I recommend combining formal training with informal reinforcement through leadership communication, recognition programs for compliant behavior, and consistent enforcement of non-compliance consequences. The reinforcement should be visible and regular, not annual and ceremonial. Monthly leadership communications about compliance performance, quarterly recognition of compliant behavior, and consistent application of consequences for violations create a compliance culture that technical controls alone cannot achieve. Budget planning for compliance programs should follow a base-plus-growth model. The base budget covers ongoing operations: personnel, tools, training, and auditing. The growth budget covers new initiatives: regulatory changes, business expansions, technology implementations, and risk remediation. Allocating separate budgets for base and growth prevents operational activities from consuming resources needed for improvement initiatives. I recommend targeting a base-to-growth ratio of 70-30, meaning 70 percent of the budget supports ongoing operations and 30 percent supports improvement initiatives. This ratio varies by organization maturity, with immature programs requiring higher growth investment and mature programs requiring higher base investment. Communication with stakeholders requires different approaches for different audiences. Executives need summary metrics and risk status. Lawyers need regulatory language and precedent analysis. Operations teams need procedures and control descriptions. Auditors need evidence and documentation. I recommend establishing a communication plan that specifies what information each audience receives, how frequently, and through what channels. The plan should include both proactive communication about compliance performance and reactive communication about incidents and findings. Proactive communication builds trust and demonstrates value. Reactive communication manages expectations and demonstrates responsiveness.
Finally, compliance program success depends on executive sponsorship and organizational culture more than any technical factor. A well-designed program with executive support and cultural alignment will succeed despite imperfections. A technically perfect program without executive support and cultural alignment will fail regardless of how sophisticated the controls are. I recommend measuring executive engagement through visible participation in compliance steering committee meetings, resource allocation decisions, and public communication about compliance importance. Organizations with engaged executive leadership typically achieve compliance maturity one stage faster than organizations with passive executive leadership, regardless of budget or tooling differences.