Understanding Congruence in Mathematics
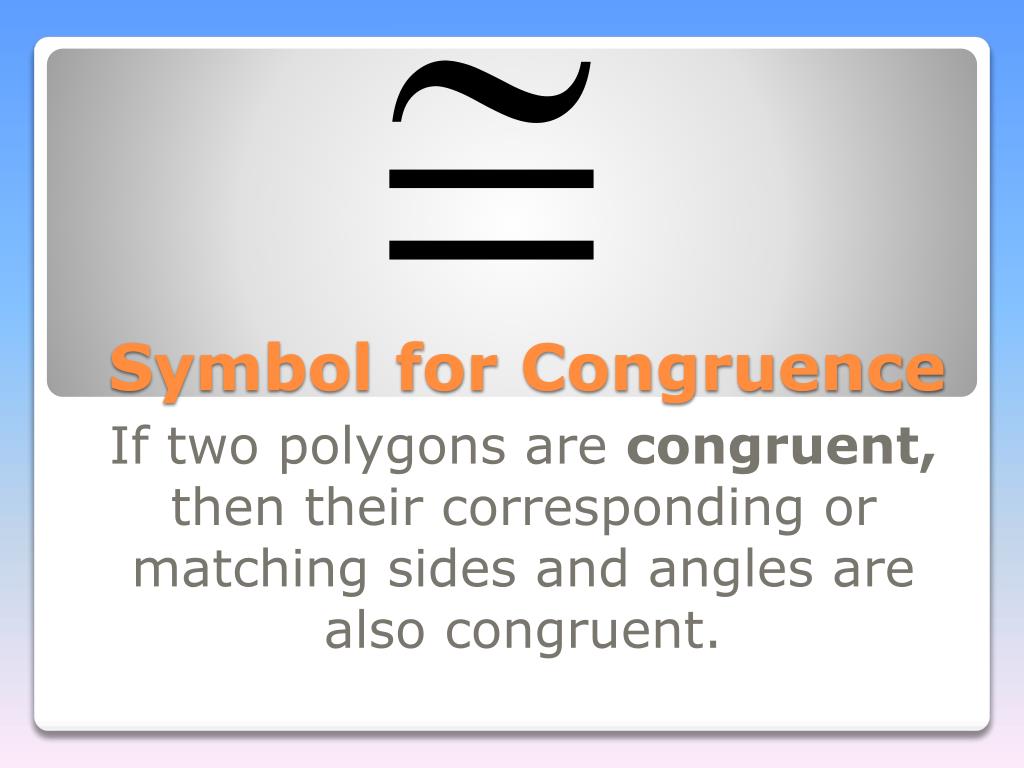
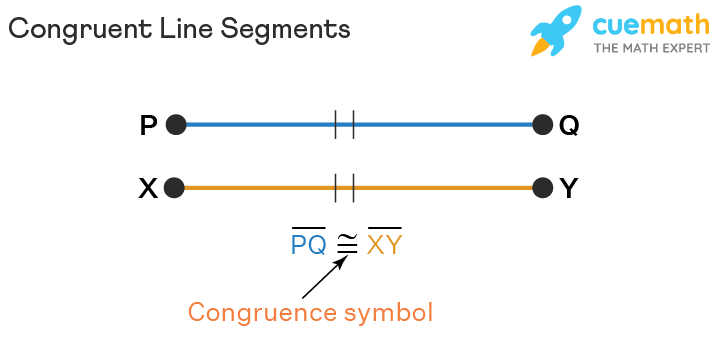
Congruence is one of those foundational ideas that shows up everywhere once you actually pay attention to it. The symbol used is , and it means two objects are essentially the same in some specific sense. In number theory you will see it most often as a b (mod n), which means a b is divisible by n. That is the whole thing, really, once you strip away the textbook presentation. I ran into a problem a while back where I was working with polynomial rings modulo some composite modulus, and I had to verify whether two large polynomials were congruent without expanding everything out. The naive approach would have been to compute the difference and then factor it, which for degree-12 polynomials with coefficients in the thousands was not practical. What actually worked was reducing both polynomials modulo the prime factors of n separately, then checking agreement on each factor. CRT handles the rest. It saved me from doing a bunch of unnecessary computation.
Common Pitfalls When Working With Congruent Sign In Math
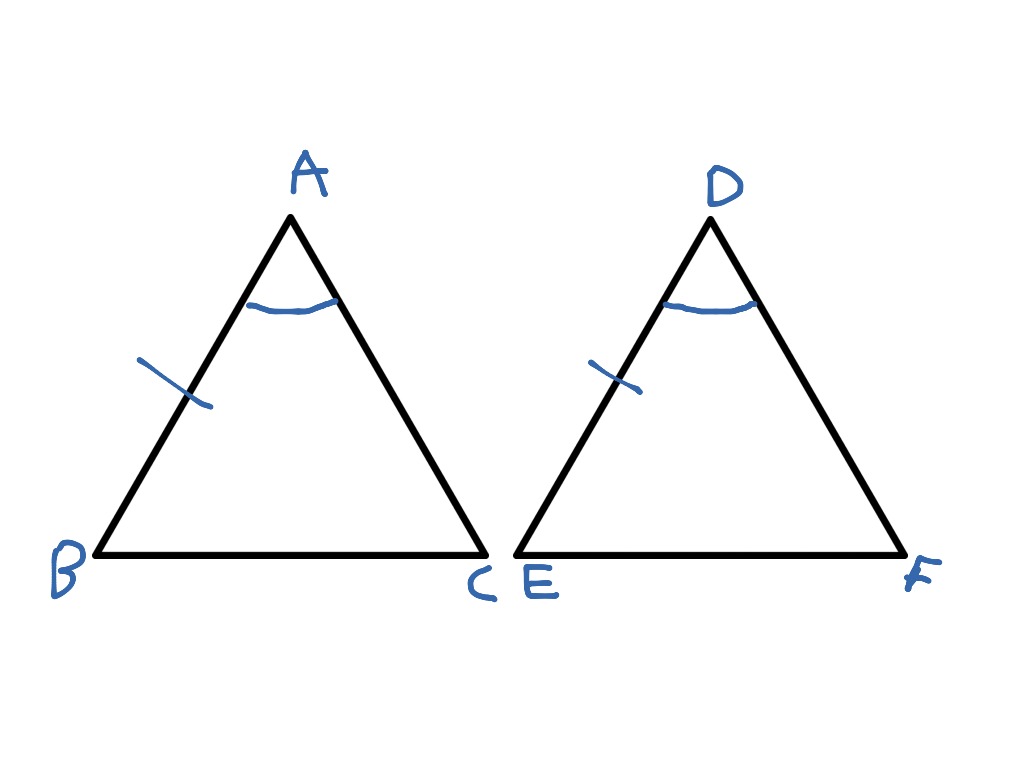
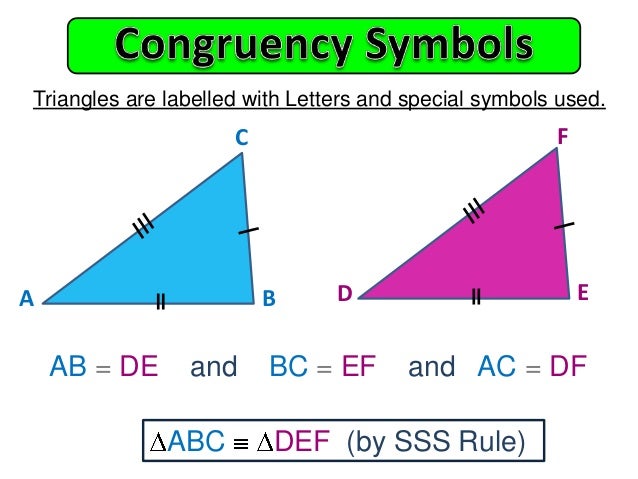
Beginners tend to treat the symbol as if it were just = with extra steps. The biggest mistake is assuming you can cancel terms the same way you do with ordinary equations. If a b (mod n) and you want to divide both sides by some integer d, you can only do that if gcd(d, n) = 1. If the gcd is not 1, the modulus effectively shrinks and you lose information. I have seen people miss this and then wonder why their solutions are incomplete. Another issue is the scope of what "congruent" means depending on context. In geometry it means same shape and size. In number theory it means same residue class. In abstract algebra it often means equivalent under some equivalence relation defined by an ideal. The symbol looks identical but the meaning shifts. Pay attention to what structure you are working in before you start manipulating things.
How to Use Congruence Relations in Practice
When you are solving a problem that involves congruences, the first thing to do is figure out what modulus makes sense for your situation. Sometimes the modulus is given explicitly. Other times it emerges from the problem structure. For example, if you are working with periods or cycles, the modulus is often related to the order of the elements involved. The Chinese Remainder Theorem is probably the most useful tool here. If you can decompose your problem into smaller moduli that are pairwise coprime, you solve each piece separately and then recombine. This is not just a theoretical convenience. In computational number theory it cuts runtime significantly because operations on smaller moduli are faster and avoid coefficient explosion. When I was working on a project involving discrete logarithms in a group of unknown order, I used congruence relations to reduce the search space from something exponential to something polynomial in the relevant parameters. The key insight was that the answer had to satisfy a system of congruences, and each one eliminated a chunk of possibilities. Without that reduction I would have been stuck doing brute force searches that were completely infeasible.
Get the Full Details
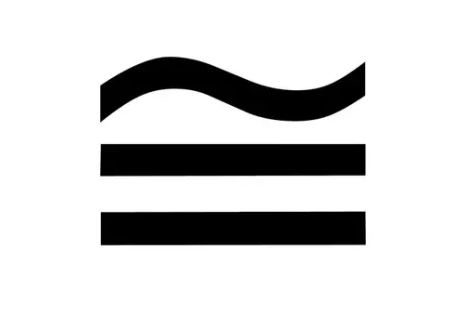
There are cases where congruence is not enough and you need to move to something stronger. If you are dealing with approximate arithmetic or floating point work, modular congruence does not help because the whole framework assumes exact integers. In those situations you are better off using hash functions or checksums, or just working with exact arithmetic from the start even if it is slower. Congruence is powerful but it has clear boundaries.
Practical Example Walkthrough
Let me show a concrete case. Suppose you need to find x such that 7x 13 (mod 20). First check that gcd(7, 20) = 1, which it is, so an inverse exists. The inverse of 7 modulo 20 is 3 because 7 × 3 = 21 1 (mod 20). Multiply both sides by 3 and you get x 39 19 (mod 20). Done. The solution set is all integers congruent to 19 modulo 20. Now try the same with 6x 13 (mod 20). Here gcd(6, 20) = 2, which does not divide 13, so there is no solution. This is the kind of thing that trips people up. Always check the gcd before trying to invert anything. It takes two seconds and prevents a lot of wasted effort. If you want to dig deeper into this, the standard references are still the number theory textbooks, but the online resources around computational number theory tend to cover the practical side better. Look for material on modular arithmetic implementations and CRT-based algorithms if you are actually building something that uses these ideas.