What Actually Happens When You Review a Contract Without a System
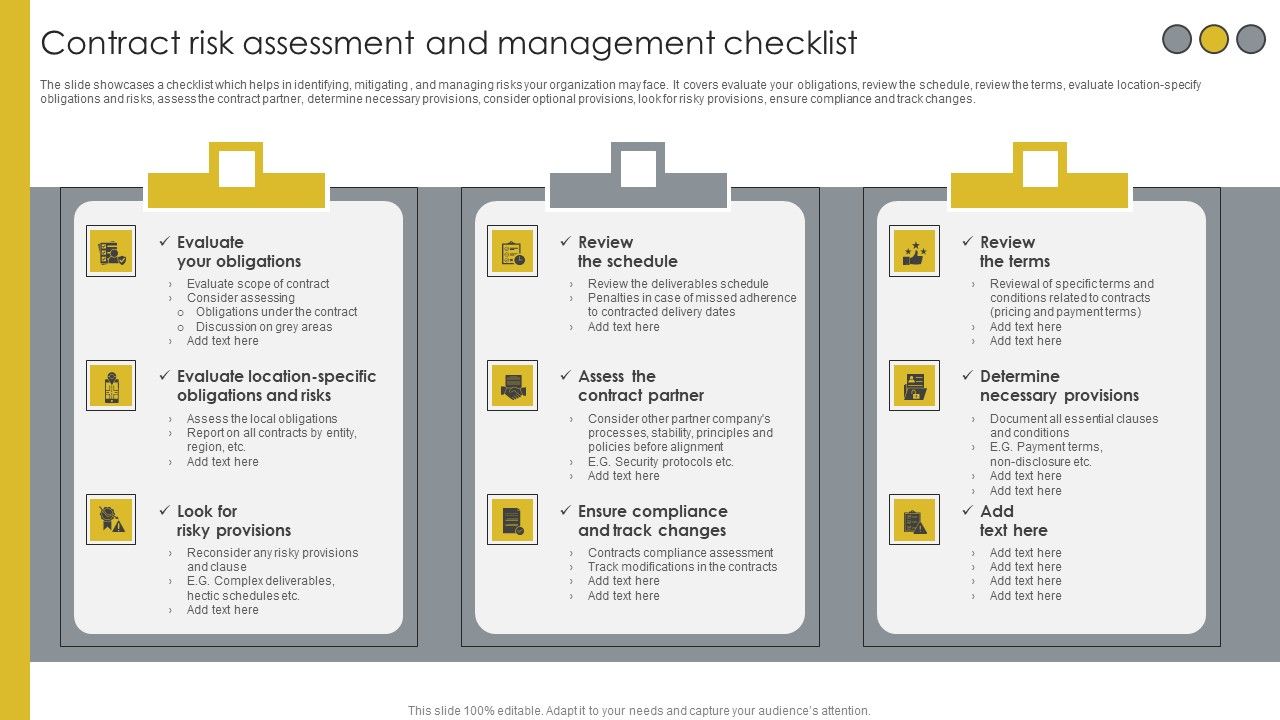
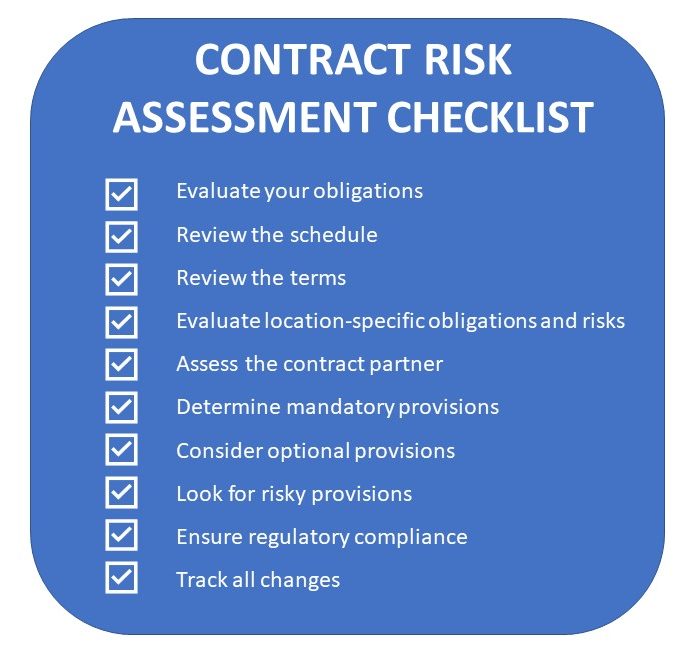
You pull up a vendor agreement, you scan through the liability clause, the termination terms, the indemnification language, and somehow two weeks later you realize you missed the auto-renewal provision that locks you in for another year. This is the default experience for most legal teams and procurement departments that haven't built a structured review process. A Contract Risk Assessment Checklist is the tool that stops this from happening, but honestly, the checklist itself is only as useful as the methodology behind it. I built ours from scratch about six years ago after a services contract cost us roughly forty thousand dollars in an unexpected renewal we hadn't caught, and I can tell you with no enthusiasm that the real value isn't in having a document with checkboxes. It's in having a living framework that forces you to confront questions you would otherwise skip over because they seem obvious or unimportant at the time. Most people start by copying a template from somewhere online and then wonder why their team ignores it. The problem is that generic templates cover every possible clause type without any weighting or prioritization, which means everything looks equally risky and nothing does. I recommend starting with your own contract history. Pull the last twenty agreements your organization signed and catalog every issue that caused problems afterward. The clauses that created disputes, delays, or financial exposure will tell you what actually matters in your context. That's how you build a checklist that reflects your real risk profile instead of someone else's hypothetical worst case. Structure the checklist around four core risk domains: financial, operational, legal, and strategic. Under financial, you're looking at payment terms, penalty structures, audit rights, and fee escalation mechanisms. Operational covers service level commitments, deliverable specifications, substitution rights, and continuity provisions. Legal encompasses indemnification, limitation of liability, confidentiality, IP ownership, and dispute resolution mechanisms. Strategic involves term length, renewal conditions, change-of-control provisions, and exclusivity restrictions. Each item should have a clear pass, flag, or escalate designation so reviewers aren't left guessing about what constitutes a problem.
I learned pretty quickly that requiring every single field to be filled out for every contract was a terrible idea. You'll slow down routine renewals and get checkbox fatigue within three weeks. Instead, I implemented a tiered approach based on contract value and duration. Agreements under fifty thousand dollars with terms under twelve months get a abbreviated review covering only the financial and legal domains. Mid-tier contracts between fifty thousand and five hundred thousand get the full four-domain checklist plus mandatory legal sign-off on any flagged items. Anything above five hundred thousand or with multi-year terms gets a full review with stakeholder consultation across departments. This cut our average review time from about three hours per contract down to roughly forty minutes for the majority of our volume while actually improving the quality of reviews on high-value deals because reviewers were spending their attention where it mattered.
Specific Clauses That Cause the Most Damage
If you only memorize five things from this, make them these. The limitation of liability clause is where most contracts fail. Vendors will push for caps at the contract value or even lower, and accepting that without challenge means your actual damages could far exceed your recovery. I've seen a client accept a liability cap equal to one month's fees on a three-year infrastructure management contract where the vendor's negligence caused a week of downtime that cost them well over half a million dollars. The cap limited their recovery to roughly six thousand. Always negotiate liability caps as a multiple of annual contract value, and never accept a cap that doesn't account for gross negligence or willful breach. The auto-renewal trap is the second most common source of unexpected exposure. Contracts with silent auto-renewal terms that require notice ninety or even one hundred eighty days before expiration are essentially landmines. Teams miss the window, the contract renews, and suddenly they're locked into unfavorable terms with no leverage to renegotiate. My workaround was to build a calendar integration into our contract management system that triggers alerts at ninety, sixty, and thirty days before any renewal date, with the ninety-day alert requiring a formal go or no-go decision documented in the system. This turned a process that relied on individual memory into something institutional. Change-of-control provisions deserve more attention than they get. A vendor selling their business to a competitor or an acquisition by a less favorable owner can completely alter your risk profile, yet these clauses are routinely buried in boilerplate. I once reviewed a contract where the change-of-control clause only covered the vendor changing hands, not the customer. Our purchasing department got acquired by a larger organization and the vendor used that clause to justify a forty percent price increase because they claimed the change in ownership altered their risk exposure. There was no defense against that argument because we hadn't included reciprocal change-of-control protections. Always make these provisions mutual unless you have a specific business reason not to.
Get the Full Details

Where the Checklist Breaks Down
A Contract Risk Assessment Checklist will not save you from bad faith negotiations, vague language that requires legal interpretation, or relationships where the other party has significantly more drafting power than you do. If you're dealing with a platform company that provides take-it-or-leave-it terms, checking off that their liability cap is below industry standard doesn't give you any ability to actually change it. In those situations, the checklist becomes a documentation tool rather than a negotiating lever, and that distinction matters. You still need it for your records and for post-signature reference, but you shouldn't confuse completeness of review with control over outcomes. The biggest structural weakness I've observed is that checklists tend to be static while contracts evolve. A risk item that was critical three years ago might be irrelevant now because the market shifted, new regulations came into effect, or your organization's risk tolerance changed. I've seen teams faithfully checking off items that haven't been a real concern since 2019 while missing new risks that emerged from regulatory changes in data privacy or cross-border data flow requirements. The checklist needs a scheduled review process, not just a creation event. We rebuilt ours annually in the first quarter, cross-referencing it against any contracts that had issues in the prior year and updating based on regulatory and market changes. This took about a day of work for our team and prevented at least two significant oversights per year. Another limitation is that checklists create a false sense of security when the person using it lacks domain expertise. A procurement specialist might check off the standard clauses correctly but miss the operational implication of a specific performance metric because they don't understand the underlying technology. I solved this by requiring that any contract involving specialized services or technology must include a technical stakeholder review section appended to the checklist, with their sign-off documented separately. This added about twenty minutes to those reviews but caught issues that a purely procedural checklist would have missed every time.
Practical Implementation Notes
Don't build the checklist in a Word document. This sounds obvious but it's surprisingly common, and the result is always the same: the document gets printed, annotated in pen, lost, and recreated from memory when the next contract comes around. A shared digital form with required fields, dropdown selections, and mandatory escalation paths for flagged items makes the process trackable and auditable. You also get data you can actually analyze, like average review times per contract type, frequency of specific risk flags, and which clauses trigger the most escalations. That data is useful for training, for negotiation strategy, and for demonstrating to leadership that the process is working. Training matters more than the checklist itself. I've seen organizations invest heavily in building elaborate review frameworks and then assign them to people who received one email explaining how to use them. The checklist is only as good as the person applying it. A half-hour walkthrough with real examples from your own contract history will produce better results than a twenty-page handbook nobody reads. Walk through three contracts, two that went smoothly and one that had problems, and show exactly which checklist items caught or should have caught the issues. Concrete examples beat abstract guidance every time. One thing worth mentioning about integration: if your organization uses a contract lifecycle management platform, building the checklist into that system rather than keeping it as a separate document dramatically increases adoption. People already log into the platform for approvals and version tracking, so embedding the risk assessment there eliminates the friction of switching between tools. We migrated from a standalone spreadsheet system to our CLM platform and saw completion rates jump from about sixty percent to roughly ninety-five percent within three months. The checklist wasn't better. The distribution channel was just less annoying.
Contract Risk Assessment Checklist
The framework I described above can be adapted to virtually any organization, but the specific clause language and thresholds will depend on your industry, contract volume, and risk appetite. There's no universal standard that fits all situations, and anyone selling you a one-size-fits-all template is either selling you something generic or trying to offload work onto you. The most reliable approach is to start with your own contract history, identify the patterns of risk you've actually encountered, and build the checklist to address those patterns directly. You'll end up with something shorter and more targeted than most templates, and that's the point. A focused checklist that addresses your real problems will always outperform a comprehensive one that addresses everyone's hypothetical problems. If you want a starting point to adapt rather than build from zero, the basic structure I outlined with the four risk domains and the tiered review approach will serve most organizations. Fill in the specific clause language based on your prior contract issues, run it against your next three contracts, and adjust based on what the process revealed. Iteration beats perfection here because a good checklist that evolves with your experience is more valuable than a perfect one that becomes stale.