Building something usable instead of another spreadsheet nobody looks at
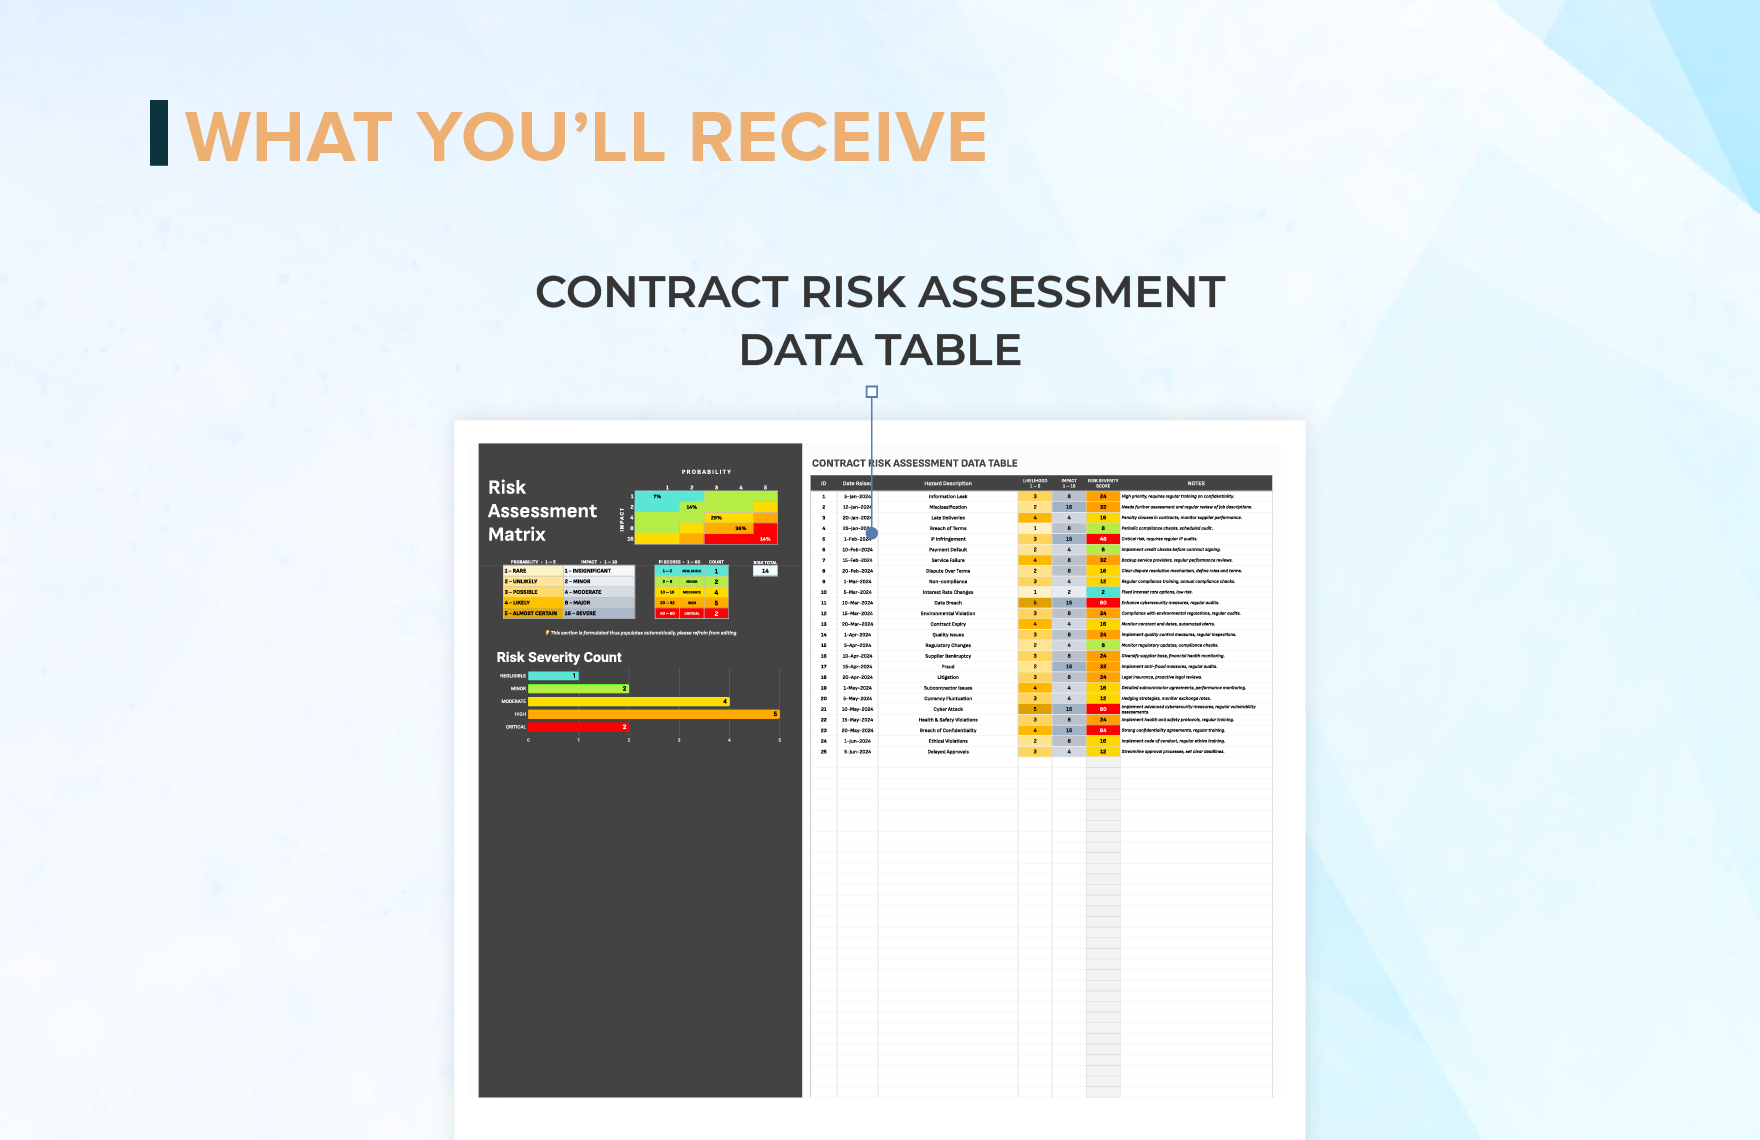
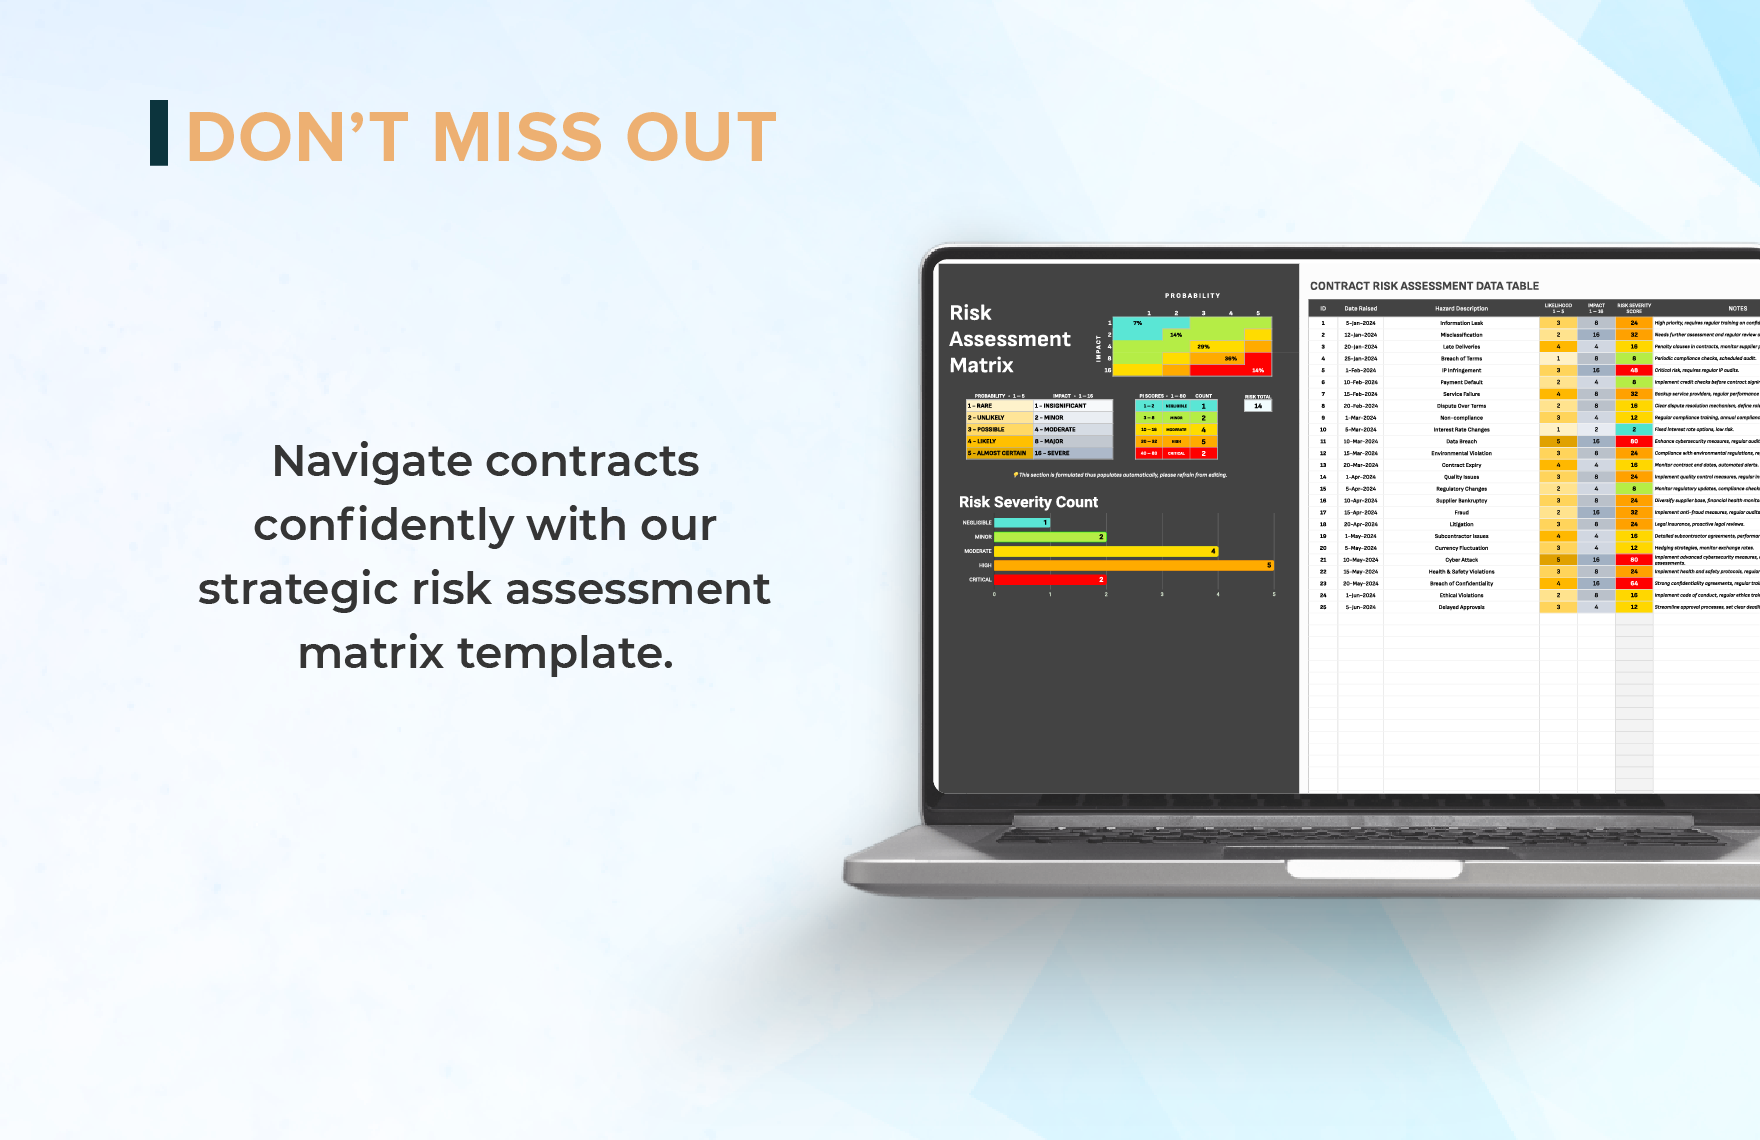
A Contract Risk Assessment Matrix is just a structured way to score the risks in a contract before you sign it. You list the risk factors, assign a likelihood and an impact rating, multiply them, and get a number that tells you which clauses need more attention. Sounds simple enough. The problem is most people build them wrong, then wonder why their legal team ignores the output. I spent three years working with contracts for procurement and vendor management. The first matrix I built was a 40-row Excel file with dropdowns, conditional formatting, and a pivot table that supposedly "ranked risk." It took four hours to complete per contract. Nobody used it after month two. What I ended up using instead was a much simpler version that fit on a single page and took about twelve minutes to fill out. The difference wasn't the quality of the analysis. It was friction.
How to Build a Contract Risk Assessment Matrix That People Actually Use
Start by identifying the risk categories that matter for your organization. For B2B vendor contracts, these are usually data privacy, intellectual property, liability caps, termination clauses, indemnification, compliance requirements, and force majeure. If you're doing construction contracts, add performance bonding and change order exposure. Don't copy a template from a consulting firm's website and use twenty categories. Pick the ones your team actually argues about during negotiation. Next, define your scoring scale. Most matrices use a three-point or five-point scale for both likelihood and impact. I prefer a five-point scale because three points creates too much clustering. When everything lands on a two or a three, you can't tell anything apart. Here's what I use: Likelihood: 1 = rare, 2 = unlikely, 3 = possible, 4 = likely, 5 = almost certain
Impact: 1 = negligible, 2 = minor, 3 = moderate, 4 = significant, 5 = critical The risk score is simply likelihood multiplied by impact. That gives you a range from 1 to 25. Anything above 15 gets flagged for senior review. Between 8 and 15 needs a negotiated mitigation. Below 8 is standard risk and you move on. This cutoff isn't sacred. Adjust it based on your organization's risk appetite. One thing most people miss: you need to weight the categories. Not every risk area is equally important. In my experience, liability and indemnification clauses typically account for 60 to 70 percent of real-world contract disputes. Data privacy is growing fast, especially with GDPR and state-level regulations. IP ownership matters more for software and consulting than for supply agreements. Assign a weight to each category and multiply the raw risk score by that weight. A simple weighting like 1.5x for high-priority areas and 0.8x for low-priority ones makes the output actually reflect where the real danger sits.
Get the Full Details
I ran into a specific edge case that broke my first few matrices. We had a software licensing agreement where the vendor pushed a clause that limited their liability to the amount paid in the previous twelve months. The matrix scored it as medium risk because the likelihood of a breach was low and the financial impact for a standard license looked manageable. But we were deploying this software across forty-five offices with fifty thousand users. The impact wasn't medium. It was catastrophic if there was a data loss event. The matrix didn't capture this because I hadn't built in an "aggregate exposure" multiplier for enterprise-wide deployments. I added a field after that called deployment scope multiplier, which scales the impact score by the number of affected locations and users. It added two minutes to the process and caught at least three deals that would have walked into serious problems. Here's how the final structure looks in practice: Risk Category | Likelihood (1-5) | Impact (1-5) | Weight | Adjusted Score
You fill this out during the contract review phase, before you send it back to the vendor with redlines. Some organizations do it after receiving the vendor's draft. Both work. The first approach is better because it tells you what you're willing to accept before you see their language. The second approach is more common because legal gets involved after the business side has already committed to the deal. Counters you should include for the major risk areas. I mean actual negotiating positions, not generic "we need better terms" notes. For liability, know your floor. If the vendor won't go above two times annual fees, decide now whether that's acceptable or whether you walk. For indemnification, understand whether you're asking for mutual or one-way. One-way indemnification from the vendor is standard for software and services. Mutual indemnification is common in partnerships and joint ventures. Data privacy clauses need to address sub-processing, breach notification timelines, and audit rights. Notification timelines under thirty days are a red flag. Most regulations require prompt notification, and thirty days gives the vendor time to discover the breach, contain it, and maybe cover it up. There's a common pitfall where people score every clause independently and then average the results. This smooths out the dangerous spots. A contract with one catastrophic risk and nine manageable ones should still flag as high risk. Use the maximum adjusted score, not the average, as your overall contract risk rating. That's how you avoid signing a deal with a single terrible clause and then wondering why something went wrong later.
The matrix doesn't replace legal review. It prioritizes it. A senior attorney can review a fully scored matrix in twenty minutes and focus on the flagged items. A blank contract takes an hour and forty-five minutes to do a competent review. If your legal team is buried and your contracts are going unsigned for weeks, the bottleneck is usually review time, not review quality. The matrix fixes that by making the dangerous parts obvious.
Where Contract Risk Assessment Matrix Falls Short
It doesn't handle relationship risk. Two companies can have a perfectly scored contract and still fail because the vendor lacks capacity, the key personnel leave, or the market shifts and the vendor decides your contract is no longer profitable for them. For that, you need separate vendor due diligence and continuous monitoring.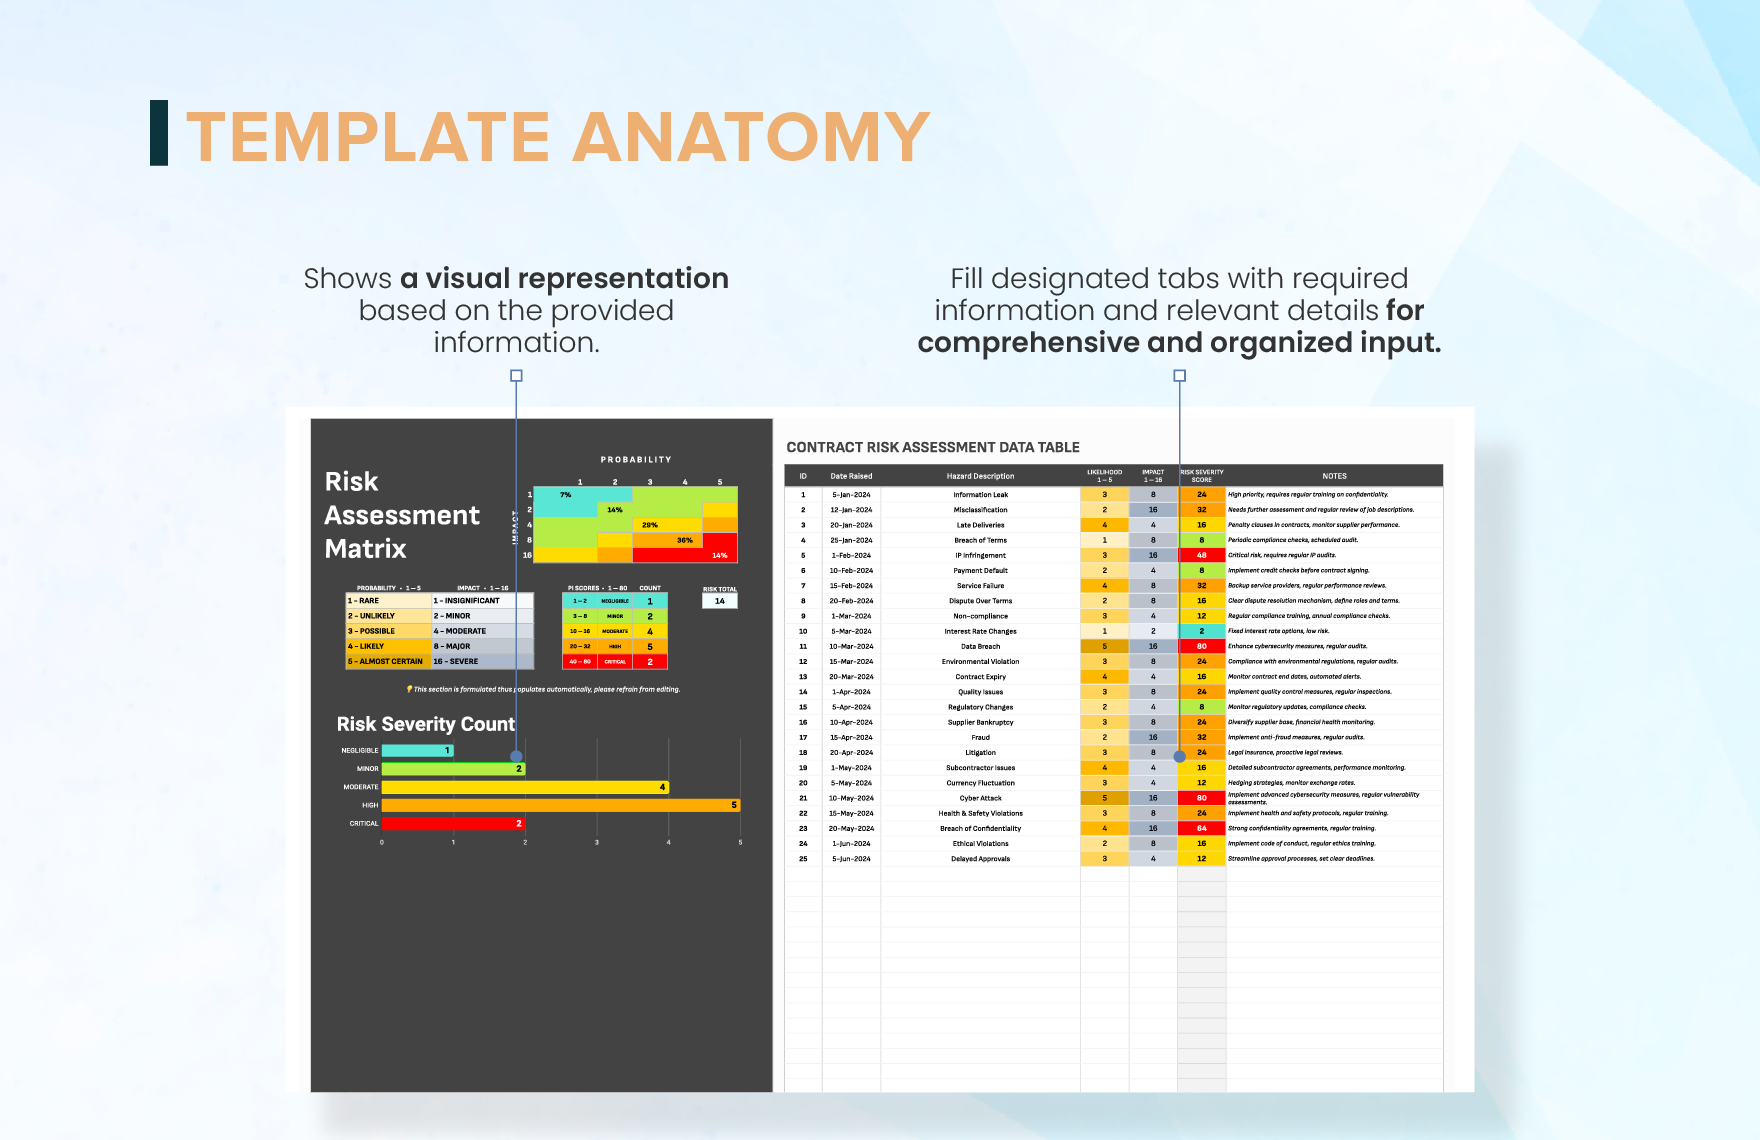
It also struggles with ambiguous clauses. Language like "reasonable efforts" or "best commercial efforts" doesn't score well on a numeric scale. You have to add a qualitative judgment field for these. I keep a notes column for every high-score item where I write the specific concern and the recommended negotiation position. That column is usually more valuable than the scores themselves. Some organizations try to automate this with contract management platforms. It works if your templates are standardized. If every contract is custom-drafted, automation adds complexity without reducing effort. A simple spreadsheet with clear instructions beats a half-configured tool every time. If you want a starting point, build yours from the categories I mentioned, use the five-point scale, apply weights based on your industry, and test it on five recent contracts. See which ones the matrix flags that surprised you. Adjust the weights and cutoffs accordingly. The version you ship on day one will be wrong. The version after three iterations will be useful.