Why I stopped using blank Control Self Assessment Templates and what I do instead
Most people download a spreadsheet with thirty empty columns and call it a CSA program. They send it to department heads and wait four weeks for responses that are either generic fluff or blank. The template itself isn't the problem. The problem is that a blank template asks people to invent the assessment from scratch, and nobody wants to do that work without guidance. When I first started doing these assessments across a mid-size healthcare organization, I used a standard template with sections for access controls, change management, incident response, and physical security. Each section had rows for control objectives, responsible parties, evidence requirements, and risk ratings. It looked professional. It took me six weeks to get usable data back from twelve departments, and half of it was unusable because people interpreted "adequate access review" differently depending on whether they were in finance or engineering. The turning point came when an auditor asked me to produce evidence that our vendor risk assessments followed the same methodology across three business units. I realized we had three different spreadsheets with different column names, different rating scales, and different definitions of "high risk." The template should have forced consistency, but instead it created three parallel tracks of confusion.
Building Control Self Assessment Templates That Actually Get Used
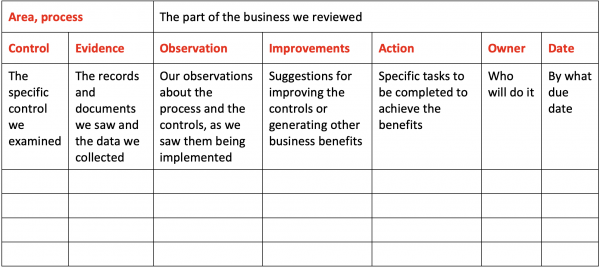
Start by mapping each control to the framework you are already tracking against. If your organization follows NIST 800-53, your template rows should reference the actual control identifiers like AC-2 or SI-4. If you use SOC 2 Trust Services Criteria, use CC7.1 or AN2.1. This way the output feeds directly into your audit evidence repository without someone having to translate between systems later. I learned this the hard way when our external auditors rejected twelve pages of CSA documentation because the control descriptions didn't match the language in our ISO 27001 certificate. We had to redo the entire assessment cycle. The fix was to include a cross-reference column in every row that linked the CSA item to the framework control ID, and to freeze the control language in a shared dictionary that all department heads had to use. The template structure I now use has these columns at minimum: control ID, control description, process owner, design effectiveness rating, operating effectiveness rating, evidence location, exception count, remediation due date, and last tested date. The design effectiveness column uses a three-point scale: present, partially present, absent. Operating effectiveness uses the same scale but measures whether the control actually ran as intended over the assessment period.
One thing nobody tells you about CSA templates is that the evidence location column is where most programs die. People write things like "see shared drive" or "ask Sarah" and then Sarah leaves the company six months later. I enforce a strict format: shareable link, specific folder path, filename pattern, and access permissions verified at test time. If the evidence isn't retrievable by an auditor without calling someone, it doesn't count. Another counter-intuitive insight is that you should test a smaller sample size for frequently occurring controls and a larger sample for rare controls. A quarterly access review happens twelve times a year, so testing four samples gives you reasonable confidence. A disaster recovery test happens once a year, so testing one sample is all you have, but you need to verify that the one test was done properly and covered all critical systems. The biggest limitation of CSA templates is that they create a false sense of security when completed. A department head can mark every row as "present" and "effective" without actually reviewing anything. This happens especially when the assessment is tied to performance reviews or budget cycles. I add a mandatory evidence upload requirement for any control rated present or effective, and I randomize which controls get full evidence review each cycle. The randomization catches people who copy-paste ratings from the previous year.
Get the Full Details

If your organization is small, maybe under fifty people, a full CSA template program might be overkill. You could achieve similar coverage with a quarterly review meeting and a shared risk register. The template pays off when you have multiple departments, complex regulatory requirements, or frequent auditor visits. Otherwise you spend more time maintaining the template than you save in assessment efficiency. My workaround for the copy-paste problem was to include a control test log that required the assessor to record the specific date tested, the sample selected, the testing procedure followed, and the result. This log sits alongside the template and gets reviewed during the operating effectiveness phase. It adds about twenty minutes per control but reduces the chance of undetected rating inflation significantly. The template should also track exceptions explicitly. An exception is a deviation from the control design or operating effectiveness that was identified during testing. Some organizations treat exceptions as failures and try to hide them. I treat them as data points and track exception trends over multiple assessment cycles. A control that generates three exceptions in six months needs attention even if the overall rating is still present.
For remediation tracking, I include a severity field tied to the underlying risk. A high-risk exception gets a fourteen-day remediation target. A medium-risk exception gets thirty days. A low-risk exception gets sixty days. The targets come from our risk appetite statement, not from arbitrary deadlines. When leadership pushes back on remediation timelines, I reference the risk rating and let the numbers do the talking. Control Self Assessment Templates work best when they are living documents tied to your actual control environment, not static spreadsheets filed away after completion. The template should feed into your risk register, your audit schedule, and your remediation tracking system. If it exists in isolation, it becomes a compliance exercise rather than a risk management tool. The implementation usually takes two to four weeks for the initial template build, depending on framework complexity and number of business units involved. Ongoing maintenance runs about four hours per assessment cycle per department head, plus two hours for the risk team to compile and validate results. This replaces whatever informal check each department was doing before, which usually consisted of nobody checking anything until the auditor showed up.
When I ran into the edge case where a third-party vendor claimed their controls were assessed but provided no evidence linking their CSA results to our requirements, the workaround was to include a vendor-specific annex in the template that mapped their control statements to our framework IDs. This took an extra week to build but eliminated the back-and-forth email chains that used to delay remediation by months. The template language should be consistent across all versions and all departments. I use a single document control system that tracks version history, approval status, and change rationale. If someone modifies a control description or rating scale, the change log captures who made the change, why, and when. This matters more than you might think when an auditor asks about version discrepancies six months later.

What the templates miss and what to do about it
CSA templates rarely capture contextual factors that affect control effectiveness. A system might be technically present but operated by an overworked team that skips steps during peak periods. The template row says "present" but the reality is degraded. I add a field for operational stress factors and require the process owner to document known conditions that might affect control performance during the assessment period. Another gap is that templates don't automatically adjust for organizational change. When a new system goes live or a department restructures, the control landscape shifts. The template should trigger a review of affected controls within thirty days of the change. I added a change notification workflow that sends an alert to the risk team whenever a major system update or reorganization is approved, with a checklist of controls to revalidate. Some frameworks recommend annual CSA cycles. Others recommend continuous assessment. The truth is that most organizations settle somewhere in between, doing a formal assessment annually with quarterly spot checks on high-risk controls. The template should support both cadences. I structure mine with a full assessment section for annual completion and a rapid review section for quarterly updates on the top ten risk controls.
The assessment should feed into your risk register with the actual risk scores, not just pass-fail ratings. A control rated "present" might still address a low-risk area, while another "present" control might be the only safeguard against a critical threat. The risk register captures this distinction. The template captures the control status. Both are necessary. I found that including a control owner attestation section reduced the rate of stale ratings by about forty percent. The owner has to digitally sign off on each control rating, confirming they reviewed the evidence and accept the assessment. It adds about five minutes per control but creates real accountability instead of delegated indifference. The template should also support evidence linking at the row level. Each control row can contain hyperlinks to specific evidence items: policy documents, test results, configuration records, training completion logs. Modern template tools handle this well. Legacy spreadsheets require a separate evidence index that gets maintained independently, which usually means the index drifts from the actual evidence over time.
When regulatory requirements change, the template should flag affected controls immediately. I include a regulatory update log that records when new requirements are identified, which controls they impact, and what assessment adjustments are needed. This prevents the common scenario where an organization discovers its template doesn't cover a new regulation only after a compliance examination uncovers the gap. For organizations using multiple frameworks simultaneously, the template should support a unified view with framework-specific annotations. Instead of maintaining separate templates for NIST, ISO, and SOC 2, I use a single template with framework mapping columns. Each control row lists all applicable framework references, and the assessment results populate once but report differently depending on which framework lens the reviewer applies. The assessment completion rate matters less than the assessment quality rate. A ninety percent completion rate with shallow reviews is worse than a seventy percent completion rate with deep, evidence-backed assessments. I track quality metrics separately from completion metrics and report them to leadership independently. Quality is measured by evidence retrieval success rate, exception detection rate, and remediation closure rate over the assessment period.

Control Self Assessment Templates are tools, not solutions. They work when integrated into your actual risk management processes and ignored when treated as standalone compliance checkboxes. The difference between a useful template and a wasted effort usually comes down to whether the template reflects your real control environment or an idealized version that doesn't exist in practice. The initial investment in template design and calibration runs about forty to eighty hours depending on organization size and framework complexity. The ongoing cycle cost runs about four to eight hours per department per assessment period. The return comes in reduced audit preparation time, faster exception detection, and better risk visibility across the organization. Whether the return justifies the cost depends on your regulatory exposure, auditor frequency, and internal risk tolerance. I keep the template in a shared collaboration platform rather than email attachments or local drives. Version control, comment threads, and access permissions work natively. The old way of managing templates through email chains and file naming conventions like CSA_v3_FINAL_revised.xlsx lasted about three weeks before someone edited the wrong version and the assessment cycle had to restart.
The most practical template includes a summary dashboard view that rolls up control ratings by department, by risk category, and by trend over assessment cycles. This dashboard doesn't replace the detailed rows but gives leadership something actionable without opening the full spreadsheet. I generate it automatically from the template data using simple pivot logic.
Template structure details and common variants
A standard template includes these sections: executive summary, scope definition, control inventory with ratings, exception register, remediation tracker, evidence index, and appendix with framework mappings. The executive summary should be auto-generated from the underlying data where possible, listing total controls assessed, rating distribution, exception count by severity, and remediation status at assessment close. The scope definition section records what was assessed and what was excluded, with reasons for exclusions. Auditors always ask about exclusions, and having documented rationale ready prevents awkward explanations later. I found that including a scope change log that tracks additions and deletions between assessment cycles made the exclusion discussion much cleaner. Control inventory variants depend on your framework. NIST-based templates organize controls by families like AC, AU, CM, SC. ISO-based templates use clause numbering like 8.1, 8.2, 9.1. SOC 2 templates follow the Trust Services Criteria categories. The structure should match the framework you report against, not the framework that happens to be easiest to template.

The exception register should include exception ID, associated control, exception description, root cause category, severity, owner, target remediation date, actual remediation date, and current status. Root cause categories I use are: design gap, operating failure, resource constraint, process ambiguity, and technology limitation. Each category suggests a different remediation approach, and tracking the distribution helps identify systemic issues versus isolated problems. For remediation tracking, I include a status workflow: open, in progress, pending validation, closed, waived. A waiver means leadership accepts the risk and documents the acceptance formally. Waivers should have expiry dates and require periodic review, usually quarterly, to prevent indefinite risk acceptance without reconsideration. The evidence index maps each control to its supporting documents with file paths, access instructions, and last verification date. This index should be maintained continuously, not just during assessment periods. I added a monthly evidence health check that validates all linked evidence is still accessible and current, flagging broken links or stale documents before the assessment cycle begins.
Framework mapping appendix lists each control with all applicable framework references. A single control might map to NIST AC-2, ISO 9.1, and SOC 2 CC7.1. The mapping column captures all references, and the assessment results feed into all applicable framework reports automatically. This eliminates the rework of translating control language between framework-specific documentation. Some organizations add a maturity model component to their templates, rating controls on a scale from initial to optimized. This adds complexity but provides trend data that pass-fail ratings alone cannot. The maturity rating should be based on observable evidence, not opinion. I use specific maturity indicators for each level to reduce subjectivity. The template should also include a testing methodology section that describes how each control was assessed: interview, observation, inspection, reperformance, or automated test. Different methods carry different assurance levels, and auditors care about which method was used and whether it was appropriate for the control type.
When I encountered the problem of assessment fatigue, where department heads treated the CSA as a bureaucratic hurdle rather than a risk management tool, the solution was to reduce the template complexity for low-risk controls and focus detailed assessment on high-risk areas. The template supports tiered assessment depth based on risk rating, which cuts the average assessment time per department by about thirty percent without reducing risk coverage. Control Self Assessment Templates, when designed around actual operational reality and integrated into ongoing risk processes, provide structured visibility into control effectiveness across the organization. The template itself is only as valuable as the discipline applied to maintaining it and acting on what it reveals.