Building a Practical Risk Assessment Template
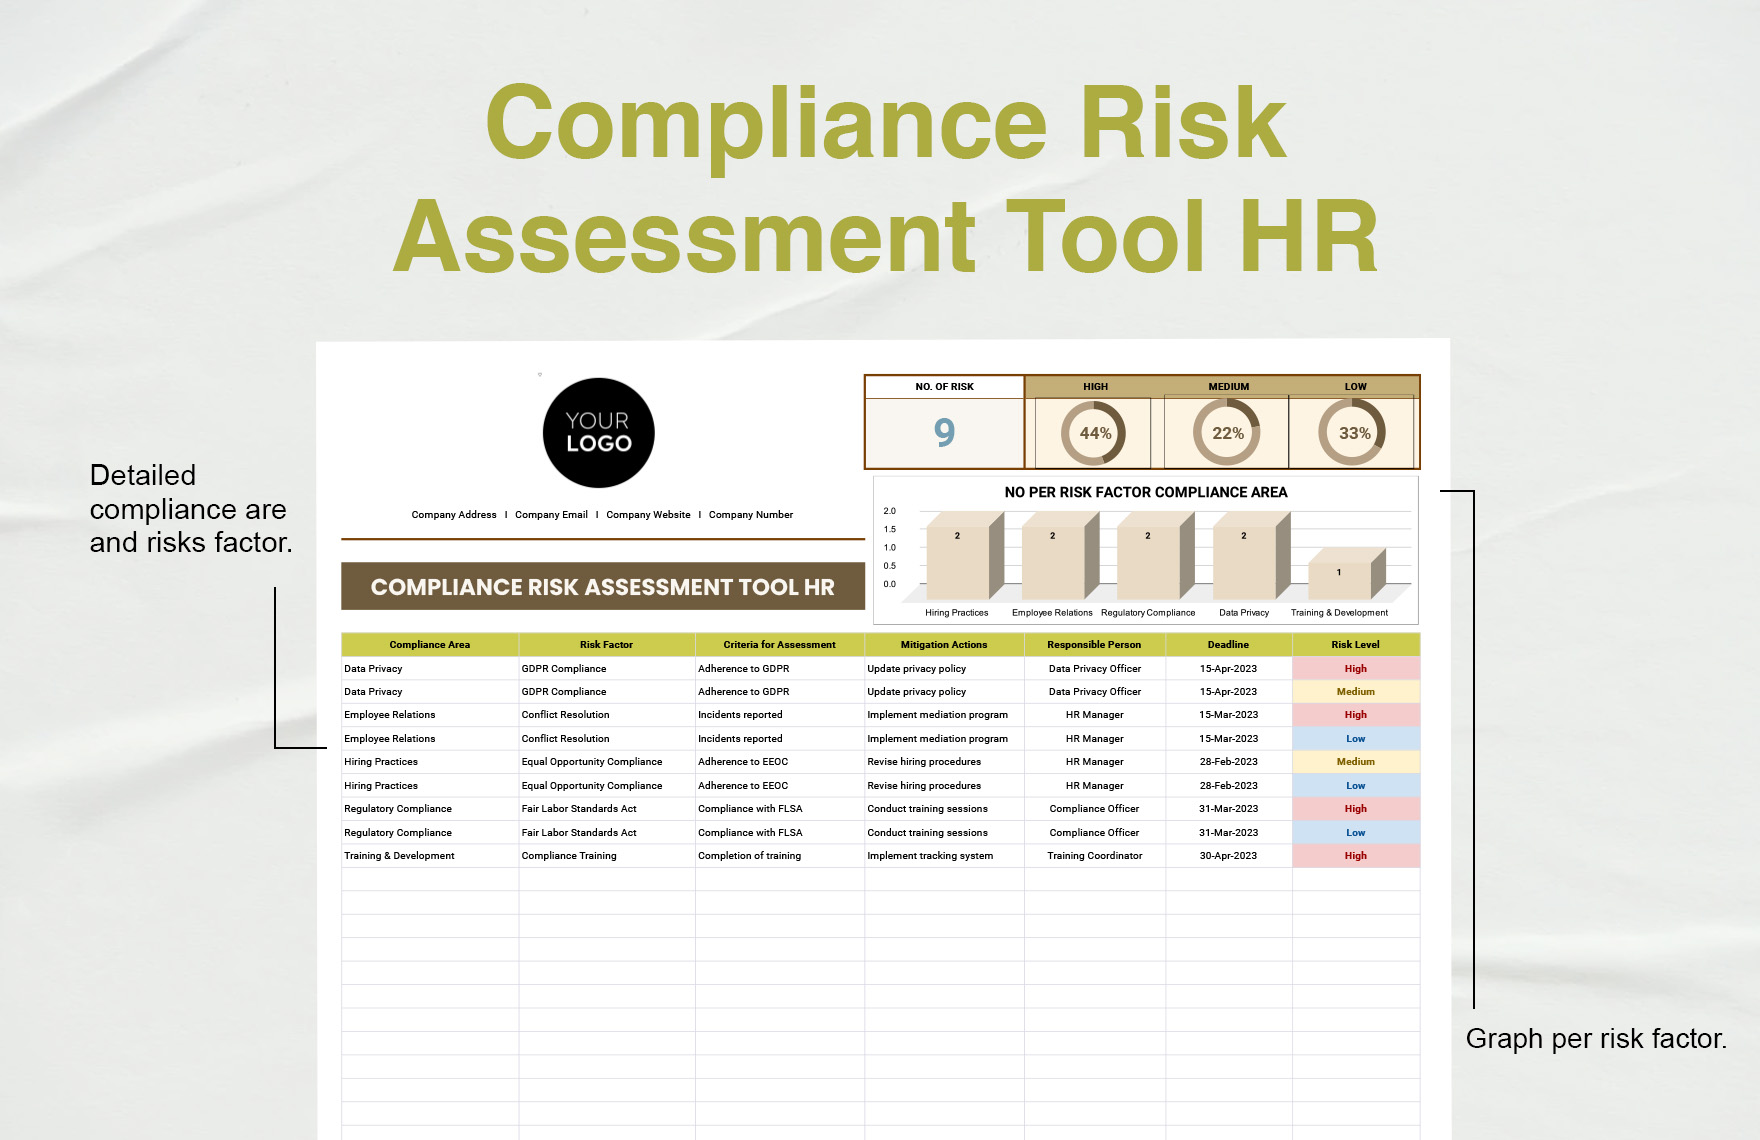
Most compliance teams I talk to end up with a template that looks impressive on paper and falls apart the moment you try to use it. The problem is usually that people build for auditors instead of for the actual work. Let me walk through what works and what does not. At its core, a risk assessment template is a structured document that forces you to identify compliance obligations, evaluate the likelihood and impact of non-compliance, and document mitigating controls. That sounds simple until you actually sit down to fill one out for a company operating across four jurisdictions with overlapping regulatory requirements. The fields I always include are: obligation source, risk statement, likelihood rating, impact rating, inherent risk score, control description, control owner, residual risk after controls, and a date for the next review. The likelihood and impact scales need to be explicitly defined right there in the document. If your template says "high" without saying what high means in concrete terms, every person who fills it out will interpret it differently and you will never get comparable results across departments.
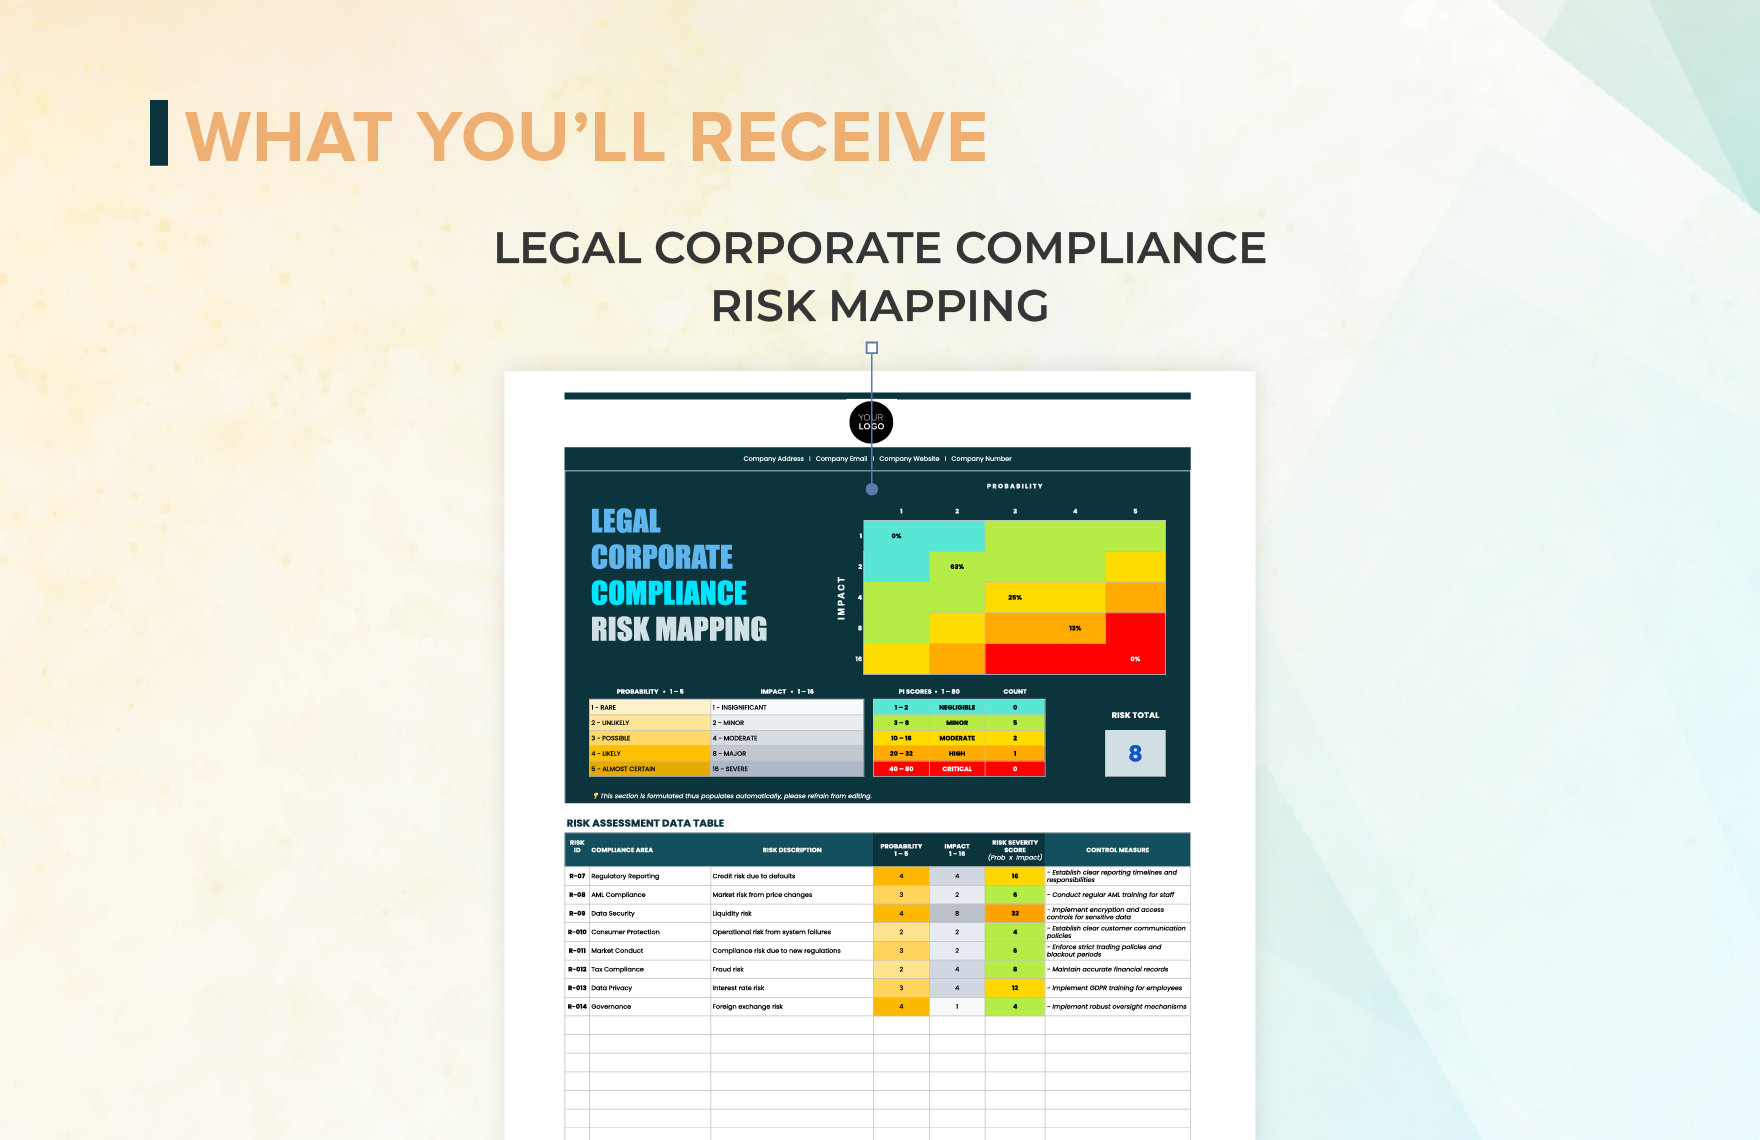
I use a five-point scale for both likelihood and impact, and I attach a one-line definition to each point. For impact, a 5 means regulatory sanction exceeding fifty thousand dollars or material reputational harm. A 1 means a minor procedural deviation with no measurable consequence. Likelihood follows the same logic: a 5 is something that has happened before in our environment and happens at least annually. A 1 is theoretically possible but has no occurrence history and requires multiple simultaneous failures. The calculation itself is straightforward multiplication. Inherent risk equals likelihood times impact, giving you a range from one to twenty-five. Then you subtract the effectiveness score of your existing controls to arrive at residual risk. Control effectiveness runs on its own scale: four means the control is fully designed and operating as intended. One means the control exists only on paper or has failed in recent testing. Here is where most templates break down in practice. The control effectiveness rating is almost always subjective unless you tie it to evidence. I require the control owner to reference a specific document or log entry that proves the control actually operates. A policy PDF is not sufficient evidence. A sign-off sheet from quarterly training is also not enough on its own. I want to see the actual monitoring output: access review logs, exception reports, reconciliation outputs, the things you can point to on a Tuesday morning when someone asks why a control exists.
I ran into a specific problem last year with a client trying to assess anti-bribery and corruption risk across their Southeast Asian operations. The template showed low residual risk because the controls were well documented. But when I dug into the evidence, the expense report reviews were being conducted by the same people whose expenses were under review. The control had design intent but zero operating effectiveness. The template fields were correctly filled but the actual risk was severely understated because nobody questioned whether the control evidence was independent. The workaround was to add a control independence field. Every control must have an independent verification component. If the control owner and the verifier are the same role, the effectiveness score gets capped at two regardless of documentation quality. This single field prevented us from going home with a false sense of security on that engagement. It also revealed similar issues in three other business units during the same assessment cycle. Another thing people miss: the template needs a section for emerging risks that do not fit neatly into existing categories. Regulatory landscapes shift and your template should have room for that without forcing new risks into old boxes. I keep a separate emerging risk register linked to the main template. Things like new data privacy legislation pending in a jurisdiction you operate in, or recent enforcement actions against your industry that signal where regulators are heading. These get reviewed quarterly alongside the standard assessment cycle.
Get the Full Details
The template should also specify how often each risk category gets reassessed. Not everything needs an annual review. Payment processing risks change weekly. Workplace safety compliance changes monthly. Corporate governance and anti-fraud policies might be safe with an annual refresh. Stating the review cadence for each category in the template eliminates the guesswork and the tendency to treat every risk as equally urgent. There are honest limitations to this approach. A template cannot substitute for actual domain expertise. If the person filling it out has never worked in procurement, they will systematically underestimate third-party corruption risk. If they have never dealt with data privacy regulation, they will rate notification process controls as adequate when they are not. The template amplifies whatever bias the assessor brings to it. Another limitation is that risk assessments tend to become static documents once completed. People fill them out, submit them, and forget about them until the next audit cycle. The template only adds value if it is treated as a living document with assigned review dates and actual follow-through. I have seen more compliance programs waste time producing elaborate templates that collected dust than I care to count.
If your organization has fewer than fifty employees and operates in a single jurisdiction with straightforward regulatory requirements, a full risk assessment template may be overkill. A simpler checklist-based approach covering your top five regulatory obligations with basic likelihood and impact ratings will get you further. Save the detailed template for when you actually have the volume of obligations and the complexity of operations to justify it. The template file itself should live in a shared location with version control. I recommend using a spreadsheet format for the main assessment because it handles calculations automatically and makes it easy to sort, filter, and aggregate risk data across business units. The supporting narrative and control evidence references can live in linked documents or a separate column. Keep the template lightweight enough that updating it takes minutes, not hours. If filling it out feels like a major project, people will find ways to game it or delay it. The real measure of whether your Corporate Compliance Risk Assessment Template is working is whether it surfaces risks that would otherwise stay hidden. If every risk in your assessment is already known and already being addressed, the template is not doing its job. It should force you to confront uncertainties and gaps in your control environment that comfortable assumptions would otherwise keep buried.