What the CrowdStrike Falcon User Guide Actually Covers
The
CrowdStrike Falcon User Guide
is the official documentation portal for CrowdStrike's endpoint detection and response platform. It sits at docs.crowdstrike.com and covers everything from agent installation to hunting queries, policy configuration, and incident workflow. Most people go there when something breaks and they need the answer fast.
I've spent years configuring Falcon deployments across enterprise environments, and the guide is decent if you know where to look. It is not a tutorial series. It is reference documentation organized by module. If you want step-by-step walkthroughs for a particular workflow, you will often need to piece together sections from multiple pages.
The guide is split into functional areas: sensor management, policy and rules configuration, incident response workflows, threat intelligence integration, and reporting. Each section has its own hierarchy. The navigation can feel repetitive because CrowdStrike maintains separate docs for Falcon Go, Falcon Cloud Security, and Falcon Identity Protection even though they share infrastructure under the hood.
How I Actually Use It
When I need to configure something in Falcon, I do not browse the sidebar. I search directly within the docs for the specific component. For example, if I am setting up a new containment policy, I search for "containment policy configuration Falcon" rather than clicking through from the main overview page. The search index respects CrowdStrike's internal taxonomy and returns results much faster than manual navigation.
One thing the guide does not make clear enough is how agent versioning interacts with policy compatibility. I learned this the hard way during a deployment at a client site last year. We migrated from Falcon agent version 7.x to 8.x across approximately 4,000 endpoints. The migration itself was straightforward using the deploy tool, but the custom detection rules we had written for the older sensor started throwing false positives immediately after the switch.
The issue was that Falcon 8.x changed how it reports certain process creation events to the backend. The detection logic in our policies was looking for a specific event sequence that the newer sensor reported differently. I had to rewrite about 12 of our custom rules. The workaround was checking the migration guide's change log section, which lists the exact API differences between versions, and then cross-referencing each rule against the new event schema. It took me about three hours total, but without that document, I would have been guessing blind.
Common Pitfalls Beginners Miss
The first thing most people get wrong is assuming the Falcon console and the user guide describe the same version. The console you are logged into might be running a newer or older build than the latest published documentation. CrowdStrike rolls out feature updates on a continuous cycle, and the docs sometimes lag behind by a sprint or two. Always check the version number in the bottom right corner of your console and compare it against the date on the document you are reading.
Another subtle issue is how Falcon handles overlapping policies. The guide explains the policy precedence rules, but the practical behavior is confusing until you test it. If you have two policies that match the same process and they specify different actions, Falcon does not merge the actions. It applies the policy with the highest precedence score. I once had a containment rule and a remediation rule conflict on the same endpoint group, and the containment action never fired because the remediation policy had a higher score. The fix was adjusting the precedence values in the policy editor, not creating a new rule.
What the Guide Gets Wrong or Leaves Out
The Falcon User Guide does not cover network-level integration with third-party SIEM platforms in any depth. It references the API endpoints and gives basic field descriptions, but if you are building a custom integration with Splunk, Sentinel, or QRadar, you will spend more time in the API reference than in the main guide. The API docs are actually better maintained than the narrative sections, which is unusual but helpful.
There is also very little about performance impact tuning. You can configure how aggressively the sensor collects telemetry, but the guide treats this as an advanced topic with minimal explanation. In practice, sensor CPU and memory footprint varies significantly based on your logging level and the rules you enable. A fully enabled detection policy with real-time file reputation checks can add roughly 3 to 5 percent CPU overhead on average workloads. I have seen it spike higher on systems running database workloads because the sensor hooks into process creation and file access at a deeper level.
The guide also assumes you already understand basic endpoint security concepts. It does not explain what a containment policy actually does at the OS level. If you are new to EDR, you might enable containment on a production server cluster without realizing it blocks all network egress and ingress for that host. I have watched this happen more than once. The result is immediate service disruption, and the on-call engineer spends an hour trying to figure out why the application servers are unreachable.
Navigation Tips That Save Time
Use the breadcrumb trail at the top of each page. It shows you exactly where you are in the documentation hierarchy. Many articles link to related sections, but the breadcrumb is the fastest way to jump back to a parent topic without losing your place.
The search function supports operators like site: and filetype: in some cases. If you need the API reference specifically, appending /api/ to your search query filters results appropriately. The Falcon console itself also has a built-in help icon that sometimes links to older documentation pages. Ignore that and stick to the standalone docs portal. The console help is not always in sync with the main guide.
When to Look Elsewhere
If you are troubleshooting a specific error code, the Knowledge Base article is more useful than the user guide. CrowdStrike maintains a separate KB section with numbered articles that address common failure modes. The user guide explains how features work. The KB explains what happens when they do not.
For deployment planning and sizing guidance, the CrowdStrike documentation center has architecture and best practices sections that are separate from the user guide. These cover agent deployment strategies, bandwidth requirements, and storage planning. They are not part of the Falcon User Guide proper, but they are essential for any production rollout. I always review these before handing a deployment to an engineer because the sizing numbers in the guide are conservative and assume typical enterprise workloads, not high-throughput server environments.
The guide is reliable reference material once you understand its structure and its gaps. It will not teach you from scratch, but it will give you the specifics you need when you are in the middle of a configuration task or trying to decode an unexpected behavior in your Falcon console.
Gallery Crowdstrike Falcon User Guide
Crowdstrike Falcon Intel Extension For Qradar: Installation and User Guide | PDF | Mobile App ...
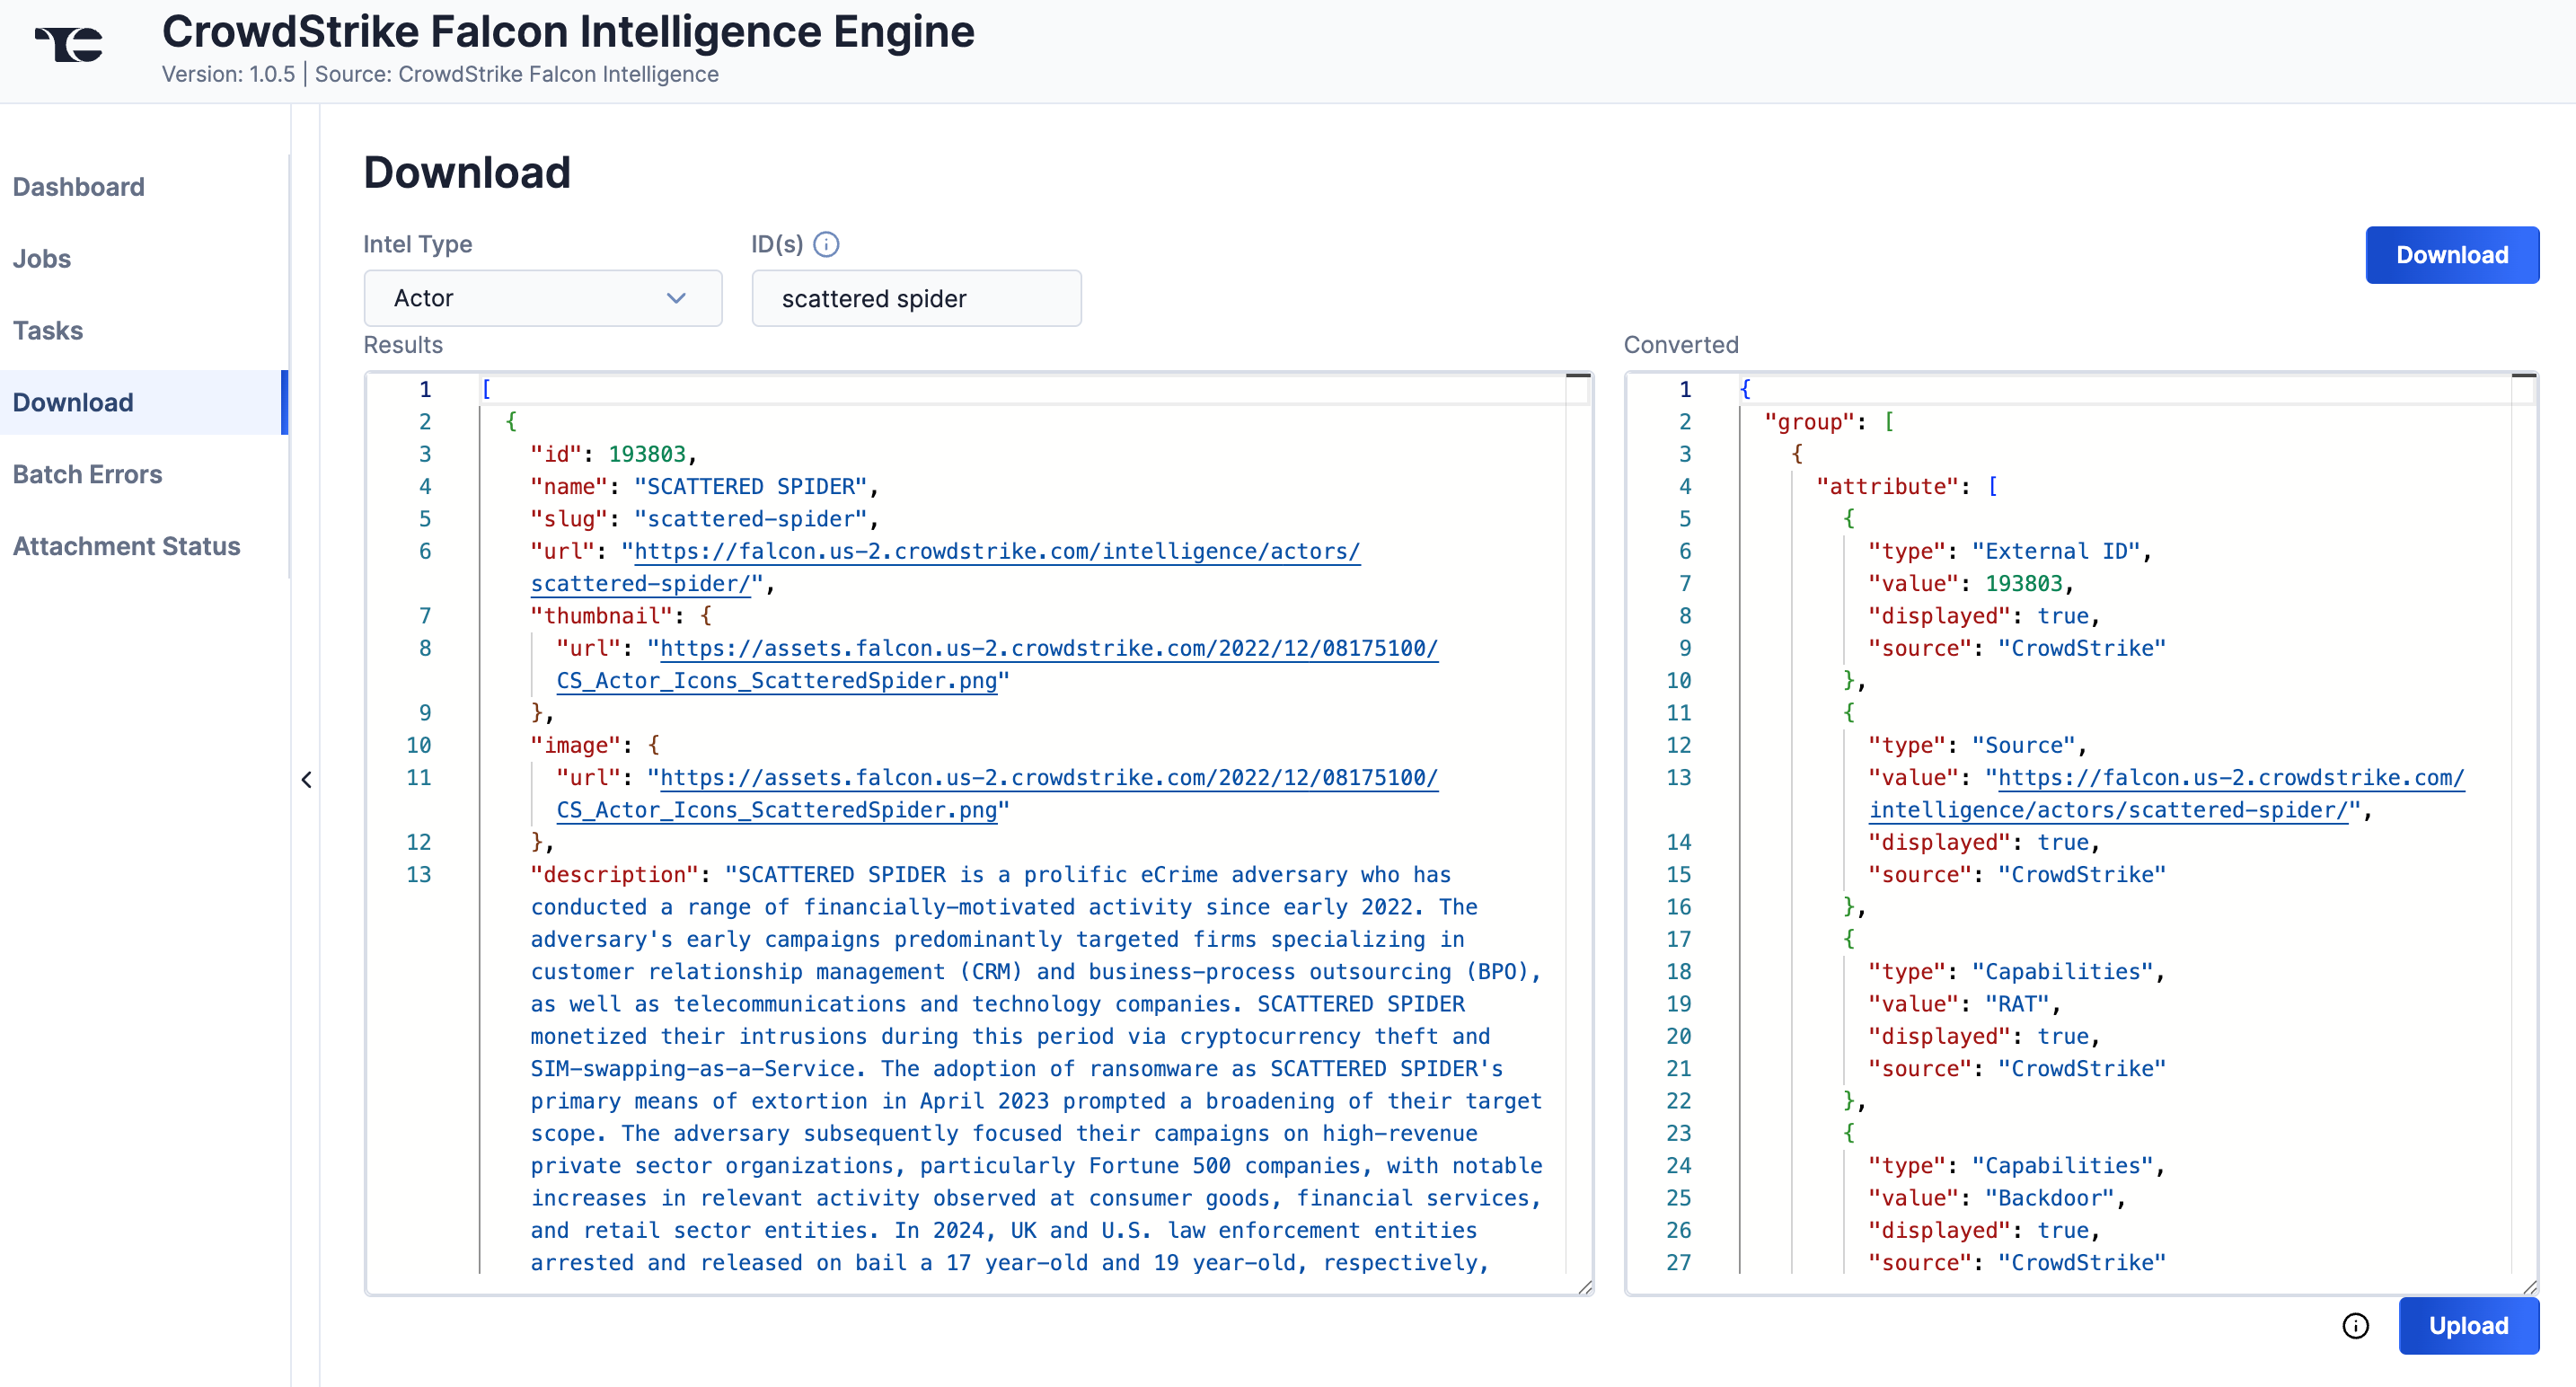
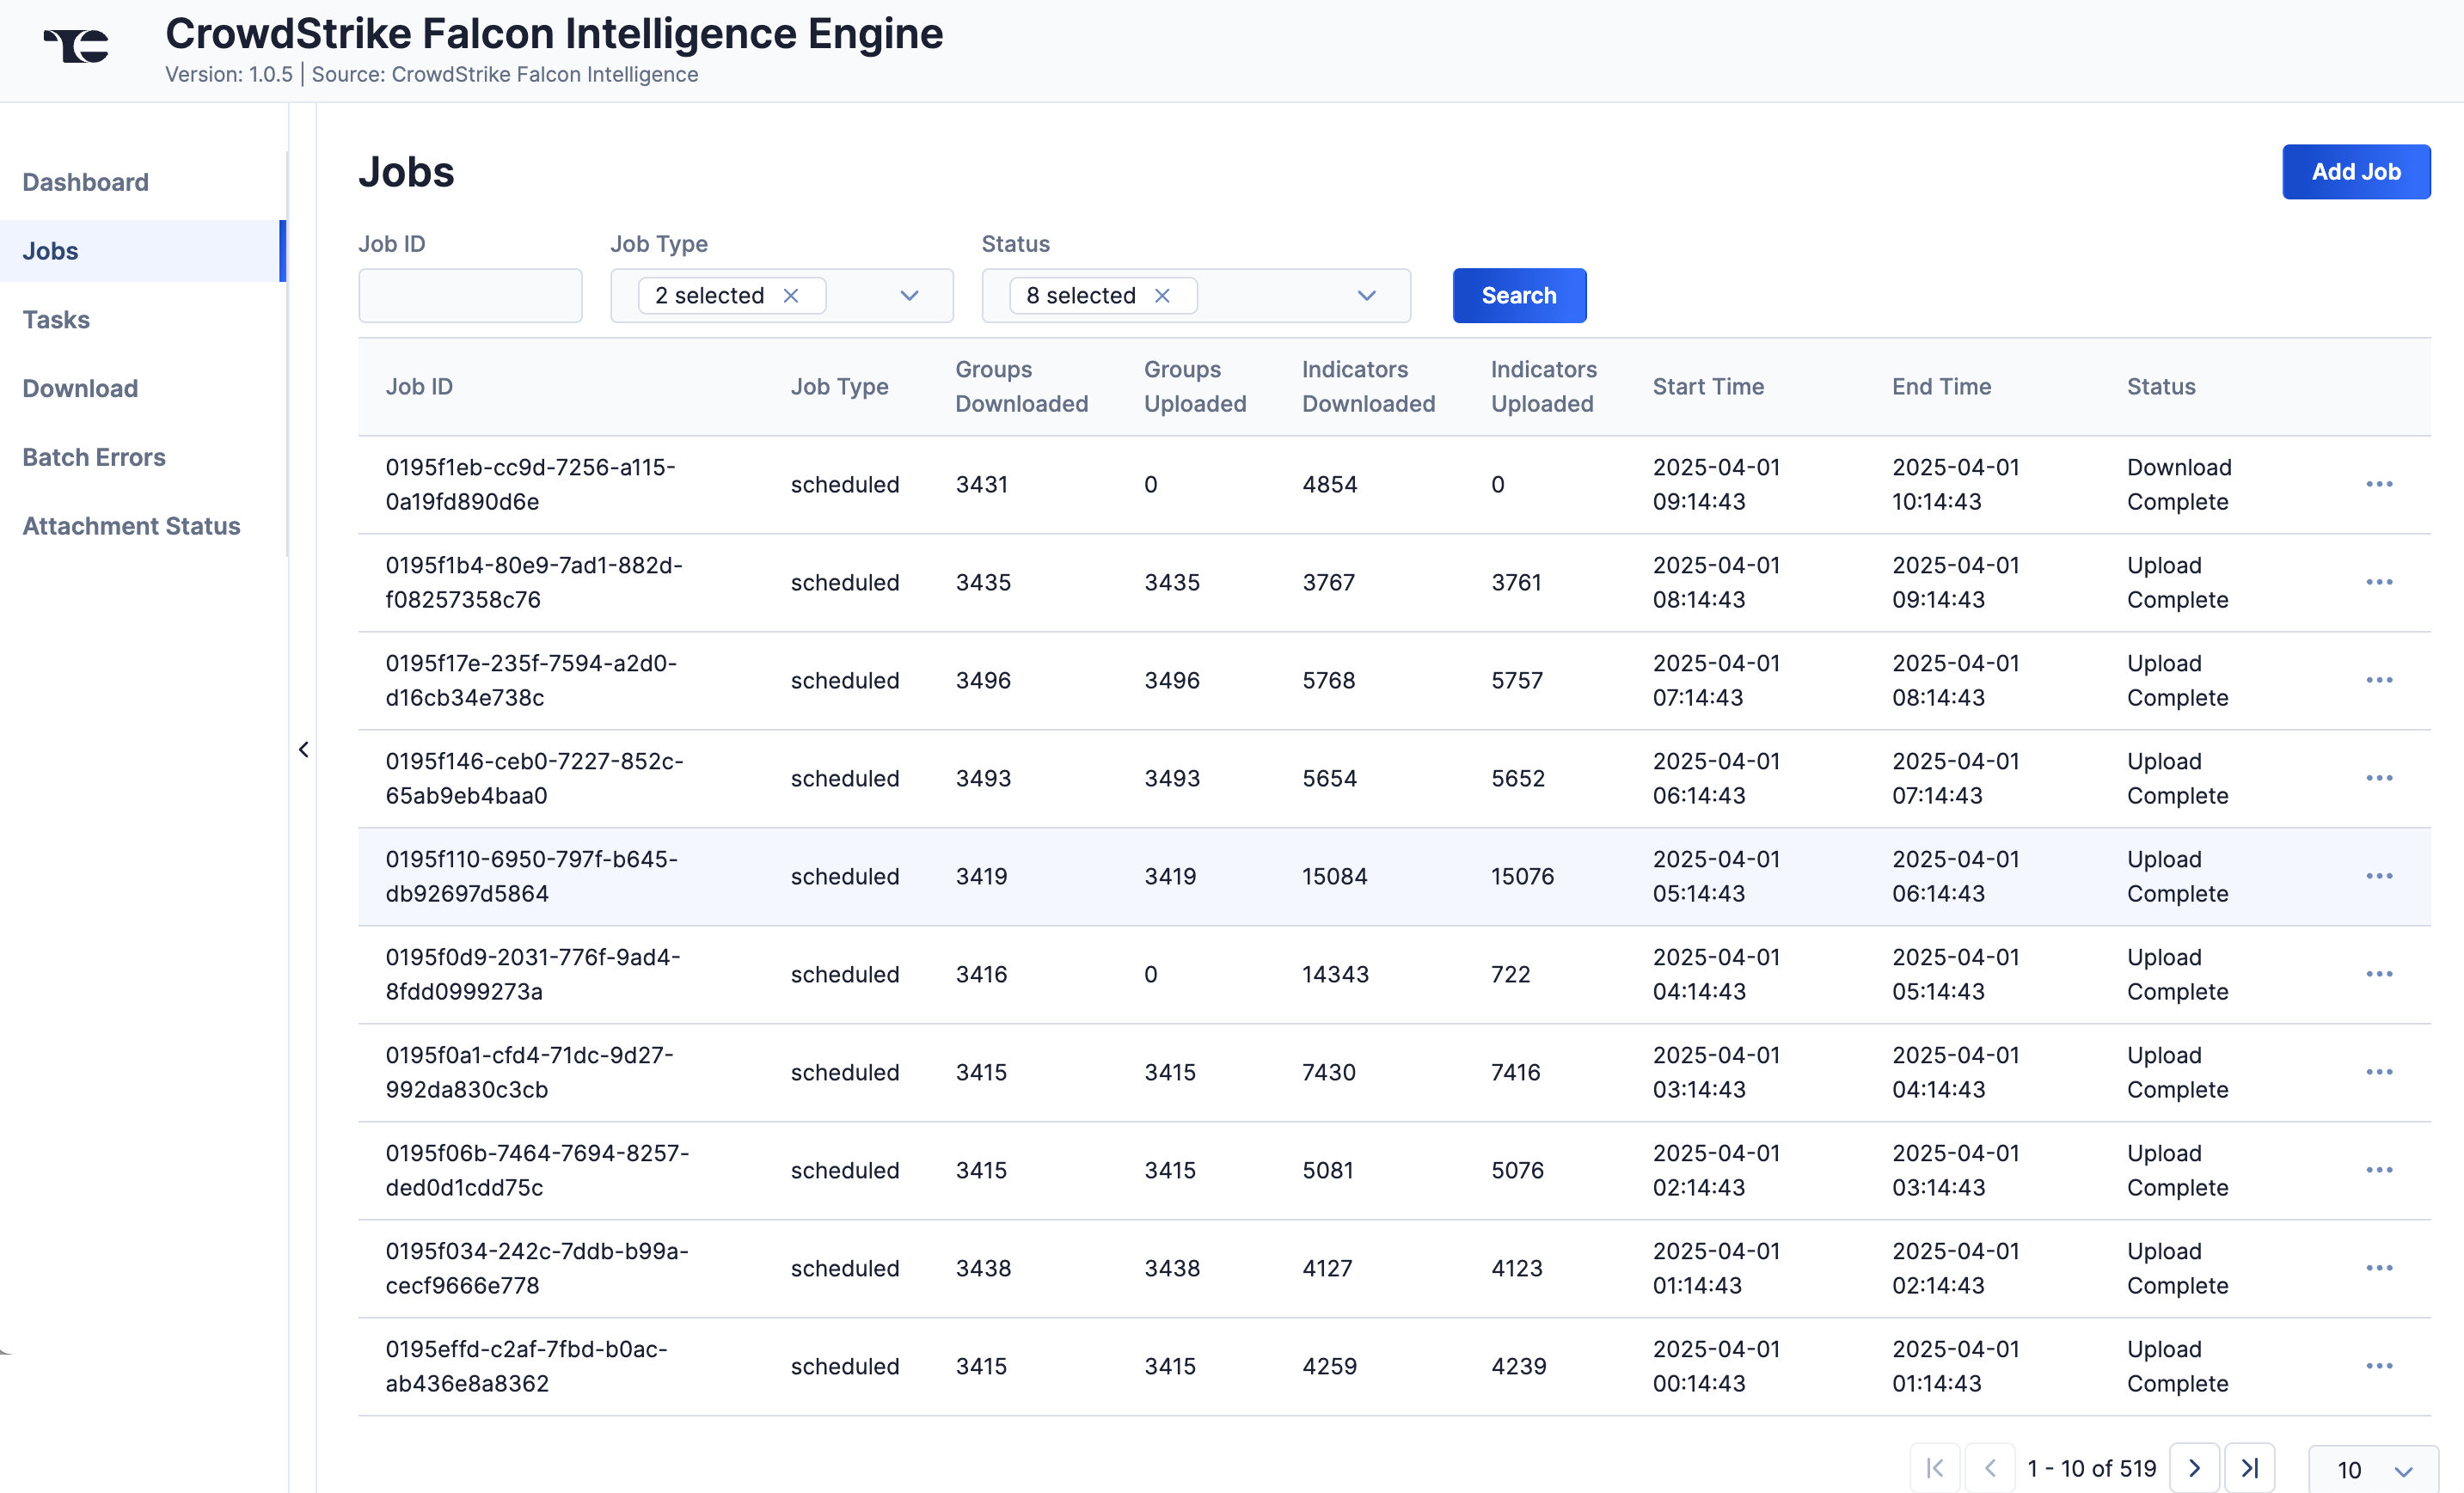
CrowdStrike Falcon Intelligence Engine Integration User Guide
CrowdStrike Falcon Intelligence Engine Integration User Guide
CrowdStrike Falcon Splunk App User and Configuration Guide | PDF | Mobile App | Information
CrowdStrike Falcon Intelligence Engine Integration User Guide