Working Through the Cyber Awareness Challenge 2025
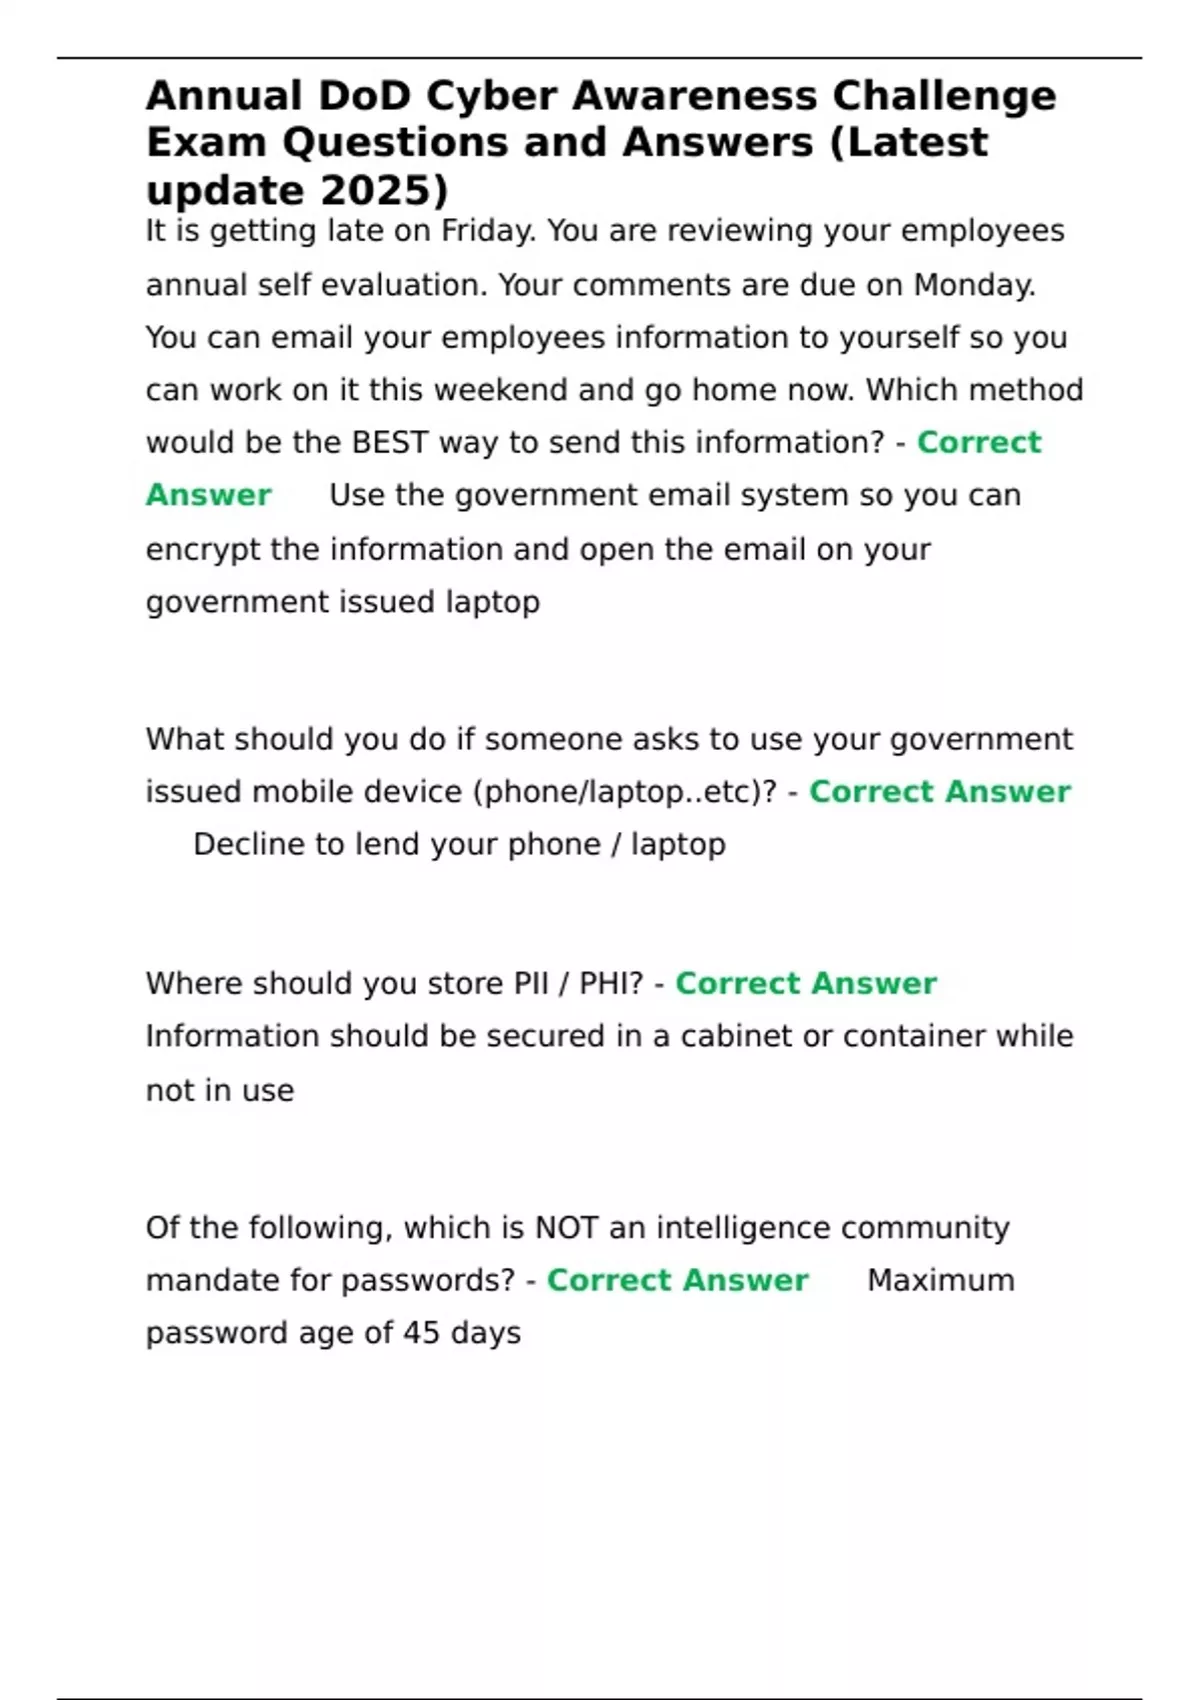
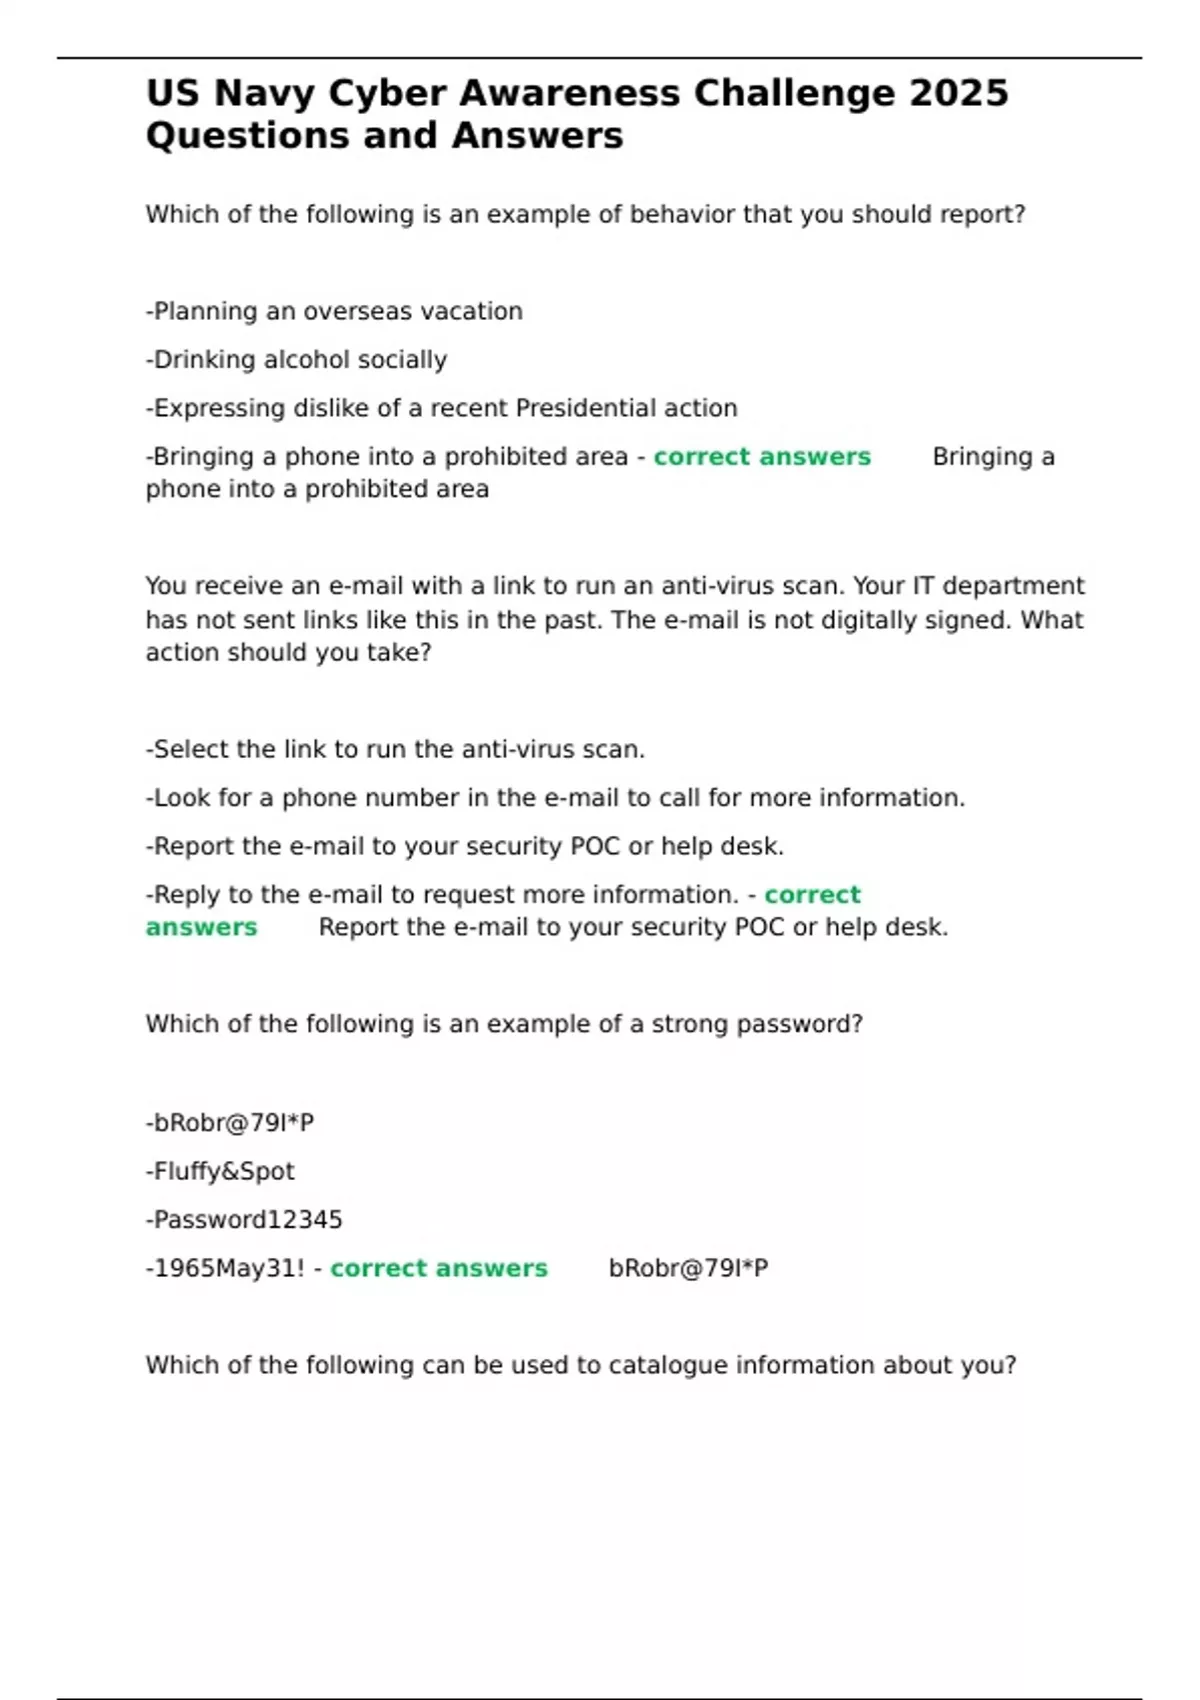
The Cyber Awareness Challenge is an annual training requirement for Department of Defense personnel and contractor employees. It covers everything from phishing recognition to physical security. I've been working through these cycles for years, and the format has stayed mostly consistent even as the question pool shifts. People look for Cyber Awareness Challenge 2025 Answers because the training module contains scenarios that aren't always straightforward, and the stakes are real — failure means having to restart or complete remedial training. The legitimate way to handle this challenge is through the official DoD Learning Portal. You log in with your CAC or DEP-ID credentials and access the module through COTC or the Defense Information School platform depending on your organization's tracking method. The answers you need are embedded in the training material itself. That's the thing most people miss — the module teaches you what you need to know before the assessment section even starts. I spent about forty minutes going through the 2025 version last cycle. The scenarios involve email analysis, USB device handling, social engineering calls, and physical access questions. The trick isn't memorizing answers. It's understanding the decision framework behind each scenario. For example, one question in the 2024 cycle asked about finding a labeled USB drive in the parking lot. The obvious "good citizen" answer of turning it in to a random office was wrong. The correct path was reporting it through proper channels with documentation. That same logic applied in 2025.
There are third-party sites posting answer keys. Some are accurate. Some are outdated from previous years with slightly reworded questions. I've seen people fail because they followed a 2023 answer key verbatim when the 2024 version changed the correct option. If you use external sources, cross-reference them against the official material. The DoD updates question wording periodically.
What Actually Changes Between Years
The core curriculum doesn't shift dramatically. Phishing still dominates. Ransomware awareness gets more emphasis each cycle. Supply chain compromise topics have been around since 2022 and they stay. What changes is the scenario framing — a ransom note email looks different, the social engineering attempt plays out through a different channel, the physical security violation happens in a new context. The principles behind the right answer remain constant. The 2025 version added more questions around AI-generated content detection in phishing attempts. This is a noticeable shift. Several scenarios now involve emails or messages that are almost but not quite right — subtle grammar that seems correct but has an off rhythm typical of AI composition. The training material covers this, but it moves fast. I had to pause and rewatch that section because the examples were genuinely tricky. The difference between AI-generated and human-generated text in these scenarios often comes down to unnatural phrasing patterns and overly formal tone in messages that should be casual. If you're taking this for a command or agency requirement, don't rush through it. The assessment portion usually requires a 70% or 80% pass rate depending on your organization's policy. You can retake it, but it eats into productive time. Going in prepared cuts the whole process from two hours down to about forty-five minutes on a first attempt.
Get the Full Details
The Scenario That Tripped Me Up
There was one question in the 2025 cycle about receiving a message from your supervisor asking you to transfer funds urgently with a note saying the normal approval process was unavailable due to a system outage. The instinctive answer for someone who hasn't thought about this recently is to comply. It's your supervisor. There's urgency. The system issue justifies skipping protocol. The correct answer involves verifying through a separate communication channel before taking any action. What made this harder than previous years was the realistic detail. The message included references to actual internal systems and used the supervisor's real email pattern. I second-guessed myself because the scenario was written to feel legitimate. The training module does address this exact pattern under business email compromise protocols, but you have to be paying attention during that section. The answer wasn't intuitive. It required recalling the specific verification steps taught earlier in the module. My workaround was to take notes while watching the training videos. Not summary notes — just writing down the exact verification procedures word for word. When I hit that question, I could trace my hand back to what I'd written. It's not glamorous, but it works. The DoD isn't testing whether you can guess. They're testing whether you absorbed the procedures.
Common Mistakes That Cause Failures
The biggest reason people get below the passing threshold is treating the scenarios as general knowledge questions instead of procedure-based ones. Cyber awareness isn't about opinion. It's about following established policy. When a question asks what you should do, there is a specific correct sequence defined in DoD policy. Guessing based on what seems reasonable usually lands you on the wrong option. Another failure pattern is skimming the scenario text. Many questions include critical details in the middle of a long paragraph. A date stamp, a sender address detail, a quoted phrase — one of these elements is the differentiator between two plausible answers. I've seen the same question fail half the people in a room simply because they missed a detail in the setup description. Physical security questions also trip people up because they apply civilian logic instead of facility logic. In a civilian context, holding a door for someone is polite. In a DoD facility context, tailgating through a controlled access point is a violation regardless of intent. The scenarios reflect this distinction, but it requires shifting your frame of reference from everyday behavior to institutional protocol.
What the Official Material Covers
The 2025 module runs through several distinct sections. The first covers foundational topics like malware variants, password hygiene, and device security. This is the part most people breeze through because it aligns with common sense. The assessment questions here are generally straightforward if you paid attention. The middle sections get into more specific territory — secure communications, data handling classifications, removable media policies, and remote access procedures. These are where the scenarios become detailed and the right answers less obvious. The training presents you with a situation and asks you to identify the violation or the correct response. Multiple choice options often include one clearly wrong answer, one partially correct answer, and one fully correct answer. Picking the partially correct one is the most common error. The final sections address emerging threats and organizational responsibilities. Social engineering, insider threats, and reporting procedures make up this portion. The AI content detection questions I mentioned earlier fall here. This section also reinforces the reporting culture — knowing where and how to report suspected incidents matters as much as recognizing them.
Practical Steps Before You Start the Assessment
Make sure your browser is compatible. The module works on Chrome and Edge but I've encountered rendering issues on Safari with certain scenario animations. If the video content doesn't load properly, you'll miss training material. Use a supported browser and clear your cache if the page seems unresponsive. Set aside uninterrupted time. The full module including assessment takes roughly fifty to seventy-five minutes depending on your reading speed. Trying to complete it in fragments leads to forgetting scenario details by the time you reach the end. I once split mine across three sessions and failed the assessment on the first attempt because I'd conflated details from different years of practice questions with the current material. The second attempt, done in one sitting, took under an hour. If your organization provides a practice quiz, take it. It won't match the exact questions, but it calibrates your understanding of the format and difficulty level. The real assessment tends to be slightly harder than practice material, so if you score well on practice, you should be in good shape for the actual module.
The Cyber Awareness Challenge isn't designed to be impossible. It's designed to ensure that every person with access to DoD systems understands the basic threat landscape and knows the correct procedures. The questions reward careful reading and attention to the training material. They punish assumption and haste. Work through the module methodically, verify your understanding of each section before moving on, and the assessment becomes a matter of recalling what you've already been taught rather than figuring things out on the spot.