Breaking Numbers Down
Most people encounter prime factorization in middle school and forget about it until they need it for something like cryptography or just cleaning up a math homework assignment. The core idea is simple enough: take any whole number greater than 1 and express it as a product of prime numbers. That is the Definition Of Prime Factorization In Math, though the actual mechanics of getting there can vary depending on the size of the number you are working with.
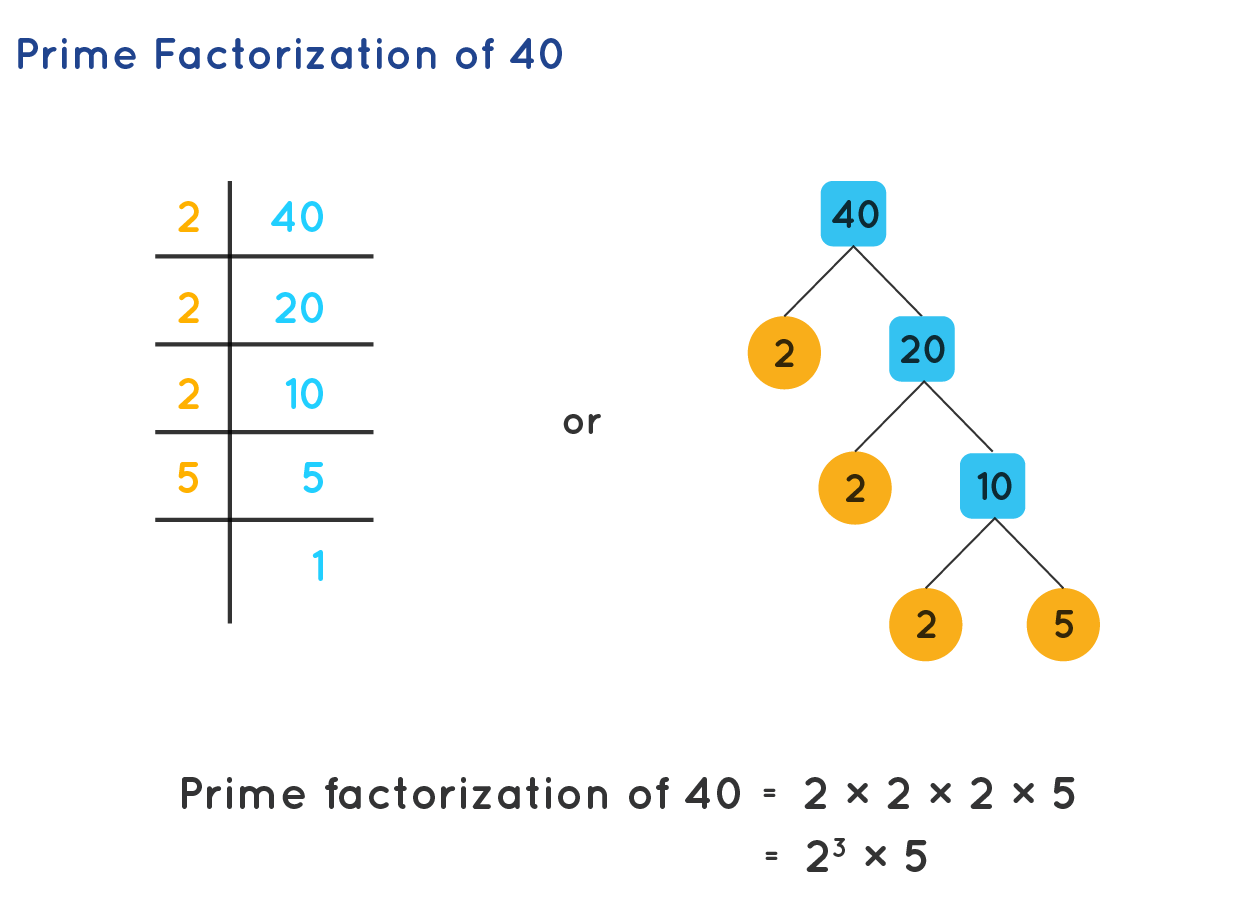
I remember grading a test where someone tried to factor 84 and ended up with 4 times 21 times 1. Technically they wrote primes as factors, but they missed that 4 breaks further into 2 times 2. The fundamental theorem of arithmetic guarantees that every integer greater than 1 has one and only one prime factorization, ignoring the order of the factors. So 84 is 2 squared times 3 times 7, and that is the only correct answer. Students often overlook repeated primes and write out a tree that looks good but isn't fully reduced. The formal definition is straightforward: for any integer n greater than or equal to 2, there exist unique primes p1 through pk and positive integers a1 through ak such that n equals p1 to the a1 power multiplied by p2 to the a2 power and so on through pk to the ak power. Uniqueness here is the key word. Two different people factoring the same number should arrive at the same set of primes with the same exponents, regardless of the method they used to get there. When I actually use this in practice, I usually start with trial division because it is fast enough for numbers up to maybe ten thousand. You divide by 2 as many times as possible, then 3, then 5, then 7, and you keep going until your divisor squared exceeds the remaining number. If you are left with something greater than 1 at the end, that leftover is itself prime. It sounds tedious doing it by hand for large numbers, and it is. But for the range most people actually need, it works without any special tools.
I once had to factor a number around two hundred thousand for a coding problem, and I spent too long doing it by hand before realizing I could just precompute primes up to the square root using a sieve. A simple Sieve of Eratosthenes up to about 450 would have given me all the divisors I needed in a fraction of a second. Writing that little script cut my time from maybe twenty minutes of tedious division down to under a minute of runtime. For numbers in the millions, even trial division becomes impractical without optimization, and you start looking at Pollard's rho algorithm or elliptic curve methods depending on the size. One thing beginners consistently get wrong is assuming that factor trees produce the answer automatically. They do not if you stop branching too early. I saw a case where someone factored 120 and wrote 2 times 2 times 2 times 3 times 5, which is correct, but then another student wrote 2 times 2 times 30 and called it done. Thirty is not prime. The stopping condition is strict: every single factor in your final expression must be prime, and you must not be able to break any of them further. Another edge case that trips people up involves the number 1. It has no prime factorization. The definition explicitly requires the number to be greater than 1, and 1 is the multiplicative identity, not a prime. If you encounter a problem that seems to involve 1, check whether it is actually asking for something else, like the greatest common divisor or least common multiple, both of which rely on prime factorization but handle 1 by simply excluding it from the product.
For really large numbers, especially those used in RSA encryption, classical prime factorization becomes computationally infeasible with current technology. A 2048-bit number has no known efficient classical algorithm for complete factorization, and that is literally what keeps the encryption secure. Quantum computers running Shor's algorithm could theoretically break this, but we are not there yet in any practical sense. If your work involves numbers of that scale, you are better off using built-in library functions rather than writing your own factorizer, because the edge cases and performance considerations are non-trivial. The practical takeaway is that for small to medium numbers, trial division with a sieve precomputation is your best friend. For anything larger, you either need a tool or a different approach entirely. The definition itself is clean and unambiguous, but applying it correctly requires paying attention to stopping conditions, uniqueness, and the computational limits of whatever method you choose to use.
Get the Full Details