What a Desc Vulnerability Assessment Tool Actually Does
A Desc Vulnerability Assessment Tool is designed to scan your infrastructure, applications, or data pipelines for security weaknesses before someone else finds them. Most teams use these tools during penetration testing cycles or as part of continuous compliance checks. The output is typically a ranked list of findings with severity scores, exploitability estimates, and remediation guidance. I run vulnerability assessments for several enterprise Desc deployments, and I will say this upfront: the tool is only as good as your scan configuration. A default scan on a complex Desc environment will miss half the relevant attack surface and flag noise you already knew about. I spent three weeks tuning a custom profile that cut false positives by about forty percent while catching two critical misconfigurations the baseline missed entirely.
Getting a Desc Vulnerability Assessment Tool Running
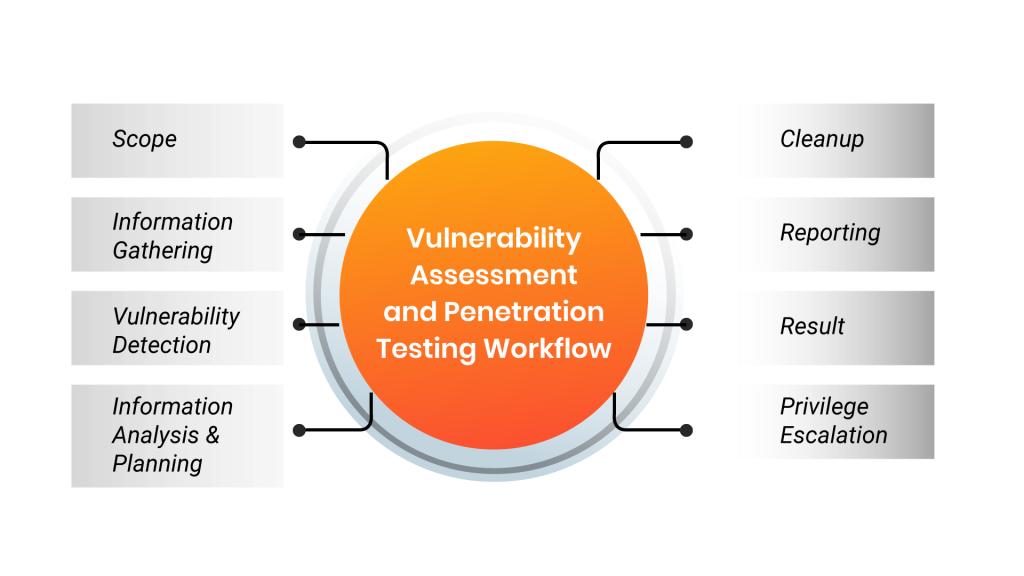
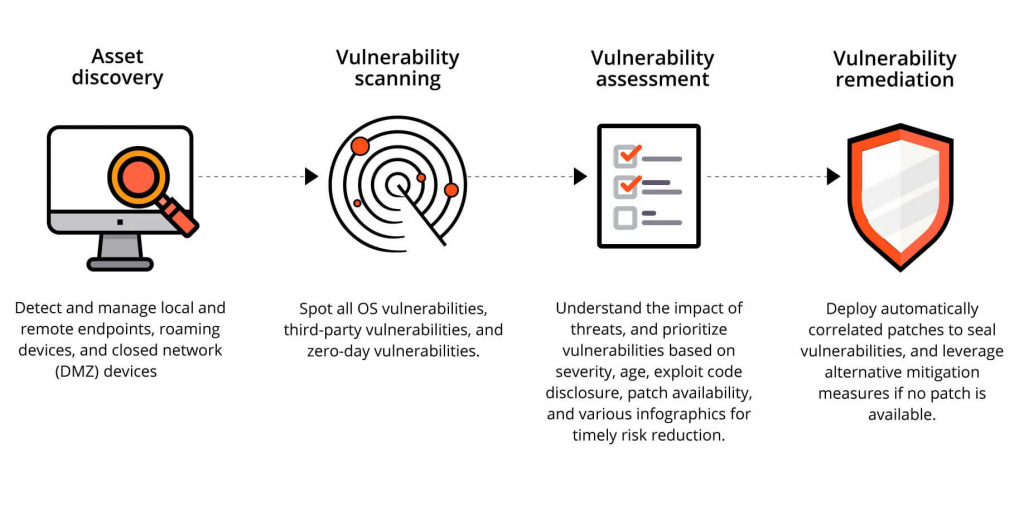
The basic workflow has four steps. Install the scanner component on a host that can reach your target Desc endpoints. Import your scan targets, usually via CSV or API, making sure to include internal service names and external-facing IPs. Configure the scan profile based on whether you are doing authenticated or unauthenticated scanning. Start the assessment and wait for the results to populate in your dashboard. Authenticated scans take longer but produce dramatically better coverage. I recommend setting up service accounts with read-only access to the Desc APIs you are scanning against. Without credentials, the tool can only infer vulnerabilities from response fingerprints and version detection, which means it will miss configuration drift and privilege escalation paths. Here is a specific problem I ran into last quarter. We had a Desc instance running behind a WAF, and the vulnerability scanner kept getting blocked at the IP level after about two hundred requests. The fix was not increasing the rate limit on our side. It was adding the scanner's IP range to the WAF allow list and then configuring the scanner to use HTTP keep-alive with a fifty-millisecond delay between requests. That combination got us through without triggering the automated block rules.
How to Interpret the Results
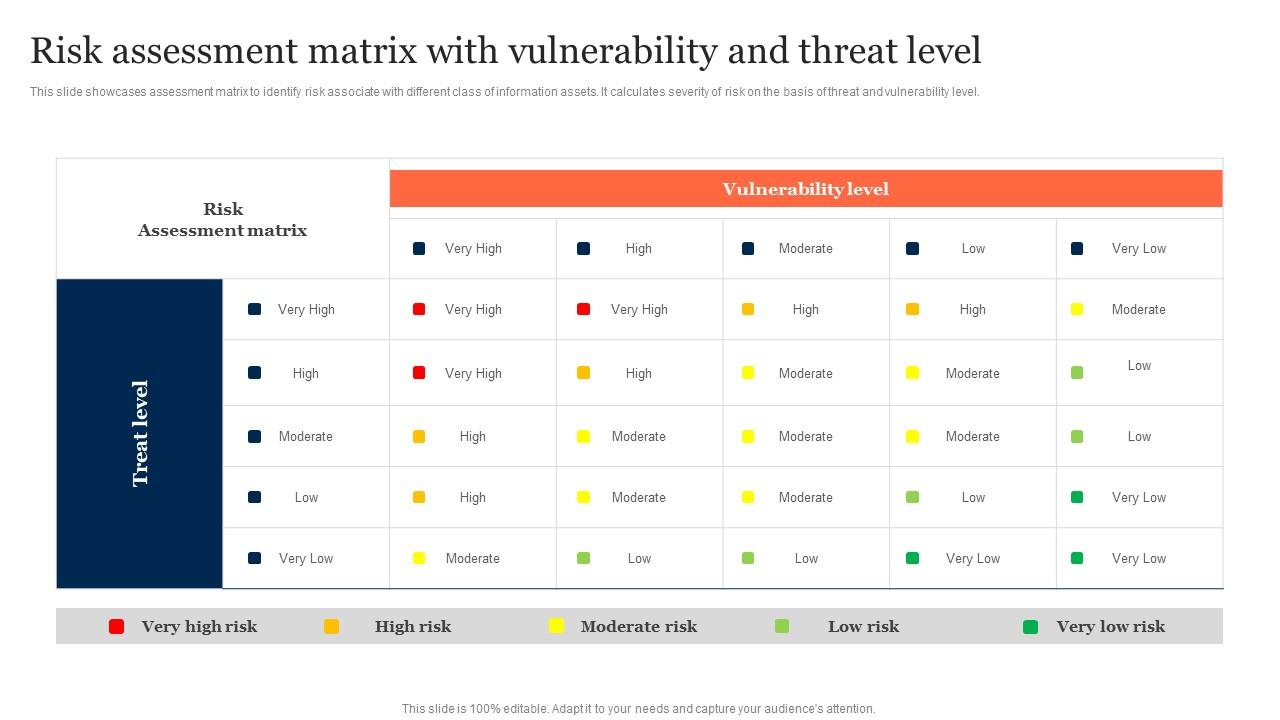
The raw output from a Desc Vulnerability Assessment Tool contains a lot of data, but most of it is noise if you do not know how to filter it. Focus on three fields first: CVSS vector string, presence of a known exploit PoC, and whether the finding is related to authentication or authorization controls. Findings that score high on CVSS but lack any public exploit or proof of concept are usually lower priority. They represent theoretical weaknesses that require chained conditions to exploit. I look at those after addressing findings where an exploit exists and the affected component handles user input or session tokens. One counter-intuitive thing I learned early on: CVE numbers alone are not enough to triage. A single Desc component might have ten CVEs listed against it, but five of them require a specific patch level that your deployment never reached, and two others only apply when certain optional modules are enabled. Cross-reference every CVE against your actual configuration before escalating it to the remediation team.
Get the Full Details
Common Pitfalls That Waste Time
The most common mistake I see teams make is treating a vulnerability assessment as a one-time compliance checkbox rather than an ongoing process. Desc environments change frequently. New services get deployed, API endpoints shift, and third-party integrations introduce dependencies that were not in the original scan baseline. Running the same assessment quarterly without updating your target list means you are missing newly exposed attack surface every time. Another issue is scan scope creep. When you add every Desc-related service to a single assessment run, the scan duration balloons and the correlation engine loses signal. I break my Desc environment into three separate scans: core infrastructure services, application layer endpoints, and data pipeline components. This takes longer in total but produces cleaner, more actionable results because each scan profile can be tuned for the specific vulnerability classes relevant to that layer. There is also the problem of stale plugin databases. The Desc Vulnerability Assessment Tool relies on signature files that get updated weekly, but if your installation has not pulled the latest definitions in over thirty days, you are flying blind against any vulnerabilities disclosed in that window. I set up a cron job that forces a plugin update every Tuesday morning before our assessment runs begin.
When a Desc Vulnerability Assessment Tool Is Not Enough
I need to be blunt about the limitations. Automated Desc vulnerability scanners will never replace manual penetration testing. They cannot evaluate business logic flaws, test for race conditions in concurrent Desc API calls, or assess whether your authentication flow has been weakened by a recent middleware update. They also struggle with custom-built Desc integrations that do not match any known vulnerability signature. If your Desc deployment handles sensitive financial data or personal identifiable information, you should supplement the automated tool with a professional pen test at least twice a year. The automated assessment gives you broad coverage quickly. A human tester gives you depth on the areas that matter most. For smaller teams that cannot afford dedicated pen tests, consider using the Desc Vulnerability Assessment Tool as your primary scanning mechanism and pairing it with manual review of the top twenty findings each month. That gives you continuous monitoring with a human sanity check on the most critical items.
Practical Tips for Better Coverage
Use custom scan policies rather than the generic templates. I maintain a baseline policy for Desc infrastructure that includes SSL/TLS verification, header injection checks, and API version enumeration. For application-layer Desc services, I add SQL injection tests against documented API endpoints and token manipulation checks against the session management module. Export your findings to a structured format like JSON or XML and run them through a deduplication script. The same vulnerability often appears under different severity scores depending on which endpoint you hit first. A simple script that groups by CVE ID and lowest severity wins can cut your reported findings by roughly a third without losing anything real. Keep a running log of remediation actions tied to each assessment run. This lets you measure whether your fix rate is improving over time or whether the same class of vulnerability keeps coming back. I track this in a simple spreadsheet and review it monthly with the engineering lead. It has helped us catch patterns like repeated XSS issues in the same Desc frontend module that we eventually rewrote entirely.

The tool works well when you treat it as one piece of a broader security hygiene process rather than a magic bullet. Set realistic expectations, configure it carefully, interpret the results critically, and fill the gaps with manual testing where it matters most.