IT and Security Are Different Jobs With Different Problems
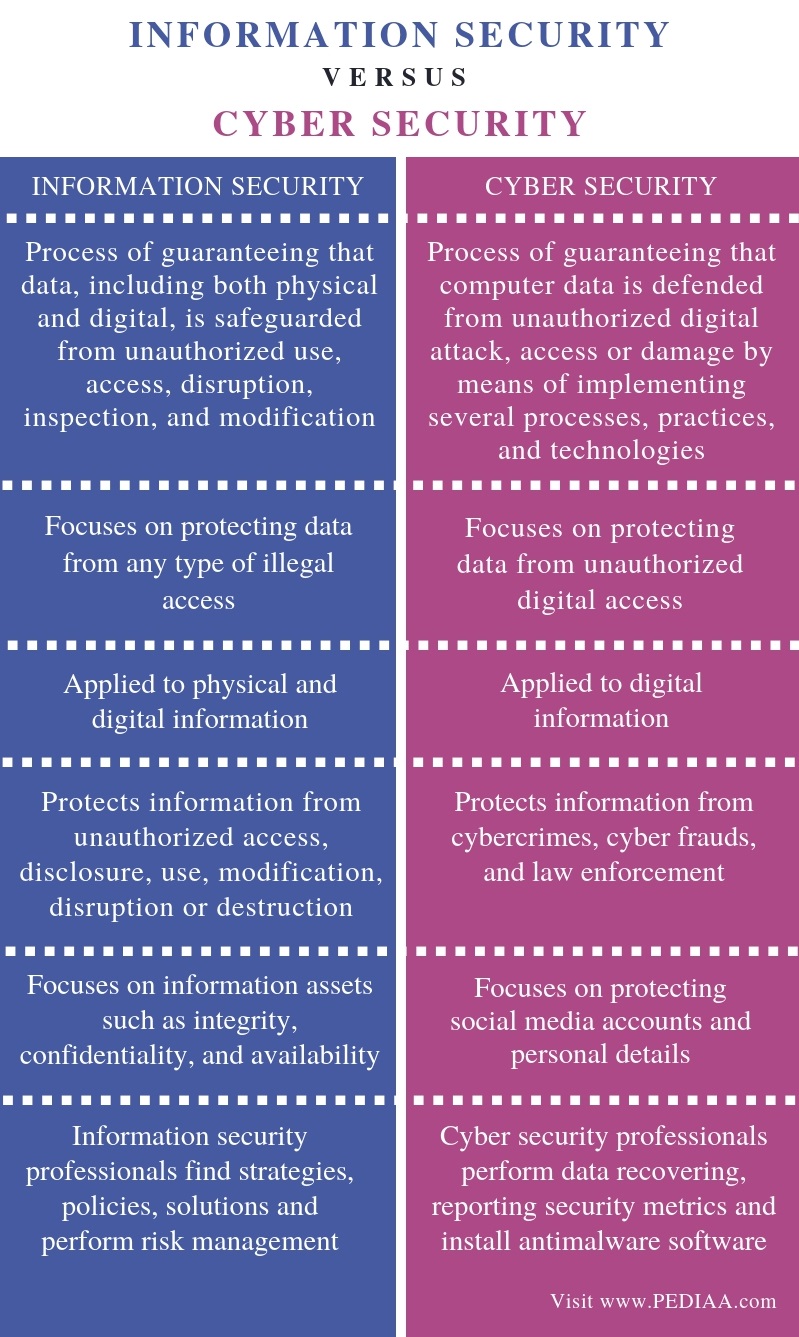
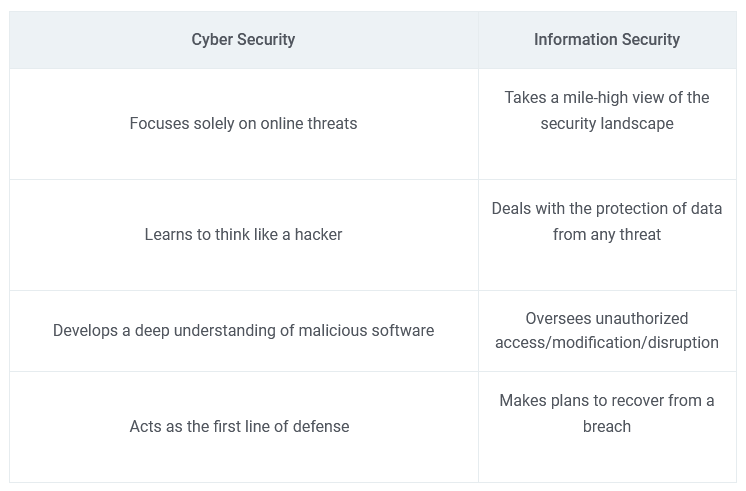
Most people treat Information Technology and Cyber Security as the same department because they both work with computers. That assumption breaks things fast. IT builds and maintains the systems that keep a business running. Cyber Security protects those systems from threats. One focuses on uptime and functionality. The other focuses on risk and control. They overlap, but the work is fundamentally different. In my experience managing infrastructure, the core split is about incentives. IT is rewarded when systems are available and users can do their jobs. Speed, accessibility, and cost efficiency drive IT decisions. Security is rewarded when incidents don't happen, which means being the department that says no more often than yes. That tension isn't philosophical. It shows up every single day in ticket queues and change management meetings. Let me walk through what this looks like in practice. I once inherited a mid-size company where the IT team had deployed a new cloud file-sharing solution across three divisions in under two weeks. The solution worked fine technically. What nobody had considered was that the authentication method was basic password-based login with no MFA, the data classified as "internal" was flowing through to a public-facing tenant, and the audit logs were set to delete after 30 days by default. From an IT standpoint, this was a win. From a security standpoint, it was an exposure. Fixing it required a complete authentication overhaul, data classification mapping, and a SIEM integration that added about six weeks to the rollout. Nobody on the IT side expected that friction. It's not because they were careless. It's because their success metric was different.
What IT Actually Does Day to Day
Information Technology covers infrastructure, applications, networking, helpdesk support, and system administration. IT professionals keep servers running, manage user accounts, deploy software updates, maintain networks, and resolve the daily technical problems that come up. They work in cycles of provisioning, monitoring, and maintenance. The work is cyclical and operational. When a server goes down, IT fixes it. When a printer breaks, IT handles it. When a new employee starts, IT provisions their equipment and access. The focus is functional continuity. IT teams typically use tools like Active Directory for identity management, Cisco networking gear for infrastructure, VMware or Hyper-V for virtualization, and ticketing platforms like ServiceNow or Jira for incident tracking. They measure success through metrics like mean time to resolution, system uptime percentages, and user satisfaction scores. Most IT departments operate on annual budgets with predictable resource allocation. The work is stable in a way that security work rarely is.
What Cyber Security Actually Does Day to Day
Cyber security is about identifying threats, building defenses, and responding to incidents. Security professionals work in a state of uncertainty. They can't predict what will be attacked tomorrow. Their work involves threat intelligence monitoring, vulnerability assessment, penetration testing, incident response, and policy development. Where IT has a to-do list, security has a worry list. The tool landscape looks completely different. You'll see SIEM platforms like Splunk or Microsoft Sentinel for log aggregation, EDR solutions like CrowdStrike or Microsoft Defender for Endpoint for endpoint protection, vulnerability scanners like Nessus or Qualys for asset exposure tracking, and SIEM tuning becomes its own full-time discipline because false positives can drown a team in noise. A well-tuned SIEM reduces alert fatigue by roughly 60 to 70 percent. A poorly tuned one generates so many incidents that security staff spend more time triaging false alarms than investigating real threats. This is something most beginners don't understand until they're living through it.
Get the Full Details

The Overlap Zone Where Things Actually Break
Security and IT intersect most visibly in identity and access management, patch management, and network segmentation. These are areas where both teams have to agree on how work gets done. The problems start when the agreement doesn't exist or when one team operates without the other. I remember a specific engagement where the IT team configured a new VPN gateway for remote employees. The configuration was technically sound. The device worked, throughput was adequate, and the rollout went smoothly. The security team found the issue two weeks later during a routine audit. The VPN was configured to allow split tunneling by default, which meant encrypted corporate traffic and unencrypted personal traffic were both passing through the same interface. The firewall rules on the internal side were designed assuming all traffic came through a unified gateway, not a hybrid setup. We had to reconfigure the VPN client profiles to force all traffic through the tunnel, update the firewall policies to match the new traffic pattern, and retrain about eighty remote users on the updated client software. That was a three-day operation that could have been a fifteen-minute configuration review if both teams had been in the same room before deployment. It wasn't a security failure. It was a communication failure between two functions that use different languages.
Skill Sets Required for Each Track
IT professionals need strong operational knowledge. Networking fundamentals, operating system administration, database management, and application support are core competencies. Certifications like CompTIA Network+, Server+, and vendor-specific credentials from Cisco, Microsoft, and VMware are standard career steps. The learning curve is steep but structured. There's a clear progression from helpdesk to systems administration to infrastructure engineering. Security requires a broader and less linear knowledge base. You need to understand IT well enough to know what you're protecting, then add layers of specialized knowledge in cryptography, threat modeling, forensic analysis, compliance frameworks, and attack methodology. Certifications like Security+, CISSP, CEH, and OSCP represent different paths. The field changes faster than any certification curriculum can keep up with. New attack techniques emerge regularly. Defensive strategies need constant adaptation. A security professional who stops learning for two years is effectively working with outdated defenses.
A Counter-Intuitive Point About Security Hiring
Most entry-level job postings for security roles require two to three years of experience. The problem is that genuine security experience usually requires being inside a security team. It's a catch-22 that pushes people toward IT first and then pivoting later. The practical workaround is building home labs, participating in capture-the-flag competitions, and contributing to open-source security projects. A GitHub repository with Python scripts for log parsing or network monitoring carries more weight than most entry-level candidates realize. IT work has its own frustrations that people outside the field don't always see. The endless cycle of maintenance, the blame when something breaks, and the perception that IT is just "computer people" who fix printers are real career drains. Burnout rates in IT support roles are high. The technical depth varies wildly depending on the organization. Some IT teams get to work on architecture and automation. Others spend forty hours a week resetting passwords and replacing keyboards. Security has a different set of burnout drivers. The constant threat awareness, the on-call rotations for incident response, and the institutional resistance to security controls create a unique stress profile. Security professionals also face the problem of being measured by the absence of events. When security works well, nothing happens. Leadership rarely applauds a quarter with zero breaches. They notice immediately when one occurs. This asymmetry affects performance reviews, budget requests, and career progression more than most people entering the field expect.

A Note on Tools and Implementation Reality
Buying security tools doesn't create security. This is the single biggest misconception I see organizations make. A $50,000 vulnerability scanner sitting unused saves zero assets. The tools have to be integrated into operational workflows, staffed with people who know how to interpret results, and fed with current intelligence data. A typical enterprise vulnerability management program costs between $150,000 and $400,000 annually when you factor in licensing, staffing, and ongoing tuning. The return isn't dramatic. The return is the absence of a catastrophic event that would have cost ten times that amount. For smaller organizations, the realistic path is starting with fundamental hygiene rather than chasing comprehensive security frameworks. Patch management, enforced MFA, network segmentation at the subnet level, and centralized logging will cover the majority of common attack vectors. These measures typically reduce incident likelihood by 70 to 80 percent with minimal ongoing cost. Frameworks like NIST CSF or ISO 27001 are useful for maturity scaling, but they're not required to achieve basic security posture. Most small teams skip straight to framework compliance and never establish the operational foundation underneath it.
How the Fields Are Converging
DevSecOps, infrastructure as code, and cloud-native security are blurring the traditional lines between IT and security. Security is moving left into development workflows. IT is adopting more security-minded tooling by default. Cloud providers bake security features into their platforms, which means IT teams deploying infrastructure now interact with security controls regularly. The distinction between the two fields is narrowing in practice, even though the core priorities remain different. The professionals who thrive in this environment understand both sides. An IT engineer who can write a Python script to automate vulnerability scanning findings into a ticketing system adds disproportionate value. A security analyst who understands Kubernetes networking can actually design effective container security policies instead of just reading about them. The pure specialists still exist and are necessary, but the hybrid skill set is where career growth is happening right now.
Practical Steps If You're Deciding Between the Two
Start with IT fundamentals regardless of which direction you ultimately choose. Networking, operating systems, and basic scripting are prerequisites for effective security work. If you jump straight into security without understanding how the underlying systems operate, you'll spend your career applying generic controls that don't fit the actual infrastructure. That approach works for compliance checklists. It fails during real incidents. Gain six to twelve months of hands-on IT experience before transitioning into security. In that time, you'll learn how systems are actually deployed, how users interact with technology, and where the real failure points are in typical environments. The gap between textbook security and operational security is wide enough that practical experience fills it faster than any course can.