The Actual Size of a Payment Card and Why It Matters More Than You Think
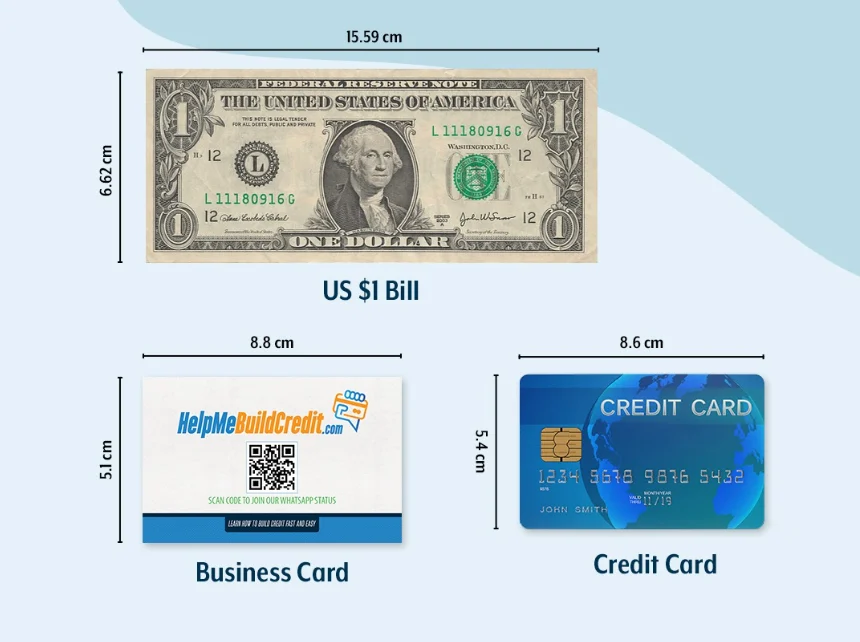
A credit card measures 85.60mm by 53.98mm with a corner radius of about 3.18mm. That is ISO/IEC 7810 ID-1, and it is the standard for virtually every payment card you will encounter in the real world. The thickness sits at 0.76mm, give or take a fraction depending on the issuer and laminate process. I have spent years dealing with card readers, embedding modules, and the occasional disaster where a merchant's machine refused a perfectly valid card. The dimensions are not arbitrary. They exist because a global standard needed to solve a practical problem: magnetic stripes, chip contacts, and later, contactless antennas all have to sit in predictable locations on a predictable surface. Move the track two millimeters and your whole acceptance ecosystem breaks.
Dimensions Of A Credit Card You Should Actually Memorize
The full width is 85.60mm. The height is 53.98mm. The thickness is 0.76mm. Corner radius is 3.18mm. The magnetic stripe occupies the top third of the card, running the full width. EMV chip contacts sit roughly in the center-left area. NFC antenna traces are embedded just below the surface, spanning most of the card face. These placements are codified in ISO/IEC 7811 for the magstripe and ISO/IEC 7816 for the chip. What most people miss is that the standard leaves very little tolerance for variation. The allowable deviation on width and height is fractions of a millimeter. Card manufacturers work in that tight band because readers are built to expect cards within those tolerances. A card that is even 0.5mm too thick will jam in certain ATMs, especially older machines with worn feed rollers.
How This Shows Up In Practice
When you design for card acceptance, whether you are building a POS system, validating a checkout flow, or just trying to figure out why your card gets rejected at a particular terminal, the dimensions dictate everything. The reader's guidance mechanism, the skipper in the ATM, the chip insertion depth, and the NFC coupling zone all depend on the card being within spec. I once dealt with a merchant who had an old Verifone terminal from around 2008. It swallowed cards consistently. Not every card, but certain ones. We traced it to a batch of corporate cards from a fintech issuer that measured 0.82mm thick, just over spec. The feed rollers were worn enough that the extra height caused a slight angle shift during insertion, and the card would bind before reaching the full read position. The workaround was manual key-enter for those specific cards while the terminal was serviced. Replacing the roller assembly solved it permanently, but it took three weeks and a parts order that the merchant had to push through support.
Get the Full Details
The Edge Cases Nobody Talks About
There are scenarios where the standard dimensions do not match what you receive. Some metal cards from premium issuers are thicker, sometimes up to 1.0mm. Many of these will not work in certain terminals or ATMs. The metal also interferes with the NFC antenna if the conductive layer is too dense. I have seen contactless fail on a titanium card where the manufacturer did not isolate the antenna zone properly from the metal substrate. Another issue is the card surface texture. Matte finishes, embossed lettering, and protective coatings all affect how the card interacts with the reader. A deeply embossed number can prevent a card from sitting flush in a contactless reader, which reduces the coupling efficiency just enough to cause intermittent failures. This is more common on cards that market themselves as premium or novelty designs. If you are working with card validation software, you need to account for the fact that some terminals will reject cards that are slightly out of spec even when the data is perfectly fine. The terminal is not being difficult. It is designed around the ISO standard, and anything outside that range introduces mechanical or RF variability that the hardware cannot reliably compensate for.
Why This Is Not Just a Measurement Exercise
Understanding the Dimensions Of A Credit Card is relevant whenever you deal with payment infrastructure. If you are a developer integrating a card reader SDK, you need to know the physical constraints that affect your user experience. If you run a retail operation, you need to know which cards your equipment might reject and why. If you manufacture cards, you are living inside those tolerances every day. The NFC field sensitivity of a reader is calibrated for a card of this size and shape. A business card or ID card that happens to contain an NFC tag will not couple as efficiently because the antenna size and positioning are different. Readers optimize their field for the ISO card footprint. Smaller tags simply sit outside the sweet spot of that field. Magstripe readers have a gap that matches the stripe position on the standard card. If you try to swipe something wider or narrower, the head does not align correctly with the data tracks. This is why some people attempt DIY solutions with custom-shaped cards and wonder why they never work in real terminals.
What You Can Do With This Information
If you are troubleshooting a card rejection, check the physical card first. Look for signs of warping, excessive thickness, or surface damage. Run the card through a different terminal to see if the problem is consistent. If it is terminal-specific, it is likely a mechanical fit issue rather than a data problem. Document the card issuer and card type so you can escalate to the right team. If you are designing a system that handles cards physically, build in tolerance for cards at the upper end of the thickness spec and account for minor warpage from temperature and usage. Terminals that only accept cards exactly at 0.76mm will frustrate users more than those that accommodate the full allowed range. For digital integrations, the dimensions matter less than the data formats, but they still influence how users interact with your product. If your app asks users to photograph their card for onboarding, knowing the standard size helps you set the right framing guidelines. A card that fills too much or too little of the frame leads to poor OCR results and higher failure rates during entry.

Limitations Worth Stating Clearly
The ISO standard covers the vast majority of payment cards, but it does not cover every variant in circulation. Some novelty cards, travel cards, and regional payment instruments deviate from ID-1 dimensions. These cards are not invalid. They are just outside the equipment that most merchants and financial institutions maintain. If you rely solely on standard card readers, you will exclude those. Thickness tolerance is another area where things break down. The standard allows variation, but individual terminals have their own mechanical limits. A card that passes one reader may fail another. There is no universal test that guarantees acceptance across all equipment, and no single dimension measurement can predict compatibility with 100% accuracy. If you need guaranteed acceptance across all terminals, the only reliable path is to stay within the ISO standard and avoid metal or oversized cards. Premium metal cards are a liability in any environment where universal acceptance matters, and issuers that produce them should be aware of that tradeoff.