Understanding What Actually Happens When You Run Through This
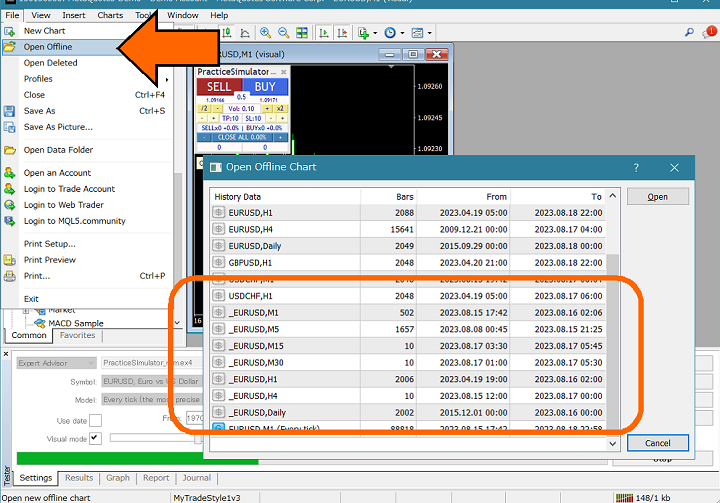
A Directory Practice Simulator is exactly what it sounds like: a sandbox environment where you can interact with simulated directory objects, run queries, modify attributes, and break things without any risk to a real Active Directory or LDAP deployment. I spent years working with AD infrastructure before I ever saw one of these, and honestly, my early experience was mostly winging it in small test domains I threw together on spare hardware. Those lab environments always had some quirk that didn't match real production—sometimes it was a weird schema extension that conflicted with my test script, sometimes it was a Domain Controller with a replication issue I couldn't reproduce. That's what a simulator tries to eliminate. The core concept is straightforward. You get a virtual directory tree, user accounts, groups, OUs, and enough functionality to practice things like delegation, Group Policy targeting, attribute manipulation, and replication troubleshooting. Some simulators go deeper, giving you simulated DNS integration or even simulated authentication flows through Kerberos. The ones I've used that include KDC simulation are worth your time if you're studying for something like the Microsoft Certified: Identity and Access Administrator credential. They save you from needing an entire domain controller VM running in a corner of your lab.
Directory Practice Simulator: Getting Started
If you're downloading one, look for something that gives you a working directory instance you can connect to with standard tools—LDP, ADSI Edit, PowerShell with the ActiveDirectory module. The moment a simulator requires you to use some proprietary client interface, it's probably not teaching you anything transferable. I once went through two weeks with a simulator that had its own custom management console. Every task I practiced felt useful until I tried to apply it to a real environment and realized the object models and attribute paths were completely different. That was a waste. Stick with simulators that expose standard LDAP ports and let you connect the way you would to a real server. Most of these tools run locally on Windows. You'll need .NET Framework or .NET Core depending on the version, and some require a minimum amount of RAM just to hold the simulated directory in memory. I've seen simulators choke at around 4GB of directory data when you start throwing bulk import scripts at them. Don't try to simulate a Fortune 500 org structure in your practice environment. Start small—three OUs, a couple hundred objects, basic group policies. You can always scale up later once you're comfortable with the tool itself.
What These Tools Actually Teach You and Where They Fall Short
The honest part: a Directory Practice Simulator will make you faster at navigation and syntax. You'll stop second-guessing whether to use -Filter or -LDAPFilter in PowerShell. You'll internalize the difference between a global catalog query and a standard directory search. That's real. But there are things no simulator can teach you. Real replication latency, actual schema migration pain, the experience of a broken SYSVOL share during a Group Policy refresh on a Friday afternoon at 4:47 PM—none of that exists in a simulator. The simulators I've used simulate replication errors by letting you toggle a "simulate failure" switch. It's not the same as watching a DC sit out of rotation for six hours because a subnet mask was misconfigured. One thing I learned the hard way involves the way simulators handle object class inheritance. When you create a custom object or extend a schema class in a simulator, the validation is often much more lenient than in production AD. I spent a solid afternoon building a script that created a bunch of custom contacts with non-standard attributes, and the simulator accepted everything without complaint. I ran the same script against a domain controller in a training environment and got attrtype violations on three of the attribute definitions. The simulator had been silently ignoring schema validation rules that would have blocked the entire operation in reality. The workaround was to enable strict schema mode if the simulator supports it, or to cross-reference your test results against the actual schema documentation rather than trusting the simulator's acceptance as proof of correctness. Another common pitiful gap is Group Policy processing order. Simulators will show you that a policy applied, but they almost never reflect the real timing issues—like a user logging in while a background policy refresh is still writing to the registry, or the infamous slow-site detection that changes GPO application order depending on which domain controller authenticates them. I once diagnosed a "random" Group Policy issue in a simulator by toggling between controllers, and the behavior made sense in the simulated environment. When I replicated the scenario with actual DCs, the outcomes diverged enough that I had to go back to first principles instead of relying on simulator logic.
Get the Full Details
Practical Workflow I Use When Practicing
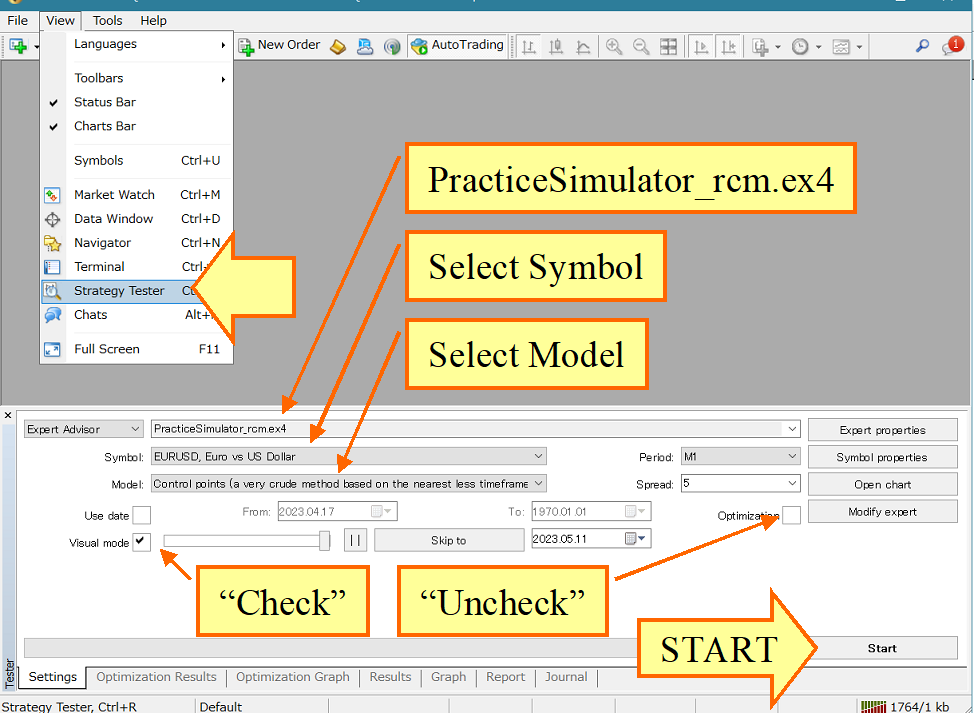
Here's how I actually use a Directory Practice Simulator without fooling myself into thinking I've learned everything. I start with a clean install, reset the directory to its default state, and then pick one specific skill area for the session. Maybe it's delegation. Maybe it's filtering a complex LDAP query. I don't wander around trying everything at once—that's a recipe for surface-level familiarity with no depth. For delegation practice, I set up a scenario where a helpdesk admin should be able to reset passwords and unlock accounts in a specific OU but absolutely nothing else. I configure it, test it with a low-privilege account, and then deliberately try to escalate. Can I add myself to Domain Admins? Can I modify the delegation rules? Simulators sometimes let you brute-force your way around restrictions because the security model isn't fully enforced. When I notice that happening, I note it and move on. The lesson is still valid even if the simulator's access control implementation is a bit loose. When practicing PowerShell cmdlets, I write the commands in a plain text editor first, run them, and then check the results. I use Get-ADUser with -Properties to pull attributes that aren't returned by default, and I practice piping objects through Select-Object to shape output the way I'd need it for reporting. This takes about twenty minutes per session and builds actual muscle memory. Reading about the cmdlets in documentation doesn't produce the same result.
One technique that actually works better than most people expect: export a snapshot of your simulated directory, mess things up deliberately, and then practice recovery. Restore from the snapshot, introduce a problem like a misplaced delegation or a corrupted group membership, and work through it. This is closer to real incident response than any structured tutorial you'll find online. I've used this approach for troubleshooting attribute replication inconsistencies and it's been the most effective way to build the kind of intuition that matters when something breaks in production.
Alternatives If a Simulator Isn't Cutting It
If you can't find a Directory Practice Simulator that fits your needs, or if you've hit the limits of what simulation can teach you, there are other paths. A virtual machine with a Windows Server evaluation copy and the AD DS role installed will give you the full experience for 180 days without a license. It takes more setup, but it's the closest thing to reality you can get on a laptop. I maintain one of these specifically for scenarios where I need to test things the simulator handles poorly, like FSMO role transfers, schema master operations, or inter-site replication topology issues. Cloud-based labs exist too. Some training platforms provision temporary Azure AD tenants or simulated cloud identities for hands-on practice. These are useful if your focus is hybrid identity or Entra ID rather than on-premises Active Directory, but they have their own constraints—network latency, session timeouts, and limited access to low-level directory tools. If you're studying for an exam that includes on-prem AD questions, a local simulator or VM is the better choice. The bottom line is that a Directory Practice Simulator is a tool, not a substitute for real experience. It fills the gap between reading documentation and having a lab environment, and it's genuinely useful for building procedural fluency. But know where its blind spots are, don't trust it blindly, and supplement it with actual directory work whenever you can. The skills you need don't live in the simulator—they live in the moments when the simulator fails to predict what's actually going to happen.