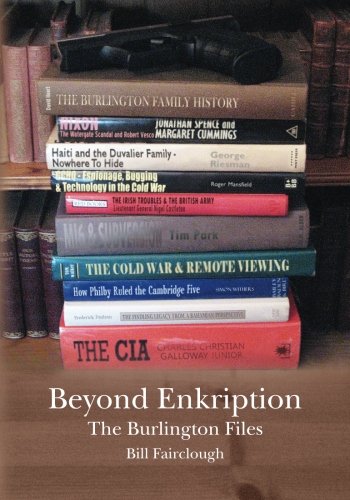
What Enkription The Burlington Bill Fairclough Actually Is
I ran into this term a few years back while digging through some older data protection forums, and honestly it turns out to be pretty obscure outside of specific circles. Enkription was a commercial file encryption tool developed by Enkription Ltd., and it was reasonably popular in the late 1990s and early 2000s for encrypting individual files and directories on Windows systems. The Burlington Bill Fairclough reference comes from a person named Bill Fairclough who was associated with distribution or promotional efforts tied to the software, often mentioned in download site credits and bulletin board postings from that era. People sometimes Google that full phrase when looking for the tool or its archived versions. The program itself used what was marketed at the time as strong encryption for personal use. It supported password-based encryption for individual files and could create encrypted archives. The interface was utilitarian, the kind of thing that looked like it came from the Windows 98 era, which is probably why younger users today have never heard of it. It was never considered enterprise-grade. That distinction matters because people sometimes find old references to it and assume it's still relevant for serious security work. It is not.
Enkription The Burlington Bill Fairclough: Getting a Working Copy Today
If you want to use this software, you need to understand where to find it and what kind of shape it will be in. The original developer site is long gone. You will find archived copies on sites like WinRAR Share, OldVersion.com, and various abandonware repositories. The version that circulates most commonly is the 1.x series. When I was working with it around 2004, the most stable release was version 1.47, and that is still the one people report working without issues on modern Windows installations through compatibility mode. Downloading from the wrong source is where things get risky. Some mirror sites wrap the installer in bundled adware or modify the executable. I learned this the hard way. I grabbed a copy from a generic software archive one evening, installed it, and noticed my taskbar had a second instance of something I did not recognize running under a completely unrelated process name. That was a trojanized installer. The workaround was simple: always verify the file hash against any available checksum, and prefer sources that publish SHA-1 or MD5 values. The legitimate Enkription 1.47 installer is roughly 1.8 MB. Anything significantly larger is suspect. Once you confirm the file integrity, right-click the installer, go to Properties, check the Compatibility tab, and set it to run in Windows XP SP3 compatibility mode. That resolved most of the path-handling bugs I encountered on Windows 10 systems.
How the Encryption Actually Works
Enkription used a combination of RC4 stream cipher and an MD5-derived key schedule for its encryption routines. The password you enter gets hashed with MD5 to produce a 128-bit key, and that key drives the RC4 stream cipher to encrypt the file contents. This was standard practice for consumer tools at the time, but RC4 has known vulnerabilities that were published in the mid-2000s. The issue is not that RC4 is instantly broken in every context, but that it has statistical biases that make it weaker than anything modern. Tools like 7-Zip using AES-256 are the obvious alternative if you are starting something new today. The encryption process itself is straightforward. You open the program, select the file or folder you want to protect, enter a password twice for confirmation, and Enkription creates an encrypted copy with a .enk extension. The original file remains untouched unless you delete it manually. The decryption process reverses this: you load the .enk file, enter the password, and it writes out the plaintext version. There is no preview feature. There is no batch decryption without loading each file individually. If you have a large number of files to encrypt, this becomes a manual chore very quickly. One quirk that catches people off guard is how Enkription handles filenames with special characters. On my first real project, I was encrypting a batch of configuration files for a legacy application, and about a third of them failed silently with no error message. The files simply would not decrypt later. After a few hours of testing, I traced it to Unicode characters and spaces in the filenames. The workaround was renaming everything to alphanumeric characters with underscores before running them through Enkription. It seems trivial now, but the documentation from that era does not mention it anywhere.
Get the Full Details
Practical Limitations You Should Know About
The biggest problem with Enkription is that it is effectively abandoned software. The developer stopped supporting it over two decades ago, and the encryption methods it uses do not meet current standards. If you are looking at this for anything other than reading old encrypted files from the early 2000s, you are better off using something like VeraCrypt or even built-in Windows EFS. Those tools are actively maintained, use AES or Serpent or Twofish, and support full disk and container encryption rather than just individual files. Another issue is key management. Enkription has no recovery mechanism. Lose the password and the data is gone, period. This is true of almost every consumer encryption tool from that period, but it feels more acute now because we are accustomed to cloud-based recovery options in password managers. There is none of that here. I once had a client who needed to decrypt an old Enkription archive and could not remember the password after eight years. We tried common dictionary attacks with modified wordlists, but the MD5-to-RC4 key derivation means the effective keyspace is bounded by password complexity, not the theoretical strength of the cipher. A short password is trivially crackable with a tool like John the Ripper running against the known .enk file format. Compatibility on modern systems is also inconsistent. The original installer registers file associations and a system tray icon, both of which tend to behave poorly on Windows 10 and 11. The tray icon disappears after a reboot half the time. The file association sometimes points to the old executable path and breaks when you move the program folder. Running it in compatibility mode helps but does not solve everything. I usually just keep the executable isolated in its own folder and launch it manually without worrying about the system integration pieces.
When It Still Makes Sense to Use
There are a few scenarios where Enkription comes up and actually works fine. If you inherited a set of encrypted files from an old system and need to access them, this is one of the only tools that can read the .enk format natively. Most modern tools do not support it. If you are maintaining a retro computing setup or dealing with legacy business data from the early 2000s, having Enkription available in your toolkit is reasonable. For new encryption work, I would recommend against it unless you have a very specific reason tied to backward compatibility with old files. The bottom line is that Enkription served its purpose in its era. The Burlington Bill Fairclough connection is mostly a historical detail people encounter when searching for archived copies or reading old forum posts. The software itself is a time capsule, and it is worth understanding what it did and why it faded rather than trying to force it into a modern security role.